0
preview
Archive link: archive.ph/c8Dbc
Archive link: archive.ph/c8Dbc
Not on this instance? Enter your own instance's domain to go straight to following c/bpf@group.lt there.
Archive link: archive.ph/c8Dbc
Archive link: archive.ph/c8Dbc


Video
Video
Anyone plans to attend?
Anyone plans to attend?


Learning tracks to explore Cilium
Learning tracks to explore Cilium

virtual event
virtual event

Series of articles on using Rust with eBPF
Series of articles on using Rust with eBPF

Very nice article to introduce to development using eBPF
Very nice article to introduce to development using eBPF

Very well written guide
Very well written guide

Challenges with the traditional network stack Packet flow in the kernel with XDP The mechanics of XDP programs How to build a simple XDP program Conclusion References
Challenges with the traditional network stack Packet flow in the kernel with XDP The mechanics of XDP programs How to build a simple XDP program Conclusion References
Introduced me to Lima (Lima: Linux virtual machines (on macOS, in most cases))
Introduced me to Lima (Lima: Linux virtual machines (on macOS, in most cases))
Great post overviewing BPF and some programming advice for it.
Great post overviewing BPF and some programming advice for it.
eBPF is a power horse you don’t really need to care about (unless you want to)
eBPF is a power horse you don’t really need to care about (unless you want to)
Built with eBPF & OpenTelemetry - Applications are instrumented using well-known, battle-tested open source observability technologies
Built with eBPF & OpenTelemetry - Applications are instrumented using well-known, battle-tested open source observability technologies

https://github.com/Gui774ume/krie
KRIe is a research project that aims to detect Linux Kernel exploits with eBPF. KRIe is far from being a bulletproof strategy: from eBPF related limitations to post exploitation detections that might rely on a compromised kernel to emit security events, it is clear that a motivated attacker will eventually be able to bypass it. That being said, the goal of the project is to make attackers’ lives harder and ultimately prevent out-of-the-box exploits from working on a vulnerable kernel.
https://github.com/Gui774ume/krie
KRIe is a research project that aims to detect Linux Kernel exploits with eBPF. KRIe is far from being a bulletproof strategy: from eBPF related limitations to post exploitation detections that might rely on a compromised kernel to emit security events, it is clear that a motivated attacker will eventually be able to bypass it. That being said, the goal of the project is to make attackers’ lives harder and ultimately prevent out-of-the-box exploits from working on a vulnerable kernel.
Another kubernetes observability tool ;)
Another kubernetes observability tool ;)

Rather deep talk
Rather deep talk


Nice overview of eBPF
Nice overview of eBPF

Very nice summary about eBPF.
Very nice summary about eBPF.

Catching up with eBPF events
Catching up with eBPF events
Some eBPF promo if you are still not convinced ;)
Some eBPF promo if you are still not convinced ;)
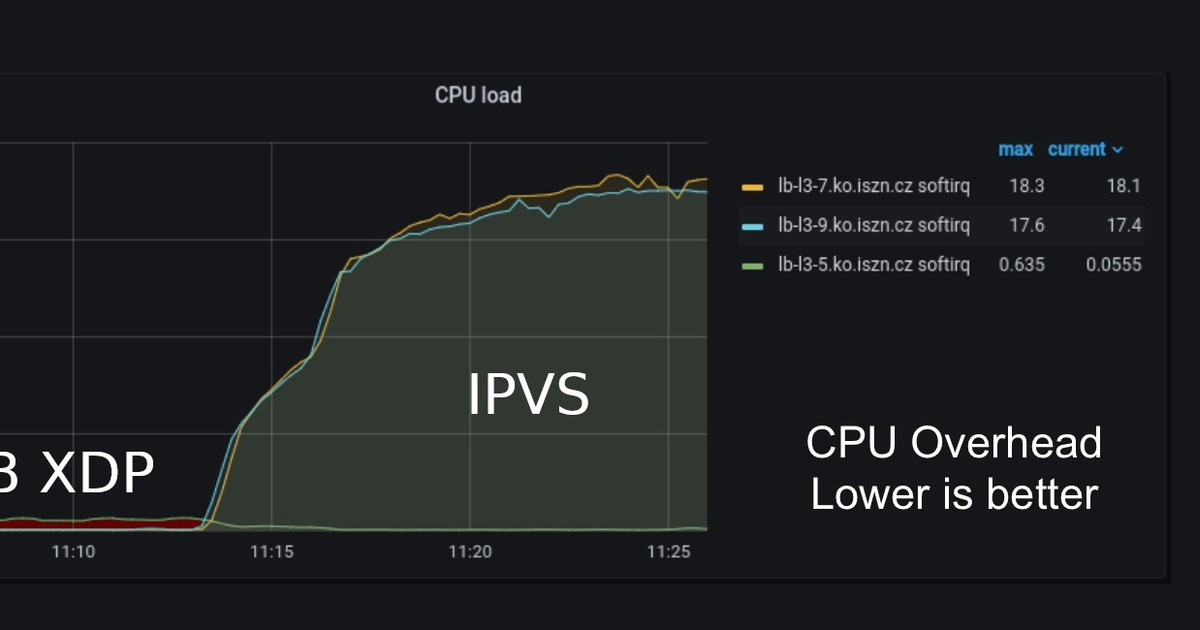
The screenshots speak for themselves, but the key take away for us was, L4LB XDP at the driver layer with a majority of HTTP traffic (~90% of our traffic is HTTP requests) saves us an unbelievable amount of CPUs needed to handle our production traffic.
The screenshots speak for themselves, but the key take away for us was, L4LB XDP at the driver layer with a majority of HTTP traffic (~90% of our traffic is HTTP requests) saves us an unbelievable amount of CPUs needed to handle our production traffic.

A take on eBPF, but what I have found mostly interesting is host proxies vs sidecars
A take on eBPF, but what I have found mostly interesting is host proxies vs sidecars
nifty tool
nifty tool


This is a video that really got me looking into bpf more deeply
This is a video that really got me looking into bpf more deeply