
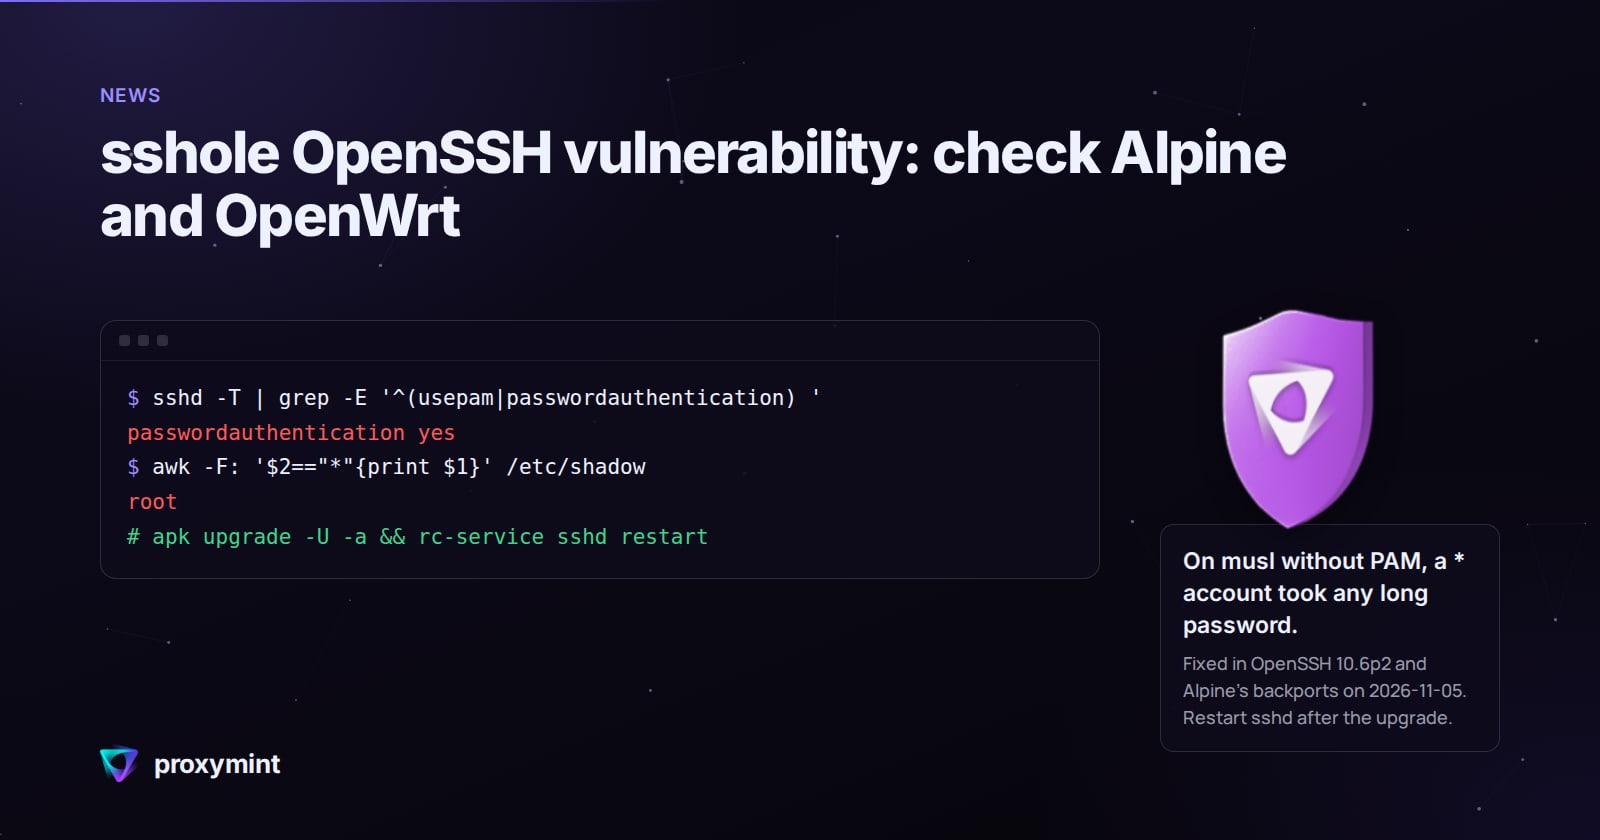
From the Alpine advisory and the researcher’s notes: musl’s crypt() gives back * when a password is over 256 bytes, and sshd then compares it with an account whose stored field is also *. Key-only users have that field, and so does the alpine user on tiny-cloud images. Fix is OpenSSH 10.6p2 or Alpine’s backport (on 3.24 that’s 10.3_p1-r2), plus an sshd restart. PasswordAuthentication no also closes it. Package table and check commands are in the link. Disclosure: it’s our blog, we run a proxy service.
0
sshole: OpenSSH on musl without PAM lets * accounts in with any 256+ byte password (fixed 5 Nov)
proxymint
sshole OpenSSH vulnerability: check Alpine and OpenWrt
sshole lets long passwords into OpenSSH on musl without PAM. Who is affected, the fixed Alpine and OpenWrt packages, and how to check your logs.
proxymint.com
0 comments
log in to comment.