0

12ft.io is critical to netneutrality, and now it’s gone

ResearchBuzz: Firehose The Verge: News publishers take paywall-blocker 12ft.io offline rbfirehose.com
preview

12ft.io was a clever service that exploited the fact that paywalls allowed Google to crawl their articles. By licking the boots of Google’s crawler, paywalls pollute the search index with their exclusive/closed content. Enshitification culminates by cluttering our search results with paywalls.

12ft.io gave people direct access to Google’s caches, so we could read the text that feeds Google’s index.

☠ 12ft.io is apparently dead now. “404 page not found”. wtf. We just lost an important disenshification mechanism. The linked news hit ~½ a year ago, but seems to have taken some time to actually play out.

(update)

Call to action: someone plz make an onion replacement for 12ft.io.

smry.ai is said to be the best 12ft.io alternative. But I just tried it and simply got a text version of the paywall registration nag. Same with removepaywalls.com

12ft.io was a clever service that exploited the fact that paywalls allowed Google to crawl their articles. By licking the boots of Google’s crawler, paywalls pollute the search index with their exclusive/closed content. Enshitification culminates by cluttering our search results with paywalls.

12ft.io gave people direct access to Google’s caches, so we could read the text that feeds Google’s index.

☠ 12ft.io is apparently dead now. “404 page not found”. wtf. We just lost an important disenshification mechanism. The linked news hit ~½ a year ago, but seems to have taken some time to actually play out.

(update)

Call to action: someone plz make an onion replacement for 12ft.io.

smry.ai is said to be the best 12ft.io alternative. But I just tried it and simply got a text version of the paywall registration nag. Same with removepaywalls.com

0

~~Two~~ Three browsers that should/will give us netneutrality by making web fetches p2p (CENO, Akoopa & Agregore)

preview

These apps are designed to combine bittorrent tech with a web browser to enable people to share websites peer to peer, so excluded people can reach restricted access websites indirectly and enjoy some liberation from Cloudflare:

  • CENO [Android & Windows] has been around a while but apparently lost steam. It’s archived and had no development apparently in 4 years. It’s also broken in my attempt to launch it. (update: a fork of CENO apparently had a commit ~2 weeks ago… so perhaps not a dead project after all)

  • Akoopa [linux] is new and was just presented at FOSDEM 2026. It’s a Tor Browser fork in very early stages. Apparently it only functions as a bittorrent client for grabbing static data at this point.

  • (update) Agregore looks like a healthy project.

I personally would be happy with just a backend. If I could pass an URL to rtorrent and end up with a local .mhtml file that any browser of my choice could open, I would be very happy.

These apps are designed to combine bittorrent tech with a web browser to enable people to share websites peer to peer, so excluded people can reach restricted access websites indirectly and enjoy some liberation from Cloudflare:

  • CENO [Android & Windows] has been around a while but apparently lost steam. It’s archived and had no development apparently in 4 years. It’s also broken in my attempt to launch it. (update: a fork of CENO apparently had a commit ~2 weeks ago… so perhaps not a dead project after all)

  • Akoopa [linux] is new and was just presented at FOSDEM 2026. It’s a Tor Browser fork in very early stages. Apparently it only functions as a bittorrent client for grabbing static data at this point.

  • (update) Agregore looks like a healthy project.

I personally would be happy with just a backend. If I could pass an URL to rtorrent and end up with a local .mhtml file that any browser of my choice could open, I would be very happy.

0

Mint Linux project’s anti-netneutrality hostility toward Tor and privacy is why I dropped support for Mint users

preview

I stopped distributing Linux Mint to the low-tech users who I support roughly ~10 years ago when the project jailed their docs in tor-hostile Cloudflare websites (e.g. readthedocs.io, IIRC).

A recent general search for info on getting a piece of hardware working on linux led to forums.linuxmint.com (the query had no relevance to Mint specifically). This website uses #Sucuri for elitist tor-hostile gatekeeping. There is no action for me to take since I already quit supporting Mint, other than perhaps to ask others in my local linux support group to also drop Mint support because our users should not face a choice between software freedom and privacy. Certainly when I am asked to install Mint for someone, I will refuse and try to steer them to Debian, perhaps with Cinnamon.

Screenshot attached. Not sure how long linuxmint has been using Sucuri for crude IP reputation discrimination, but note that the Debian project that feeds the Mint project demonstrates respect for people’s privacy. Mint adds value in some ways, but at the same time worsens a good distro by jailing information.

This is not a “something is better than nothing” scenario. It’s actually destructive. When you host a discriminatory access-restricted forum, you create an attraction for useful info and simultaneously become an obstacle to the information that would otherwise find a better host. If forums.linuxmint.com did not exist, the discussion would still occur somewhere and it would have a chance at occurring in an open access venue.

I stopped distributing Linux Mint to the low-tech users who I support roughly ~10 years ago when the project jailed their docs in tor-hostile Cloudflare websites (e.g. readthedocs.io, IIRC).

A recent general search for info on getting a piece of hardware working on linux led to forums.linuxmint.com (the query had no relevance to Mint specifically). This website uses #Sucuri for elitist tor-hostile gatekeeping. There is no action for me to take since I already quit supporting Mint, other than perhaps to ask others in my local linux support group to also drop Mint support because our users should not face a choice between software freedom and privacy. Certainly when I am asked to install Mint for someone, I will refuse and try to steer them to Debian, perhaps with Cinnamon.

Screenshot attached. Not sure how long linuxmint has been using Sucuri for crude IP reputation discrimination, but note that the Debian project that feeds the Mint project demonstrates respect for people’s privacy. Mint adds value in some ways, but at the same time worsens a good distro by jailing information.

This is not a “something is better than nothing” scenario. It’s actually destructive. When you host a discriminatory access-restricted forum, you create an attraction for useful info and simultaneously become an obstacle to the information that would otherwise find a better host. If forums.linuxmint.com did not exist, the discussion would still occur somewhere and it would have a chance at occurring in an open access venue.

0

Public Interest Groups Won’t Take Net Neutrality Case to Supreme Court Now

Broadband Breakfast Public Interest Groups Won’t Take Net Neutrality Case to Supreme Court Now broadbandbreakfast.com
preview

Cliff’s notes: Team GOP prevailed, the people lost on netneutrality. The only thing you can do now is cancel your broadband… something very few people have the will power to do.

I suppose the reason they did not take it to the supreme court is Trump managed to stack that court in favor of the right-wing nutjobs. So if the case goes there, it will do the GOP’s bidding to favor big business over the people and enter an oppressive decision that is even harder to correct in the future.

(note this story was originally on Ars Technica but that site is enshitified so I found a less enshitified source to link – something more fedi posters should do)

Cliff’s notes: Team GOP prevailed, the people lost on netneutrality. The only thing you can do now is cancel your broadband… something very few people have the will power to do.

I suppose the reason they did not take it to the supreme court is Trump managed to stack that court in favor of the right-wing nutjobs. So if the case goes there, it will do the GOP’s bidding to favor big business over the people and enter an oppressive decision that is even harder to correct in the future.

(note this story was originally on Ars Technica but that site is enshitified so I found a less enshitified source to link – something more fedi posters should do)

0

Lemmyverse is not decentralised. It’s neutral at best.

preview

cross-posted from: slrpnk.net/post/24727683

The fediverse w/the activitypub API sell itself as being decentralised, but it’s actually just neutral. It merely enables decentralised forums to coexist with centralised venues. The Lemmy implementation in particular does nothing to proactively promote decentralisation or counter concentrations of power.

When the software is not designed to steer toward decentralisation, centralisation persists because the network effect is left uncountered. The current stats prove that a mass majority of users and their activity are subject to the concentrated power of a few, which ultimately singularly falls under the power, oversight, and competency of the biggest walled garden in the world: Cloudflare Inc, in the US.

Calling Lemmy “neutral” is overly generous, in fact. When the stock Lemmy web client is queried for communities, it prioritises the giant centralised communities in top rankings of the search results. It’s no better than Google, where Cloudflare also dominates the top slots in web search results. This exacerbates the network effect by cattle-herding people toward increased centralisation.

Lemmy ranks decentralised communities at the bottom. And in some cases the ranking is so low that it’s out of reach when cross-posting. The cross-post mechanism forces a search for the target community, and that search does not support entry of the address of the community that includes the domain. When the list is so long it exceeds the pulldown window length, it’s out of reach.

Yes, we know centralisation is not their deliberate goal. Lemmy developers fear that newcoming novices would unwittingly post in a ghost town without strategically cross-posting and then become immediately discouraged by minimal engagement, and from there bounce back to Twitter or wherever they came from. But it must be realised that the mass nannied steering they have resorted to has cultivated centralisation that defeats the founding purpose of the fedi.

cross-posted from: slrpnk.net/post/24727683

The fediverse w/the activitypub API sell itself as being decentralised, but it’s actually just neutral. It merely enables decentralised forums to coexist with centralised venues. The Lemmy implementation in particular does nothing to proactively promote decentralisation or counter concentrations of power.

When the software is not designed to steer toward decentralisation, centralisation persists because the network effect is left uncountered. The current stats prove that a mass majority of users and their activity are subject to the concentrated power of a few, which ultimately singularly falls under the power, oversight, and competency of the biggest walled garden in the world: Cloudflare Inc, in the US.

Calling Lemmy “neutral” is overly generous, in fact. When the stock Lemmy web client is queried for communities, it prioritises the giant centralised communities in top rankings of the search results. It’s no better than Google, where Cloudflare also dominates the top slots in web search results. This exacerbates the network effect by cattle-herding people toward increased centralisation.

Lemmy ranks decentralised communities at the bottom. And in some cases the ranking is so low that it’s out of reach when cross-posting. The cross-post mechanism forces a search for the target community, and that search does not support entry of the address of the community that includes the domain. When the list is so long it exceeds the pulldown window length, it’s out of reach.

Yes, we know centralisation is not their deliberate goal. Lemmy developers fear that newcoming novices would unwittingly post in a ghost town without strategically cross-posting and then become immediately discouraged by minimal engagement, and from there bounce back to Twitter or wherever they came from. But it must be realised that the mass nannied steering they have resorted to has cultivated centralisation that defeats the founding purpose of the fedi.

0

There is a “Cathedral and Bazaar” within the fediverse that manifests as utilitarian users and deontological users, respectively

preview

cross-posted from: slrpnk.net/post/24598576

The state of the fedi superficially parallels what Eric S. Raymond articulated in the 1990s on software construction. There are two models for digital community building within the fediverse. The intent was a decentralised bazaar whereby power is well dispersed, with no single entity excessively wielding disproportionate power. Activitypub was designed to enable the bazaar model to exist, but it neglects to curtail the antithetical model that anarchy-minded folks want to escape: the cathedral.

The hope and expectation was simply that builders of giant monolithic cathedrals would have no interest in the fedi; that they would want their empire to take the conventional path of walling themselves off. Fedi founders did not envision ambitions for power would emerge within the fedi. Who would have predicted that Facebook would decide to compromise its garden walls in exchange for influence over a quite small population? Or that Cloudflare’s centralized walled garden would be exploited to supercharge disproportionate growth by node operators intent on using the network effect to concentrate power? These kinds of technofeudal actors have traditionally vied for absolute power without attempting to cannabalise and occupy a fair structure to then coexist with.

Fedi founders thought the federate/defederate option would sufficiently control for actors who would work against the vision of the bazaar. This blunt tool relies heavily on the demographic of relative pseudo anarchists being larger than it is.

I think it was Kensanata (Alex Schröder) who notably stressed what I regard as a true dichotomy, the sentiment of which was something to the effect of:

you can simply go where the people are, or you can go where the platform and tech is well-designed.¹

The former are utilitarians and the latter are deontologists who find other people (though far fewer) that share the same understanding and appreciation of structures that feature resistance to tyranny. The separation is comparable to anarchists (at heart) seeking out a small freedom-rich niche away from the ivory tower cathedral.

The bazaar (decentralised) segment of the fedi comes at the cost of utility, as principles of digital ethics trump the instant gratification of a large audience. The sacrifice is not in vain. It’s made with an expectation that wisdom will spread and sustain. Though it seems clear that the cathedral will always exist and perhaps always enjoy dominance of the majority who serve it (are pawned by it).

There is a noteworthy contrast from Raymond’s C&B essay. Raymond likens the bazaar to “selfish agents” attributed to “utilitarian” Linux hackers under the idea that Linus harnesses their egos collectively (“egoboo”). Whereas in the fediverse of community builders, it is the selfish agents unwilling to compromise time and convenience who fill the cathedrals, baited by heavily populated communities.

Raves and Burning Man started off small and great; rich in culture, before rapid growth diluted the subculture and commercialisation did what it does. The natural response is to “take it underground” to try to restore the original greatness.

The fedi has passed that inflection point. We have LW serfs popping into */c/privacy communities to heckle whoever they perceive as “paranoid”, or worse, deliver a lecture on privacy (from Cloudflare). There is a profound and somewhat ironic number of CF cathedral folks making way into digital rights types of communities, not seeing the starkness of which would be comparable to Donald Trump appearing at a reggae festival, or an AOL user in the 1990s stepping into an engineering usenet newsgroup.

So here’s a fun search result:

🌩 lemmy.world🌩|decentralization 🌩 kbin.earth🌩|decentralize ⚠lemmy.ml/c/decentralized

There are just 3 communities specifically for decentralisation chatter and they are all on centralised hosts. It’s actually useful that they exist in those places from an outreach standpoint. But it’s likely being overly generous to assume they exist for outreach to those who need to be reached.

Anyway, going forward we need tools and datasets with metrics. The metrics currently serve the utilitarian who simply looks for the most exposure of their content without regard to the ethics underpinning decentralisation. Metrics that serve the bazaar would have to measure degree of power centralisation.

¹ paraphrased - not an exact quote

cross-posted from: slrpnk.net/post/24598576

The state of the fedi superficially parallels what Eric S. Raymond articulated in the 1990s on software construction. There are two models for digital community building within the fediverse. The intent was a decentralised bazaar whereby power is well dispersed, with no single entity excessively wielding disproportionate power. Activitypub was designed to enable the bazaar model to exist, but it neglects to curtail the antithetical model that anarchy-minded folks want to escape: the cathedral.

The hope and expectation was simply that builders of giant monolithic cathedrals would have no interest in the fedi; that they would want their empire to take the conventional path of walling themselves off. Fedi founders did not envision ambitions for power would emerge within the fedi. Who would have predicted that Facebook would decide to compromise its garden walls in exchange for influence over a quite small population? Or that Cloudflare’s centralized walled garden would be exploited to supercharge disproportionate growth by node operators intent on using the network effect to concentrate power? These kinds of technofeudal actors have traditionally vied for absolute power without attempting to cannabalise and occupy a fair structure to then coexist with.

Fedi founders thought the federate/defederate option would sufficiently control for actors who would work against the vision of the bazaar. This blunt tool relies heavily on the demographic of relative pseudo anarchists being larger than it is.

I think it was Kensanata (Alex Schröder) who notably stressed what I regard as a true dichotomy, the sentiment of which was something to the effect of:

you can simply go where the people are, or you can go where the platform and tech is well-designed.¹

The former are utilitarians and the latter are deontologists who find other people (though far fewer) that share the same understanding and appreciation of structures that feature resistance to tyranny. The separation is comparable to anarchists (at heart) seeking out a small freedom-rich niche away from the ivory tower cathedral.

The bazaar (decentralised) segment of the fedi comes at the cost of utility, as principles of digital ethics trump the instant gratification of a large audience. The sacrifice is not in vain. It’s made with an expectation that wisdom will spread and sustain. Though it seems clear that the cathedral will always exist and perhaps always enjoy dominance of the majority who serve it (are pawned by it).

There is a noteworthy contrast from Raymond’s C&B essay. Raymond likens the bazaar to “selfish agents” attributed to “utilitarian” Linux hackers under the idea that Linus harnesses their egos collectively (“egoboo”). Whereas in the fediverse of community builders, it is the selfish agents unwilling to compromise time and convenience who fill the cathedrals, baited by heavily populated communities.

Raves and Burning Man started off small and great; rich in culture, before rapid growth diluted the subculture and commercialisation did what it does. The natural response is to “take it underground” to try to restore the original greatness.

The fedi has passed that inflection point. We have LW serfs popping into */c/privacy communities to heckle whoever they perceive as “paranoid”, or worse, deliver a lecture on privacy (from Cloudflare). There is a profound and somewhat ironic number of CF cathedral folks making way into digital rights types of communities, not seeing the starkness of which would be comparable to Donald Trump appearing at a reggae festival, or an AOL user in the 1990s stepping into an engineering usenet newsgroup.

So here’s a fun search result:

🌩 lemmy.world🌩|decentralization 🌩 kbin.earth🌩|decentralize ⚠lemmy.ml/c/decentralized

There are just 3 communities specifically for decentralisation chatter and they are all on centralised hosts. It’s actually useful that they exist in those places from an outreach standpoint. But it’s likely being overly generous to assume they exist for outreach to those who need to be reached.

Anyway, going forward we need tools and datasets with metrics. The metrics currently serve the utilitarian who simply looks for the most exposure of their content without regard to the ethics underpinning decentralisation. Metrics that serve the bazaar would have to measure degree of power centralisation.

¹ paraphrased - not an exact quote

0

Wrote a script to find decentralised communities w/in the fedi. It selects nodes w/active users < avg+2σ. Is that a good approach? Check my math plz.

preview

cross-posted from: slrpnk.net/post/24512484

(The pic is sample output for an arbitrary query on “vegan vege pesc”. Irrelevant side note: there is no free-world venue for pescatarians… just one in L/W that scrolled off the screen)

CF

The federation is not wholly decentralised, obviously, when giant centralised fiefdoms like Facebook “Threads”™ and Cloudflare hook in their technofeudal variety of oppressive infra and abuse their power.

Each post submission begins with finding a relevant venue for the content and it must be consistent with my sense of ethics. Cloudflare is automatically nixed because it’s inherently centralised in a walled garden (regardless of the user count for any given node). CF is a non-starter for an open, free, and fair society (fair implying power balance, equality, transparency, etc).

My script queries the catalog of communities for relevant venues. It still prints the Cloudflare walled garden because it’s useful to see what names match my regex queries, which sometimes helps form a better query. It’s the only thing #LemmyWorld is good for (a shit-ton of community names with redundant variations of the same subject matter). Those results are in red, tagged with a thundercloud (🌩 ), and printed first (because when they scroll off the terminal I don’t typically care to scroll up to see them).

non-CF

CF is not the only issue. Some non-CF nodes are centralized due to uncontrolled growth to disproportionately large sizes. I don’t cancel them hard-and-fast like CF nodes, but they get treated with low “last resort” favorability. They have the warning symbol (⚠) and are in yellow.

Is my math decent?

My script began by filtering on total user count. Then I realised dead or dormant users probably should not count because such users don’t really contribute to a node’s disproportionate power over a population. It’s active users that matter. But if the number of active users in a day are filtered on, that’s too dynamic for deciding where my post can live for a month or however long it is relevant. So I took the users_active_half_year count. Is that sensible?

What constitutes an “active” user, simply logging in, or commenting?

The line is drawn at 2 standard deviations above the average – after tossing outliers. Nodes with less than 5 active users in ½ a year are likely 1-person nodes which do not influence the average. The average is around 320 active ½yr users per node. The standard deviation is ~702 users. My statistical competence is rusty for sure, but I’m a bit bothered by a standard deviation that’s more than double the mean. Seems like a variation so wild it should perhaps be disregarded. Nonetheless, I opted to flag nodes that exceed ~1724 users_active_half_year.

The pseudocode looks like this:

avg=$(sqlite3 "$db" 'select round(avg([counts.users_active_half_year])) from node_tbl where tags not like "%cloudflare%" and [counts.users_active_half_year] > 4')
variance=$(sqlite3 "$db" 'select avg(([counts.users_active_half_year] - subtbl.aua) * ([counts.users_active_half_year] - subtbl.aua)) as var from node_tbl, (select avg([counts.users_active_half_year]) as aua from node_tbl where tags not like "%cloudflare%" and [counts.users_active_half_year] > 4) as subtbl where tags not like "%cloudflare%" and [counts.users_active_half_year] > 4;')

sqlite3 "$db" "select case when baseurl in (select baseurl from node_tbl where [counts.users_active_half_year] > $avg+sqrt($variance)*2) then '$yellow⚠' else '$cyan' end||baseurl||'$reset',name from community_tbl where (name like '%${1}%' or desc like '%${1}%') and baseurl not in (select baseurl from node_tbl where tags like '%cloudflare%') order by baseurl,name"

Code is ugly because sqlite does not have a stdev builtin function.

My other thought is to cut slack for closed nodes because at least they are expected to shrink. To list the possible figures to filter on, this is a record for lemmy.ml (the biggest non-Cloudflare node): :::spoiler record for lemmy.ml url = lemmy.ml baseurl = lemmy.ml name = Lemmy desc = A community of privacy and FOSS enthusiasts, run by Lemmy’s developers downvotes = 1 nsfw = 1 create_admin = 0 private = 0 fed = 1 version = 0.19.12 open = 1 usage.users.total = 54790 usage.users.activeHalfyear = 4201 usage.users.activeMonth = 2125 usage.localPosts = 167331 usage.localComments = 818559 counts.site_id = 1 counts.users = 54790 counts.posts = 167331 counts.comments = 818559 counts.communities = 4608 counts.users_active_day = 947 counts.users_active_week = 1496 counts.users_active_month = 2125 counts.users_active_half_year = 4201 icon = lemmy.ml/…/fa6d9660-4f1f-4e90-ac73-b897216db6f3.p… banner = langs = [“all”] date = 2019-04-20T18:53:54.608882Z published = 1555786434000 time = 1751974533970 score = uptime.domain = lemmy.ml uptime.latency = 0.034 uptime.countryname = France uptime.uptime_alltime = 99.04 uptime.date_created = uptime.date_updated = 2021-10-29 15:09:21 uptime.date_laststats = 2025-04-11 21:03:25 uptime.score = 100 uptime.status = 1 isSuspicious = 0 metrics.usersTotal = 54790 metrics.usersMonth = 2125 metrics.usersWeek = 1496 metrics.totalActivity = 985890 metrics.localPosts = 167331 metrics.localComments = 818559 metrics.averageUsers = 50720.8825256975 metrics.biggestJump = 225 metrics.averagePerMinute = 0.02475 metrics.userActivityScore = 0.055574151274483 metrics.activityUserScore = 17.9939770031028 metrics.userActiveMonthScore = 25.7835294117647 tags = [] susReason = [] trust.lastCrawled = 1751974533970 trust.baseurl = lemmy.ml trust.metrics.usersTotal = 54790 trust.metrics.usersMonth = 2125 trust.metrics.usersWeek = 1496 trust.metrics.totalActivity = 985890 trust.metrics.localPosts = 167331 trust.metrics.localComments = 818559 trust.metrics.averageUsers = 50720.8825256975 trust.metrics.biggestJump = 225 trust.metrics.averagePerMinute = 0.02475 trust.metrics.userActivityScore = 0.055574151274483 trust.metrics.activityUserScore = 17.9939770031028 trust.metrics.userActiveMonthScore = 25.7835294117647 trust.users = 54790 trust.name = Lemmy trust.base = lemmy.ml trust.actor_id = lemmy.ml trust.tags = [] trust.guarantor = fediseer.com trust.endorsements = 17 trust.score = 598.1875 trust.reasons = [] blocks.incoming = 0 blocks.outgoing = 0 blocked = [] :::

Some communities missing from the Lemmyverse DB - why?

Anyone know why some slrpnk.net communities are in the Lemmyverse DB, and some are not? E.g. why is !nolawns@slrpnk.net missing, despite many others from the same node that are included?

More importantly, what’s the fix apart from crawling all the nodes (which would probably be unwelcome)? Is there another open DB apart from Lemmyverse? There is fediverse.space and fediverse.observer, but they don’t appear to be sharing their data.

cross-posted from: slrpnk.net/post/24512484

(The pic is sample output for an arbitrary query on “vegan vege pesc”. Irrelevant side note: there is no free-world venue for pescatarians… just one in L/W that scrolled off the screen)

CF

The federation is not wholly decentralised, obviously, when giant centralised fiefdoms like Facebook “Threads”™ and Cloudflare hook in their technofeudal variety of oppressive infra and abuse their power.

Each post submission begins with finding a relevant venue for the content and it must be consistent with my sense of ethics. Cloudflare is automatically nixed because it’s inherently centralised in a walled garden (regardless of the user count for any given node). CF is a non-starter for an open, free, and fair society (fair implying power balance, equality, transparency, etc).

My script queries the catalog of communities for relevant venues. It still prints the Cloudflare walled garden because it’s useful to see what names match my regex queries, which sometimes helps form a better query. It’s the only thing #LemmyWorld is good for (a shit-ton of community names with redundant variations of the same subject matter). Those results are in red, tagged with a thundercloud (🌩 ), and printed first (because when they scroll off the terminal I don’t typically care to scroll up to see them).

non-CF

CF is not the only issue. Some non-CF nodes are centralized due to uncontrolled growth to disproportionately large sizes. I don’t cancel them hard-and-fast like CF nodes, but they get treated with low “last resort” favorability. They have the warning symbol (⚠) and are in yellow.

Is my math decent?

My script began by filtering on total user count. Then I realised dead or dormant users probably should not count because such users don’t really contribute to a node’s disproportionate power over a population. It’s active users that matter. But if the number of active users in a day are filtered on, that’s too dynamic for deciding where my post can live for a month or however long it is relevant. So I took the users_active_half_year count. Is that sensible?

What constitutes an “active” user, simply logging in, or commenting?

The line is drawn at 2 standard deviations above the average – after tossing outliers. Nodes with less than 5 active users in ½ a year are likely 1-person nodes which do not influence the average. The average is around 320 active ½yr users per node. The standard deviation is ~702 users. My statistical competence is rusty for sure, but I’m a bit bothered by a standard deviation that’s more than double the mean. Seems like a variation so wild it should perhaps be disregarded. Nonetheless, I opted to flag nodes that exceed ~1724 users_active_half_year.

The pseudocode looks like this:

avg=$(sqlite3 "$db" 'select round(avg([counts.users_active_half_year])) from node_tbl where tags not like "%cloudflare%" and [counts.users_active_half_year] > 4')
variance=$(sqlite3 "$db" 'select avg(([counts.users_active_half_year] - subtbl.aua) * ([counts.users_active_half_year] - subtbl.aua)) as var from node_tbl, (select avg([counts.users_active_half_year]) as aua from node_tbl where tags not like "%cloudflare%" and [counts.users_active_half_year] > 4) as subtbl where tags not like "%cloudflare%" and [counts.users_active_half_year] > 4;')

sqlite3 "$db" "select case when baseurl in (select baseurl from node_tbl where [counts.users_active_half_year] > $avg+sqrt($variance)*2) then '$yellow⚠' else '$cyan' end||baseurl||'$reset',name from community_tbl where (name like '%${1}%' or desc like '%${1}%') and baseurl not in (select baseurl from node_tbl where tags like '%cloudflare%') order by baseurl,name"

Code is ugly because sqlite does not have a stdev builtin function.

My other thought is to cut slack for closed nodes because at least they are expected to shrink. To list the possible figures to filter on, this is a record for lemmy.ml (the biggest non-Cloudflare node): :::spoiler record for lemmy.ml url = lemmy.ml baseurl = lemmy.ml name = Lemmy desc = A community of privacy and FOSS enthusiasts, run by Lemmy’s developers downvotes = 1 nsfw = 1 create_admin = 0 private = 0 fed = 1 version = 0.19.12 open = 1 usage.users.total = 54790 usage.users.activeHalfyear = 4201 usage.users.activeMonth = 2125 usage.localPosts = 167331 usage.localComments = 818559 counts.site_id = 1 counts.users = 54790 counts.posts = 167331 counts.comments = 818559 counts.communities = 4608 counts.users_active_day = 947 counts.users_active_week = 1496 counts.users_active_month = 2125 counts.users_active_half_year = 4201 icon = lemmy.ml/…/fa6d9660-4f1f-4e90-ac73-b897216db6f3.p… banner = langs = [“all”] date = 2019-04-20T18:53:54.608882Z published = 1555786434000 time = 1751974533970 score = uptime.domain = lemmy.ml uptime.latency = 0.034 uptime.countryname = France uptime.uptime_alltime = 99.04 uptime.date_created = uptime.date_updated = 2021-10-29 15:09:21 uptime.date_laststats = 2025-04-11 21:03:25 uptime.score = 100 uptime.status = 1 isSuspicious = 0 metrics.usersTotal = 54790 metrics.usersMonth = 2125 metrics.usersWeek = 1496 metrics.totalActivity = 985890 metrics.localPosts = 167331 metrics.localComments = 818559 metrics.averageUsers = 50720.8825256975 metrics.biggestJump = 225 metrics.averagePerMinute = 0.02475 metrics.userActivityScore = 0.055574151274483 metrics.activityUserScore = 17.9939770031028 metrics.userActiveMonthScore = 25.7835294117647 tags = [] susReason = [] trust.lastCrawled = 1751974533970 trust.baseurl = lemmy.ml trust.metrics.usersTotal = 54790 trust.metrics.usersMonth = 2125 trust.metrics.usersWeek = 1496 trust.metrics.totalActivity = 985890 trust.metrics.localPosts = 167331 trust.metrics.localComments = 818559 trust.metrics.averageUsers = 50720.8825256975 trust.metrics.biggestJump = 225 trust.metrics.averagePerMinute = 0.02475 trust.metrics.userActivityScore = 0.055574151274483 trust.metrics.activityUserScore = 17.9939770031028 trust.metrics.userActiveMonthScore = 25.7835294117647 trust.users = 54790 trust.name = Lemmy trust.base = lemmy.ml trust.actor_id = lemmy.ml trust.tags = [] trust.guarantor = fediseer.com trust.endorsements = 17 trust.score = 598.1875 trust.reasons = [] blocks.incoming = 0 blocks.outgoing = 0 blocked = [] :::

Some communities missing from the Lemmyverse DB - why?

Anyone know why some slrpnk.net communities are in the Lemmyverse DB, and some are not? E.g. why is !nolawns@slrpnk.net missing, despite many others from the same node that are included?

More importantly, what’s the fix apart from crawling all the nodes (which would probably be unwelcome)? Is there another open DB apart from Lemmyverse? There is fediverse.space and fediverse.observer, but they don’t appear to be sharing their data.

0

StackExchange / StackOverflow ratchets up the aggression against non-boot-licking free-worlders, using Cloudflare to thwart decentralised access

GitHub 403 error · Issue #175 · httpjamesm/AnonymousOverflow github.com
preview

A lot of tech knowledge is jailed in #StackOverflow, #StackExchange. Too much. The tech world is very dependant on this single gate keeper. This week, freedom to access SE’s indispensible tech knowledge has been lost.

Timeline

  • pre-2016: SE jailed itself inside Cloudflare
  • ? - At some point SE became “openly” accessible and Cloudflare-free. But a massive #cookieWall blocked content and it was broken to a large extent. That is, in some browsers there was no way to get past the cookie wall.
  • 2022 - #AnonymousOverflow was founded. This front-end platform made the cookie wall problem go away regardless of your browser and anonymity.
  • 2023 - SE reverted back to Cloudflare, effectively making the need for AnonymousOverflow more dire; more important.
  • This week - SE tunes the Cloudflare settings to aggressively block AnonymousOverflow instances, ultimately killing off free-world access to tech information.

A lot of tech knowledge is jailed in #StackOverflow, #StackExchange. Too much. The tech world is very dependant on this single gate keeper. This week, freedom to access SE’s indispensible tech knowledge has been lost.

Timeline

  • pre-2016: SE jailed itself inside Cloudflare
  • ? - At some point SE became “openly” accessible and Cloudflare-free. But a massive #cookieWall blocked content and it was broken to a large extent. That is, in some browsers there was no way to get past the cookie wall.
  • 2022 - #AnonymousOverflow was founded. This front-end platform made the cookie wall problem go away regardless of your browser and anonymity.
  • 2023 - SE reverted back to Cloudflare, effectively making the need for AnonymousOverflow more dire; more important.
  • This week - SE tunes the Cloudflare settings to aggressively block AnonymousOverflow instances, ultimately killing off free-world access to tech information.
0

(success story) A fiber carrier drilled into homes without consent to run their cables and used Cloudflare to make their service exclusive -- and how my friend hit back

preview

A new fiber network provider drilled into the façades of private homes to run their cables, without consent, to save themselves the cost of digging. Their website was in Cloudflare’s exclusive walled garden – which means they were drilling people’s façades who were not even necessarily in the included group who could get service.

So my friend hand-delivered a letter and got the receptionist to sign for it (thus can be recognised by a court). The letter objected to the use of their home to deploy a network that exclude everyone Cloudflare excludes, and also said something like “since you had no consent to drill my house and I explicitly object, I will detach your cable on date X. And unless you say otherwise, if you consent to my work then take no action. Your inaction will signal acceptance to my plans.”

The Internet carrier had to employ a lawyer to write a long strongly worded response citing laws and their right to drill people’s façades, which they then had to send using registered mail (these letters are not cheap).

That’s it. My friend did not actually go through with it. But it’s a bit of justice nonetheless because the Internet provider had to pay a lawyer then pay the reg. letter costs. Would be even better if a lot of people would react in this way and help pile on the costs.

Incidentally, the network carrier quit using Cloudflare. They did not state why, but it’s nice to think that it’s possible that they realised the injustice of being exclusive.

A new fiber network provider drilled into the façades of private homes to run their cables, without consent, to save themselves the cost of digging. Their website was in Cloudflare’s exclusive walled garden – which means they were drilling people’s façades who were not even necessarily in the included group who could get service.

So my friend hand-delivered a letter and got the receptionist to sign for it (thus can be recognised by a court). The letter objected to the use of their home to deploy a network that exclude everyone Cloudflare excludes, and also said something like “since you had no consent to drill my house and I explicitly object, I will detach your cable on date X. And unless you say otherwise, if you consent to my work then take no action. Your inaction will signal acceptance to my plans.”

The Internet carrier had to employ a lawyer to write a long strongly worded response citing laws and their right to drill people’s façades, which they then had to send using registered mail (these letters are not cheap).

That’s it. My friend did not actually go through with it. But it’s a bit of justice nonetheless because the Internet provider had to pay a lawyer then pay the reg. letter costs. Would be even better if a lot of people would react in this way and help pile on the costs.

Incidentally, the network carrier quit using Cloudflare. They did not state why, but it’s nice to think that it’s possible that they realised the injustice of being exclusive.

0

New forum where people excluded by Twitter and Facebook can get their msgs proxied

Proxy my message to my reps in the walled garden - Fedia fedia.io
preview

The linked “magazine” (community) is where Twitter & FB users can converge with non-Twitter & non-FB users to have their messages to their gov reps relayed. This is a hack to circumvent digital exclusion.

The linked “magazine” (community) is where Twitter & FB users can converge with non-Twitter & non-FB users to have their messages to their gov reps relayed. This is a hack to circumvent digital exclusion.

0

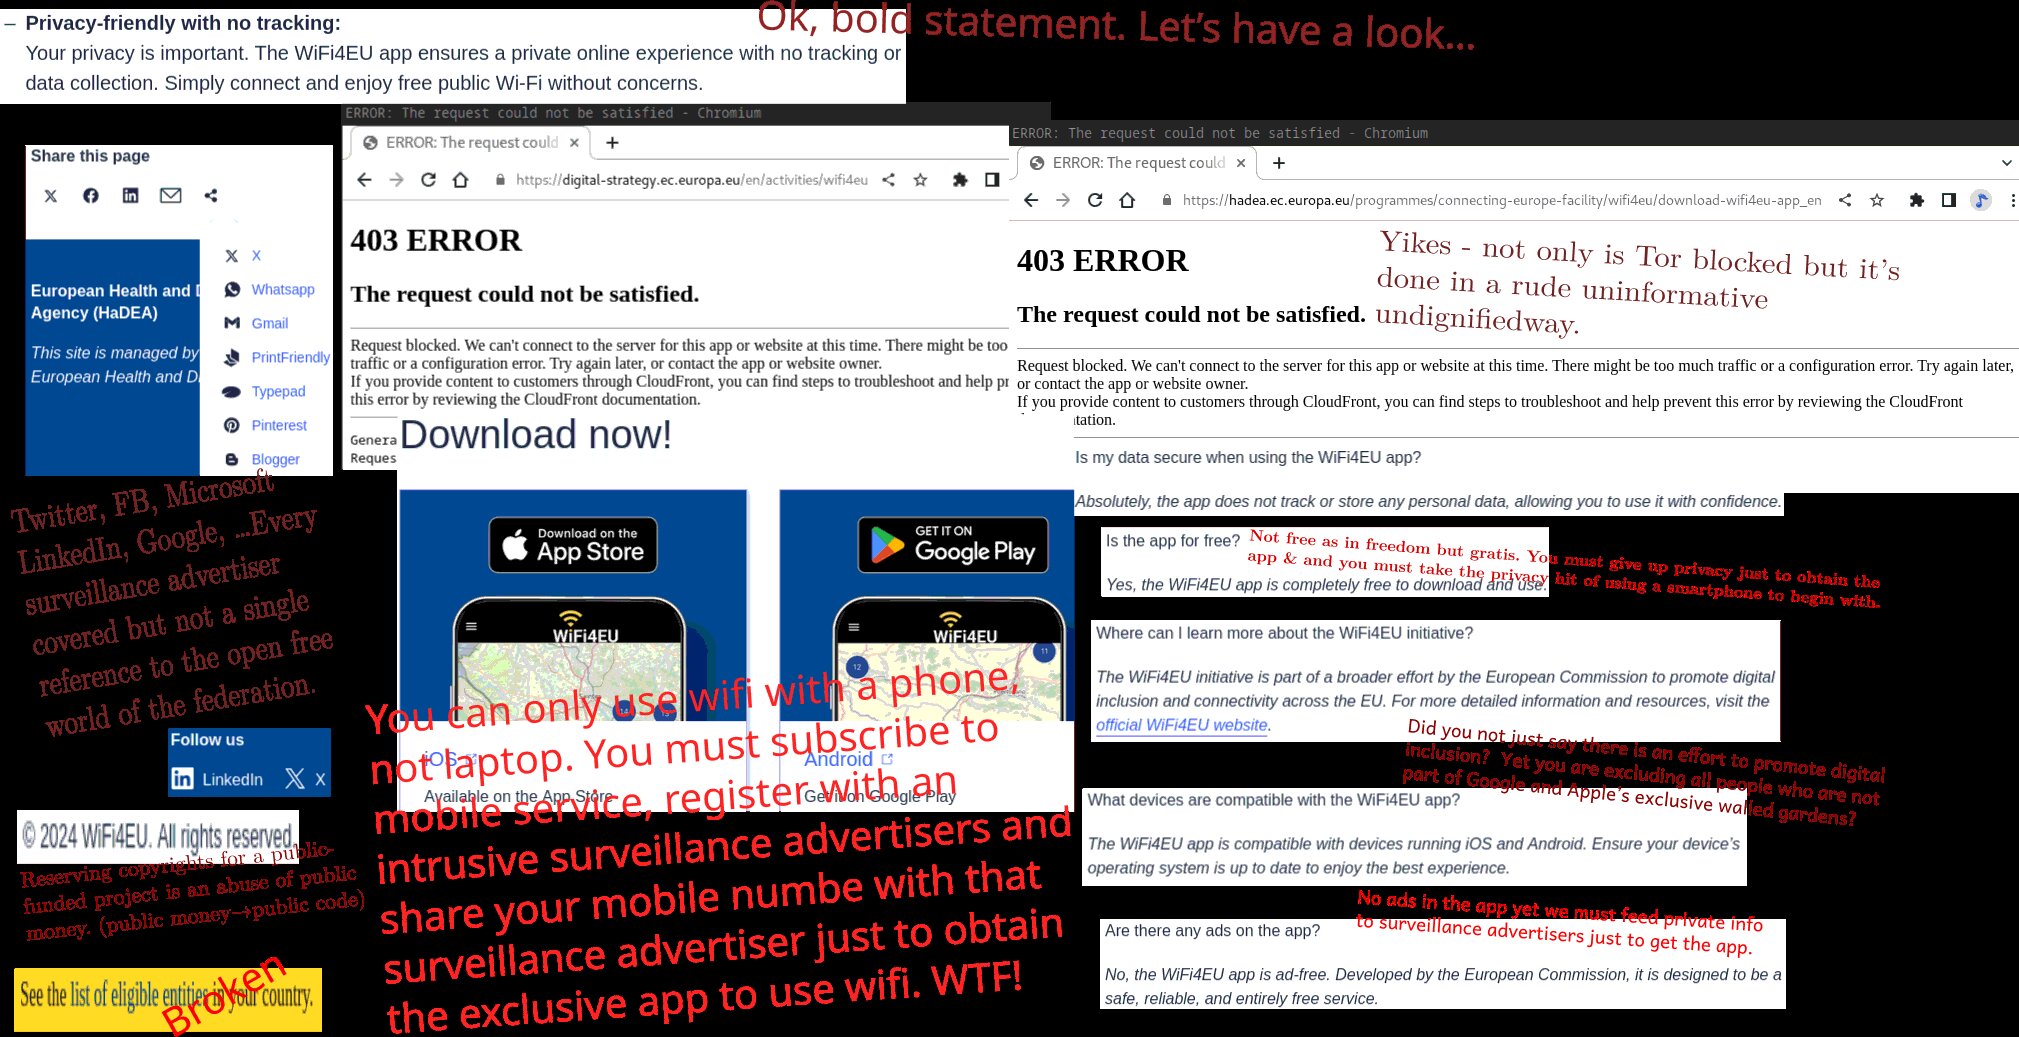
Collage illustrating the EU’s Wifi4EU shit-show of digital exclusion

Collage illustrating the EU’s Wifi4EU shit-show - europe - Fedia fedia.io
preview

What’s going to happen in the EU is public spaces like libraries which already have wi-fi service are going unplug their wi-fi service and take this free wifi4eu option. Then only people who can get the special Google/Apple-only app will have wi-fi access.

So while the project falsely claims to favor digital inclusion, they will actually be making existing networks more exclusive.

What’s going to happen in the EU is public spaces like libraries which already have wi-fi service are going unplug their wi-fi service and take this free wifi4eu option. Then only people who can get the special Google/Apple-only app will have wi-fi access.

So while the project falsely claims to favor digital inclusion, they will actually be making existing networks more exclusive.

0

US federal law becoming inaccessible (Cloudflare!)

preview

ecfr.gov used to be a decent source for looking up laws. When looking up the anti spam laws, the linked page is littered with links to an access-restricted Cloudflare site (www.govinfo.gov). The important parts of the law are missing from ecfr.gov. It’s common for various states to have this mom-pop shop competency level, but tragic and embarrassing that the US feds lack competency to the point of Cloudflare-dependency.

Often Cornell University publishes federal law and mitigates the embarrassment to some extent. But when looking up the CAN-SPAM law at Cornell, the Cornell law site redirects to another access-restricted Cloudflare site (www.gpo.gov).

There needs to be a fundamental high-level that requires all laws to be accessible to all people, not just people who Cloudflare is willing to give access to.

ecfr.gov used to be a decent source for looking up laws. When looking up the anti spam laws, the linked page is littered with links to an access-restricted Cloudflare site (www.govinfo.gov). The important parts of the law are missing from ecfr.gov. It’s common for various states to have this mom-pop shop competency level, but tragic and embarrassing that the US feds lack competency to the point of Cloudflare-dependency.

Often Cornell University publishes federal law and mitigates the embarrassment to some extent. But when looking up the CAN-SPAM law at Cornell, the Cornell law site redirects to another access-restricted Cloudflare site (www.gpo.gov).

There needs to be a fundamental high-level that requires all laws to be accessible to all people, not just people who Cloudflare is willing to give access to.

0

The UN plans to create a “Global Digital Compact” (the same UN that blocks Tor users from accessing the text of human rights law)

preview

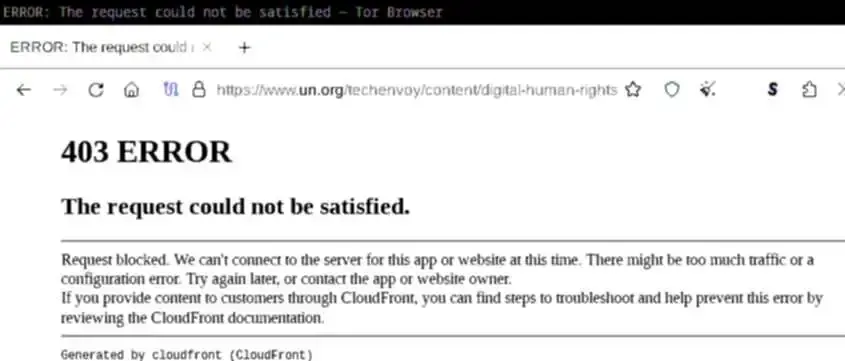
Yikes. As some Tor users may know, the UN drafted the Unified Declaration of Human Rights, which in principle calls for privacy respect and inclusion. That same UN blocks the Tor community from their website. Indeed, being denied access to the text that embodies our human rights is rich in irony.

Well that same UN plans to create a “Global Digital Compact” to protect digital human rights. It’s a good idea, but wow, they just don’t have their shit together. I have so little confidence that they can grasp the problems they are hoping to solve. Cloudflare probably isn’t the least bit worried. Competence prevailing, Cloudflare should be worried, theoretically, but the UN doesn’t have the competence to even know who Cloudflare is.

Yikes. As some Tor users may know, the UN drafted the Unified Declaration of Human Rights, which in principle calls for privacy respect and inclusion. That same UN blocks the Tor community from their website. Indeed, being denied access to the text that embodies our human rights is rich in irony.

Well that same UN plans to create a “Global Digital Compact” to protect digital human rights. It’s a good idea, but wow, they just don’t have their shit together. I have so little confidence that they can grasp the problems they are hoping to solve. Cloudflare probably isn’t the least bit worried. Competence prevailing, Cloudflare should be worried, theoretically, but the UN doesn’t have the competence to even know who Cloudflare is.

0

How to unclutter your Lemmy search results by filtering out exclusive centralised nodes (like Lemmy.World)

preview

One quite annoying Lemmy behaviour is when you search for a community that has many results spanning multiple screens (e.g. query “software”), the list is largely clusterfucked with crappy centralised instances that go against the #fedi philosophy (e.g. #lemmyWorld, #ShItjustWorks, #lemmyCa, #LemmEE, #LemmyZip, #programmingDev, etc).

I discovered a fix: ctrl-rt-click on every community in the list to open each in a tab. Then click “block community”, then repeat the search. It works the way it should: blocked communities are excluded from search results.

Wish I realised that sooner… would have saved me some effort and frustration in trying to search only for communities in the decentralised free world.

One quite annoying Lemmy behaviour is when you search for a community that has many results spanning multiple screens (e.g. query “software”), the list is largely clusterfucked with crappy centralised instances that go against the #fedi philosophy (e.g. #lemmyWorld, #ShItjustWorks, #lemmyCa, #LemmEE, #LemmyZip, #programmingDev, etc).

I discovered a fix: ctrl-rt-click on every community in the list to open each in a tab. Then click “block community”, then repeat the search. It works the way it should: blocked communities are excluded from search results.

Wish I realised that sooner… would have saved me some effort and frustration in trying to search only for communities in the decentralised free world.

0

wanted: a lemmy community that analyzes your post’s URL for inclusivity - robotic and manual

preview

The problem:

Most #fedi authors post links with no idea if the hosting server discriminates against people, or who. The consequence is that the fedi is muddied with references to exclusive venues that do not treat people equally, which wastes the time of readers who are impacted by discrimination. A variety of walled gardens pollute our threadiverse experience. So how can we remedy this?

Proposed fix:

Suppose we create a community and designate it as a testing area which welcomes bots. So e.g. I post something in the test community, and a bot that is paywall-aware replies yes or no whether the link is paywall-free. A bot that is Cloudflare-aware does the same. A regional bot, such as a bot in Poland can check that Polish IP addresses can reach the URL and make noise if the website blocks Poland. Etc. It need not be just bots… someone in some oppressed region might manually attempt to visit links and report access problems. We would certainly like a bot in a GDPR region to test whether access is refused on the basis of a data controller’s unwillingness to respect GDPR rules. The OONI project could have a bot that reports anything interesting in their database.

There could also be anti-enshitification bots, which point out things like cookie walls.

There are bots that find better links to replace Cloudflare links. Those bots could help direct authors to better URLs to share.

There could be a TL-DR bot that replies with a summary or even the full text, so an author can decide before posting in the target community whether to omit a shitty link and just post the content.


(update) It’s worth noting that for Mastodon there an ad hoc tool. If you follow @mg@101010.pl, that bot will follow you back and analyze every URL you share for whether it is Cloudflared. If yes, it will DM you with alternative URLs.

Note that the mitigator bot is quite loose it its judgement. If the host is not Cloudflared but another host on the same domain is Cloudflared, it is treated as a positive because it’s assumed that when you visit the host it will link to other hosts on the same domain.

The problem:

Most #fedi authors post links with no idea if the hosting server discriminates against people, or who. The consequence is that the fedi is muddied with references to exclusive venues that do not treat people equally, which wastes the time of readers who are impacted by discrimination. A variety of walled gardens pollute our threadiverse experience. So how can we remedy this?

Proposed fix:

Suppose we create a community and designate it as a testing area which welcomes bots. So e.g. I post something in the test community, and a bot that is paywall-aware replies yes or no whether the link is paywall-free. A bot that is Cloudflare-aware does the same. A regional bot, such as a bot in Poland can check that Polish IP addresses can reach the URL and make noise if the website blocks Poland. Etc. It need not be just bots… someone in some oppressed region might manually attempt to visit links and report access problems. We would certainly like a bot in a GDPR region to test whether access is refused on the basis of a data controller’s unwillingness to respect GDPR rules. The OONI project could have a bot that reports anything interesting in their database.

There could also be anti-enshitification bots, which point out things like cookie walls.

There are bots that find better links to replace Cloudflare links. Those bots could help direct authors to better URLs to share.

There could be a TL-DR bot that replies with a summary or even the full text, so an author can decide before posting in the target community whether to omit a shitty link and just post the content.


(update) It’s worth noting that for Mastodon there an ad hoc tool. If you follow @mg@101010.pl, that bot will follow you back and analyze every URL you share for whether it is Cloudflared. If yes, it will DM you with alternative URLs.

Note that the mitigator bot is quite loose it its judgement. If the host is not Cloudflared but another host on the same domain is Cloudflared, it is treated as a positive because it’s assumed that when you visit the host it will link to other hosts on the same domain.

0

How the Belgian ecolo party (French green) supports digital inclusion, free software, public $ → public code & right to repair

preview

The linked¹ #gemini article is the political platform of the French green party in Belguim w.r.t. digital rights. It was translated from French.

I’m overall impressed enough to vote for them. But I do have some concerns:

“At the Belgian level, we propose to establish a legal guarantee of 5 years for new electronic devices.”

Yikes, waaay too short. Needs to be at least 10 years. But it helps that they advocate FOSS:

“Generalize the ability to use free software on all devices to decrease software obsolescence.”

Though this statement is far too vague. If a maker of hardware with proprietary non-free software only gives 5 years of support, there needs to be a legal obligation that they port FOSS to the device at the end of the warranty. This is missing in the green party’s plan.

A lot of other things are missing in their plan, but generally their principles are sensible.

¹ (edit) actually it cannot be linked using the URL field due to a #LemmyBug. But at least it was linkable in the msg body.

The linked¹ #gemini article is the political platform of the French green party in Belguim w.r.t. digital rights. It was translated from French.

I’m overall impressed enough to vote for them. But I do have some concerns:

“At the Belgian level, we propose to establish a legal guarantee of 5 years for new electronic devices.”

Yikes, waaay too short. Needs to be at least 10 years. But it helps that they advocate FOSS:

“Generalize the ability to use free software on all devices to decrease software obsolescence.”

Though this statement is far too vague. If a maker of hardware with proprietary non-free software only gives 5 years of support, there needs to be a legal obligation that they port FOSS to the device at the end of the warranty. This is missing in the green party’s plan.

A lot of other things are missing in their plan, but generally their principles are sensible.

¹ (edit) actually it cannot be linked using the URL field due to a #LemmyBug. But at least it was linkable in the msg body.

0

Did Mastodon quit shielding people blocked by Cloudflare? Why did the error code change to 404?

preview

Mastodon used to show people the mirrored version of federated content which shielded users from Cloudflare’s discriminatory blockade. But something apparently changed. If I try to visit this mirror of a mastodonapp.uk status on layer8.space:

layer8.space/…/112387605497275701

it redirects to:

mastodonapp.uk/@tmmj/112387605489133663

which is apparently a shitty Cloudflare node that deceives us into thinking the account does not exist. If you are logged into the mirrored node, then it does not redirect and you can see the content. Of course, only if you have an account on the mirror which means anonymous viewing is no longer possible.

If I want to share that layer8.space link with other people, it would be an injustice to share the mastodonapp.uk link because it’s in a walled garden that excludes people. It would be like sharing a Facebook link with an audience that includes people outside of Facebook. So naturally I would share the layer8.space version because layer8.space allows all people to visit. But now this is impossible. Cloudflare’s stranglehold of control has been increased by this Mastodon move.

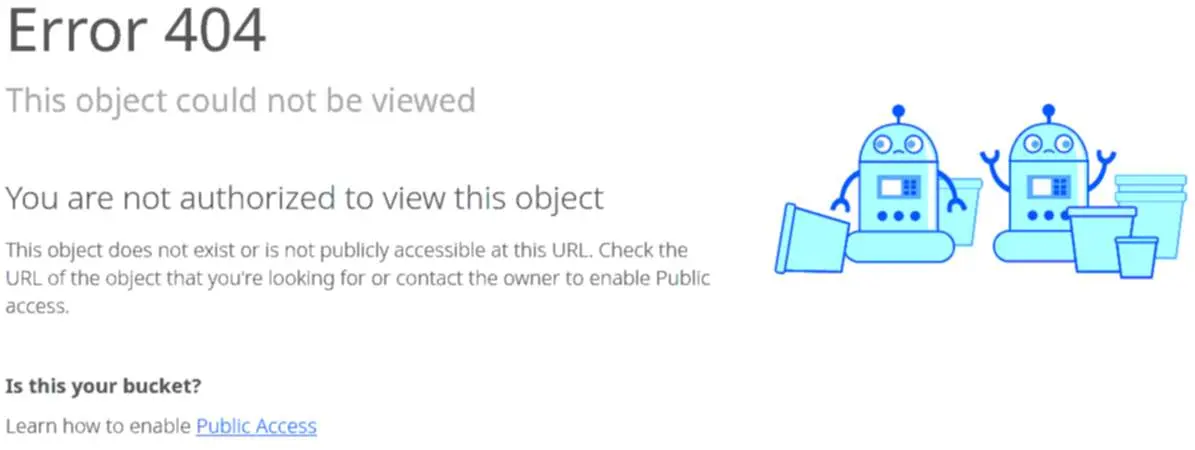
Worse, Cloudflare has started pushing error code 404, not 403. So CF is misrepresenting the error to suggest that the page does not exist. Cloudflare has carte blanche in fucking up the web. A 404 error is supposed to inform users that an object is not found, not that they are not authorised to access it.

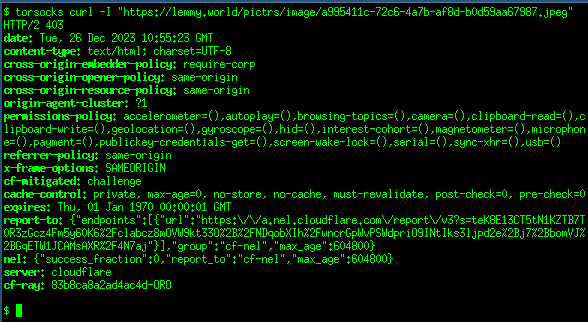
The attached image is what Cloudflare-excluded people see when trying to visit this image:

files.mastodonapp.uk/…/f4442c8789ad52c2.png

Mastodon used to show people the mirrored version of federated content which shielded users from Cloudflare’s discriminatory blockade. But something apparently changed. If I try to visit this mirror of a mastodonapp.uk status on layer8.space:

layer8.space/…/112387605497275701

it redirects to:

mastodonapp.uk/@tmmj/112387605489133663

which is apparently a shitty Cloudflare node that deceives us into thinking the account does not exist. If you are logged into the mirrored node, then it does not redirect and you can see the content. Of course, only if you have an account on the mirror which means anonymous viewing is no longer possible.

If I want to share that layer8.space link with other people, it would be an injustice to share the mastodonapp.uk link because it’s in a walled garden that excludes people. It would be like sharing a Facebook link with an audience that includes people outside of Facebook. So naturally I would share the layer8.space version because layer8.space allows all people to visit. But now this is impossible. Cloudflare’s stranglehold of control has been increased by this Mastodon move.

Worse, Cloudflare has started pushing error code 404, not 403. So CF is misrepresenting the error to suggest that the page does not exist. Cloudflare has carte blanche in fucking up the web. A 404 error is supposed to inform users that an object is not found, not that they are not authorised to access it.

The attached image is what Cloudflare-excluded people see when trying to visit this image:

files.mastodonapp.uk/…/f4442c8789ad52c2.png

0

Images from Cloudflared Lemmy instances are blocked to everyone who CF blocks -- no mirroring despite federation

preview

When an image is posted by someone on a Cloudflared instance like the following:

the image is inaccessible to all demographics of people who Cloudflare discriminates against because images are not mirrored to federated nodes.

We expect corporations to not give a shit about marginising people who are not profitable enough to care about. But when naive asshole users outnumber progressive egalitarians, it highlights a problem with the fedi, which still lacks the tooling needed to keep oppression at bay.

The six listed nodes above effectively host the AOL users of our time. Lacking the sophistication needed to detect and grasp situations of eroded digital rights with a degree of blindness and lack of concern for centralised corporate control.

Suggestions needed for Lemmy nodes that are defederated from the above listed six.

When an image is posted by someone on a Cloudflared instance like the following:

the image is inaccessible to all demographics of people who Cloudflare discriminates against because images are not mirrored to federated nodes.

We expect corporations to not give a shit about marginising people who are not profitable enough to care about. But when naive asshole users outnumber progressive egalitarians, it highlights a problem with the fedi, which still lacks the tooling needed to keep oppression at bay.

The six listed nodes above effectively host the AOL users of our time. Lacking the sophistication needed to detect and grasp situations of eroded digital rights with a degree of blindness and lack of concern for centralised corporate control.

Suggestions needed for Lemmy nodes that are defederated from the above listed six.

0

Some Belgian political parties blocking people from access to election info based on their network

preview

cross-posted from: sopuli.xyz/post/11709471

Many political parties are allowing Cloudflare to block some demographics of voters from seeing election info on their own candidates. These political parties are running exclusive websites:

  • PS/Vooruit (Socialist / Parti Socialiste [fr/nl])
  • Défi (previously part of the MR, now more at the center [fr])
  • CD & V (center / Christen Democratisch en Vlaams [nl])
  • Groen (Green Party [nl])
  • Open VLD (liberal [nl])

Effectively they are operating in an anti-democratic fashion. Open and inclusive access to election info is paramount to democracy.

The political parties who are running inclusive websites are (quite ironically) the right-wing parties. And funnily enough, some of the right-wing parties actually have an English version of their website as well. This defies their historic reputation as being relatively xenophobic. If voting purely on the basis of digital rights and digital inclusion fostered by their website implementation, the right-wingers are the clear winners here.

Voting left entails supporting parties that suppress election info from some demographics of people. Voting right is a non-starter on general principle (e.g. climate denial). Voting is mandatory but there is said to be a “none of the above” option.

(edit) OTOH, the French green party (ecolo.be) has an open website. Perhaps that’s a decent way to vote.

cross-posted from: sopuli.xyz/post/11709471

Many political parties are allowing Cloudflare to block some demographics of voters from seeing election info on their own candidates. These political parties are running exclusive websites:

  • PS/Vooruit (Socialist / Parti Socialiste [fr/nl])
  • Défi (previously part of the MR, now more at the center [fr])
  • CD & V (center / Christen Democratisch en Vlaams [nl])
  • Groen (Green Party [nl])
  • Open VLD (liberal [nl])

Effectively they are operating in an anti-democratic fashion. Open and inclusive access to election info is paramount to democracy.

The political parties who are running inclusive websites are (quite ironically) the right-wing parties. And funnily enough, some of the right-wing parties actually have an English version of their website as well. This defies their historic reputation as being relatively xenophobic. If voting purely on the basis of digital rights and digital inclusion fostered by their website implementation, the right-wingers are the clear winners here.

Voting left entails supporting parties that suppress election info from some demographics of people. Voting right is a non-starter on general principle (e.g. climate denial). Voting is mandatory but there is said to be a “none of the above” option.

(edit) OTOH, the French green party (ecolo.be) has an open website. Perhaps that’s a decent way to vote.

0

Transit service forces TLS ver 1.3 to simply agree to ToS in their captive portal, denying access to people with older phones

preview

IMO this is a #netneutrality issue due to lack of access equality. People with old phones are discriminated against.

cross-posted from: infosec.pub/post/11021006

…
TLS-encumbered captive portal (transit service)

A transit service offered wi-fi but the network forcibly redirected me to a captive portal that triggers this error:

net::ERR_SSL_VERSION_OR_CIPHER_MISMATCH

I tried a couple browsers and tried rewriting the https:// scheme as http:// but SSL redirect was forced consistently. The error apparently implies my phone’s browser can’t do TLS 1.3.

It seems like a shitty move for a transit service to require passengers to use TLS 1.3 just to tick a fucking box that says “I agree” (to the terms no one reads anyway). Couple questions:

  • I’m generally in the /protect everything by default/ school of thought. But I cannot get my head around why a captive portal where people just tap “I agree” would warrant disclosure protection that could hinder availability. In reality, I don’t really know what the captive portal at hand requests… maybe it demands people’s phone# or email, in which case it might make sense (though I would object to them collecting that info in a GDPR region in the 1st place).

  • Is there a good reason for a captive portal to require TLS 1.3? It seems either the network provider does not trust their own network, or they’re simply incompetent (assumes everyone runs the latest phones). But if I’m missing something I would like to understand it.

I still have to investigate what limitation my browser has and whether I can update this whilst being trapped on an unrooted Android 5.

Bypass methods

I guess I need to study:

  • ICMP tunnel (slow, but IIUC it’s the least commonly blocked)
  • SSH tunnel
  • others?

Are there any decent FOSS tools that implement the client side of tunnels without needing root? I have openvpn but have not tested to see if that can circumvent captive portals. I’ve only found:

  • MultiVNC - VNC over SSH
  • AVNC - VNC over SSH
  • ConnectBot - Can all traffic be routed over this SSH tunnel, or just a shell session?
  • VX ConnectBot - same as connectBot but expanded

I’m curious if the VNC clients would work but at the same time I’m not keen to bring in the complexity of then having to find a VNC server. Running my own server at home is not an option.

My to-do list of things to tinker with so far:

Legal options

If a supplier advertises Wi-Fi but then they render it dysfunctional by imposing arbitrary tech requirements after consumers have already bought the product/service it was included with (coffee, train/bus/plane fare, etc), then they neglect to support it, doesn’t that constitute false advertising? Guess this is out of scope for the community but I might be ½ tempted to file false advertising claims with consumer protection agencies in some cases.

And when a captive portal demands email or phone number, it would seem to be a GDPR violation. Some public libraries make wi-fi access conditional on sharing a mobile phone number which then entails an SMS verification loop.

IMO this is a #netneutrality issue due to lack of access equality. People with old phones are discriminated against.

cross-posted from: infosec.pub/post/11021006

…
TLS-encumbered captive portal (transit service)

A transit service offered wi-fi but the network forcibly redirected me to a captive portal that triggers this error:

net::ERR_SSL_VERSION_OR_CIPHER_MISMATCH

I tried a couple browsers and tried rewriting the https:// scheme as http:// but SSL redirect was forced consistently. The error apparently implies my phone’s browser can’t do TLS 1.3.

It seems like a shitty move for a transit service to require passengers to use TLS 1.3 just to tick a fucking box that says “I agree” (to the terms no one reads anyway). Couple questions:

  • I’m generally in the /protect everything by default/ school of thought. But I cannot get my head around why a captive portal where people just tap “I agree” would warrant disclosure protection that could hinder availability. In reality, I don’t really know what the captive portal at hand requests… maybe it demands people’s phone# or email, in which case it might make sense (though I would object to them collecting that info in a GDPR region in the 1st place).

  • Is there a good reason for a captive portal to require TLS 1.3? It seems either the network provider does not trust their own network, or they’re simply incompetent (assumes everyone runs the latest phones). But if I’m missing something I would like to understand it.

I still have to investigate what limitation my browser has and whether I can update this whilst being trapped on an unrooted Android 5.

Bypass methods

I guess I need to study:

  • ICMP tunnel (slow, but IIUC it’s the least commonly blocked)
  • SSH tunnel
  • others?

Are there any decent FOSS tools that implement the client side of tunnels without needing root? I have openvpn but have not tested to see if that can circumvent captive portals. I’ve only found:

  • MultiVNC - VNC over SSH
  • AVNC - VNC over SSH
  • ConnectBot - Can all traffic be routed over this SSH tunnel, or just a shell session?
  • VX ConnectBot - same as connectBot but expanded

I’m curious if the VNC clients would work but at the same time I’m not keen to bring in the complexity of then having to find a VNC server. Running my own server at home is not an option.

My to-do list of things to tinker with so far:

Legal options

If a supplier advertises Wi-Fi but then they render it dysfunctional by imposing arbitrary tech requirements after consumers have already bought the product/service it was included with (coffee, train/bus/plane fare, etc), then they neglect to support it, doesn’t that constitute false advertising? Guess this is out of scope for the community but I might be ½ tempted to file false advertising claims with consumer protection agencies in some cases.

And when a captive portal demands email or phone number, it would seem to be a GDPR violation. Some public libraries make wi-fi access conditional on sharing a mobile phone number which then entails an SMS verification loop.

0

The 3 oppressions of walled gardens and Cloudflare’s creation of the largest and most rigidly exclusive walled garden in the world

preview

Some people think Cloudflare is not a “walled garden”. This article goes to a great extent to show not only that Cloudflare is a #walledGarden, but it’s actually more of a walled garden than the well known ones (Facebook & Google).

Some people think Cloudflare is not a “walled garden”. This article goes to a great extent to show not only that Cloudflare is a #walledGarden, but it’s actually more of a walled garden than the well known ones (Facebook & Google).

0

Google Cache is being killed off

Engadget Google Search is losing its &apos;cached&apos; web page feature - Engadget www.engadget.com
preview

(⚠ Enshitification warning: The linked article has a cookie wall; just click “reject” and the article appears)

Google is ending the public access to the cache of sites it indexes. AFAICT, these are the consequences:

  • People getting different treatment due to their geographic location will lose the cache they used as a remedy for access inclusion.
  • People getting different treatment due to having a defensive browser will lose access.
  • The 12ft.io service which serves those who suffer access inequality will be rendered useless.
  • Google will continue to include paywalls in search results, but now consumers of Google search results will be led to a dead-end.
  • The #InternetArchive #WaybackMachine will take on the full burden of global archival.
  • Consumers will lose a very useful tool for circumventing web enshitification.

Websites treat the Google crawler like a 1st class citizen. Paywalls give Google unpaid junk-free access. Then Google search results direct people to a website that treats humans differently (worse). So Google users are led to sites they cannot access. The heart of the problem is access inequality. Google effectively serves to refer people to sites that are not publicly accessible.

I do not want to see search results I cannot access. Google cache was the equalizer that neutralizes that problem. Now that problem is back in our face.

(⚠ Enshitification warning: The linked article has a cookie wall; just click “reject” and the article appears)

Google is ending the public access to the cache of sites it indexes. AFAICT, these are the consequences:

  • People getting different treatment due to their geographic location will lose the cache they used as a remedy for access inclusion.
  • People getting different treatment due to having a defensive browser will lose access.
  • The 12ft.io service which serves those who suffer access inequality will be rendered useless.
  • Google will continue to include paywalls in search results, but now consumers of Google search results will be led to a dead-end.
  • The #InternetArchive #WaybackMachine will take on the full burden of global archival.
  • Consumers will lose a very useful tool for circumventing web enshitification.

Websites treat the Google crawler like a 1st class citizen. Paywalls give Google unpaid junk-free access. Then Google search results direct people to a website that treats humans differently (worse). So Google users are led to sites they cannot access. The heart of the problem is access inequality. Google effectively serves to refer people to sites that are not publicly accessible.

I do not want to see search results I cannot access. Google cache was the equalizer that neutralizes that problem. Now that problem is back in our face.

0

This practice of pushing an interactive map and giving no textual addresses

preview

There is hardly any discussion on this trending variety of web enshitification where a website needs to give physical locations to people. Many web devs are starting to spotlight their profound incompetence in accomplishing this very simple task. They throw up an interactive map which requires the full utilization of fancy GUI browser frills with 3rd party js enabled, which excludes all but those who “chase the shiny”. A 1990s high schooler could handle this better in plain HTML.

Doesn’t this screw over blind people? How does a screen reader handle a map?

My hardened low-bandwidth browser can’t handle this absurd degree of putting fancy above access equality. When this shit happens on a vendor’s website and I’m trying to locate them to give them business, the answer is easy: they can fuck off and lose my business. But it’s sad when a government does it and the information has medical relevance.

There is hardly any discussion on this trending variety of web enshitification where a website needs to give physical locations to people. Many web devs are starting to spotlight their profound incompetence in accomplishing this very simple task. They throw up an interactive map which requires the full utilization of fancy GUI browser frills with 3rd party js enabled, which excludes all but those who “chase the shiny”. A 1990s high schooler could handle this better in plain HTML.

Doesn’t this screw over blind people? How does a screen reader handle a map?

My hardened low-bandwidth browser can’t handle this absurd degree of putting fancy above access equality. When this shit happens on a vendor’s website and I’m trying to locate them to give them business, the answer is easy: they can fuck off and lose my business. But it’s sad when a government does it and the information has medical relevance.

0

Cloudflare’s attack on Tor users blocks ability to see an image size before fetching

preview

This is what it looks like when a Tor user attempts to fetch a file or even just obtain the size of a file from a Cloudflared resource like #LemmyWorld.

This is what it looks like when a Tor user attempts to fetch a file or even just obtain the size of a file from a Cloudflared resource like #LemmyWorld.

0

Road traffic information is encrypted in Norway, Germany, Sweden, Australia, Finland, and Italy. But it’s freely open access in France and Estonia

preview

TMC is a broadcast of traffic information which usually uses an FM signal. These protectionist countries encrypt the data:

That’s fucked up, is it not? Shouldn’t publicly funded information be open to the public? These countries provide unencrypted #TMC data:

  • Estonia
  • France

#openData

TMC is a broadcast of traffic information which usually uses an FM signal. These protectionist countries encrypt the data:

That’s fucked up, is it not? Shouldn’t publicly funded information be open to the public? These countries provide unencrypted #TMC data:

  • Estonia
  • France

#openData

0

Tactic needed to counter all communities living on lemmy.world and get more of the threadiverse into the free world

preview

cross-posted from: lemmy.dbzer0.com/post/6251633

LemmyWorld is a terrible place for communities to exist. Rationale:

  • Lemmy World is centralized by disproportionately high user count
  • Lemmy World is centralized by #Cloudflare
  • Lemmy World is exclusive because Cloudflare is exclusive

It’s antithetical to the #decentralized #fediverse for one node to be positioned so centrally and revolting that it all happens on the network of a privacy-offender (CF). If #Lemmy World were to go down, a huge number of communities would go with it.

So what’s the solution?

Individual action protocol:

  1. Never post an original thread to #LemmyWorld. Find a free world non-Cloudflare decentralized instance to start new threads. Create a new community if needed.
  2. Wait for some engagement, ideally responses.
  3. Cross-post to the relevant Lemmy World community (if user poaching is needed).

This gets some exposure to the content while also tipping off readers of the LW community of alternative venues. LW readers are lazy pragmatists so they will naturally reply in the LW thread rather than the original thread. Hence step 2. If an LW user wants to interact with another responder they must do so on the more free venue. Step 3 can be omitted in situations where the free-world community is populated well enough. If /everything/ gets cross-posted to LW then there is no incentive for people to leave LW.

Better ideas? Would this work as a collective movement?

cross-posted from: lemmy.dbzer0.com/post/6251633

LemmyWorld is a terrible place for communities to exist. Rationale:

  • Lemmy World is centralized by disproportionately high user count
  • Lemmy World is centralized by #Cloudflare
  • Lemmy World is exclusive because Cloudflare is exclusive

It’s antithetical to the #decentralized #fediverse for one node to be positioned so centrally and revolting that it all happens on the network of a privacy-offender (CF). If #Lemmy World were to go down, a huge number of communities would go with it.

So what’s the solution?

Individual action protocol:

  1. Never post an original thread to #LemmyWorld. Find a free world non-Cloudflare decentralized instance to start new threads. Create a new community if needed.
  2. Wait for some engagement, ideally responses.
  3. Cross-post to the relevant Lemmy World community (if user poaching is needed).

This gets some exposure to the content while also tipping off readers of the LW community of alternative venues. LW readers are lazy pragmatists so they will naturally reply in the LW thread rather than the original thread. Hence step 2. If an LW user wants to interact with another responder they must do so on the more free venue. Step 3 can be omitted in situations where the free-world community is populated well enough. If /everything/ gets cross-posted to LW then there is no incentive for people to leave LW.

Better ideas? Would this work as a collective movement?

0

Resource needed to evaluate inclusivity of websites

preview

Before sharing a link I would like to determine whether the website excludes people from access, and who is excluded. I can test for myself whether the Tor community is excluded but what about:

  • VPNs
  • i2p
  • public libraries
  • #cgNAT-issued IP addresses (often from impoverished regions)
  • various geographical regions
  • particular browsers (e.g. lynx, w3m, non-chrome-based…)

for example? I cannot check all those means of access. If a website is implementing some form of digital exclusion, I would like to ensure that I am not helping the exclusive website gain visitors.

#askFedi #netneutrality

Before sharing a link I would like to determine whether the website excludes people from access, and who is excluded. I can test for myself whether the Tor community is excluded but what about:

  • VPNs
  • i2p
  • public libraries
  • #cgNAT-issued IP addresses (often from impoverished regions)
  • various geographical regions
  • particular browsers (e.g. lynx, w3m, non-chrome-based…)

for example? I cannot check all those means of access. If a website is implementing some form of digital exclusion, I would like to ensure that I am not helping the exclusive website gain visitors.

#askFedi #netneutrality