0

Youtube videos posted in Stop Tech -- can we get a different policy?

preview

Youtube has become a total fucking shitshow. A couple years ago Google ratcheted up its hostility and protectionism against both Invidious and the Tor community. It killed off all the public invideous instances. Some still operate in a crippled state. For example:

slrpnk.net/post/42510917/24379011

When someone posts a link to a Youtube video, we know that person was able to access the video. So that person should use their privilege to share the video. They should download it, then upload it to peertube, and share the peertube link. Otherwise it’s a bit antithetical to the Stop Tech purpose to have links into exclusive walled-gardens.

Youtube has become a total fucking shitshow. A couple years ago Google ratcheted up its hostility and protectionism against both Invidious and the Tor community. It killed off all the public invideous instances. Some still operate in a crippled state. For example:

slrpnk.net/post/42510917/24379011

When someone posts a link to a Youtube video, we know that person was able to access the video. So that person should use their privilege to share the video. They should download it, then upload it to peertube, and share the peertube link. Otherwise it’s a bit antithetical to the Stop Tech purpose to have links into exclusive walled-gardens.

0

frogfind toast?

preview

Frogfind.com was probably a little known search service that was good at filtering out the garbage and gives a lightweight web UX. Now there is some kind of anti-bot check. I pass the check and enter a query, but then that just gives a blank page. Been happening for a few days now. I hope this service isn’t dead.

Frogfind.com was probably a little known search service that was good at filtering out the garbage and gives a lightweight web UX. Now there is some kind of anti-bot check. I pass the check and enter a query, but then that just gives a blank page. Been happening for a few days now. I hope this service isn’t dead.

0

(US) A stock broker gives extra privileges to online customers by withholding some tax disclosures from offline customers

preview

If you download your tax forms from the shitty tor-hostile website of the stock broker, they give you worksheets and extra reports for dividends and FX to use for tax preparation.

Offline customers get nothing, automatically. To get a 1099 in the mail, you must call every year and request it specifically. If you ask for the worksheets and other docs, they refuse. Apparently they only legally have to give you a 1099, so offline people get the bare legal minimum.

I suppose the question is: is it legal that we must call every year to requst the 1099? Shouldn’t a 1099 be sent automatically?

If you download your tax forms from the shitty tor-hostile website of the stock broker, they give you worksheets and extra reports for dividends and FX to use for tax preparation.

Offline customers get nothing, automatically. To get a 1099 in the mail, you must call every year and request it specifically. If you ask for the worksheets and other docs, they refuse. Apparently they only legally have to give you a 1099, so offline people get the bare legal minimum.

I suppose the question is: is it legal that we must call every year to requst the 1099? Shouldn’t a 1099 be sent automatically?

0

Use an app to broadcast your boycott on the dynamic pricing tags in grocery stores

GitHub GitHub - i12bp8/TagTinker: Flipper Zero app for ESL research using IR. All based on https://www.furrtek.org/?a=esl github.com
preview

Suppose you boycott #Unilever because they fight cash as a member of Bill Gates’ “Better than Cash Alliance”. You could use the linked app on a flipper zero to change the price tags of Unilever goods to a message like “Boycott Unilever”, for example.

Suppose you boycott #Unilever because they fight cash as a member of Bill Gates’ “Better than Cash Alliance”. You could use the linked app on a flipper zero to change the price tags of Unilever goods to a message like “Boycott Unilever”, for example.

0

Use an app to broadcast your boycott on the dynamic pricing tags in grocery stores

GitHub GitHub - i12bp8/TagTinker: Flipper Zero app for ESL research using IR. All based on https://www.furrtek.org/?a=esl github.com
preview

Suppose you boycott #Unilever because they fight cash as a member of Bill Gates’ “Better than Cash Alliance”. You could use the linked app on a flipper zero to change the price tags of Unilever goods to “Boycott Unilever”, for example.

Suppose you boycott #Unilever because they fight cash as a member of Bill Gates’ “Better than Cash Alliance”. You could use the linked app on a flipper zero to change the price tags of Unilever goods to “Boycott Unilever”, for example.

0

Printing checks with regular toner (not MICR) -- anyone experienced w/this?

preview

I intend to print some checks and cannot do MICR toner. Since archive.org is down right now, about half the Internet is down for me because so many enshitified websites are access restricted and I rely heavily on archive.org.

What is the risk for submitting a non-MICR check to pay a credit card bill? Slower processing, sure, fine with me. However, this page mentions returned check fees. My knee-jerk thought is: WTF, it would be a valid check, so would some lazy motherfucker whose check reader has no optical cabability really be able to legally justify hitting me with a returned check fee as a consequence of them being too lazy to do a manual entry?

The law apparently makes it clear that a non-MICR check would not comply with ANSI standards. Fair enough; but really the question is whether a non-standard check can be treated as invalid to the point of levying penalties when in fact the information presented is both valid and usable? It’s all down to what lazy motherfuckers will do with their discretion, correct?

I happen to know that the credit card company does not process checks like normal. They do an ARC conversion. They use the info on the check to generate an “electronic check” and then they pull the money electronically. They probably do that to move the money faster. So is it safe to say there is no chance of my bank rejecting the check – that the only possible rejection would be by the credit card company?

A credit card company would obviously be processing copious checks. So it stands to reason that they would use a modern reader that is both magnetic and optical. So IMO it should work. But they could still be dicks. The reader could read the info optically but send a “dodgy check” flag due to the lack of magnetism and maybe they are just happy to have an excuse to collect an arbitrary penalty.

Anyone test this?

I intend to print some checks and cannot do MICR toner. Since archive.org is down right now, about half the Internet is down for me because so many enshitified websites are access restricted and I rely heavily on archive.org.

What is the risk for submitting a non-MICR check to pay a credit card bill? Slower processing, sure, fine with me. However, this page mentions returned check fees. My knee-jerk thought is: WTF, it would be a valid check, so would some lazy motherfucker whose check reader has no optical cabability really be able to legally justify hitting me with a returned check fee as a consequence of them being too lazy to do a manual entry?

The law apparently makes it clear that a non-MICR check would not comply with ANSI standards. Fair enough; but really the question is whether a non-standard check can be treated as invalid to the point of levying penalties when in fact the information presented is both valid and usable? It’s all down to what lazy motherfuckers will do with their discretion, correct?

I happen to know that the credit card company does not process checks like normal. They do an ARC conversion. They use the info on the check to generate an “electronic check” and then they pull the money electronically. They probably do that to move the money faster. So is it safe to say there is no chance of my bank rejecting the check – that the only possible rejection would be by the credit card company?

A credit card company would obviously be processing copious checks. So it stands to reason that they would use a modern reader that is both magnetic and optical. So IMO it should work. But they could still be dicks. The reader could read the info optically but send a “dodgy check” flag due to the lack of magnetism and maybe they are just happy to have an excuse to collect an arbitrary penalty.

Anyone test this?

0

discuss.tchncs.de under attack

preview

Not sure of the full scope of the attack but I routinely fetch the lemmyverse dataset and see that over the past two days someone has created over a hundred bogus communities at discuss.tchncs.de.

(update) now looking at the timestamps, there is a non-uniform time between community creations often ranging from 2—10min. So it does not look automated. Maybe some pissed off kid manually did this? Or maybe someone who is just testing their attack script. Here is a sample:

…
exhibit56355@discuss.tchncs.de     2026-08-05T23:56:07.111126Z
exhibit74575@discuss.tchncs.de     2026-08-05T23:56:53.499897Z
montage49848@discuss.tchncs.de     2026-08-05T23:57:25.442903Z
gallery78147@discuss.tchncs.de     2026-08-05T23:59:49.329487Z
archive68564@discuss.tchncs.de     2026-08-06T00:09:18.605958Z
portfolio24010@discuss.tchncs.de   2026-08-06T00:12:13.200293Z
archive57120@discuss.tchncs.de     2026-08-06T00:12:26.712641Z
stills64667@discuss.tchncs.de      2026-08-06T00:18:44.101341Z
curated97085@discuss.tchncs.de     2026-08-06T00:20:27.982432Z
montage57326@discuss.tchncs.de     2026-08-06T00:25:18.222482Z
visuals79552@discuss.tchncs.de     2026-08-06T00:26:32.490046Z
portfolio82493@discuss.tchncs.de   2026-08-06T00:31:00.950359Z
curated50274@discuss.tchncs.de     2026-08-06T00:32:35.967834Z
archive62242@discuss.tchncs.de     2026-08-06T00:33:19.683080Z
archive95840@discuss.tchncs.de     2026-08-06T00:37:49.730539Z
visuals27150@discuss.tchncs.de     2026-08-06T00:40:28.852659Z
visuals37605@discuss.tchncs.de     2026-08-06T00:43:18.418426Z
curated85385@discuss.tchncs.de     2026-08-06T00:47:10.542885Z
visuals85531@discuss.tchncs.de     2026-08-06T00:49:14.857853Z
collection63981@discuss.tchncs.de  2026-08-06T00:51:42.154544Z
collection44977@discuss.tchncs.de  2026-08-06T00:53:34.997045Z
portfolio58030@discuss.tchncs.de   2026-08-06T01:02:16.596242Z
archive79163@discuss.tchncs.de     2026-08-06T01:04:15.370817Z
frames63631@discuss.tchncs.de      2026-08-06T01:11:01.770464Z
portfolio93081@discuss.tchncs.de   2026-08-06T01:23:46.632166Z
…

Maybe it’s not an attack per-se but rather a coded way to signal to a botnet.

Not sure of the full scope of the attack but I routinely fetch the lemmyverse dataset and see that over the past two days someone has created over a hundred bogus communities at discuss.tchncs.de.

(update) now looking at the timestamps, there is a non-uniform time between community creations often ranging from 2—10min. So it does not look automated. Maybe some pissed off kid manually did this? Or maybe someone who is just testing their attack script. Here is a sample:

…
exhibit56355@discuss.tchncs.de     2026-08-05T23:56:07.111126Z
exhibit74575@discuss.tchncs.de     2026-08-05T23:56:53.499897Z
montage49848@discuss.tchncs.de     2026-08-05T23:57:25.442903Z
gallery78147@discuss.tchncs.de     2026-08-05T23:59:49.329487Z
archive68564@discuss.tchncs.de     2026-08-06T00:09:18.605958Z
portfolio24010@discuss.tchncs.de   2026-08-06T00:12:13.200293Z
archive57120@discuss.tchncs.de     2026-08-06T00:12:26.712641Z
stills64667@discuss.tchncs.de      2026-08-06T00:18:44.101341Z
curated97085@discuss.tchncs.de     2026-08-06T00:20:27.982432Z
montage57326@discuss.tchncs.de     2026-08-06T00:25:18.222482Z
visuals79552@discuss.tchncs.de     2026-08-06T00:26:32.490046Z
portfolio82493@discuss.tchncs.de   2026-08-06T00:31:00.950359Z
curated50274@discuss.tchncs.de     2026-08-06T00:32:35.967834Z
archive62242@discuss.tchncs.de     2026-08-06T00:33:19.683080Z
archive95840@discuss.tchncs.de     2026-08-06T00:37:49.730539Z
visuals27150@discuss.tchncs.de     2026-08-06T00:40:28.852659Z
visuals37605@discuss.tchncs.de     2026-08-06T00:43:18.418426Z
curated85385@discuss.tchncs.de     2026-08-06T00:47:10.542885Z
visuals85531@discuss.tchncs.de     2026-08-06T00:49:14.857853Z
collection63981@discuss.tchncs.de  2026-08-06T00:51:42.154544Z
collection44977@discuss.tchncs.de  2026-08-06T00:53:34.997045Z
portfolio58030@discuss.tchncs.de   2026-08-06T01:02:16.596242Z
archive79163@discuss.tchncs.de     2026-08-06T01:04:15.370817Z
frames63631@discuss.tchncs.de      2026-08-06T01:11:01.770464Z
portfolio93081@discuss.tchncs.de   2026-08-06T01:23:46.632166Z
…

Maybe it’s not an attack per-se but rather a coded way to signal to a botnet.

0

Cannot buy tickets for a Bob Dylan concert without cloud access

preview

cross-posted from: slrpnk.net/post/40597815

WTF Bob Dylan? A friend who is offline is blocked from buying tickets to Bob Dylan in Antwerp, Belgium. The concert is effectively exclusively for online people. Most likely cash payers must fuck off.

It’s exactly the kind of shit Bob Dylan should be bitching about in his songs. WTF, Bob Dylan?

cross-posted from: slrpnk.net/post/40597815

WTF Bob Dylan? A friend who is offline is blocked from buying tickets to Bob Dylan in Antwerp, Belgium. The concert is effectively exclusively for online people. Most likely cash payers must fuck off.

It’s exactly the kind of shit Bob Dylan should be bitching about in his songs. WTF, Bob Dylan?

0

hardware.watch dead, or tor-hostile

preview

I could never reach hardware.watch. Not sure if they block Tor or if they died before I discovered them. Lemmyverse shows them as having high uptime:

lemmyverse.net/instance/hardware.watch

So perhaps they are just tor-hostile.

(edit) I see recent fedi-cached posts… so I guess the node is just tor-hostile.

I could never reach hardware.watch. Not sure if they block Tor or if they died before I discovered them. Lemmyverse shows them as having high uptime:

lemmyverse.net/instance/hardware.watch

So perhaps they are just tor-hostile.

(edit) I see recent fedi-cached posts… so I guess the node is just tor-hostile.

0

search.fabiomanganiello.com → 504 gateway time-out (update: it’s back online)

preview

My favorite searx instance is down. I like this instance because it has a lot of built-in alternative front-ends. E.g. it gives Invidious links in place of Youtube links and more importantly stackexchange links.

My favorite searx instance is down. I like this instance because it has a lot of built-in alternative front-ends. E.g. it gives Invidious links in place of Youtube links and more importantly stackexchange links.

0

Train hopping only a thing in the US, or Europe too? (A: yes, Europe too but less common.. must dodge A/C power lines)

NPR It's dangerous, illegal and uncomfortable — but train hoppers ride the rails anyway www.npr.org
preview

cross-posted from: slrpnk.net/post/36305825

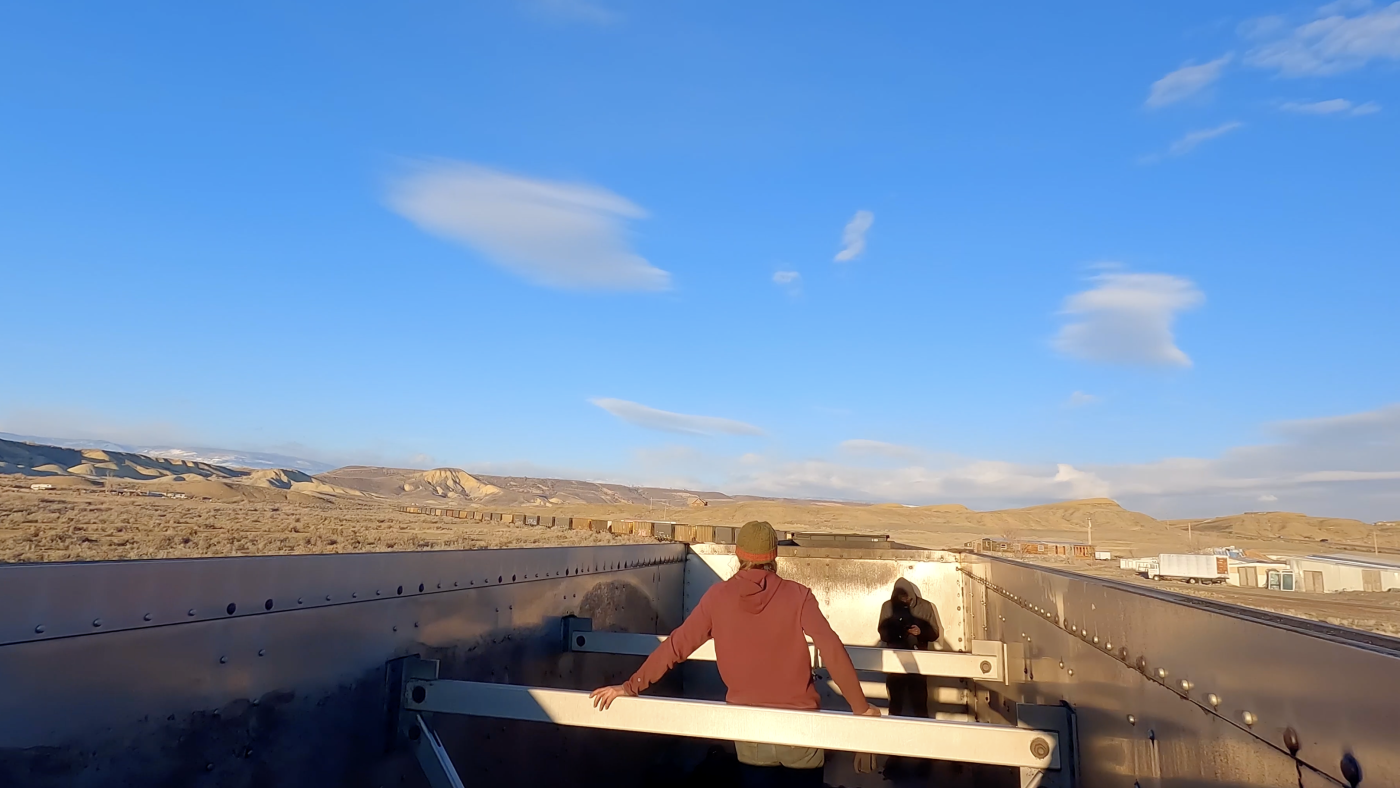
Train hopping is still a thing in the US, I suspect because freight trains are slow.

But what about Europe? Even the slow trains are fast. Although I say that only having seen passenger trains. Are there freight trains that are slow enough? What about controls? The article mentions thermal cams being used to spot train hoppers. I might expect Europe’s tendency to push for safety to manifest as rigorous controls.

UPDATE: found this→ hitchwiki.org/en/Train_hopping#Europe


cross-posted from: slrpnk.net/post/36305703

Would like to add this to my lifestyle.

“Working remotely as a software engineer, the 25-year-old spends his free time combing through open source railway data and online forums to determine which trains to take, when they’ll slow or stop, where to hide in wait and what type of train car to jump into.”

cross-posted from: slrpnk.net/post/36305825

Train hopping is still a thing in the US, I suspect because freight trains are slow.

But what about Europe? Even the slow trains are fast. Although I say that only having seen passenger trains. Are there freight trains that are slow enough? What about controls? The article mentions thermal cams being used to spot train hoppers. I might expect Europe’s tendency to push for safety to manifest as rigorous controls.

UPDATE: found this→ hitchwiki.org/en/Train_hopping#Europe


cross-posted from: slrpnk.net/post/36305703

Would like to add this to my lifestyle.

“Working remotely as a software engineer, the 25-year-old spends his free time combing through open source railway data and online forums to determine which trains to take, when they’ll slow or stop, where to hide in wait and what type of train car to jump into.”

0

lemmy.sdf.org is down (update: woah, wtf, still down ~~16 days~~ 1 MONTH later!) UPDATE 2: after 2 months, SDF is back up but logins time-out

preview

announcement:

lemmy.sdf.org/post/40936795

Apparently 9 months of data was lost? Not sure. Looks like a 9 month gap in history.

announcement:

lemmy.sdf.org/post/40936795

Apparently 9 months of data was lost? Not sure. Looks like a 9 month gap in history.

0

Govs are migrating to Matrix in a misguided attempt at tech sovereignty (amid [cough] Cloudflare [cough])

theregister Matrix messaging gaining ground in government IT www.theregister.com
preview

cross-posted from: slrpnk.net/post/33983108

Obviously it’s not smart to switch to a Cloudflare-plagued network like that of Matrix if your goal is to escape US tech giants. For strictly internal use on self-hosted instances, sure. But as soon as a matrix room becomes open public Cloudflare rears its ugly head.

Zulip and SimpleX are probably better options. Certainly IRC is a better option so long as the channel has no Matrix gateway. SimpleX is also free of Cloudflare.

cross-posted from: slrpnk.net/post/33983108

Obviously it’s not smart to switch to a Cloudflare-plagued network like that of Matrix if your goal is to escape US tech giants. For strictly internal use on self-hosted instances, sure. But as soon as a matrix room becomes open public Cloudflare rears its ugly head.

Zulip and SimpleX are probably better options. Certainly IRC is a better option so long as the channel has no Matrix gateway. SimpleX is also free of Cloudflare.

0

Decreasing visibility of physical addresses appearing on websites.. even public/government agencies and human rights NGOs

preview

It’s as if humanity is dying off. They don’t want to see you in person so physical addresses are being withheld from contact pages. I now must dig into the privacy policy or ToS to find an address. It’s really a shitshow because a data protection officer or whoever handles privacy requests could be entirely outsourced to someone who has nothing to do with an org.

It boils down to nannying. They don’t even want to enable people to write snail-mail letters – which is king for escaping enshitification and the digital transformation.

It’s as if humanity is dying off. They don’t want to see you in person so physical addresses are being withheld from contact pages. I now must dig into the privacy policy or ToS to find an address. It’s really a shitshow because a data protection officer or whoever handles privacy requests could be entirely outsourced to someone who has nothing to do with an org.

It boils down to nannying. They don’t even want to enable people to write snail-mail letters – which is king for escaping enshitification and the digital transformation.

0

Fedi platform feature: original post downvotes blocked from those who have not commented or upvoted an existing comment

preview

I’ve not studied the ActivityPub protocol much, and certainly not examined the voting API. My question for those who have:

Is it possible or easy for a platform to suppress downvotes from users who have not first satisfied either of these preconditions:

  • created a comment in the thread being downvoted; OR
  • upvoted a comment in the thread being downvoted

?

And perhaps more complex, cancel the downvotes of cheaters who would circumvent the above policy by making a temporary dummy comment, downvoting, then deleting the dummy.

Voting is a shit-show on Lemmy. I wonder to what extent the ActivityPub API is the culprit or if it’s an implementation specific problem.

I’ve not studied the ActivityPub protocol much, and certainly not examined the voting API. My question for those who have:

Is it possible or easy for a platform to suppress downvotes from users who have not first satisfied either of these preconditions:

  • created a comment in the thread being downvoted; OR
  • upvoted a comment in the thread being downvoted

?

And perhaps more complex, cancel the downvotes of cheaters who would circumvent the above policy by making a temporary dummy comment, downvoting, then deleting the dummy.

Voting is a shit-show on Lemmy. I wonder to what extent the ActivityPub API is the culprit or if it’s an implementation specific problem.

0

Why is Lemmy so network-heavy?

preview

I have images disabled in my browser and also in my profile. So I should only be getting text when browsing a Lemmy server, and it should be compressed because TLS is in play and compression is usually/conventionally done before encryption (or so I thought). Animated GIFs are immune to my settings but I did not notice any.

After a couple(?) hours of activity involving mostly reading and writing and not a crazy amount of searching or jumping around, my session consumed ~65mb. That seems like a lot for just text. Hi-res binary images are often around 1 mb, so it seems a bit off that my text-only session would use the equivalent of 65 hi-res pics.

To give an idea of sizes, I have a text file holding 260 of my posts going back several months. The uncompressed size is 558k. It seems very unlikely that I would have read that many posts/comments in 2 hours. So 65mb is at least 2 orders of magnitude more bandwidth consumption than I would expect.

With probably 95+% of fedi ppl on quasi unlimited broadband, probably no one pays attention to this.

Any theories? I had a few different accounts open from different nodes. So I wonder if the JavaScript client code is where all the fat is, which must be fetched upon every single login. Would the stock Lemmy client code be as big as 10mb compressed? A few nodes have some kind of anti-bot thing that runs. I wonder if that has some network fat.

I have images disabled in my browser and also in my profile. So I should only be getting text when browsing a Lemmy server, and it should be compressed because TLS is in play and compression is usually/conventionally done before encryption (or so I thought). Animated GIFs are immune to my settings but I did not notice any.

After a couple(?) hours of activity involving mostly reading and writing and not a crazy amount of searching or jumping around, my session consumed ~65mb. That seems like a lot for just text. Hi-res binary images are often around 1 mb, so it seems a bit off that my text-only session would use the equivalent of 65 hi-res pics.

To give an idea of sizes, I have a text file holding 260 of my posts going back several months. The uncompressed size is 558k. It seems very unlikely that I would have read that many posts/comments in 2 hours. So 65mb is at least 2 orders of magnitude more bandwidth consumption than I would expect.

With probably 95+% of fedi ppl on quasi unlimited broadband, probably no one pays attention to this.

Any theories? I had a few different accounts open from different nodes. So I wonder if the JavaScript client code is where all the fat is, which must be fetched upon every single login. Would the stock Lemmy client code be as big as 10mb compressed? A few nodes have some kind of anti-bot thing that runs. I wonder if that has some network fat.

0

~~infosec.pub: 504 gateway timeout~~ (it’s back; momentary glitch, apparently)

preview

I wonder who will even be able to see this post since this community is hosted on infosec.pub. Just slrpnk.net folks, or others?

I wonder who will even be able to see this post since this community is hosted on infosec.pub. Just slrpnk.net folks, or others?

0

Please consider removing *@lemmy.world from the sidebar

preview

It’s antithetical to Framasoft and against the principles and spirit of peertube to promote giant centralised walled gardens, like Cloudflare. I suggest removing this paradoxical centralised community from the sidebar: peertube@lemmy.world.

Otherwise what’s the point? Just use Youtube if digital sovereignty doesn’t matter.

It’s antithetical to Framasoft and against the principles and spirit of peertube to promote giant centralised walled gardens, like Cloudflare. I suggest removing this paradoxical centralised community from the sidebar: peertube@lemmy.world.

Otherwise what’s the point? Just use Youtube if digital sovereignty doesn’t matter.

0

Is banking at the root of much of our tech-based oppression?

preview

I’ve been trying to work out how so many people got to be obsessed with smartphones to the point of using the tiny screens for tasks where it makes no sense. There are many Lemmy apps for smartphones but just a couple half-assed ones for the desktop.

It’s banks. Banks have been cattle-herding security-naive people onto smartphones designed for obsolescence with huge attack surfaces to push their closed-source app which requires licking Google’s boot to obtain. This seems to strike a parallel with Zuckerberg’s comment: “I don’t know why those dumb fucks give me all their data”.

The number of people willing to resist banks can probably be counted on one hand. From there, most people are easy enough to just say “fuck it, I’ll run the app”. This is what drives the “must have a recent phone at all times” brain malfunction. Most of the population is trapped on this shit like caged animals that can’t see the cage bars.

Many don’t bother owning a PC now. They want an all-in-one device. Then they read large amounts of text on that tiny display. So every industry has to cator for smartphone pawns to stay relevant.

Consumers wise enough to keep the GSM SIM slot empty and use smartphones just for innocuous tasks like offline navigation face this onslaught of app-pushers. Some public operations between ppl and government are becoming “app only”.

We are losing our human right to self-determination and autonomy. Normally we could let fools be fools and carry on. But there is a critical mass threshold by which the foolish consumption of many triggers oppression of the few who had enough sense to avoid it.

The offline alternatives and FOSS alternatives are being silently driven out of existence.

I was an early adopter (AOS 2.2). Thought: great, Android is linux based and under FOSS licensing. I am liberated. Got my update to AOS 2.3. Then I was abandoned. I saw right away the shit show I was baited into. Being at the vendor’s mercy for upgrades sent a stark msg to me that I learned from. And apparently not many others.

I wouldn’t care about the foolish decisions of consumers to keep buying new phones if it only affected them. But it’s fucking up the world.

I’ve been trying to work out how so many people got to be obsessed with smartphones to the point of using the tiny screens for tasks where it makes no sense. There are many Lemmy apps for smartphones but just a couple half-assed ones for the desktop.

It’s banks. Banks have been cattle-herding security-naive people onto smartphones designed for obsolescence with huge attack surfaces to push their closed-source app which requires licking Google’s boot to obtain. This seems to strike a parallel with Zuckerberg’s comment: “I don’t know why those dumb fucks give me all their data”.

The number of people willing to resist banks can probably be counted on one hand. From there, most people are easy enough to just say “fuck it, I’ll run the app”. This is what drives the “must have a recent phone at all times” brain malfunction. Most of the population is trapped on this shit like caged animals that can’t see the cage bars.

Many don’t bother owning a PC now. They want an all-in-one device. Then they read large amounts of text on that tiny display. So every industry has to cator for smartphone pawns to stay relevant.

Consumers wise enough to keep the GSM SIM slot empty and use smartphones just for innocuous tasks like offline navigation face this onslaught of app-pushers. Some public operations between ppl and government are becoming “app only”.

We are losing our human right to self-determination and autonomy. Normally we could let fools be fools and carry on. But there is a critical mass threshold by which the foolish consumption of many triggers oppression of the few who had enough sense to avoid it.

The offline alternatives and FOSS alternatives are being silently driven out of existence.

I was an early adopter (AOS 2.2). Thought: great, Android is linux based and under FOSS licensing. I am liberated. Got my update to AOS 2.3. Then I was abandoned. I saw right away the shit show I was baited into. Being at the vendor’s mercy for upgrades sent a stark msg to me that I learned from. And apparently not many others.

I wouldn’t care about the foolish decisions of consumers to keep buying new phones if it only affected them. But it’s fucking up the world.

0

Boycott Transcend. Their storage products use a dark pattern that blocks consumers from keeping a copy of hard drive maintenance & repair s/w

preview

cross-posted from: slrpnk.net/post/26435334 > A Transcend Storejet external HDD has this software: > > - RecoveRx_v2.6.zip > - RecoveRx_Win_4.3_setup.exe > - SecureEraseTool_Win_v1.10_setup.exe > - TranscendElite_Win_v4.28_setup.exe > > I am offline, so I went to a public library to fetch the above files. Early in the installation process the piece of shit tries to connect to the Internet and craps out when it discovers there is no Internet connection. WTF? > > It’s a nasty trend. I’ve seen other drivers and various hardware support tools pull this shit in recent years. > > Is it legal? Seems questionable considering: > > - They use deception. The packaging for the harddrive probably does not have an “Internet required” disclosure, nor would any reasonable buyer expect Internet to be required to use a hard drive. Then they use deception again when you download the tools. I am led to believe I am downloading a “SecureEraseTool” and a “TranscendElite” software package, but in fact these are just proprietary download managers pretending to be tools. > - (GDPR regions) By forcing you to needlessly access the cloud with their proprietary tool, they collect your IP address and whatever else that download manager collects to share with them. This does not seem compliant with data minimization. > > :::spoiler Tech discussion unrelated to the forum topic > Why are those tools needed (you might wonder). The drive is in a shitty state. It’s in a usb3 enclosure and was usb-attached to 3 different machines: > > * linux laptop with usb3 expresscard, attached both with and without supplemental power. The drive spins, LED on the enclosure blinks rapidly, it gets a device handle and /var/log/kern.log shows it was detected okay. Running fdisk on the unmounted drive just hangs for ~10—15′ before timing out. Reattaching and trying to mount it also causes a long ~10—15′ hang before it gives up. > * win7 one two different machines: spins forever, LED blinking rapidly. Windows never gives up and it never gets recognized or mounted. > > So I wanted to first try the official tools to see how they react to the drive. Since they turned out to be a piece of shit, I will probably try next: > > * Remove the drive from the enclosure and attaching directly to a real SATA bus (not one of those shitty SATA-USB adapters and not a SATA-PATA drive bay adapter, even though those would be easier. I will put it on a proper SATA bus because the SMART diag stuff is often crippled when going over a bus adapter of some kind. > * Run the DOS Ultimate Boot CD, which (IIRC) is still the king of disk diagnostic tools. > * See what smartctl does. > * Try zero-filling with dd > ::: > > ### ⚠ Avoid Transcend products for being anti-consumer > > Anyway, the main point of this thread is to expose the shit Transcend pulls by shipping download managers that masquerade as tools. It’s a shitty practice because: > > * The tools are forever dependent on the supplier keeping a host running. Not only to snoop on you but so to do a sneaky form of designed obsolescence. When your drive model is old enough to need the tools, that is when they will pull the plug. You only think you have the software, until it’s game over. You lose autonomy and control over your own product without knowing it. > * Discriminates against offline people. > * Discriminates against tech illiterates, who rely on the easy tools and cannot handle tools like dd, smartctl, and UBCD. > * Assaults right to repair. No right to repair laws are good enough to think of this kind of dark pattern. > * Obsolescence by design. If you cannot install the tools you need to keep the device running, they are effectively bullying you into buying your way out of the problem. >

cross-posted from: slrpnk.net/post/26435334 > A Transcend Storejet external HDD has this software: > > - RecoveRx_v2.6.zip > - RecoveRx_Win_4.3_setup.exe > - SecureEraseTool_Win_v1.10_setup.exe > - TranscendElite_Win_v4.28_setup.exe > > I am offline, so I went to a public library to fetch the above files. Early in the installation process the piece of shit tries to connect to the Internet and craps out when it discovers there is no Internet connection. WTF? > > It’s a nasty trend. I’ve seen other drivers and various hardware support tools pull this shit in recent years. > > Is it legal? Seems questionable considering: > > - They use deception. The packaging for the harddrive probably does not have an “Internet required” disclosure, nor would any reasonable buyer expect Internet to be required to use a hard drive. Then they use deception again when you download the tools. I am led to believe I am downloading a “SecureEraseTool” and a “TranscendElite” software package, but in fact these are just proprietary download managers pretending to be tools. > - (GDPR regions) By forcing you to needlessly access the cloud with their proprietary tool, they collect your IP address and whatever else that download manager collects to share with them. This does not seem compliant with data minimization. > > :::spoiler Tech discussion unrelated to the forum topic > Why are those tools needed (you might wonder). The drive is in a shitty state. It’s in a usb3 enclosure and was usb-attached to 3 different machines: > > * linux laptop with usb3 expresscard, attached both with and without supplemental power. The drive spins, LED on the enclosure blinks rapidly, it gets a device handle and /var/log/kern.log shows it was detected okay. Running fdisk on the unmounted drive just hangs for ~10—15′ before timing out. Reattaching and trying to mount it also causes a long ~10—15′ hang before it gives up. > * win7 one two different machines: spins forever, LED blinking rapidly. Windows never gives up and it never gets recognized or mounted. > > So I wanted to first try the official tools to see how they react to the drive. Since they turned out to be a piece of shit, I will probably try next: > > * Remove the drive from the enclosure and attaching directly to a real SATA bus (not one of those shitty SATA-USB adapters and not a SATA-PATA drive bay adapter, even though those would be easier. I will put it on a proper SATA bus because the SMART diag stuff is often crippled when going over a bus adapter of some kind. > * Run the DOS Ultimate Boot CD, which (IIRC) is still the king of disk diagnostic tools. > * See what smartctl does. > * Try zero-filling with dd > ::: > > ### ⚠ Avoid Transcend products for being anti-consumer > > Anyway, the main point of this thread is to expose the shit Transcend pulls by shipping download managers that masquerade as tools. It’s a shitty practice because: > > * The tools are forever dependent on the supplier keeping a host running. Not only to snoop on you but so to do a sneaky form of designed obsolescence. When your drive model is old enough to need the tools, that is when they will pull the plug. You only think you have the software, until it’s game over. You lose autonomy and control over your own product without knowing it. > * Discriminates against offline people. > * Discriminates against tech illiterates, who rely on the easy tools and cannot handle tools like dd, smartctl, and UBCD. > * Assaults right to repair. No right to repair laws are good enough to think of this kind of dark pattern. > * Obsolescence by design. If you cannot install the tools you need to keep the device running, they are effectively bullying you into buying your way out of the problem. >

0

Transcend storage products require Internet - wtf… forced obsolescence dark pattern?

preview

cross-posted from: slrpnk.net/post/26435334

A Transcend Storejet external HDD has this software:

  • RecoveRx_v2.6.zip
  • RecoveRx_Win_4.3_setup.exe
  • SecureEraseTool_Win_v1.10_setup.exe
  • TranscendElite_Win_v4.28_setup.exe

I am offline, so I went to a public library to fetch the above files. Early in the installation process the piece of shit tries to connect to the Internet and craps out when it discovers there is no Internet connection. WTF?

It’s a nasty trend. I’ve seen other drivers and various hardware support tools pull this shit in recent years.

Is it legal? Seems questionable considering:

  • They use deception. The packaging for the harddrive probably does not have an “Internet required” disclosure, nor would any reasonable buyer expect Internet to be required to use a hard drive. Then they use deception again when you download the tools. I am led to believe I am downloading a “SecureEraseTool” and a “TranscendElite” software package, but in fact these are just proprietary download managers pretending to be tools.
  • (GDPR regions) By forcing you to needlessly access the cloud with their proprietary tool, they collect your IP address and whatever else that download manager collects to share with them. This does not seem compliant with data minimization.

:::spoiler Tech discussion unrelated to the forum topic Why are those tools needed (you might wonder). The drive is in a shitty state. It’s in a usb3 enclosure and was usb-attached to 3 different machines:

  • linux laptop with usb3 expresscard, attached both with and without supplemental power. The drive spins, LED on the enclosure blinks rapidly, it gets a device handle and /var/log/kern.log shows it was detected okay. Running fdisk on the unmounted drive just hangs for ~10—15′ before timing out. Reattaching and trying to mount it also causes a long ~10—15′ hang before it gives up.
  • win7 one two different machines: spins forever, LED blinking rapidly. Windows never gives up and it never gets recognized or mounted.

So I wanted to first try the official tools to see how they react to the drive. Since they turned out to be a piece of shit, I will probably try next:

  • Remove the drive from the enclosure and attaching directly to a real SATA bus (not one of those shitty SATA-USB adapters and not a SATA-PATA drive bay adapter, even though those would be easier. I will put it on a proper SATA bus because the SMART diag stuff is often crippled when going over a bus adapter of some kind.
  • Run the DOS Ultimate Boot CD, which (IIRC) is still the king of disk diagnostic tools.
  • See what smartctl does.
  • Try zero-filling with dd :::

⚠ Avoid Transcend products for being anti-consumer

Anyway, the main point of this thread is to expose the shit Transcend pulls by shipping download managers that masquerade as tools. It’s a shitty practice because:

  • The tools are forever dependent on the supplier keeping a host running. Not only to snoop on you but so to do a sneaky form of designed obsolescence. When your drive model is old enough to need the tools, that is when they will pull the plug. You only think you have the software, until it’s game over. You lose autonomy and control over your own product without knowing it.
  • Discriminates against offline people.
  • Discriminates against tech illiterates, who rely on the easy tools and cannot handle tools like dd, smartctl, and UBCD.
  • Assaults right to repair. No right to repair laws are good enough to think of this kind of dark pattern.
  • Obsolescence by design. If you cannot install the tools you need to keep the device running, they are effectively bullying you into buying your way out of the problem.

cross-posted from: slrpnk.net/post/26435334

A Transcend Storejet external HDD has this software:

  • RecoveRx_v2.6.zip
  • RecoveRx_Win_4.3_setup.exe
  • SecureEraseTool_Win_v1.10_setup.exe
  • TranscendElite_Win_v4.28_setup.exe

I am offline, so I went to a public library to fetch the above files. Early in the installation process the piece of shit tries to connect to the Internet and craps out when it discovers there is no Internet connection. WTF?

It’s a nasty trend. I’ve seen other drivers and various hardware support tools pull this shit in recent years.

Is it legal? Seems questionable considering:

  • They use deception. The packaging for the harddrive probably does not have an “Internet required” disclosure, nor would any reasonable buyer expect Internet to be required to use a hard drive. Then they use deception again when you download the tools. I am led to believe I am downloading a “SecureEraseTool” and a “TranscendElite” software package, but in fact these are just proprietary download managers pretending to be tools.
  • (GDPR regions) By forcing you to needlessly access the cloud with their proprietary tool, they collect your IP address and whatever else that download manager collects to share with them. This does not seem compliant with data minimization.

:::spoiler Tech discussion unrelated to the forum topic Why are those tools needed (you might wonder). The drive is in a shitty state. It’s in a usb3 enclosure and was usb-attached to 3 different machines:

  • linux laptop with usb3 expresscard, attached both with and without supplemental power. The drive spins, LED on the enclosure blinks rapidly, it gets a device handle and /var/log/kern.log shows it was detected okay. Running fdisk on the unmounted drive just hangs for ~10—15′ before timing out. Reattaching and trying to mount it also causes a long ~10—15′ hang before it gives up.
  • win7 one two different machines: spins forever, LED blinking rapidly. Windows never gives up and it never gets recognized or mounted.

So I wanted to first try the official tools to see how they react to the drive. Since they turned out to be a piece of shit, I will probably try next:

  • Remove the drive from the enclosure and attaching directly to a real SATA bus (not one of those shitty SATA-USB adapters and not a SATA-PATA drive bay adapter, even though those would be easier. I will put it on a proper SATA bus because the SMART diag stuff is often crippled when going over a bus adapter of some kind.
  • Run the DOS Ultimate Boot CD, which (IIRC) is still the king of disk diagnostic tools.
  • See what smartctl does.
  • Try zero-filling with dd :::

⚠ Avoid Transcend products for being anti-consumer

Anyway, the main point of this thread is to expose the shit Transcend pulls by shipping download managers that masquerade as tools. It’s a shitty practice because:

  • The tools are forever dependent on the supplier keeping a host running. Not only to snoop on you but so to do a sneaky form of designed obsolescence. When your drive model is old enough to need the tools, that is when they will pull the plug. You only think you have the software, until it’s game over. You lose autonomy and control over your own product without knowing it.
  • Discriminates against offline people.
  • Discriminates against tech illiterates, who rely on the easy tools and cannot handle tools like dd, smartctl, and UBCD.
  • Assaults right to repair. No right to repair laws are good enough to think of this kind of dark pattern.
  • Obsolescence by design. If you cannot install the tools you need to keep the device running, they are effectively bullying you into buying your way out of the problem.
0

The hidden attack on people living analog lifestyles: they just ignore you. US and Europe compared; Europe has a fix for this, but the fix is broken.

preview

I write a lot of snail-mail paper letters. Why? Two primary drivers:

  • Enshitification. If the digital path has CAPTCHAs or dark patterns, I refuse to serve as an enabler. I don’t do CAPTCHAs.
  • Boycotts. I boycott both Microsoft and Google. When a recipient’s email provider is one of them, an honest boycott entails not feeding data to those surveillance advertisers who profit from the data.

Government offices sometimes just ignore the letters – letters which require a response.

:::spoiler The problem in the US Gov agencies have some “public access” databases such as courts that let you search past cases and state secretary’s business registries. But then they impose a CAPTCHA on queries. How does an offline analog person get the info? They put their request for info in writing, which is then simply ignored. You don’t even get enough dignity for an acknowledgement. :::

:::spoiler The problem in Europe As the “digital transformation” movement is shoved down people’s throats, they cattle-herd folks toward their enshitified web portals and their Microsoft-hosted email addresses. Regulators have an obligation to process complaints. E.g. when a transport carrier breaks a transport law or a telecom supplier breaks a telecom law, there is a national authority who must treat your complaint. But if the complaint comes by mail, they sometimes just ignore it. :::

The insideous nature of being ignored is you are also naturally blocked from knowing why you were ignored. Maybe the mail was trully lost - you don’t know. Or maybe they are ignoring paper letters because young workers (born with Internet) don’t know how to write paper letters, or can’t be bothered. Ignoring letters is common in the US because there is usually no oversight. That is, there is no easy escalation option when a state secretary ignores a request. You’re simply fucked unless you’re willing to sue them (and likely lose, but at least you’ll have a chance at getting an answer on why you were ignored).

Europe is structurally more competent. Most¹ NEBs² and other gov agencies have an oversight authority like an ombudsman, where you can complain that your complaint was ignored. Sometimes I strangely find that my complaint actually was being silently treated or investigated, but the agency was just not competent enough to acknowledge the complaint. Other times, they simply ignore. Nonetheless, it’s a shit-show. There is rarely an ultimate answer and the original non-compliance you were reporting goes uncorrected. You don’t even get an apology, generally.

European agencies and ombudsmen are competent as far as keeping stats on the data they process. Complaints get categorised, counted, and stats reported annually. But there is no stat on the number of submissions that get ignored.

We need a federal agency to simply take reports of ignored correspondence, and investigate why it was ignored.

:::spoiler The fix in the US (nothing practical) If the orignal reason for writing was to request public info, you can package your request as an official “Freedom of Information Act” request (FOIA), and they cannot ignore that. But it’s not gratis. You must pay them per page for their costs and effort.

Perhaps a FOIA solves your problem. But for me, it does not because my reason for using analog correspondence is often to punish them for enshitifying the digital platform or for trying to force me to expose info to the surveillance capitalist who handles their email. Paying them for analog info defeats that purpose because it compensates them more than your CAPTCHA-fiddling time is worth. Nevermind the human rights that forced GUI captcha puzzles violate.

If your original request was not for information but for action, then you’re fucked anyway unless you are happy to go to court with confidence in a successful lawsuit in a country where you do not have a right to an analog life. :::

:::spoiler The hack of a fix in Europe (and why it’s broken) The GDPR gives us a theoretically useful fix to being ignored: Article 15. You have a right to access your personal data and to know how your personal data was processed. When you hand-sign a paper letter, that signature satisfies the definition of “personal data” (EDPB confirms this fact). So when they ignore your letter, you can then send them a GDPR Art.15 request asking how your previous letter was processed. They then have a legal obligation to answer you as soon as possible and no later than 30 days later.

Why this fails: data controllers always ignore the Art.15 request asking how the previous letter was processed. Yes, they bluntly violate the GDPR because the GDPR is mostly just a prop to comfort people during the forced digital transformation. The GDPR is not enforced in most cases.

Sure, you can file an Art.77 complaint with the DPA. The DPA will not “ignore” it, per se. They will acknowledge the complaint, assign a case number, and then they will ignore the case which gets moth-balled (neglected) because all DPAs are severely under-staffed and buried in cases. Your attempt to use Art.15 as a hack for purposes it was not intended will have the absolute lowest of priorities and will never get treated. It will just rot.

Nonetheless, file it anyway so at least there is a record of the problem somewhere. :::

¹ Exceptionally, there is no effective oversight above the data protection authorities. You have no recourse when they ignore you. Same problem with federal ombudsmen.
² NEB: National Enforcement Body

I write a lot of snail-mail paper letters. Why? Two primary drivers:

  • Enshitification. If the digital path has CAPTCHAs or dark patterns, I refuse to serve as an enabler. I don’t do CAPTCHAs.
  • Boycotts. I boycott both Microsoft and Google. When a recipient’s email provider is one of them, an honest boycott entails not feeding data to those surveillance advertisers who profit from the data.

Government offices sometimes just ignore the letters – letters which require a response.

:::spoiler The problem in the US Gov agencies have some “public access” databases such as courts that let you search past cases and state secretary’s business registries. But then they impose a CAPTCHA on queries. How does an offline analog person get the info? They put their request for info in writing, which is then simply ignored. You don’t even get enough dignity for an acknowledgement. :::

:::spoiler The problem in Europe As the “digital transformation” movement is shoved down people’s throats, they cattle-herd folks toward their enshitified web portals and their Microsoft-hosted email addresses. Regulators have an obligation to process complaints. E.g. when a transport carrier breaks a transport law or a telecom supplier breaks a telecom law, there is a national authority who must treat your complaint. But if the complaint comes by mail, they sometimes just ignore it. :::

The insideous nature of being ignored is you are also naturally blocked from knowing why you were ignored. Maybe the mail was trully lost - you don’t know. Or maybe they are ignoring paper letters because young workers (born with Internet) don’t know how to write paper letters, or can’t be bothered. Ignoring letters is common in the US because there is usually no oversight. That is, there is no easy escalation option when a state secretary ignores a request. You’re simply fucked unless you’re willing to sue them (and likely lose, but at least you’ll have a chance at getting an answer on why you were ignored).

Europe is structurally more competent. Most¹ NEBs² and other gov agencies have an oversight authority like an ombudsman, where you can complain that your complaint was ignored. Sometimes I strangely find that my complaint actually was being silently treated or investigated, but the agency was just not competent enough to acknowledge the complaint. Other times, they simply ignore. Nonetheless, it’s a shit-show. There is rarely an ultimate answer and the original non-compliance you were reporting goes uncorrected. You don’t even get an apology, generally.

European agencies and ombudsmen are competent as far as keeping stats on the data they process. Complaints get categorised, counted, and stats reported annually. But there is no stat on the number of submissions that get ignored.

We need a federal agency to simply take reports of ignored correspondence, and investigate why it was ignored.

:::spoiler The fix in the US (nothing practical) If the orignal reason for writing was to request public info, you can package your request as an official “Freedom of Information Act” request (FOIA), and they cannot ignore that. But it’s not gratis. You must pay them per page for their costs and effort.

Perhaps a FOIA solves your problem. But for me, it does not because my reason for using analog correspondence is often to punish them for enshitifying the digital platform or for trying to force me to expose info to the surveillance capitalist who handles their email. Paying them for analog info defeats that purpose because it compensates them more than your CAPTCHA-fiddling time is worth. Nevermind the human rights that forced GUI captcha puzzles violate.

If your original request was not for information but for action, then you’re fucked anyway unless you are happy to go to court with confidence in a successful lawsuit in a country where you do not have a right to an analog life. :::

:::spoiler The hack of a fix in Europe (and why it’s broken) The GDPR gives us a theoretically useful fix to being ignored: Article 15. You have a right to access your personal data and to know how your personal data was processed. When you hand-sign a paper letter, that signature satisfies the definition of “personal data” (EDPB confirms this fact). So when they ignore your letter, you can then send them a GDPR Art.15 request asking how your previous letter was processed. They then have a legal obligation to answer you as soon as possible and no later than 30 days later.

Why this fails: data controllers always ignore the Art.15 request asking how the previous letter was processed. Yes, they bluntly violate the GDPR because the GDPR is mostly just a prop to comfort people during the forced digital transformation. The GDPR is not enforced in most cases.

Sure, you can file an Art.77 complaint with the DPA. The DPA will not “ignore” it, per se. They will acknowledge the complaint, assign a case number, and then they will ignore the case which gets moth-balled (neglected) because all DPAs are severely under-staffed and buried in cases. Your attempt to use Art.15 as a hack for purposes it was not intended will have the absolute lowest of priorities and will never get treated. It will just rot.

Nonetheless, file it anyway so at least there is a record of the problem somewhere. :::

¹ Exceptionally, there is no effective oversight above the data protection authorities. You have no recourse when they ignore you. Same problem with federal ombudsmen.
² NEB: National Enforcement Body
0

Lemmyverse is not decentralised. It’s neutral at best.

preview

cross-posted from: slrpnk.net/post/24727683

The fediverse w/the activitypub API sell itself as being decentralised, but it’s actually just neutral. It merely enables decentralised forums to coexist with centralised venues. The Lemmy implementation in particular does nothing to proactively promote decentralisation or counter concentrations of power.

When the software is not designed to steer toward decentralisation, centralisation persists because the network effect is left uncountered. The current stats prove that a mass majority of users and their activity are subject to the concentrated power of a few, which ultimately singularly falls under the power, oversight, and competency of the biggest walled garden in the world: Cloudflare Inc, in the US.

Calling Lemmy “neutral” is overly generous, in fact. When the stock Lemmy web client is queried for communities, it prioritises the giant centralised communities in top rankings of the search results. It’s no better than Google, where Cloudflare also dominates the top slots in web search results. This exacerbates the network effect by cattle-herding people toward increased centralisation.

Lemmy ranks decentralised communities at the bottom. And in some cases the ranking is so low that it’s out of reach when cross-posting. The cross-post mechanism forces a search for the target community, and that search does not support entry of the address of the community that includes the domain. When the list is so long it exceeds the pulldown window length, it’s out of reach.

Yes, we know centralisation is not their deliberate goal. Lemmy developers fear that newcoming novices would unwittingly post in a ghost town without strategically cross-posting and then become immediately discouraged by minimal engagement, and from there bounce back to Twitter or wherever they came from. But it must be realised that the mass nannied steering they have resorted to has cultivated centralisation that defeats the founding purpose of the fedi.

cross-posted from: slrpnk.net/post/24727683

The fediverse w/the activitypub API sell itself as being decentralised, but it’s actually just neutral. It merely enables decentralised forums to coexist with centralised venues. The Lemmy implementation in particular does nothing to proactively promote decentralisation or counter concentrations of power.

When the software is not designed to steer toward decentralisation, centralisation persists because the network effect is left uncountered. The current stats prove that a mass majority of users and their activity are subject to the concentrated power of a few, which ultimately singularly falls under the power, oversight, and competency of the biggest walled garden in the world: Cloudflare Inc, in the US.

Calling Lemmy “neutral” is overly generous, in fact. When the stock Lemmy web client is queried for communities, it prioritises the giant centralised communities in top rankings of the search results. It’s no better than Google, where Cloudflare also dominates the top slots in web search results. This exacerbates the network effect by cattle-herding people toward increased centralisation.

Lemmy ranks decentralised communities at the bottom. And in some cases the ranking is so low that it’s out of reach when cross-posting. The cross-post mechanism forces a search for the target community, and that search does not support entry of the address of the community that includes the domain. When the list is so long it exceeds the pulldown window length, it’s out of reach.

Yes, we know centralisation is not their deliberate goal. Lemmy developers fear that newcoming novices would unwittingly post in a ghost town without strategically cross-posting and then become immediately discouraged by minimal engagement, and from there bounce back to Twitter or wherever they came from. But it must be realised that the mass nannied steering they have resorted to has cultivated centralisation that defeats the founding purpose of the fedi.

0

We have lost our right to boycott because we don’t have a right to be analog (everywhere, but Danish ppl in particular)

preview

cross-posted from: slrpnk.net/post/24727109

The right to be analog is a critical enabler to the power to boycott.

Suppose you boycott Microsoft and Google. If you need to reach a gov office who uses MS or Google for email, then you are writing a snail mail letter. Denmark has eliminated the national postal service. The loss of an important analog option forces Danes to use the digital mechanism. No one in Denmark can say: “hold on, I am boycotting Microsoft, so I cannot be obligated to correspond with your office”.

No country gives its people either rights. That is, there is no country that gives you a right to boycott or the right be analog. In principle, we could loosely claim to derive those rights through the human rights to autonomy, dignity, and self-determination. But that won’t hold up in court, as human rights are generally disregarded in court. Abstract human rights like that are really a long-shot as well. Even if a court were to concede to human rights, you’ve already lost if you have to go to court because in Europe you cannot generally recover all damages even if the judge takes your side.

I believe a window of opportunity is passing us by. If we do not establish a right to be analog hard and fast, it will be too late once mechanisms supporting our analog refuge are gone.

Europe is quietly removing the cash option. Europeans are boiling frogs. They don’t see that they have already lost the option to be free from banks. Forced banking is already in force. This enables banks to gradually force you onto their enshitified digital platforms.

What I find most disturbing is how a vast majority are blind to this.

cross-posted from: slrpnk.net/post/24727109

The right to be analog is a critical enabler to the power to boycott.

Suppose you boycott Microsoft and Google. If you need to reach a gov office who uses MS or Google for email, then you are writing a snail mail letter. Denmark has eliminated the national postal service. The loss of an important analog option forces Danes to use the digital mechanism. No one in Denmark can say: “hold on, I am boycotting Microsoft, so I cannot be obligated to correspond with your office”.

No country gives its people either rights. That is, there is no country that gives you a right to boycott or the right be analog. In principle, we could loosely claim to derive those rights through the human rights to autonomy, dignity, and self-determination. But that won’t hold up in court, as human rights are generally disregarded in court. Abstract human rights like that are really a long-shot as well. Even if a court were to concede to human rights, you’ve already lost if you have to go to court because in Europe you cannot generally recover all damages even if the judge takes your side.

I believe a window of opportunity is passing us by. If we do not establish a right to be analog hard and fast, it will be too late once mechanisms supporting our analog refuge are gone.

Europe is quietly removing the cash option. Europeans are boiling frogs. They don’t see that they have already lost the option to be free from banks. Forced banking is already in force. This enables banks to gradually force you onto their enshitified digital platforms.

What I find most disturbing is how a vast majority are blind to this.

0

We have lost our right to boycott because we don’t have a right to be analog (everywhere, but Danish ppl in particular)

preview

The right to be analog is a critical intrinsic enabler to the power to boycott.

Suppose you boycott Microsoft and Google. If you need to reach a gov office who uses MS or Google for email, then you are writing a snail mail letter. Denmark has eliminated the national postal service. The loss of an important analog option forces Danes to use the digital mechanism. No one in Denmark can say: “hold on, I am boycotting Microsoft, so I cannot be obligated to correspond with your office”.

No country gives its people either rights. That is, there is no country that gives you a right to boycott or the right be analog. In principle, we could loosely claim to derive those rights through the human rights to autonomy, dignity, and self-determination. But that won’t hold up in court, as human rights are generally disregarded in court. Abstract human rights like that are really a long-shot as well. Even if a court were to concede to human rights, you’ve already lost if you have to go to court because in Europe you cannot generally recover all damages even if the judge takes your side.

I believe a window of opportunity is passing us by. If we do not establish a right to be analog hard and fast, it will be too late once mechanisms supporting our analog refuge are gone.

Europe is quietly removing the cash option. Europeans are boiling frogs. They don’t see that they have already lost the option to be free from banks. Forced banking is already in force. This enables banks to gradually force you onto their enshitified digital platforms.

What I find most disturbing is how a vast majority are blind to this.

The right to be analog is a critical intrinsic enabler to the power to boycott.

Suppose you boycott Microsoft and Google. If you need to reach a gov office who uses MS or Google for email, then you are writing a snail mail letter. Denmark has eliminated the national postal service. The loss of an important analog option forces Danes to use the digital mechanism. No one in Denmark can say: “hold on, I am boycotting Microsoft, so I cannot be obligated to correspond with your office”.

No country gives its people either rights. That is, there is no country that gives you a right to boycott or the right be analog. In principle, we could loosely claim to derive those rights through the human rights to autonomy, dignity, and self-determination. But that won’t hold up in court, as human rights are generally disregarded in court. Abstract human rights like that are really a long-shot as well. Even if a court were to concede to human rights, you’ve already lost if you have to go to court because in Europe you cannot generally recover all damages even if the judge takes your side.

I believe a window of opportunity is passing us by. If we do not establish a right to be analog hard and fast, it will be too late once mechanisms supporting our analog refuge are gone.

Europe is quietly removing the cash option. Europeans are boiling frogs. They don’t see that they have already lost the option to be free from banks. Forced banking is already in force. This enables banks to gradually force you onto their enshitified digital platforms.

What I find most disturbing is how a vast majority are blind to this.

0

There is a “Cathedral and Bazaar” within the fediverse that manifests as utilitarian users and deontological users, respectively

preview

cross-posted from: slrpnk.net/post/24598576

The state of the fedi superficially parallels what Eric S. Raymond articulated in the 1990s on software construction. There are two models for digital community building within the fediverse. The intent was a decentralised bazaar whereby power is well dispersed, with no single entity excessively wielding disproportionate power. Activitypub was designed to enable the bazaar model to exist, but it neglects to curtail the antithetical model that anarchy-minded folks want to escape: the cathedral.

The hope and expectation was simply that builders of giant monolithic cathedrals would have no interest in the fedi; that they would want their empire to take the conventional path of walling themselves off. Fedi founders did not envision ambitions for power would emerge within the fedi. Who would have predicted that Facebook would decide to compromise its garden walls in exchange for influence over a quite small population? Or that Cloudflare’s centralized walled garden would be exploited to supercharge disproportionate growth by node operators intent on using the network effect to concentrate power? These kinds of technofeudal actors have traditionally vied for absolute power without attempting to cannabalise and occupy a fair structure to then coexist with.

Fedi founders thought the federate/defederate option would sufficiently control for actors who would work against the vision of the bazaar. This blunt tool relies heavily on the demographic of relative pseudo anarchists being larger than it is.

I think it was Kensanata (Alex Schröder) who notably stressed what I regard as a true dichotomy, the sentiment of which was something to the effect of:

you can simply go where the people are, or you can go where the platform and tech is well-designed.¹

The former are utilitarians and the latter are deontologists who find other people (though far fewer) that share the same understanding and appreciation of structures that feature resistance to tyranny. The separation is comparable to anarchists (at heart) seeking out a small freedom-rich niche away from the ivory tower cathedral.

The bazaar (decentralised) segment of the fedi comes at the cost of utility, as principles of digital ethics trump the instant gratification of a large audience. The sacrifice is not in vain. It’s made with an expectation that wisdom will spread and sustain. Though it seems clear that the cathedral will always exist and perhaps always enjoy dominance of the majority who serve it (are pawned by it).

There is a noteworthy contrast from Raymond’s C&B essay. Raymond likens the bazaar to “selfish agents” attributed to “utilitarian” Linux hackers under the idea that Linus harnesses their egos collectively (“egoboo”). Whereas in the fediverse of community builders, it is the selfish agents unwilling to compromise time and convenience who fill the cathedrals, baited by heavily populated communities.

Raves and Burning Man started off small and great; rich in culture, before rapid growth diluted the subculture and commercialisation did what it does. The natural response is to “take it underground” to try to restore the original greatness.

The fedi has passed that inflection point. We have LW serfs popping into */c/privacy communities to heckle whoever they perceive as “paranoid”, or worse, deliver a lecture on privacy (from Cloudflare). There is a profound and somewhat ironic number of CF cathedral folks making way into digital rights types of communities, not seeing the starkness of which would be comparable to Donald Trump appearing at a reggae festival, or an AOL user in the 1990s stepping into an engineering usenet newsgroup.

So here’s a fun search result:

🌩 lemmy.world🌩|decentralization 🌩 kbin.earth🌩|decentralize ⚠lemmy.ml/c/decentralized

There are just 3 communities specifically for decentralisation chatter and they are all on centralised hosts. It’s actually useful that they exist in those places from an outreach standpoint. But it’s likely being overly generous to assume they exist for outreach to those who need to be reached.

Anyway, going forward we need tools and datasets with metrics. The metrics currently serve the utilitarian who simply looks for the most exposure of their content without regard to the ethics underpinning decentralisation. Metrics that serve the bazaar would have to measure degree of power centralisation.

¹ paraphrased - not an exact quote

cross-posted from: slrpnk.net/post/24598576

The state of the fedi superficially parallels what Eric S. Raymond articulated in the 1990s on software construction. There are two models for digital community building within the fediverse. The intent was a decentralised bazaar whereby power is well dispersed, with no single entity excessively wielding disproportionate power. Activitypub was designed to enable the bazaar model to exist, but it neglects to curtail the antithetical model that anarchy-minded folks want to escape: the cathedral.

The hope and expectation was simply that builders of giant monolithic cathedrals would have no interest in the fedi; that they would want their empire to take the conventional path of walling themselves off. Fedi founders did not envision ambitions for power would emerge within the fedi. Who would have predicted that Facebook would decide to compromise its garden walls in exchange for influence over a quite small population? Or that Cloudflare’s centralized walled garden would be exploited to supercharge disproportionate growth by node operators intent on using the network effect to concentrate power? These kinds of technofeudal actors have traditionally vied for absolute power without attempting to cannabalise and occupy a fair structure to then coexist with.

Fedi founders thought the federate/defederate option would sufficiently control for actors who would work against the vision of the bazaar. This blunt tool relies heavily on the demographic of relative pseudo anarchists being larger than it is.

I think it was Kensanata (Alex Schröder) who notably stressed what I regard as a true dichotomy, the sentiment of which was something to the effect of:

you can simply go where the people are, or you can go where the platform and tech is well-designed.¹

The former are utilitarians and the latter are deontologists who find other people (though far fewer) that share the same understanding and appreciation of structures that feature resistance to tyranny. The separation is comparable to anarchists (at heart) seeking out a small freedom-rich niche away from the ivory tower cathedral.

The bazaar (decentralised) segment of the fedi comes at the cost of utility, as principles of digital ethics trump the instant gratification of a large audience. The sacrifice is not in vain. It’s made with an expectation that wisdom will spread and sustain. Though it seems clear that the cathedral will always exist and perhaps always enjoy dominance of the majority who serve it (are pawned by it).

There is a noteworthy contrast from Raymond’s C&B essay. Raymond likens the bazaar to “selfish agents” attributed to “utilitarian” Linux hackers under the idea that Linus harnesses their egos collectively (“egoboo”). Whereas in the fediverse of community builders, it is the selfish agents unwilling to compromise time and convenience who fill the cathedrals, baited by heavily populated communities.

Raves and Burning Man started off small and great; rich in culture, before rapid growth diluted the subculture and commercialisation did what it does. The natural response is to “take it underground” to try to restore the original greatness.

The fedi has passed that inflection point. We have LW serfs popping into */c/privacy communities to heckle whoever they perceive as “paranoid”, or worse, deliver a lecture on privacy (from Cloudflare). There is a profound and somewhat ironic number of CF cathedral folks making way into digital rights types of communities, not seeing the starkness of which would be comparable to Donald Trump appearing at a reggae festival, or an AOL user in the 1990s stepping into an engineering usenet newsgroup.

So here’s a fun search result:

🌩 lemmy.world🌩|decentralization 🌩 kbin.earth🌩|decentralize ⚠lemmy.ml/c/decentralized

There are just 3 communities specifically for decentralisation chatter and they are all on centralised hosts. It’s actually useful that they exist in those places from an outreach standpoint. But it’s likely being overly generous to assume they exist for outreach to those who need to be reached.

Anyway, going forward we need tools and datasets with metrics. The metrics currently serve the utilitarian who simply looks for the most exposure of their content without regard to the ethics underpinning decentralisation. Metrics that serve the bazaar would have to measure degree of power centralisation.

¹ paraphrased - not an exact quote

0

Wrote a script to find decentralised communities w/in the fedi. It selects nodes w/active users < avg+2σ. Is that a good approach? Check my math plz.

preview

cross-posted from: slrpnk.net/post/24512484

(The pic is sample output for an arbitrary query on “vegan vege pesc”. Irrelevant side note: there is no free-world venue for pescatarians… just one in L/W that scrolled off the screen)

CF

The federation is not wholly decentralised, obviously, when giant centralised fiefdoms like Facebook “Threads”™ and Cloudflare hook in their technofeudal variety of oppressive infra and abuse their power.

Each post submission begins with finding a relevant venue for the content and it must be consistent with my sense of ethics. Cloudflare is automatically nixed because it’s inherently centralised in a walled garden (regardless of the user count for any given node). CF is a non-starter for an open, free, and fair society (fair implying power balance, equality, transparency, etc).

My script queries the catalog of communities for relevant venues. It still prints the Cloudflare walled garden because it’s useful to see what names match my regex queries, which sometimes helps form a better query. It’s the only thing #LemmyWorld is good for (a shit-ton of community names with redundant variations of the same subject matter). Those results are in red, tagged with a thundercloud (🌩 ), and printed first (because when they scroll off the terminal I don’t typically care to scroll up to see them).

non-CF

CF is not the only issue. Some non-CF nodes are centralized due to uncontrolled growth to disproportionately large sizes. I don’t cancel them hard-and-fast like CF nodes, but they get treated with low “last resort” favorability. They have the warning symbol (⚠) and are in yellow.

Is my math decent?

My script began by filtering on total user count. Then I realised dead or dormant users probably should not count because such users don’t really contribute to a node’s disproportionate power over a population. It’s active users that matter. But if the number of active users in a day are filtered on, that’s too dynamic for deciding where my post can live for a month or however long it is relevant. So I took the users_active_half_year count. Is that sensible?

What constitutes an “active” user, simply logging in, or commenting?

The line is drawn at 2 standard deviations above the average – after tossing outliers. Nodes with less than 5 active users in ½ a year are likely 1-person nodes which do not influence the average. The average is around 320 active ½yr users per node. The standard deviation is ~702 users. My statistical competence is rusty for sure, but I’m a bit bothered by a standard deviation that’s more than double the mean. Seems like a variation so wild it should perhaps be disregarded. Nonetheless, I opted to flag nodes that exceed ~1724 users_active_half_year.

The pseudocode looks like this:

avg=$(sqlite3 "$db" 'select round(avg([counts.users_active_half_year])) from node_tbl where tags not like "%cloudflare%" and [counts.users_active_half_year] > 4')
variance=$(sqlite3 "$db" 'select avg(([counts.users_active_half_year] - subtbl.aua) * ([counts.users_active_half_year] - subtbl.aua)) as var from node_tbl, (select avg([counts.users_active_half_year]) as aua from node_tbl where tags not like "%cloudflare%" and [counts.users_active_half_year] > 4) as subtbl where tags not like "%cloudflare%" and [counts.users_active_half_year] > 4;')

sqlite3 "$db" "select case when baseurl in (select baseurl from node_tbl where [counts.users_active_half_year] > $avg+sqrt($variance)*2) then '$yellow⚠' else '$cyan' end||baseurl||'$reset',name from community_tbl where (name like '%${1}%' or desc like '%${1}%') and baseurl not in (select baseurl from node_tbl where tags like '%cloudflare%') order by baseurl,name"

Code is ugly because sqlite does not have a stdev builtin function.

My other thought is to cut slack for closed nodes because at least they are expected to shrink. To list the possible figures to filter on, this is a record for lemmy.ml (the biggest non-Cloudflare node): :::spoiler record for lemmy.ml url = lemmy.ml baseurl = lemmy.ml name = Lemmy desc = A community of privacy and FOSS enthusiasts, run by Lemmy’s developers downvotes = 1 nsfw = 1 create_admin = 0 private = 0 fed = 1 version = 0.19.12 open = 1 usage.users.total = 54790 usage.users.activeHalfyear = 4201 usage.users.activeMonth = 2125 usage.localPosts = 167331 usage.localComments = 818559 counts.site_id = 1 counts.users = 54790 counts.posts = 167331 counts.comments = 818559 counts.communities = 4608 counts.users_active_day = 947 counts.users_active_week = 1496 counts.users_active_month = 2125 counts.users_active_half_year = 4201 icon = lemmy.ml/…/fa6d9660-4f1f-4e90-ac73-b897216db6f3.p… banner = langs = [“all”] date = 2019-04-20T18:53:54.608882Z published = 1555786434000 time = 1751974533970 score = uptime.domain = lemmy.ml uptime.latency = 0.034 uptime.countryname = France uptime.uptime_alltime = 99.04 uptime.date_created = uptime.date_updated = 2021-10-29 15:09:21 uptime.date_laststats = 2025-04-11 21:03:25 uptime.score = 100 uptime.status = 1 isSuspicious = 0 metrics.usersTotal = 54790 metrics.usersMonth = 2125 metrics.usersWeek = 1496 metrics.totalActivity = 985890 metrics.localPosts = 167331 metrics.localComments = 818559 metrics.averageUsers = 50720.8825256975 metrics.biggestJump = 225 metrics.averagePerMinute = 0.02475 metrics.userActivityScore = 0.055574151274483 metrics.activityUserScore = 17.9939770031028 metrics.userActiveMonthScore = 25.7835294117647 tags = [] susReason = [] trust.lastCrawled = 1751974533970 trust.baseurl = lemmy.ml trust.metrics.usersTotal = 54790 trust.metrics.usersMonth = 2125 trust.metrics.usersWeek = 1496 trust.metrics.totalActivity = 985890 trust.metrics.localPosts = 167331 trust.metrics.localComments = 818559 trust.metrics.averageUsers = 50720.8825256975 trust.metrics.biggestJump = 225 trust.metrics.averagePerMinute = 0.02475 trust.metrics.userActivityScore = 0.055574151274483 trust.metrics.activityUserScore = 17.9939770031028 trust.metrics.userActiveMonthScore = 25.7835294117647 trust.users = 54790 trust.name = Lemmy trust.base = lemmy.ml trust.actor_id = lemmy.ml trust.tags = [] trust.guarantor = fediseer.com trust.endorsements = 17 trust.score = 598.1875 trust.reasons = [] blocks.incoming = 0 blocks.outgoing = 0 blocked = [] :::

Some communities missing from the Lemmyverse DB - why?

Anyone know why some slrpnk.net communities are in the Lemmyverse DB, and some are not? E.g. why is !nolawns@slrpnk.net missing, despite many others from the same node that are included?

More importantly, what’s the fix apart from crawling all the nodes (which would probably be unwelcome)? Is there another open DB apart from Lemmyverse? There is fediverse.space and fediverse.observer, but they don’t appear to be sharing their data.

cross-posted from: slrpnk.net/post/24512484

(The pic is sample output for an arbitrary query on “vegan vege pesc”. Irrelevant side note: there is no free-world venue for pescatarians… just one in L/W that scrolled off the screen)

CF

The federation is not wholly decentralised, obviously, when giant centralised fiefdoms like Facebook “Threads”™ and Cloudflare hook in their technofeudal variety of oppressive infra and abuse their power.

Each post submission begins with finding a relevant venue for the content and it must be consistent with my sense of ethics. Cloudflare is automatically nixed because it’s inherently centralised in a walled garden (regardless of the user count for any given node). CF is a non-starter for an open, free, and fair society (fair implying power balance, equality, transparency, etc).

My script queries the catalog of communities for relevant venues. It still prints the Cloudflare walled garden because it’s useful to see what names match my regex queries, which sometimes helps form a better query. It’s the only thing #LemmyWorld is good for (a shit-ton of community names with redundant variations of the same subject matter). Those results are in red, tagged with a thundercloud (🌩 ), and printed first (because when they scroll off the terminal I don’t typically care to scroll up to see them).

non-CF

CF is not the only issue. Some non-CF nodes are centralized due to uncontrolled growth to disproportionately large sizes. I don’t cancel them hard-and-fast like CF nodes, but they get treated with low “last resort” favorability. They have the warning symbol (⚠) and are in yellow.

Is my math decent?

My script began by filtering on total user count. Then I realised dead or dormant users probably should not count because such users don’t really contribute to a node’s disproportionate power over a population. It’s active users that matter. But if the number of active users in a day are filtered on, that’s too dynamic for deciding where my post can live for a month or however long it is relevant. So I took the users_active_half_year count. Is that sensible?

What constitutes an “active” user, simply logging in, or commenting?

The line is drawn at 2 standard deviations above the average – after tossing outliers. Nodes with less than 5 active users in ½ a year are likely 1-person nodes which do not influence the average. The average is around 320 active ½yr users per node. The standard deviation is ~702 users. My statistical competence is rusty for sure, but I’m a bit bothered by a standard deviation that’s more than double the mean. Seems like a variation so wild it should perhaps be disregarded. Nonetheless, I opted to flag nodes that exceed ~1724 users_active_half_year.

The pseudocode looks like this:

avg=$(sqlite3 "$db" 'select round(avg([counts.users_active_half_year])) from node_tbl where tags not like "%cloudflare%" and [counts.users_active_half_year] > 4')
variance=$(sqlite3 "$db" 'select avg(([counts.users_active_half_year] - subtbl.aua) * ([counts.users_active_half_year] - subtbl.aua)) as var from node_tbl, (select avg([counts.users_active_half_year]) as aua from node_tbl where tags not like "%cloudflare%" and [counts.users_active_half_year] > 4) as subtbl where tags not like "%cloudflare%" and [counts.users_active_half_year] > 4;')

sqlite3 "$db" "select case when baseurl in (select baseurl from node_tbl where [counts.users_active_half_year] > $avg+sqrt($variance)*2) then '$yellow⚠' else '$cyan' end||baseurl||'$reset',name from community_tbl where (name like '%${1}%' or desc like '%${1}%') and baseurl not in (select baseurl from node_tbl where tags like '%cloudflare%') order by baseurl,name"

Code is ugly because sqlite does not have a stdev builtin function.

My other thought is to cut slack for closed nodes because at least they are expected to shrink. To list the possible figures to filter on, this is a record for lemmy.ml (the biggest non-Cloudflare node): :::spoiler record for lemmy.ml url = lemmy.ml baseurl = lemmy.ml name = Lemmy desc = A community of privacy and FOSS enthusiasts, run by Lemmy’s developers downvotes = 1 nsfw = 1 create_admin = 0 private = 0 fed = 1 version = 0.19.12 open = 1 usage.users.total = 54790 usage.users.activeHalfyear = 4201 usage.users.activeMonth = 2125 usage.localPosts = 167331 usage.localComments = 818559 counts.site_id = 1 counts.users = 54790 counts.posts = 167331 counts.comments = 818559 counts.communities = 4608 counts.users_active_day = 947 counts.users_active_week = 1496 counts.users_active_month = 2125 counts.users_active_half_year = 4201 icon = lemmy.ml/…/fa6d9660-4f1f-4e90-ac73-b897216db6f3.p… banner = langs = [“all”] date = 2019-04-20T18:53:54.608882Z published = 1555786434000 time = 1751974533970 score = uptime.domain = lemmy.ml uptime.latency = 0.034 uptime.countryname = France uptime.uptime_alltime = 99.04 uptime.date_created = uptime.date_updated = 2021-10-29 15:09:21 uptime.date_laststats = 2025-04-11 21:03:25 uptime.score = 100 uptime.status = 1 isSuspicious = 0 metrics.usersTotal = 54790 metrics.usersMonth = 2125 metrics.usersWeek = 1496 metrics.totalActivity = 985890 metrics.localPosts = 167331 metrics.localComments = 818559 metrics.averageUsers = 50720.8825256975 metrics.biggestJump = 225 metrics.averagePerMinute = 0.02475 metrics.userActivityScore = 0.055574151274483 metrics.activityUserScore = 17.9939770031028 metrics.userActiveMonthScore = 25.7835294117647 tags = [] susReason = [] trust.lastCrawled = 1751974533970 trust.baseurl = lemmy.ml trust.metrics.usersTotal = 54790 trust.metrics.usersMonth = 2125 trust.metrics.usersWeek = 1496 trust.metrics.totalActivity = 985890 trust.metrics.localPosts = 167331 trust.metrics.localComments = 818559 trust.metrics.averageUsers = 50720.8825256975 trust.metrics.biggestJump = 225 trust.metrics.averagePerMinute = 0.02475 trust.metrics.userActivityScore = 0.055574151274483 trust.metrics.activityUserScore = 17.9939770031028 trust.metrics.userActiveMonthScore = 25.7835294117647 trust.users = 54790 trust.name = Lemmy trust.base = lemmy.ml trust.actor_id = lemmy.ml trust.tags = [] trust.guarantor = fediseer.com trust.endorsements = 17 trust.score = 598.1875 trust.reasons = [] blocks.incoming = 0 blocks.outgoing = 0 blocked = [] :::

Some communities missing from the Lemmyverse DB - why?

Anyone know why some slrpnk.net communities are in the Lemmyverse DB, and some are not? E.g. why is !nolawns@slrpnk.net missing, despite many others from the same node that are included?

More importantly, what’s the fix apart from crawling all the nodes (which would probably be unwelcome)? Is there another open DB apart from Lemmyverse? There is fediverse.space and fediverse.observer, but they don’t appear to be sharing their data.

0

StackExchange / StackOverflow ratchets up the aggression against non-boot-licking free-worlders, using Cloudflare to thwart decentralised access

GitHub 403 error · Issue #175 · httpjamesm/AnonymousOverflow github.com
preview

A lot of tech knowledge is jailed in #StackOverflow, #StackExchange. Too much. The tech world is very dependant on this single gate keeper. This week, freedom to access SE’s indispensible tech knowledge has been lost.

Timeline

  • pre-2016: SE jailed itself inside Cloudflare
  • ? - At some point SE became “openly” accessible and Cloudflare-free. But a massive #cookieWall blocked content and it was broken to a large extent. That is, in some browsers there was no way to get past the cookie wall.
  • 2022 - #AnonymousOverflow was founded. This front-end platform made the cookie wall problem go away regardless of your browser and anonymity.
  • 2023 - SE reverted back to Cloudflare, effectively making the need for AnonymousOverflow more dire; more important.
  • This week - SE tunes the Cloudflare settings to aggressively block AnonymousOverflow instances, ultimately killing off free-world access to tech information.

A lot of tech knowledge is jailed in #StackOverflow, #StackExchange. Too much. The tech world is very dependant on this single gate keeper. This week, freedom to access SE’s indispensible tech knowledge has been lost.

Timeline

  • pre-2016: SE jailed itself inside Cloudflare
  • ? - At some point SE became “openly” accessible and Cloudflare-free. But a massive #cookieWall blocked content and it was broken to a large extent. That is, in some browsers there was no way to get past the cookie wall.
  • 2022 - #AnonymousOverflow was founded. This front-end platform made the cookie wall problem go away regardless of your browser and anonymity.
  • 2023 - SE reverted back to Cloudflare, effectively making the need for AnonymousOverflow more dire; more important.
  • This week - SE tunes the Cloudflare settings to aggressively block AnonymousOverflow instances, ultimately killing off free-world access to tech information.
0

How old TomTom and Garmin Satnavs could be useful, instead of e-waste (but OSMand and Organic Maps need to improve)

preview

cross-posted from: slrpnk.net/post/21637924

A box of really old TomToms (softball sized) appeared at a street market a year ago, two for a dollar. I doubt anyone was interested in any and I doubt the seller would bother to return with them. They were probably be wasted.

In principle, old TomToms could be used to feed a smartphone. If you use a smartphone for navigation, these components compete to suck the battery dry:

  • the color LCD
  • GPS radio receiver
  • WiFi¹
  • GSM¹

(1) only applies to Google boot-lickers who enable location tracking in order to avoid the wait to acquire satellites.

The GPS is a significant drain because it’s heavy on non-stop calculations, which generates heat (wasted energy), and the heat itself hits the battery even harder.

We can do better. TomToms with bluetooth tend to suppot NMEA (I think). So the old TomTom w/outdated maps could be used purely to get a fix using its own battery supply, which it then transmits over bluetooth. So you toss TT in your backpack. Disable the GPS on your smartphone and enable bluetooth. Bluetooth is like 1 tenth the energy consumption of GPS. Then you enable mock GPS in advanced settings and run a FOSS bluetooth app that serves as middleware to feed the mock location.

The problem: OSMand and Organic Maps are both incapable of using mock GPS locations. And even if they add the capability, it would only be in their recent version which has already left behind older phones. (edit: well Organic Maps is not that bad… their latest version supports AOS 5)

Refusing to support Google means using airplane mode with location svcs off and being wholly dependent on GPS. And for whatever reason it takes me around 20—30 min to get a fix despite being in a large major city; every time. This must make Google happy. The old TomToms were faster at getting a fix. IIRC, they would take 20—30″ only the first time but quickly got a fix after subsequent power cycles in the same area thereafter.

Smartphones have the sensors to do inertial nav if you calibrate a starting point. But the apps don’t have their shit together yet. I vaguely a recall a FOSS app doing inertial nav, but not too useful if it results in a mock location that OSMand cannot handle.

cross-posted from: slrpnk.net/post/21637924

A box of really old TomToms (softball sized) appeared at a street market a year ago, two for a dollar. I doubt anyone was interested in any and I doubt the seller would bother to return with them. They were probably be wasted.

In principle, old TomToms could be used to feed a smartphone. If you use a smartphone for navigation, these components compete to suck the battery dry:

  • the color LCD
  • GPS radio receiver
  • WiFi¹
  • GSM¹

(1) only applies to Google boot-lickers who enable location tracking in order to avoid the wait to acquire satellites.

The GPS is a significant drain because it’s heavy on non-stop calculations, which generates heat (wasted energy), and the heat itself hits the battery even harder.

We can do better. TomToms with bluetooth tend to suppot NMEA (I think). So the old TomTom w/outdated maps could be used purely to get a fix using its own battery supply, which it then transmits over bluetooth. So you toss TT in your backpack. Disable the GPS on your smartphone and enable bluetooth. Bluetooth is like 1 tenth the energy consumption of GPS. Then you enable mock GPS in advanced settings and run a FOSS bluetooth app that serves as middleware to feed the mock location.

The problem: OSMand and Organic Maps are both incapable of using mock GPS locations. And even if they add the capability, it would only be in their recent version which has already left behind older phones. (edit: well Organic Maps is not that bad… their latest version supports AOS 5)

Refusing to support Google means using airplane mode with location svcs off and being wholly dependent on GPS. And for whatever reason it takes me around 20—30 min to get a fix despite being in a large major city; every time. This must make Google happy. The old TomToms were faster at getting a fix. IIRC, they would take 20—30″ only the first time but quickly got a fix after subsequent power cycles in the same area thereafter.

Smartphones have the sensors to do inertial nav if you calibrate a starting point. But the apps don’t have their shit together yet. I vaguely a recall a FOSS app doing inertial nav, but not too useful if it results in a mock location that OSMand cannot handle.

0

How to support your national postal svc w/out spending your own money -- while fending off surveillance advertisers (Danes move along; this won’t work for you; perhaps not Americans either)

preview

Tl;dr: deliver snail-mail by hand

Most corporations and gov agencies have outsourced email service to a highly unethical corporation (Microsoft). Every time you send an email to a recipient who uses MS for email service, you feed profitable data to a surveillance advertiser who snoops on email payloads for profit. You also reveal to the recipient your email address which they can use to feed profitable data to the surveillance advertiser beyond your control for an indefinite time.

It’s baffling how many people think this is a good idea.

As a Microsoft boycotter, I have naturally reverted back to old-fashioned snail mail. If the recipient is in my city, I personally hand-deliver the letter to their mailbox. Costs me nearly nothing. The recipient who is typically a gov agency or corporation is generally forced to respond using the national postal service (as I withhold email addresses from the correspondence). And rightfully so. It’s an extra perk that they pay a built-in postage penalty for poorly choosing their email provider.

This has been working well for me¹. I spend nothing if the recipient is in cycling range, and the recipient helps fund the national postal service when they respond using an option that is increasingly under the threat of mass digitization by privacy adversaries (MS and Google). Case in point: Denmark ends postal service this year, so it’s already too late there.

To verify whether the recipient’s email traverses a surveillance advertiser:

torsocks dig @8.20.247.20 -t mx -q "$domain" +noclass +nocomments +nostats +short +tcp +nosearch

where $domain is the domain portion of their email address. This command will check whether their vanity address is Microsoft or Google in disguise – which is usually the case. It will usually output “yada yada outlook yada yada” to indicate Microsoft.

If you live remotely, can’t cycle, etc, then stop being cheap and buy stamps. They are cheaper than your Internet subscription which leaves you feeding surveillance advertisers.

¹ Exceptionally, one recipient went to the trouble of collecting my email address from a 3rd party without my consent in order to respond to my snail mail via email hosted by their surveillance advertiser. They naturally received an instant GDPR Article 17 request to erase my email address at that point along with a notice that they violated Article 5 (data minimisation).

Tl;dr: deliver snail-mail by hand

Most corporations and gov agencies have outsourced email service to a highly unethical corporation (Microsoft). Every time you send an email to a recipient who uses MS for email service, you feed profitable data to a surveillance advertiser who snoops on email payloads for profit. You also reveal to the recipient your email address which they can use to feed profitable data to the surveillance advertiser beyond your control for an indefinite time.

It’s baffling how many people think this is a good idea.

As a Microsoft boycotter, I have naturally reverted back to old-fashioned snail mail. If the recipient is in my city, I personally hand-deliver the letter to their mailbox. Costs me nearly nothing. The recipient who is typically a gov agency or corporation is generally forced to respond using the national postal service (as I withhold email addresses from the correspondence). And rightfully so. It’s an extra perk that they pay a built-in postage penalty for poorly choosing their email provider.

This has been working well for me¹. I spend nothing if the recipient is in cycling range, and the recipient helps fund the national postal service when they respond using an option that is increasingly under the threat of mass digitization by privacy adversaries (MS and Google). Case in point: Denmark ends postal service this year, so it’s already too late there.

To verify whether the recipient’s email traverses a surveillance advertiser:

torsocks dig @8.20.247.20 -t mx -q "$domain" +noclass +nocomments +nostats +short +tcp +nosearch

where $domain is the domain portion of their email address. This command will check whether their vanity address is Microsoft or Google in disguise – which is usually the case. It will usually output “yada yada outlook yada yada” to indicate Microsoft.

If you live remotely, can’t cycle, etc, then stop being cheap and buy stamps. They are cheaper than your Internet subscription which leaves you feeding surveillance advertisers.

¹ Exceptionally, one recipient went to the trouble of collecting my email address from a 3rd party without my consent in order to respond to my snail mail via email hosted by their surveillance advertiser. They naturally received an instant GDPR Article 17 request to erase my email address at that point along with a notice that they violated Article 5 (data minimisation).

0

(success story) A fiber carrier drilled into homes without consent to run their cables and used Cloudflare to make their service exclusive -- and how my friend hit back

preview

A new fiber network provider drilled into the façades of private homes to run their cables, without consent, to save themselves the cost of digging. Their website was in Cloudflare’s exclusive walled garden – which means they were drilling people’s façades who were not even necessarily in the included group who could get service.

So my friend hand-delivered a letter and got the receptionist to sign for it (thus can be recognised by a court). The letter objected to the use of their home to deploy a network that exclude everyone Cloudflare excludes, and also said something like “since you had no consent to drill my house and I explicitly object, I will detach your cable on date X. And unless you say otherwise, if you consent to my work then take no action. Your inaction will signal acceptance to my plans.”

The Internet carrier had to employ a lawyer to write a long strongly worded response citing laws and their right to drill people’s façades, which they then had to send using registered mail (these letters are not cheap).

That’s it. My friend did not actually go through with it. But it’s a bit of justice nonetheless because the Internet provider had to pay a lawyer then pay the reg. letter costs. Would be even better if a lot of people would react in this way and help pile on the costs.

Incidentally, the network carrier quit using Cloudflare. They did not state why, but it’s nice to think that it’s possible that they realised the injustice of being exclusive.

A new fiber network provider drilled into the façades of private homes to run their cables, without consent, to save themselves the cost of digging. Their website was in Cloudflare’s exclusive walled garden – which means they were drilling people’s façades who were not even necessarily in the included group who could get service.

So my friend hand-delivered a letter and got the receptionist to sign for it (thus can be recognised by a court). The letter objected to the use of their home to deploy a network that exclude everyone Cloudflare excludes, and also said something like “since you had no consent to drill my house and I explicitly object, I will detach your cable on date X. And unless you say otherwise, if you consent to my work then take no action. Your inaction will signal acceptance to my plans.”

The Internet carrier had to employ a lawyer to write a long strongly worded response citing laws and their right to drill people’s façades, which they then had to send using registered mail (these letters are not cheap).

That’s it. My friend did not actually go through with it. But it’s a bit of justice nonetheless because the Internet provider had to pay a lawyer then pay the reg. letter costs. Would be even better if a lot of people would react in this way and help pile on the costs.

Incidentally, the network carrier quit using Cloudflare. They did not state why, but it’s nice to think that it’s possible that they realised the injustice of being exclusive.

0

The EU gives everyone a right to open a “basic” bank account, but some banks put the application exclusively online

preview

cross-posted from: slrpnk.net/post/12108012

The EU guarantees most people a right to open a “basic”¹ bank account. Superficially that sounds good, but of course having a right to open a bank account implies that you can then be expected to have an account. It’s an enabler for the #warOnCash. The right to a bank account is a masquerade of freedom from which oppression manifests.

Anyway, you have to ask: do you really have a “right” to open a basic bank account if the procedure for opening the account is inherently exclusive? That is, if a bank only offers a basic account to people who are online, doesn’t a problem arise when this right to an account then leads to an assumption that everyone has an account?

Some banks take the requirement to offer basic accounts seriously by making the application a static PDF which can also be obtained on paper form. So the only thing you need is a pen (to open the account and presumably to use it). But it’s bizarre some banks put the application for their basic account exclusively in an interactive online format. Are offline people just getting “lucky” if a bank happens to offer a basic account application on paper?

¹ “basic” is not just common language here. It refers to a specific type of account that fulfills specific legal criteria.

cross-posted from: slrpnk.net/post/12108012

The EU guarantees most people a right to open a “basic”¹ bank account. Superficially that sounds good, but of course having a right to open a bank account implies that you can then be expected to have an account. It’s an enabler for the #warOnCash. The right to a bank account is a masquerade of freedom from which oppression manifests.

Anyway, you have to ask: do you really have a “right” to open a basic bank account if the procedure for opening the account is inherently exclusive? That is, if a bank only offers a basic account to people who are online, doesn’t a problem arise when this right to an account then leads to an assumption that everyone has an account?

Some banks take the requirement to offer basic accounts seriously by making the application a static PDF which can also be obtained on paper form. So the only thing you need is a pen (to open the account and presumably to use it). But it’s bizarre some banks put the application for their basic account exclusively in an interactive online format. Are offline people just getting “lucky” if a bank happens to offer a basic account application on paper?

¹ “basic” is not just common language here. It refers to a specific type of account that fulfills specific legal criteria.

0

US federal law becoming inaccessible (Cloudflare!)

preview

ecfr.gov used to be a decent source for looking up laws. When looking up the anti spam laws, the linked page is littered with links to an access-restricted Cloudflare site (www.govinfo.gov). The important parts of the law are missing from ecfr.gov. It’s common for various states to have this mom-pop shop competency level, but tragic and embarrassing that the US feds lack competency to the point of Cloudflare-dependency.

Often Cornell University publishes federal law and mitigates the embarrassment to some extent. But when looking up the CAN-SPAM law at Cornell, the Cornell law site redirects to another access-restricted Cloudflare site (www.gpo.gov).

There needs to be a fundamental high-level that requires all laws to be accessible to all people, not just people who Cloudflare is willing to give access to.

ecfr.gov used to be a decent source for looking up laws. When looking up the anti spam laws, the linked page is littered with links to an access-restricted Cloudflare site (www.govinfo.gov). The important parts of the law are missing from ecfr.gov. It’s common for various states to have this mom-pop shop competency level, but tragic and embarrassing that the US feds lack competency to the point of Cloudflare-dependency.

Often Cornell University publishes federal law and mitigates the embarrassment to some extent. But when looking up the CAN-SPAM law at Cornell, the Cornell law site redirects to another access-restricted Cloudflare site (www.gpo.gov).

There needs to be a fundamental high-level that requires all laws to be accessible to all people, not just people who Cloudflare is willing to give access to.

0

Eating cheaply

preview

Instead of splurging at restaurants I’ve been making some effort to eat cheaply. I’m not looking to hit ridiculous rock-bottom costs to the point of malnutrition. I’m eating well but I exploit whatever is cheap at each visit to the grocery store. I have yet to cut out junk food… so I could perhaps do better yet.

For the past year, my daily avg cost has been ¾ the cost of a big mac. Anyone else doing this, perhaps motivated by inflation?

There are some youtube videos of people living somewhat harshly and eating bizarre meals in order to get below the $5/day line, which is a magic number for some reason. I got the impression that simulates a welfare amount or something.

(edit)
It seems like there should be an app for this. I heard that aubergine (US: eggplant) is quite low on nutritional value, so I quit buying it on that basis. But then if aubergine is marked 50% off, maybe it has a worthy nutrition for the dollar outlook. In principle I would want to enter a price of something into an app and it should work out whether it’s a good value nutrition wise, not just w.r.t price history of that thing. Maybe this is crazy talk considering the complexity of nutrition.

Instead of splurging at restaurants I’ve been making some effort to eat cheaply. I’m not looking to hit ridiculous rock-bottom costs to the point of malnutrition. I’m eating well but I exploit whatever is cheap at each visit to the grocery store. I have yet to cut out junk food… so I could perhaps do better yet.

For the past year, my daily avg cost has been ¾ the cost of a big mac. Anyone else doing this, perhaps motivated by inflation?

There are some youtube videos of people living somewhat harshly and eating bizarre meals in order to get below the $5/day line, which is a magic number for some reason. I got the impression that simulates a welfare amount or something.

(edit)
It seems like there should be an app for this. I heard that aubergine (US: eggplant) is quite low on nutritional value, so I quit buying it on that basis. But then if aubergine is marked 50% off, maybe it has a worthy nutrition for the dollar outlook. In principle I would want to enter a price of something into an app and it should work out whether it’s a good value nutrition wise, not just w.r.t price history of that thing. Maybe this is crazy talk considering the complexity of nutrition.

0

for climate, boycott all ALEC members (AmEx, Chevron, FedEx, Marlboro, Motorola, Sony, Texaco, etc)

preview

cross-posted from: slrpnk.net/post/4625325

The following corporations are members of #ALEC, a giant far right bill mill and lobbyist in the US who fights environmental protections and promotes #climateDenial. Boycott them:

Notice that FedEx and UPS are both ALEC members. So naturally you should favor your national post. But if you must choose between FedEx and UPS, FedEx is worse because:

  • FedEx supports the NRA discounts. The NRA and ALEC are aligned and support each other and support the same politicians (e.g. Trump).
  • FedEx ships slave dolphins
  • FedEx ships hunting trophies
  • FedEx ships #sharkFins
  • FedEx aggressively claims in advertisements to be pro-environment with low emissions. This misleads consumers as they obviously do not acknowledge how ALEC, NRA, and their other activities are quite detrimental.

All of which are different forms of environmental abuse. So UPS is the lesser of evils IMO.

cross-posted from: slrpnk.net/post/4625325

The following corporations are members of #ALEC, a giant far right bill mill and lobbyist in the US who fights environmental protections and promotes #climateDenial. Boycott them:

Notice that FedEx and UPS are both ALEC members. So naturally you should favor your national post. But if you must choose between FedEx and UPS, FedEx is worse because:

  • FedEx supports the NRA discounts. The NRA and ALEC are aligned and support each other and support the same politicians (e.g. Trump).
  • FedEx ships slave dolphins
  • FedEx ships hunting trophies
  • FedEx ships #sharkFins
  • FedEx aggressively claims in advertisements to be pro-environment with low emissions. This misleads consumers as they obviously do not acknowledge how ALEC, NRA, and their other activities are quite detrimental.

All of which are different forms of environmental abuse. So UPS is the lesser of evils IMO.

0

[COP28] climate experts on vegan-driven activism: not viable. What about nixing livestock subsidies?

BBC BBC World Service - The Climate Question, Your Climate Questions Answered www.bbc.co.uk
preview

cross-posted from: slrpnk.net/post/4664992

(the audio associated to the link will air on BBC World Service again in a couple hours from now [20:00 GMT today], if anyone is on a strained internet uplink) (that’s in the past now)

A panel of climate experts answered questions related to #COP28. Someone asked about the viability of an agenda to get people off animal products. IIRC, the answers basically boiled down to:

  • An elected politician telling people not to eat meat would be political suicide
  • Nutrition would be a problem

IMO both answers are accurate. But isn’t there an oversight in terms of subsidies? The US gives huge subsidies to farmers and that includes livestock subsidies (not sure about other countries). A politician would not get away with intervening in people’s diets but canceling livestock subsidies would not be an intervention - it would actually be non-intervention. Would that still necessarily be political suicide?

W.r.t nutrition, someone who works 2 jobs and struggles for a survivable income would not have time/resources to study avoiding malnutrition on a strictly plant-based diet. So if animal products were priced out of the market for poor people, it would cause real problems, no?

Would it make sense to cut the subsidies, let animal product prices skyrocket, but then put the subsidies on the consumer side so overworked underpaid workers could maintain their diets? Apart from that, it seems a bit shitty that vegan taxpayers still finance animal exploitation by simply paying their tax.

Are there any states/countries known to not subsidize animal exploitation, where vegans can be vegan in the most absolute sense?

cross-posted from: slrpnk.net/post/4664992

(the audio associated to the link will air on BBC World Service again in a couple hours from now [20:00 GMT today], if anyone is on a strained internet uplink) (that’s in the past now)

A panel of climate experts answered questions related to #COP28. Someone asked about the viability of an agenda to get people off animal products. IIRC, the answers basically boiled down to:

  • An elected politician telling people not to eat meat would be political suicide
  • Nutrition would be a problem

IMO both answers are accurate. But isn’t there an oversight in terms of subsidies? The US gives huge subsidies to farmers and that includes livestock subsidies (not sure about other countries). A politician would not get away with intervening in people’s diets but canceling livestock subsidies would not be an intervention - it would actually be non-intervention. Would that still necessarily be political suicide?

W.r.t nutrition, someone who works 2 jobs and struggles for a survivable income would not have time/resources to study avoiding malnutrition on a strictly plant-based diet. So if animal products were priced out of the market for poor people, it would cause real problems, no?

Would it make sense to cut the subsidies, let animal product prices skyrocket, but then put the subsidies on the consumer side so overworked underpaid workers could maintain their diets? Apart from that, it seems a bit shitty that vegan taxpayers still finance animal exploitation by simply paying their tax.

Are there any states/countries known to not subsidize animal exploitation, where vegans can be vegan in the most absolute sense?