0

This community is indefinitely defunct on Lemmy

preview

r/privatelife on Reddit is once again the primary and sole host for this community. Any further communication will be on Reddit or Telegram. Thanks for the attention!
r/privatelife on Reddit is once again the primary and sole host for this community. Any further communication will be on Reddit or Telegram. Thanks for the attention!
0

Why free software?!

preview

People here’s take about why free software (“open source”) should be preferred, in my opinion (basically the OpenBSD’s opinion) is flawed.

You said “open source” is “good” because it permits having eyes on (“auditing”) and make sure there isn’t malware.

This is NOT the most important benefit. But it is flawed because, you guys don’t even have the knowledge to do coding. You guys are activist/“journalists” working for CIA. So you cannot audit the software yourselves.

Or “open source” but with a bad code style, how can you make sure the code doesn’t have backdoors? But I think hilarious journalists that is only smart enough to post fake news about how down is the Russia and China economy can’t even write bad code.

“open source” is good, firstly, because it permits auditing the source code and find the bugs, replace flawed/bad code with safer alternative (for example, the advantage of an open-source C software when porting to OpenBSD is they can replace every occurrence of strcat/strcpy with safer strlcat/strlcpy), sandbox it (on OpenBSD, with pledge and unveil), do privileges separation and revocation, etc.

And I think “you can make sure there isn’t malware/backdoors” is the second benefit, NEVER THE FIRST.

Conclusion: Do not blindly trust what is “open source” when you can’t even do code auditing.

People here’s take about why free software (“open source”) should be preferred, in my opinion (basically the OpenBSD’s opinion) is flawed.

You said “open source” is “good” because it permits having eyes on (“auditing”) and make sure there isn’t malware.

This is NOT the most important benefit. But it is flawed because, you guys don’t even have the knowledge to do coding. You guys are activist/“journalists” working for CIA. So you cannot audit the software yourselves.

Or “open source” but with a bad code style, how can you make sure the code doesn’t have backdoors? But I think hilarious journalists that is only smart enough to post fake news about how down is the Russia and China economy can’t even write bad code.

“open source” is good, firstly, because it permits auditing the source code and find the bugs, replace flawed/bad code with safer alternative (for example, the advantage of an open-source C software when porting to OpenBSD is they can replace every occurrence of strcat/strcpy with safer strlcat/strlcpy), sandbox it (on OpenBSD, with pledge and unveil), do privileges separation and revocation, etc.

And I think “you can make sure there isn’t malware/backdoors” is the second benefit, NEVER THE FIRST.

Conclusion: Do not blindly trust what is “open source” when you can’t even do code auditing.

0

How's "made in Germany" on a website any better data-protection wise than "made in South Africa, Indonesia, Bolivia"?

preview

Whenever I encounter the label “made in EU”, “Germany”, “Estonia”, “France” … in the footer of a web project, which implies enhanced data-protection, apparently, I wonder:

How can it be so? There’re some data-protection laws, yes. But one can’t control a hosting provider 24h/day. One can’t know whether an employer there copies all data on his memory-drivers.

Can’t the police, if need be, seize a server as easily as it would in any other country on Earth?

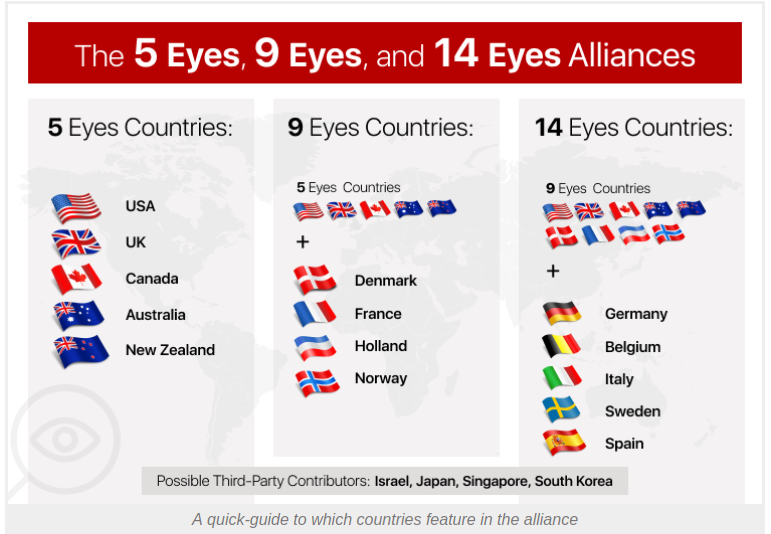
Don’t the majority of all of countries in Europe share information with the intelligence of US by the agreements of the 5 eyes, 9 eyes, 14 eyes? Whereas the 2nd and 3rd world countries don’t.

How is it better than a label “made in South Africa”, “Thailand”, “Costa Rica”, “Egypt”, “Kuwait”?

I can see how “made in Germany” or EU makes a project worse in terms of privacy and data-protection. How could it make it better, though?

Whenever I encounter the label “made in EU”, “Germany”, “Estonia”, “France” … in the footer of a web project, which implies enhanced data-protection, apparently, I wonder:

How can it be so? There’re some data-protection laws, yes. But one can’t control a hosting provider 24h/day. One can’t know whether an employer there copies all data on his memory-drivers.

Can’t the police, if need be, seize a server as easily as it would in any other country on Earth?

Don’t the majority of all of countries in Europe share information with the intelligence of US by the agreements of the 5 eyes, 9 eyes, 14 eyes? Whereas the 2nd and 3rd world countries don’t.

How is it better than a label “made in South Africa”, “Thailand”, “Costa Rica”, “Egypt”, “Kuwait”?

I can see how “made in Germany” or EU makes a project worse in terms of privacy and data-protection. How could it make it better, though?

0

Migrating off of Onedrive / Google Drive

preview

I’m undertaking the process of disentangling Google and Microsoft from my life. Does anyone have any tips for removing my last 20 years of files from Onedrive and Google Drive? Where do you host your long-term storage? What’s a good way to handle the migration?

I’m undertaking the process of disentangling Google and Microsoft from my life. Does anyone have any tips for removing my last 20 years of files from Onedrive and Google Drive? Where do you host your long-term storage? What’s a good way to handle the migration?

0

Ex-minister predicts ‘battle royale’ over US firm’s bid for NHS data contract

the Guardian Ex-minister predicts ‘battle royale’ over US firm’s bid for NHS data contract www.theguardian.com
preview

A former cabinet minister has warned that there could be a “battle royale” over a £480m NHS England data software contract sought by the controversial US tech firm Palantir, whose chair has accused the UK health service of “making people sick”.

David Davis, the Conservative former Brexit secretary who previously led the campaign against ID cards, said he was one of those with serious privacy concerns about Palantir’s bid. He is among at least a dozen MPs and peers across the political spectrum who are pressing the government for more reassurances about how patient data will be treated as the new data operating system is built.

Palantir, which grew out of a US spy organisation, is the frontrunner for the contract after it worked for almost nothing to create data software for the NHS during the Covid pandemic.

A former cabinet minister has warned that there could be a “battle royale” over a £480m NHS England data software contract sought by the controversial US tech firm Palantir, whose chair has accused the UK health service of “making people sick”.

David Davis, the Conservative former Brexit secretary who previously led the campaign against ID cards, said he was one of those with serious privacy concerns about Palantir’s bid. He is among at least a dozen MPs and peers across the political spectrum who are pressing the government for more reassurances about how patient data will be treated as the new data operating system is built.

Palantir, which grew out of a US spy organisation, is the frontrunner for the contract after it worked for almost nothing to create data software for the NHS during the Covid pandemic.

0

There is a telegram group for the sub, but no matrix room?

preview

A matrix room can easily be bridged into a telegram group. It’d be nice to have a privacy matrix room than isn’t run by ptio/privacy-guide’s jonah.

A matrix room can easily be bridged into a telegram group. It’d be nice to have a privacy matrix room than isn’t run by ptio/privacy-guide’s jonah.