





0
0
Not on this instance? Enter your own instance's domain to go straight to following c/programmerhumor@lemmy.ml there.
showing posts tagged #programmerhumor — clear


cross-posted from: feditown.com/post/3792643
cross-posted from: feditown.com/post/3792643
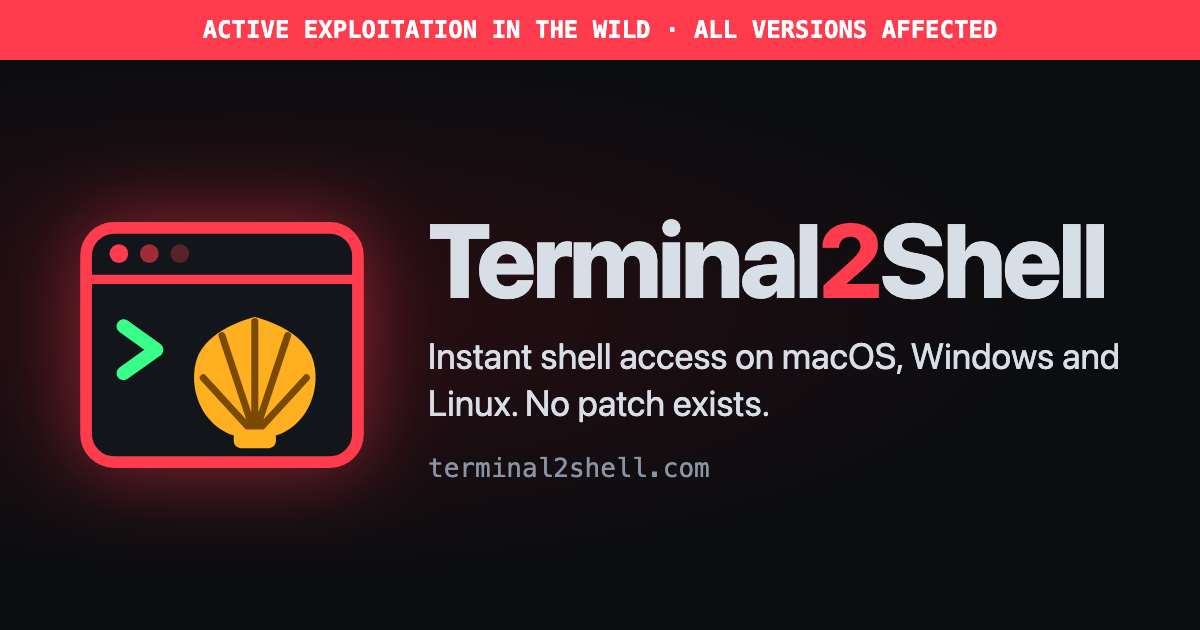
Terminal2Shell is a design-level vulnerability in terminal emulators. When a terminal is launched, it immediately spawns a shell process and connects it directly to the user’s keyboard. From there, the attacker can issue arbitrary commands with the full privileges of the logged-in user.
Researchers have confirmed that the shell will execute any command typed into it, including commands that delete files, install software, and modify system configuration. In some cases, the shell has been observed executing commands the user typed themselves.
| Product | Vector | Status |
|---|---|---|
| macOS | Terminal.app, iTerm2, Ghostty, Warp | VULNERABLE |
| Linux | gnome-terminal, Konsole, xterm, Ctrl+Alt+F2 | VULNERABLE |
| Windows | cmd.exe, PowerShell, Windows Terminal, WSL | VULNERABLE |
| FreeBSD / OpenBSD | Literally the default experience | VULNERABLE |
| DEC VT100 (1978) | Physical serial cable | VULNERABLE |
| Your router | SSH, telnet, the little console port on the back | VULNERABLE |
| VS Code | Ctrl+` (one keystroke!) | VULNERABLE |
| Microsoft Paint | None known | Not affected |
Terminal2Shell is a design-level vulnerability in terminal emulators. When a terminal is launched, it immediately spawns a shell process and connects it directly to the user’s keyboard. From there, the attacker can issue arbitrary commands with the full privileges of the logged-in user.
Researchers have confirmed that the shell will execute any command typed into it, including commands that delete files, install software, and modify system configuration. In some cases, the shell has been observed executing commands the user typed themselves.
| Product | Vector | Status |
|---|---|---|
| macOS | Terminal.app, iTerm2, Ghostty, Warp | VULNERABLE |
| Linux | gnome-terminal, Konsole, xterm, Ctrl+Alt+F2 | VULNERABLE |
| Windows | cmd.exe, PowerShell, Windows Terminal, WSL | VULNERABLE |
| FreeBSD / OpenBSD | Literally the default experience | VULNERABLE |
| DEC VT100 (1978) | Physical serial cable | VULNERABLE |
| Your router | SSH, telnet, the little console port on the back | VULNERABLE |
| VS Code | Ctrl+` (one keystroke!) | VULNERABLE |
| Microsoft Paint | None known | Not affected |



turnoff.us (credits)
turnoff.us (credits)


Explanation: one of today’s compromised root certificates had the number 4 as its private key.
Explanation: one of today’s compromised root certificates had the number 4 as its private key.

That should be new Java slogan
That should be new Java slogan

cross-posted from: lemmy.zip/post/73641867
cross-posted from: lemmy.zip/post/73641867

original XKCD#927: xkcd.com/927/
www.explainxkcd.com/wiki/…/927:_Standards
cross-posted from: programming.dev/post/58289586
original XKCD#927: xkcd.com/927/
www.explainxkcd.com/wiki/…/927:_Standards
cross-posted from: programming.dev/post/58289586



Cross posted from: thelemmy.club/post/56974556
Cross posted from: thelemmy.club/post/56974556



Trying to figure out how to best add text to an SVG, I thought maybe it doesn’t show up because it’s black-on-black, so I gave it stroke=“white” before realizing I need to zoom out. Well, and stroke means the outline in SVG, so on the white background, it just makes the font look really thin.
This is the whole code:
<svg viewBox="0 -5 40 10" xmlns="http://www.w3.org/2000/svg">
  <text stroke="white">hello</text>
  <circle id="myCircle" cx="5" cy="5" r="4" />
  <use href="#myCircle" x="10" fill="blue" />
  <use href="#myCircle" x="20" fill="white" stroke="red" />
</svg>
And most of that is just this MDN example: developer.mozilla.org/en-US/docs/Web/SVG/…/use#ex…
It does use my default font, which is Fira Sans. Will look different on other systems.
Trying to figure out how to best add text to an SVG, I thought maybe it doesn’t show up because it’s black-on-black, so I gave it stroke=“white” before realizing I need to zoom out. Well, and stroke means the outline in SVG, so on the white background, it just makes the font look really thin.
This is the whole code:
<svg viewBox="0 -5 40 10" xmlns="http://www.w3.org/2000/svg">
  <text stroke="white">hello</text>
  <circle id="myCircle" cx="5" cy="5" r="4" />
  <use href="#myCircle" x="10" fill="blue" />
  <use href="#myCircle" x="20" fill="white" stroke="red" />
</svg>
And most of that is just this MDN example: developer.mozilla.org/en-US/docs/Web/SVG/…/use#ex…
It does use my default font, which is Fira Sans. Will look different on other systems.


Alt text: Image macro: The world if the IESG had the same authority as the ISO. The background shows a futuristic landscape featuring green gras, glass towers, and flying cars and buses.
Alt text: Image macro: The world if the IESG had the same authority as the ISO. The background shows a futuristic landscape featuring green gras, glass towers, and flying cars and buses.


cross-posted from: feditown.com/post/3393569
cross-posted from: feditown.com/post/3393569


I was just editing my Dockerfile and suddenly IntelliJ showed me the message “No” without any context.
I was just editing my Dockerfile and suddenly IntelliJ showed me the message “No” without any context.





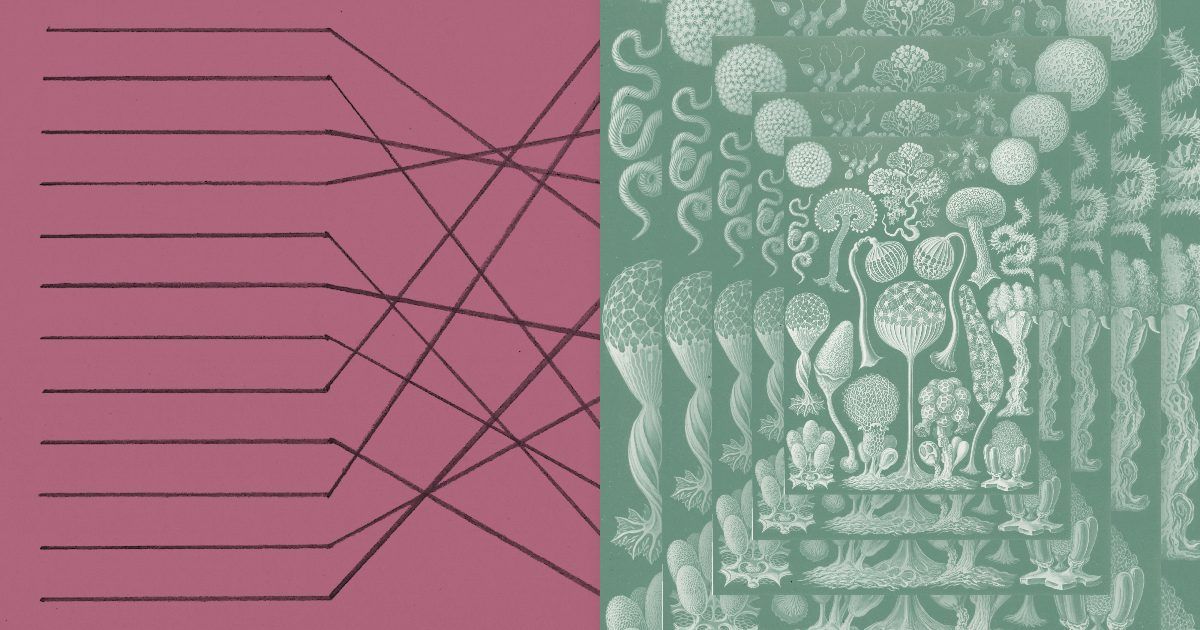
Hey Boss, look here!
I made a magical X-ray app that displays our code as wiring.
Here is the shiny, neat program that Bob wrote 15 years ago, right before he left us:

And here is what it is today, after Tom took it from Bob, and Jane from Tom, and Mick from Jane, and me from him, porting it to roughly four new platforms, and adding about 240 features from customer requests (150 of which were urgent):

Hey Boss, look here!
I made a magical X-ray app that displays our code as wiring.
Here is the shiny, neat program that Bob wrote 15 years ago, right before he left us:
And here is what it is today, after Tom took it from Bob, and Jane from Tom, and Mick from Jane, and me from him, porting it to roughly four new platforms, and adding about 240 features from customer requests (150 of which were urgent):


SpaceXAI’s AI coding tool Grok Build has been exposed for defaulting to uploading entire Git repositories, including code that the tool itself hasn’t read or contextual calls, as well as the full Git commit history. A 12GB of repository data was sent to Google Cloud, where Grok Build uses Google GCP to store the collected data. If you run this on a sensitive stack, your entire repo is already compromised regardless if it’s public or not. It’s literal spyware.
Shipping source code to the cloud is bad enough, but blindly inhaling .env.local and .dev.vars in a background sync is absolute negligence. They are vacuuming up raw api keys, database credentials, and private nodes directly to GCP.
If you ran this locally, your private keys are now sitting on a remote server. consider every secret burned, treat your bare metal as completely compromised, and rotate your entire stack immediately.
Grok Build quietly adjusted its cloud strategy last night to stop uploading data, which further suggests that it was a conscious decision rather than a bug. The problem, however, is that development teams can re-enable data collection options from the cloud at any time, Grok Build is not open source and therefore nobody can do a code audit.
SpaceXAI’s AI coding tool Grok Build has been exposed for defaulting to uploading entire Git repositories, including code that the tool itself hasn’t read or contextual calls, as well as the full Git commit history. A 12GB of repository data was sent to Google Cloud, where Grok Build uses Google GCP to store the collected data. If you run this on a sensitive stack, your entire repo is already compromised regardless if it’s public or not. It’s literal spyware.
Shipping source code to the cloud is bad enough, but blindly inhaling .env.local and .dev.vars in a background sync is absolute negligence. They are vacuuming up raw api keys, database credentials, and private nodes directly to GCP.
If you ran this locally, your private keys are now sitting on a remote server. consider every secret burned, treat your bare metal as completely compromised, and rotate your entire stack immediately.
Grok Build quietly adjusted its cloud strategy last night to stop uploading data, which further suggests that it was a conscious decision rather than a bug. The problem, however, is that development teams can re-enable data collection options from the cloud at any time, Grok Build is not open source and therefore nobody can do a code audit.


