0

DPRK Hackers Use ClickFix to Deliver BeaverTail Malware in Crypto Job Scams

preview

Threat actors with ties to the Democratic People’s Republic of Korea (aka DPRK or North Korea) have been observed leveraging ClickFix-style lures to deliver a known malware called BeaverTail and InvisibleFerret.

Threat actors with ties to the Democratic People’s Republic of Korea (aka DPRK or North Korea) have been observed leveraging ClickFix-style lures to deliver a known malware called BeaverTail and InvisibleFerret.

0

Honeypot or just vv irresponsible database?

preview

This was sent to me but one of my tech illiterate friends. Thoughts on this? Seems sketchy af. The video on TikTok is like, “It’s fun. Add your person.” Being that it’s all federal offense to dox the ice nazis, I’m feeling like this shit is a honeypot?

Edit:turns out the picture uploaded to my cache on my browser but not to the server so this post looked dumb and empty. Put the picture below in the comment thread.

This was sent to me but one of my tech illiterate friends. Thoughts on this? Seems sketchy af. The video on TikTok is like, “It’s fun. Add your person.” Being that it’s all federal offense to dox the ice nazis, I’m feeling like this shit is a honeypot?

Edit:turns out the picture uploaded to my cache on my browser but not to the server so this post looked dumb and empty. Put the picture below in the comment thread.

0

The North Korea worker problem is bigger than you think

CyberScoop The North Korea worker problem is bigger than you think cyberscoop.com
preview

Financially motivated by salaries now, but what’s next?

For now, North Korean technical workers are focused on attaining employment, doing those jobs, and sending the money they earn back to Pyongyang.

North Korean technical workers generate hundreds of millions of dollars for the North Korean regime, according to Unit 42.

Financially motivated by salaries now, but what’s next?

For now, North Korean technical workers are focused on attaining employment, doing those jobs, and sending the money they earn back to Pyongyang.

North Korean technical workers generate hundreds of millions of dollars for the North Korean regime, according to Unit 42.

0

Subaru Starlink flaw let hackers hijack cars in US and Canada

BleepingComputer Subaru Starlink flaw let hackers hijack cars in US and Canada www.bleepingcomputer.com
preview

Security researchers have discovered an arbitrary account takeover flaw in Subaru’s Starlink service that could let attackers track, control, and hijack vehicles in the United States, Canada, and Japan using just a license plate.

Curry says Subaru patched the vulnerability within 24 hours of the researchers’ report and was never exploited by an attacker.

Security researchers have discovered an arbitrary account takeover flaw in Subaru’s Starlink service that could let attackers track, control, and hijack vehicles in the United States, Canada, and Japan using just a license plate.

Curry says Subaru patched the vulnerability within 24 hours of the researchers’ report and was never exploited by an attacker.

0

Hackers use Windows RID hijacking to create hidden admin account

BleepingComputer Hackers use Windows RID hijacking to create hidden admin account www.bleepingcomputer.com
preview

A North Korean threat group has been using a technique called RID hijacking that tricks Windows into treating a low-privileged account as one with administrator permissions.

A North Korean threat group has been using a technique called RID hijacking that tricks Windows into treating a low-privileged account as one with administrator permissions.

0

Hacker infects 18,000 "script kiddies" with fake malware builder

preview

The CloudSEK researchers disrupted the botnet by utilizing hard-coded API tokens and a built-in kill switch to uninstall the malware from infected devices.

The CloudSEK researchers disrupted the botnet by utilizing hard-coded API tokens and a built-in kill switch to uninstall the malware from infected devices.

0

Mirai Variant Murdoc Botnet Exploits AVTECH IP Cameras and Huawei Routers

preview

To safeguard against such attacks, it’s advised to monitor suspicious processes, events, and network traffic spawned by the execution of any untrusted binary/scripts. It’s also recommended to apply firmware updates and change the default username and password.

To safeguard against such attacks, it’s advised to monitor suspicious processes, events, and network traffic spawned by the execution of any untrusted binary/scripts. It’s also recommended to apply firmware updates and change the default username and password.

0

Malicious PyPi package steals Discord auth tokens from devs

preview

A malicious package named ‘pycord-self’ on the Python package index (PyPI) targets Discord developers to steal authentication tokens and plant a backdoor for remote control over the system.

A malicious package named ‘pycord-self’ on the Python package index (PyPI) targets Discord developers to steal authentication tokens and plant a backdoor for remote control over the system.

0

CISA and US and International Partners Publish Guidance for OT Owners and Operators

Dark Reading CISA and US and International Partners Publish Guidance for OT Owners and Operators www.darkreading.com
preview

CISA: Secure by Demand: Priority Considerations for Operational Technology Owners and Operators when Selecting Digital Products

CISA: Secure by Demand: Priority Considerations for Operational Technology Owners and Operators when Selecting Digital Products

0

Apple Bug Allows Security Bypass Without Physical Access

Dark Reading Apple Bug Allows Security Bypass Without Physical Access www.darkreading.com
preview

cross-posted from: lemmy.zip/post/30049292

Emergent macOS vulnerability lets adversaries circumvent Apple’s System Integrity Protection (SIP) by loading third-party kernels.

cross-posted from: lemmy.zip/post/30049292

Emergent macOS vulnerability lets adversaries circumvent Apple’s System Integrity Protection (SIP) by loading third-party kernels.

0

Google OAuth Vulnerability Exposes Millions via Failed Startup Domains

preview

New research has pulled back the curtain on a “deficiency” in Google’s “Sign in with Google” authentication flow that exploits a quirk in domain ownership to gain access to sensitive data.

New research has pulled back the curtain on a “deficiency” in Google’s “Sign in with Google” authentication flow that exploits a quirk in domain ownership to gain access to sensitive data.

0

Biden White House to go all out in final, sweeping cybersecurity order

CSO Online Biden White House goes all out in final, sweeping cybersecurity order www.csoonline.com
preview

The ambitious final executive order requires 52 agency actions to bolster cyber protections and counter adversaries, including a new plan to address spiraling digital identity theft.

The ambitious final executive order requires 52 agency actions to bolster cyber protections and counter adversaries, including a new plan to address spiraling digital identity theft.

0

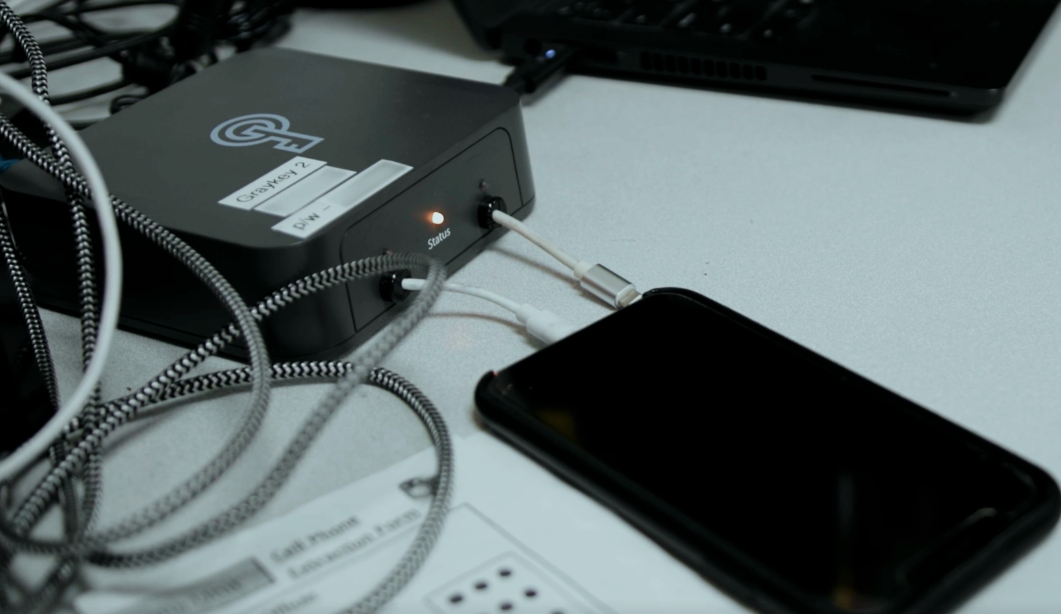
Leaks Show Which Phones Secretive Tech ‘Graykey’ Can Unlock

404 Media Leaked Documents Show What Phones Secretive Tech ‘Graykey’ Can Unlock www.404media.co
preview

Archive Today mirror: archive.ph/JTLIU

AI summary

The webpage discusses leaked documents revealing the capabilities of Graykey, a phone unlocking and forensics tool utilized by law enforcement globally. According to the documents obtained by 404 Media, Graykey can retrieve only partial data from modern iPhones running iOS 18 and iOS 18.0.1. There is no information on its functionality with the recently released iOS 18.1. This leak is significant for Grayshift, the company behind Graykey, especially since it has been acquired by Magnet Forensics, another player in the digital forensics field. Unlike its competitor Cellebrite, which has experienced similar leaks, this is the first detailed disclosure of the specific phones Graykey can and cannot access. The documents also provide insights into Graykey’s capabilities with Android devices. Overall, this situation highlights the ongoing struggle between forensics tools and phone manufacturers like Apple and Google. The information indicates a complex interplay in the evolving landscape of mobile device security and law enforcement access.

Archive Today mirror: archive.ph/JTLIU

AI summary

The webpage discusses leaked documents revealing the capabilities of Graykey, a phone unlocking and forensics tool utilized by law enforcement globally. According to the documents obtained by 404 Media, Graykey can retrieve only partial data from modern iPhones running iOS 18 and iOS 18.0.1. There is no information on its functionality with the recently released iOS 18.1. This leak is significant for Grayshift, the company behind Graykey, especially since it has been acquired by Magnet Forensics, another player in the digital forensics field. Unlike its competitor Cellebrite, which has experienced similar leaks, this is the first detailed disclosure of the specific phones Graykey can and cannot access. The documents also provide insights into Graykey’s capabilities with Android devices. Overall, this situation highlights the ongoing struggle between forensics tools and phone manufacturers like Apple and Google. The information indicates a complex interplay in the evolving landscape of mobile device security and law enforcement access.

0

Global infostealer malware operation targets crypto users, gamers

BleepingComputer Global infostealer malware operation targets crypto users, gamers www.bleepingcomputer.com
preview

The threat actors use a variety of distribution channels, including malvertising, spearphishing, and brand impersonation in online gaming, cryptocurrency, and software, to spread 50 malware payloads, including AMOS, Stealc, and Rhadamanthys.

Victims are lured into downloading malicious software by interacting with what they are tricked into believing are legitimate job opportunities or project collaborations.

On Windows, HijackLoader is used for delivering Stealc, a general-purpose lightweight info-stealer designed to collect data from browsers and crypto wallet apps, or Rhadamanthys, a more specialized stealer that targets a broad range of applications and data types.

When the target uses macOS, Marko Polo deploys Atomic (‘AMOS’). This stealer launched in mid-2023, rented to cybercriminals for $1,000/month, allowing them to snatch various data stored in web browsers.

The threat actors use a variety of distribution channels, including malvertising, spearphishing, and brand impersonation in online gaming, cryptocurrency, and software, to spread 50 malware payloads, including AMOS, Stealc, and Rhadamanthys.

Victims are lured into downloading malicious software by interacting with what they are tricked into believing are legitimate job opportunities or project collaborations.

On Windows, HijackLoader is used for delivering Stealc, a general-purpose lightweight info-stealer designed to collect data from browsers and crypto wallet apps, or Rhadamanthys, a more specialized stealer that targets a broad range of applications and data types.

When the target uses macOS, Marko Polo deploys Atomic (‘AMOS’). This stealer launched in mid-2023, rented to cybercriminals for $1,000/month, allowing them to snatch various data stored in web browsers.

0

1.3 million Android-based TV boxes backdoored; researchers still don’t know how

Ars Technica 1.3 million Android-based TV boxes backdoored; researchers still don’t know how arstechnica.com
preview

cross-posted from: programming.dev/post/19431239

Researchers still don’t know the cause of a recently discovered malware infection affecting almost 1.3 million streaming devices running an open source version of Android in almost 200 countries.

cross-posted from: programming.dev/post/19431239

Researchers still don’t know the cause of a recently discovered malware infection affecting almost 1.3 million streaming devices running an open source version of Android in almost 200 countries.

0

Transport for London staff faces systems disruptions after cyberattack

BleepingComputer Transport for London staff faces systems disruptions after cyberattack www.bleepingcomputer.com
preview

Transport for London, the city’s public transportation agency, revealed today that its staff has limited access to systems and email due to measures implemented in response to a Sunday cyberattack.

Transport for London, the city’s public transportation agency, revealed today that its staff has limited access to systems and email due to measures implemented in response to a Sunday cyberattack.

0

North Korean Threat Actors Deploy COVERTCATCH Malware via LinkedIn Job Scams

preview

“After an initial chat conversation, the attacker sent a ZIP file that contained COVERTCATCH malware disguised as a Python coding challenge,” researchers Robert Wallace, Blas Kojusner, and Joseph Dobson said.

The malware functions as a launchpad to compromise the target’s macOS system by downloading a second-stage payload that establishes persistence via Launch Agents and Launch Daemons.

“After an initial chat conversation, the attacker sent a ZIP file that contained COVERTCATCH malware disguised as a Python coding challenge,” researchers Robert Wallace, Blas Kojusner, and Joseph Dobson said.

The malware functions as a launchpad to compromise the target’s macOS system by downloading a second-stage payload that establishes persistence via Launch Agents and Launch Daemons.

0

Apache fixes critical OFBiz remote code execution vulnerability

preview

Tracked as CVE-2024-45195 and discovered by Rapid7 security researchers, this remote code execution flaw is caused by a forced browsing weakness that exposes restricted paths to unauthenticated direct request attacks.

Tracked as CVE-2024-45195 and discovered by Rapid7 security researchers, this remote code execution flaw is caused by a forced browsing weakness that exposes restricted paths to unauthenticated direct request attacks.

0

Hackers Use Fake GlobalProtect VPN Software in New WikiLoader Malware Attack

preview

The malvertising activity, observed in June 2024, is a departure from previously observed tactics wherein the malware has been propagated via traditional phishing emails, Unit 42 researchers Mark Lim and Tom Marsden said.

Definitions:

Malvertising - Internet advertising whose real intention is to deliver malware to the PC when the ad is clicked.

-wordnik

The malvertising activity, observed in June 2024, is a departure from previously observed tactics wherein the malware has been propagated via traditional phishing emails, Unit 42 researchers Mark Lim and Tom Marsden said.

Definitions:

Malvertising - Internet advertising whose real intention is to deliver malware to the PC when the ad is clicked.

-wordnik

0

FTC: Over $110 million lost to Bitcoin ATM scams in 2023

BleepingComputer FTC: Over $110 million lost to Bitcoin ATM scams in 2023 www.bleepingcomputer.com
preview

The U.S. Federal Trade Commission (FTC) has reported a massive increase in losses to Bitcoin ATM scams, nearly ten times the amount from 2020 and reaching over $110 million in 2023.

Bitcoin ATMs are typically located in convenience stores, gas stations, and other busy areas, but instead of dispensing cash like the traditional ATMs they resemble, they allow you to buy and sell cryptocurrency.

The U.S. Federal Trade Commission (FTC) has reported a massive increase in losses to Bitcoin ATM scams, nearly ten times the amount from 2020 and reaching over $110 million in 2023.

Bitcoin ATMs are typically located in convenience stores, gas stations, and other busy areas, but instead of dispensing cash like the traditional ATMs they resemble, they allow you to buy and sell cryptocurrency.

0

New Rust-Based Ransomware Cicada3301 Targets Windows and Linux Systems

preview

Written in Rust and capable of targeting both Windows and Linux/ESXi hosts, Cicada3301 first emerged in June 2024, inviting potential affiliates to join their ransomware-as-a-service (RaaS) platform via an advertisement on the RAMP underground forum.

Written in Rust and capable of targeting both Windows and Linux/ESXi hosts, Cicada3301 first emerged in June 2024, inviting potential affiliates to join their ransomware-as-a-service (RaaS) platform via an advertisement on the RAMP underground forum.

0

D-Link says it is not fixing four RCE flaws in DIR-846W routers

BleepingComputer D-Link says it is not fixing four RCE flaws in DIR-846W routers www.bleepingcomputer.com
preview

Though D-Link acknowledged the security problems and their severity, it noted that they fall under its standard end-of-life/end-of-support policies, meaning there will be no security updates to address them.

Though D-Link acknowledged the security problems and their severity, it noted that they fall under its standard end-of-life/end-of-support policies, meaning there will be no security updates to address them.

0

Docker-OSX image used for security research hit by Apple DMCA takedown

preview

The popular Docker-OSX project has been removed from Docker Hub after Apple filed a DMCA (Digital Millennium Copyright Act) takedown request, alleging that it violated its copyright.

The popular Docker-OSX project has been removed from Docker Hub after Apple filed a DMCA (Digital Millennium Copyright Act) takedown request, alleging that it violated its copyright.

0

Researchers find SQL injection to bypass airport TSA security checks

preview

Researchers Ian Carroll and Sam Curry discovered the vulnerability in FlyCASS, a third-party web-based service that some airlines use to manage the Known Crewmember (KCM) program and the Cockpit Access Security System (CASS). KCM is a Transportation Security Administration (TSA) initiative that allows pilots and flight attendants to skip security screening, and CASS enables authorized pilots to use jumpseats in cockpits when traveling.

Definitions:

SQL injection is a code injection technique used to attack data-driven applications, in which malicious SQL statements are inserted into an entry field for execution.

-Wikipedia

Researchers Ian Carroll and Sam Curry discovered the vulnerability in FlyCASS, a third-party web-based service that some airlines use to manage the Known Crewmember (KCM) program and the Cockpit Access Security System (CASS). KCM is a Transportation Security Administration (TSA) initiative that allows pilots and flight attendants to skip security screening, and CASS enables authorized pilots to use jumpseats in cockpits when traveling.

Definitions:

SQL injection is a code injection technique used to attack data-driven applications, in which malicious SQL statements are inserted into an entry field for execution.

-Wikipedia

0

North Korean hackers exploit Chrome zero-day to deploy rootkit

preview

North Korean hackers have exploited a recently patched Google Chrome zero-day (CVE-2024-7971) to deploy the FudModule rootkit after gaining SYSTEM privileges using a Windows Kernel exploit.

Citrine Sleet targets financial institutions, focusing on cryptocurrency organizations and associated individuals, and has been previously linked to Bureau 121 of North Korea’s Reconnaissance General Bureau.

North Korean hackers have exploited a recently patched Google Chrome zero-day (CVE-2024-7971) to deploy the FudModule rootkit after gaining SYSTEM privileges using a Windows Kernel exploit.

Citrine Sleet targets financial institutions, focusing on cryptocurrency organizations and associated individuals, and has been previously linked to Bureau 121 of North Korea’s Reconnaissance General Bureau.

0

Commercial Spyware Vendors Have a Copycat in Top Russian APT

Dark Reading Commercial Spyware Vendors Have a Copycat in Top Russian APT www.darkreading.com
preview

In the watering-hole attacks, threat actors infected two websites, cabinet.gov[.]mn and mfa.gov[.]mn, which belong to Mongolia’s Cabinet and Ministry of Foreign Affairs. They then injected code to exploit known flaws in iOS and Chrome on Android, with the ultimate goal of hijacking website visitors’ devices.

Definitions:

Watering hole is a computer attack strategy in which an attacker guesses or observes which websites an organization often uses and infects one or more of them with malware. Eventually, some member of the targeted group will become infected.

-Wikipedia

Whereas zero-days are a class of vulnerability that is unknown to a software developer or hardware manufacturer, an N-day is a flaw that is already publicly known but may or may not have a security patch available.

-Dark Reading

In the watering-hole attacks, threat actors infected two websites, cabinet.gov[.]mn and mfa.gov[.]mn, which belong to Mongolia’s Cabinet and Ministry of Foreign Affairs. They then injected code to exploit known flaws in iOS and Chrome on Android, with the ultimate goal of hijacking website visitors’ devices.

Definitions:

Watering hole is a computer attack strategy in which an attacker guesses or observes which websites an organization often uses and infects one or more of them with malware. Eventually, some member of the targeted group will become infected.

-Wikipedia

Whereas zero-days are a class of vulnerability that is unknown to a software developer or hardware manufacturer, an N-day is a flaw that is already publicly known but may or may not have a security patch available.

-Dark Reading

0

FBI: RansomHub ransomware breached 210 victims since February

preview

This relatively new ransomware-as-a-service (RaaS) operation extorts victims in exchange for not leaking stolen files and sells the documents to the highest bidder if negotiations fail. The ransomware group focuses on data-theft-based extortion rather than encrypting victims’ files, although they were also identified as potential buyers of Knight ransomware source code.

Since the start of the year, RansomHub has claimed responsibility for breaching American not-for-profit credit union Patelco, the Rite Aid drugstore chain, the Christie’s auction house, and U.S. telecom provider Frontier Communications. Frontier Communications later warned over 750,000 customers their personal information was exposed in a data breach.

This relatively new ransomware-as-a-service (RaaS) operation extorts victims in exchange for not leaking stolen files and sells the documents to the highest bidder if negotiations fail. The ransomware group focuses on data-theft-based extortion rather than encrypting victims’ files, although they were also identified as potential buyers of Knight ransomware source code.

Since the start of the year, RansomHub has claimed responsibility for breaching American not-for-profit credit union Patelco, the Rite Aid drugstore chain, the Christie’s auction house, and U.S. telecom provider Frontier Communications. Frontier Communications later warned over 750,000 customers their personal information was exposed in a data breach.

0

CISA Launches New Portal to Improve Cyber Reporting

Cybersecurity and Infrastructure Security Agency CISA CISA Launches New Portal to Improve Cyber Reporting | CISA www.cisa.gov
preview

Today, the Cybersecurity and Infrastructure Security Agency (CISA) announces its cyber incident reporting form moved to the new CISA Services Portal as part of its ongoing effort to improve cyber incident reporting.

CISA Services Portal

Today, the Cybersecurity and Infrastructure Security Agency (CISA) announces its cyber incident reporting form moved to the new CISA Services Portal as part of its ongoing effort to improve cyber incident reporting.

CISA Services Portal