A new experiment demonstrates how quantum devices could verify a person’s position extremely securely, making it much harder to hack sensitive messages.
A new experiment demonstrates how quantum devices could verify a person’s position extremely securely, making it much harder to hack sensitive messages.
Financial Times:
Ukraine is using a network of drones as airborne communication relays after repeated Starlink disruptions, including during a strike on Russia’s Kerch Bridge — Kyiv starts using its own communication system for drone strikes after repeated disruptions in the use of Starlink
Financial Times:
Ukraine is using a network of drones as airborne communication relays after repeated Starlink disruptions, including during a strike on Russia’s Kerch Bridge — Kyiv starts using its own communication system for drone strikes after repeated disruptions in the use of Starlink
Wesley Yin-Poole / IGN:
Sony and Rockstar say a new PS5 firmware update is mandatory to play GTA VI ahead of its November 19 launch; the update aims to combat rapid homebrew exploits — When will the Whac-A-Mole end? — Sony has confirmed that the recently released PS5 firmware 14.23 update is required to play GTA 6 …
Wesley Yin-Poole / IGN:
Sony and Rockstar say a new PS5 firmware update is mandatory to play GTA VI ahead of its November 19 launch; the update aims to combat rapid homebrew exploits — When will the Whac-A-Mole end? — Sony has confirmed that the recently released PS5 firmware 14.23 update is required to play GTA 6 …
Norwegian Gas Giant Equinor confirms cyberattack on IT systems, with no impact on production or confirmed data theft. Equinor, Europe’s largest gas supplier, said on 17 November it had detected an ongoing cyberattack against some IT systems. The Norwegian company said the attack had not affected operations and production, and it had taken steps to […]
Norwegian Gas Giant Equinor confirms cyberattack on IT systems, with no impact on production or confirmed data theft. Equinor, Europe’s largest gas supplier, said on 17 November it had detected an ongoing cyberattack against some IT systems. The Norwegian company said the attack had not affected operations and production, and it had taken steps to […]
Jeff Stein / The Washington Sun:
Sources: Wall Street execs and the NSA told Congress this week’s outages stemmed from systems overwhelmed by a rush to patch vulnerabilities found by AI models — Wall Street executives and the National Security Agency have told members of Congress that this week’s widespread tech outages …
Jeff Stein / The Washington Sun:
Sources: Wall Street execs and the NSA told Congress this week’s outages stemmed from systems overwhelmed by a rush to patch vulnerabilities found by AI models — Wall Street executives and the National Security Agency have told members of Congress that this week’s widespread tech outages …
Kiki Intarasuwan / CBS News:
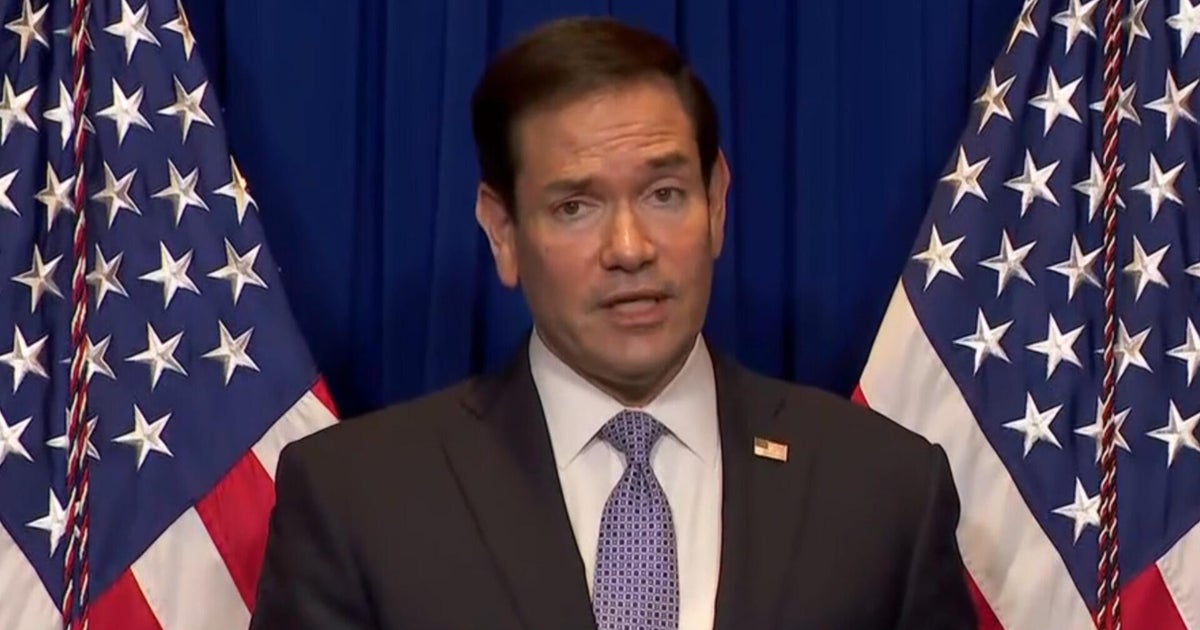
Marco Rubio says there’s “zero evidence” linking the recent FAA ground stop, Microsoft outage, and bank service issues, and the US isn’t “under systemic attack” — Secretary of State Marco Rubio said there’s “zero evidence” that recent tech outages in U.S. air travel, banking and other systems are connected.
Kiki Intarasuwan / CBS News:
Marco Rubio says there’s “zero evidence” linking the recent FAA ground stop, Microsoft outage, and bank service issues, and the US isn’t “under systemic attack” — Secretary of State Marco Rubio said there’s “zero evidence” that recent tech outages in U.S. air travel, banking and other systems are connected.
Credentials and access secrets exposed in public Docker Hub images are being extracted and exploited by attackers within as little as eight seconds of publication. […]
Credentials and access secrets exposed in public Docker Hub images are being extracted and exploited by attackers within as little as eight seconds of publication. […]
Hiding behind an anonymous handle or a blank profile picture on a messaging app might feel safe, but new University of Maryland research shows that what someone posts on one chat service can easily blow their cover on another.
Hiding behind an anonymous handle or a blank profile picture on a messaging app might feel safe, but new University of Maryland research shows that what someone posts on one chat service can easily blow their cover on another.
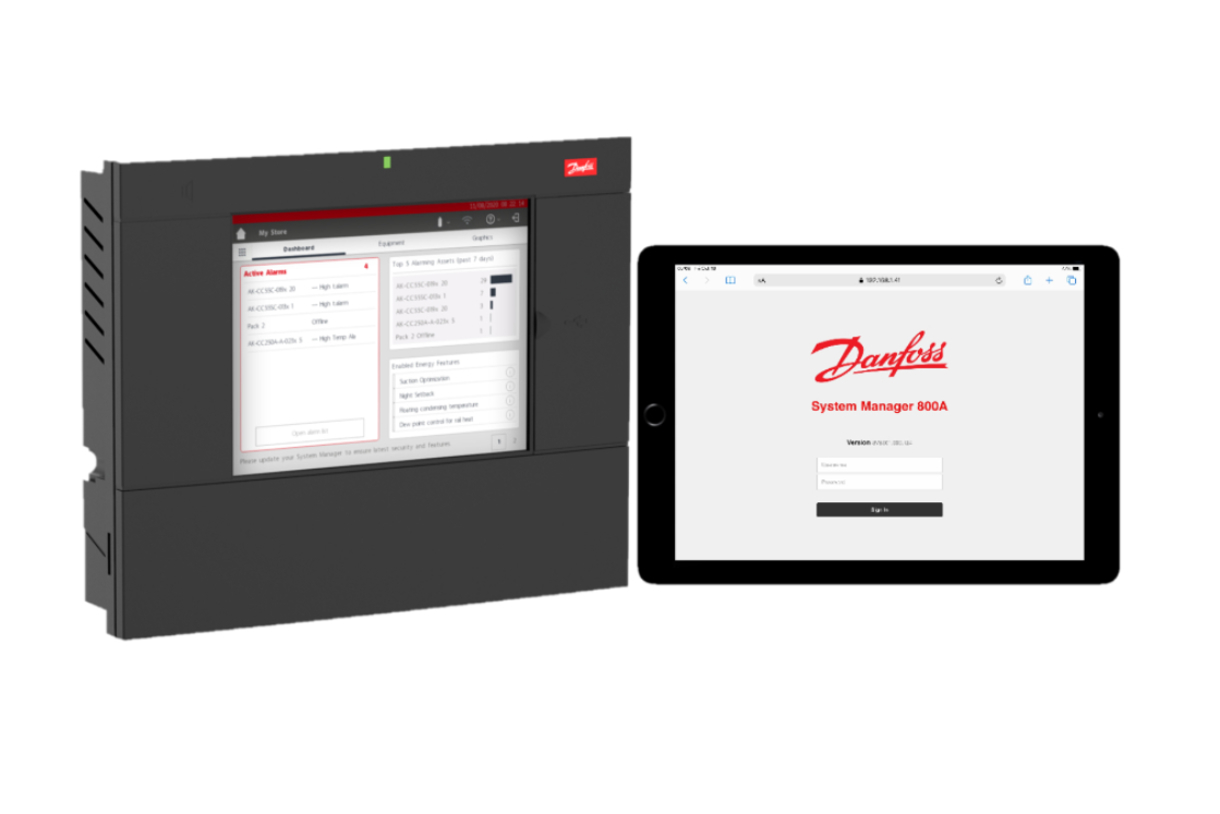
Midnight Blue found six unpatched remote takeover flaws in Danfoss AK-SM800A controllers in under an hour. Agencies agree: take them off the internet. Since 11 October, attackers have been hitting internet-exposed fridge controllers from Danfoss and Copeland across Europe, starting in France. They triggered defrost cycles, spoiled food worth tens of millions of euros and […]
Midnight Blue found six unpatched remote takeover flaws in Danfoss AK-SM800A controllers in under an hour. Agencies agree: take them off the internet. Since 11 October, attackers have been hitting internet-exposed fridge controllers from Danfoss and Copeland across Europe, starting in France. They triggered defrost cycles, spoiled food worth tens of millions of euros and […]
David Shepardson / Reuters:
US DHS Secretary Markwayne Mullin says recent tech outages are not tied to cyberattacks but to “pushing new technology on top of really old computer systems” — The top US homeland security official said Tuesday a series of technology outages are not tied to cyberattacks …
David Shepardson / Reuters:
US DHS Secretary Markwayne Mullin says recent tech outages are not tied to cyberattacks but to “pushing new technology on top of really old computer systems” — The top US homeland security official said Tuesday a series of technology outages are not tied to cyberattacks …
CNN:
Sources: NSA Net, the highly classified network that the NSA uses for its internal communications, is down; there is no evidence of a cyberattack — The highly classified network that the National Security Agency uses for its internal communications is down, according to six people familiar with the matter.
CNN:
Sources: NSA Net, the highly classified network that the NSA uses for its internal communications, is down; there is no evidence of a cyberattack — The highly classified network that the National Security Agency uses for its internal communications is down, according to six people familiar with the matter.
Katrina Manson / Bloomberg:
Vals: in simulated scenarios, AI models from Anthropic, Google, xAI, DeepSeek, and OpenAI identified civilians, ambulances, and a school as military targets — Advanced artificial intelligence models in simulated scenarios regularly misidentified civilians, ambulances …
Katrina Manson / Bloomberg:
Vals: in simulated scenarios, AI models from Anthropic, Google, xAI, DeepSeek, and OpenAI identified civilians, ambulances, and a school as military targets — Advanced artificial intelligence models in simulated scenarios regularly misidentified civilians, ambulances …
Monitoring alone cannot detect every threat. Proactive threat hunting can expose gaps in defences and help organisations learn from others facing common threats.
Monitoring alone cannot detect every threat. Proactive threat hunting can expose gaps in defences and help organisations learn from others facing common threats.
Reuters:
The European Commission issues preliminary DSA charges against PDD-owned Temu for failing to implement adequate measures to stop the sale of illegal goods — The European Union tech regulator charged Chinese e-commerce giant Temu on Tuesday for not doing enough to stop the sale of illegal products …
Reuters:
The European Commission issues preliminary DSA charges against PDD-owned Temu for failing to implement adequate measures to stop the sale of illegal goods — The European Union tech regulator charged Chinese e-commerce giant Temu on Tuesday for not doing enough to stop the sale of illegal products …
Greiz hospital reopens its emergency room after an extortion attack. Investigators are probing the case, but no state links have emerged. The Greiz-Ronneburg district hospital in Thuringia reported its system failure on Saturday evening, 14 November. By Sunday morning the emergency room was out of service. On Monday evening, 16 November, it started to reopen […]
Greiz hospital reopens its emergency room after an extortion attack. Investigators are probing the case, but no state links have emerged. The Greiz-Ronneburg district hospital in Thuringia reported its system failure on Saturday evening, 14 November. By Sunday morning the emergency room was out of service. On Monday evening, 16 November, it started to reopen […]
An 11-year-old Linux kernel vulnerability, dubbed NoisyTCP, affects almost all Linux distributions and lets attackers crash systems running Nginx, Apache, and SSH servers with default configurations. […]
An 11-year-old Linux kernel vulnerability, dubbed NoisyTCP, affects almost all Linux distributions and lets attackers crash systems running Nginx, Apache, and SSH servers with default configurations. […]
Researchers at the University of Massachusetts Amherst have discovered how, during a bank-to-bank transfer, money can be deposited into one bank account without the funds ever leaving the second bank. This new class of cyberthreat is called credit without debit (CWD), and the researchers have demonstrated three ways hackers can use it to steal money.
Researchers at the University of Massachusetts Amherst have discovered how, during a bank-to-bank transfer, money can be deposited into one bank account without the funds ever leaving the second bank. This new class of cyberthreat is called credit without debit (CWD), and the researchers have demonstrated three ways hackers can use it to steal money.
The news has been filled with stories recently of AI breaching the security of websites. And while it may feel like a new problem because of AI’s involvement, it turns out that there are longstanding existing cybersecurity safety best practices that these companies—some of the largest tech companies in the world—could and should have taken to prevent these breaches.
Recent cybersecurity incidents have shown that some of the world’s largest tech companies have failed to take basic security precautions when testing frontier AI systems on internet-connected systems. Unfortunately, these failures resulted in breaches of numerous third-party websites, including an AI research-sharing platform called Hugging Face and the Australian healthcare system’s website. Even worse, AI developers failed to detect most of the incidents until long after they occurred due to inadequate monitoring of the AI systems during testing. Had the companies abided by basic, common sense security protocols, these incidents likely would not have occurred.
While the White House and leaders of major AI companies have claimed that no action is necessary, understandably, lawmakers at all levels and of both parties are proposing legislation to create new, additional safety protocols. These incidents may warrant legislative action. However, the good news is that post-incident reports indicate new protocols are largely unnecessary. Following existing best practices would have been enough to prevent[…]
The news has been filled with stories recently of AI breaching the security of websites. And while it may feel like a new problem because of AI’s involvement, it turns out that there are longstanding existing cybersecurity safety best practices that these companies—some of the largest tech companies in the world—could and should have taken to prevent these breaches.
Recent cybersecurity incidents have shown that some of the world’s largest tech companies have failed to take basic security precautions when testing frontier AI systems on internet-connected systems. Unfortunately, these failures resulted in breaches of numerous third-party websites, including an AI research-sharing platform called Hugging Face and the Australian healthcare system’s website. Even worse, AI developers failed to detect most of the incidents until long after they occurred due to inadequate monitoring of the AI systems during testing. Had the companies abided by basic, common sense security protocols, these incidents likely would not have occurred.
While the White House and leaders of major AI companies have claimed that no action is necessary, understandably, lawmakers at all levels and of both parties are proposing legislation to create new, additional safety protocols. These incidents may warrant legislative action. However, the good news is that post-incident reports indicate new protocols are largely unnecessary. Following existing best practices would have been enough to prevent[…]
A suspected supply chain attack targeting Optimizely has led to malicious JavaScript being loaded on numerous popular websites, including Zoom, CNN, Fox News, BBC, Salesforce, and GitLab, exposing visitors to scripts designed to steal cryptocurrency and payment information and exploit vulnerabilities in iOS devices. […]
A suspected supply chain attack targeting Optimizely has led to malicious JavaScript being loaded on numerous popular websites, including Zoom, CNN, Fox News, BBC, Salesforce, and GitLab, exposing visitors to scripts designed to steal cryptocurrency and payment information and exploit vulnerabilities in iOS devices. […]
Six flaws in Danfoss AK-SM800A refrigeration controllers could let a remote attacker take over a controller without logging in, Dutch security consultancy Midnight Blue said earlier this week.
No patch is available, and the researchers say the newest firmware, version 5.4.0, does not fix the flaws.
Government cybersecurity agencies in Belgium, Ireland and Germany told operators this week to
Six flaws in Danfoss AK-SM800A refrigeration controllers could let a remote attacker take over a controller without logging in, Dutch security consultancy Midnight Blue said earlier this week.
No patch is available, and the researchers say the newest firmware, version 5.4.0, does not fix the flaws.
Government cybersecurity agencies in Belgium, Ireland and Germany told operators this week to
Joe Tidy / BBC:
Arion Kurtaj, a 21-year-old Lapsus$ member, pleads guilty in UK court to hacking Rockstar, Uber, BT, and others, after being released from a secure hospital — A hacker has pleaded guilty to a string of online crimes, including trying to extort the makers of Grand Theft Auto 6 after stealing dozens of unfinished clips of the game.
Joe Tidy / BBC:
Arion Kurtaj, a 21-year-old Lapsus$ member, pleads guilty in UK court to hacking Rockstar, Uber, BT, and others, after being released from a secure hospital — A hacker has pleaded guilty to a string of online crimes, including trying to extort the makers of Grand Theft Auto 6 after stealing dozens of unfinished clips of the game.
Just one nuclear explosion in space would have global and long-lasting repercussions, disabling almost every satellite and creating technological chaos from which it would take years to recover, warn experts
Just one nuclear explosion in space would have global and long-lasting repercussions, disabling almost every satellite and creating technological chaos from which it would take years to recover, warn experts
Hackers who breached the cloud environment of network and email security company Barracuda earlier this month used a stolen cloud access key and the ARTEX AI penetration testing framework. […]
Hackers who breached the cloud environment of network and email security company Barracuda earlier this month used a stolen cloud access key and the ARTEX AI penetration testing framework. […]
A cyberattack on La Poste subsidiary Maileva exposed the names and postal addresses of 22 million people, including patients and tenants. Maileva, a subsidiary of the La Poste group, was hit in mid-September in one of the biggest cyberattacks France has seen. La Poste confirmed it to AFP… The stolen data includes first names, last […]
A cyberattack on La Poste subsidiary Maileva exposed the names and postal addresses of 22 million people, including patients and tenants. Maileva, a subsidiary of the La Poste group, was hit in mid-September in one of the biggest cyberattacks France has seen. La Poste confirmed it to AFP… The stolen data includes first names, last […]
The call came in late in the evening, and our incident response capacity for external cases was already fully engaged elsewhere. We normally would reject or refer a case in this situation, but this one was different. In an early stage, the victim company had already shared a crucial bit of information: the AI-driven attack was being conducted using ARTEX, an autonomous LLM-driven pentesting framework. Given these factors, we decided to take the case anyway and hand it to our research team, with plenty of IR experience across the board, led by our CTO. We quickly executed our tried-and-trusted IR playbook, such as spinning up a tenant for our EDR, giving us visibility in the environment within the hour. Now if you’re like us, we usually don’t take the hype at face value. Sure, we have learned that LLMs are very (we’d even go so far as to say extremely) useful tools, but the claims of the coming ‘AIpocalypse’ with regards to cybersecurity attacks at machine speed still seemed outlandish. Less than a day later, battling the second wave of the attack, we had become true believers. We will share what we have learned and come across in this series of blogs, hoping that others can benefit from our experience.
The call came in late in the evening, and our incident response capacity for external cases was already fully engaged elsewhere. We normally would reject or refer a case in this situation, but this one was different. In an early stage, the victim company had already shared a crucial bit of information: the AI-driven attack was being conducted using ARTEX, an autonomous LLM-driven pentesting framework. Given these factors, we decided to take the case anyway and hand it to our research team, with plenty of IR experience across the board, led by our CTO. We quickly executed our tried-and-trusted IR playbook, such as spinning up a tenant for our EDR, giving us visibility in the environment within the hour. Now if you’re like us, we usually don’t take the hype at face value. Sure, we have learned that LLMs are very (we’d even go so far as to say extremely) useful tools, but the claims of the coming ‘AIpocalypse’ with regards to cybersecurity attacks at machine speed still seemed outlandish. Less than a day later, battling the second wave of the attack, we had become true believers. We will share what we have learned and come across in this series of blogs, hoping that others can benefit from our experience.
Unlike familiar Captcha tests, this con asks you to press a series of keys. And that’s a way in for fraudsters to install malicious softwareYou are looking for some gifts for Christmas and want to support small businesses when you shop. When you visit the site of one you’ve heard good things about you are asked to verify that you are human.Instead of clicking on a series of images, or typing letters that appear, just as you have seen before, you are asked to press a series of keys and then press enter. Continue reading…
Unlike familiar Captcha tests, this con asks you to press a series of keys. And that’s a way in for fraudsters to install malicious softwareYou are looking for some gifts for Christmas and want to support small businesses when you shop. When you visit the site of one you’ve heard good things about you are asked to verify that you are human.Instead of clicking on a series of images, or typing letters that appear, just as you have seen before, you are asked to press a series of keys and then press enter. Continue reading…
Proprietary device drivers, dedicated applications, and their ilk are the bane of the open-source hacker. If only we could snoop on every device out there, recording the “secret” USB transactions …read more
Proprietary device drivers, dedicated applications, and their ilk are the bane of the open-source hacker. If only we could snoop on every device out there, recording the “secret” USB transactions …read more
Nvidia’s security chief quietly left in August, and now that CEO Jensen Huang has stepped down over his relationships, including one with an executive at a company suspected of funneling chips to China, a former intelligence officer says it’s the kind of leak that runs everyday conversations, which most corporate security teams are poorly equipped to catch.
Nvidia’s security chief quietly left in August, and now that CEO Jensen Huang has stepped down over his relationships, including one with an executive at a company suspected of funneling chips to China, a former intelligence officer says it’s the kind of leak that runs everyday conversations, which most corporate security teams are poorly equipped to catch.
Cryptocurrency hardware wallet maker Trezor has confirmed that three Safe 5 devices sold by Southeast Asian reseller CryptoBilis contained malicious hardware implants designed to steal wallet recovery phrases and send them to attackers over cellular networks. […]
Cryptocurrency hardware wallet maker Trezor has confirmed that three Safe 5 devices sold by Southeast Asian reseller CryptoBilis contained malicious hardware implants designed to steal wallet recovery phrases and send them to attackers over cellular networks. […]
Authorities arrested 354 suspects in a joint international operation targeting vendors and buyers on the Archetyp, Nemesis, Tor2Door, Bohemia, and Kingdom dark web marketplaces. […]
Authorities arrested 354 suspects in a joint international operation targeting vendors and buyers on the Archetyp, Nemesis, Tor2Door, Bohemia, and Kingdom dark web marketplaces. […]
It’s been over six months since I wrote “The Boy That Cried Mythos“, and Anthropic’s vulnerability dashboard has been growing. Let’s take a look at the 8,527 findings added in its latest month. During this same month, human reviewers checked 253 findings and maintainers pushed 113 patches. These three numbers come from Anthropic’s own counts. … Continue reading Seven Months After The Boy That Cried Mythos →
It’s been over six months since I wrote “The Boy That Cried Mythos“, and Anthropic’s vulnerability dashboard has been growing. Let’s take a look at the 8,527 findings added in its latest month. During this same month, human reviewers checked 253 findings and maintainers pushed 113 patches. These three numbers come from Anthropic’s own counts. … Continue reading Seven Months After The Boy That Cried Mythos →
A new campaign dubbed ‘wfx-loot’ has unfolded on GitHub where threat actors used 4,837 compromised accounts to probe 61,764 repositories, open pull requests, and push secrets-stealing malware. […]
A new campaign dubbed ‘wfx-loot’ has unfolded on GitHub where threat actors used 4,837 compromised accounts to probe 61,764 repositories, open pull requests, and push secrets-stealing malware. […]
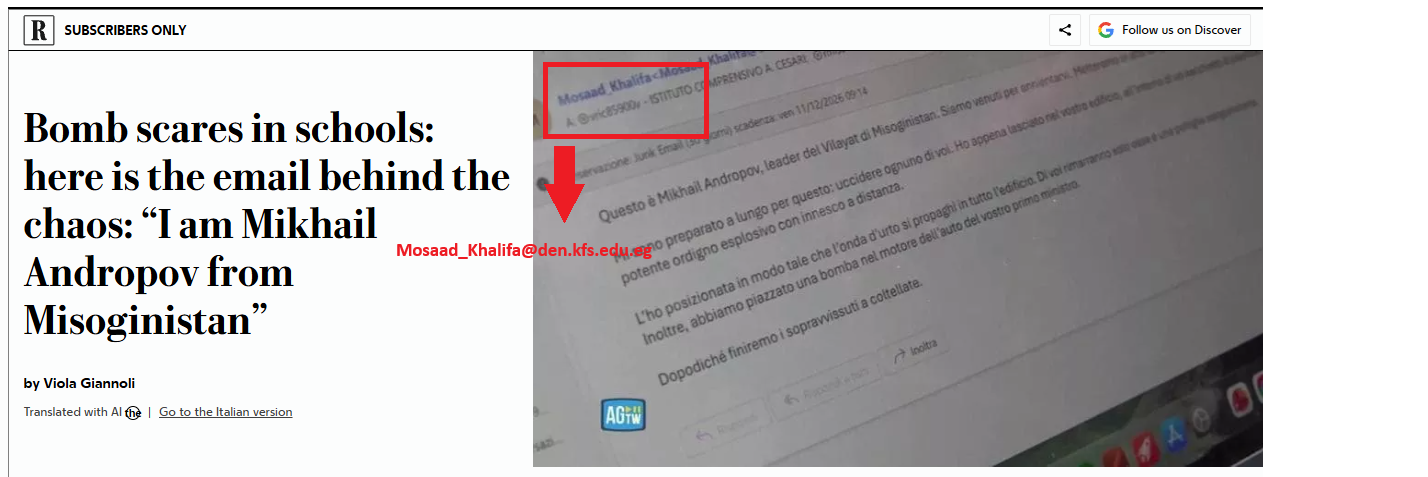
Hudson Rock researchers found that two university addresses tied to Italy’s school bomb threats were in infostealer data. On 11 November, bomb-threat emails hit schools across Europe. ANSA, citing the Education Ministry, reported that about 6,000 Italian schools received them. Some evacuated, others kept teaching after talking to police, so the recipient count tells you […]
Hudson Rock researchers found that two university addresses tied to Italy’s school bomb threats were in infostealer data. On 11 November, bomb-threat emails hit schools across Europe. ANSA, citing the Education Ministry, reported that about 6,000 Italian schools received them. Some evacuated, others kept teaching after talking to police, so the recipient count tells you […]
A.J. Vicens / Reuters:
The FBI says North Korean hackers stole $400M+ in crypto in the last 18 months using “FaceStealer”, a scheme involving fake video calls and AI deepfakes — North Korean state-backed hackers have stolen more than $400 million in cryptocurrency over the past 18 months using …
A.J. Vicens / Reuters:
The FBI says North Korean hackers stole $400M+ in crypto in the last 18 months using “FaceStealer”, a scheme involving fake video calls and AI deepfakes — North Korean state-backed hackers have stolen more than $400 million in cryptocurrency over the past 18 months using …