#main

posts tagged #main

0

Looking for feedback: First draft of multi-level guidelines for Fedecan and its various platforms (lemmy.ca, sh.itjust.works, piefed.ca, pixelfed.ca)

preview

cross-posted from: lemmy.ca/post/67952523

This is the first big step in the process to develop comprehensive guidelines for the Fedecan non-profit and the various platforms.

While this will mostly involve converting tacit knowledge and experience into an explicit written form, we expect that this process will inevitably bring up some points of disagreement on the best way to deal with different issues. We ask everyone participating in these discussions to please contribute constructively and in good faith. We encourage you to bring up any concerns or issues you have with the proposed structure and drafted guidelines, so that we can work together to fix them early on. However, in order to keep a productive environment for those discussions, we will be pruning any comment chains that devolve into personal attacks, slap fights, etc.

To help ground your feedback, consider these thought experiments when evaluating a potential guideline:

  • Veil of ignorance: Would it still feel fair to you if you switched places with someone else on the platform (ex. a new user, a moderator, an admin, a member of a vulnerable group, etc.)?
  • Equal Applicability: These rules will be enforced uniformly on everyone. A poorly written rule that helps “your side” today, can easily harm “your side” in the future as circumstances change.

The full guidelines, including governance details like the annual review cycle, can be found on the website: fedecan.ca/en/guidelines/

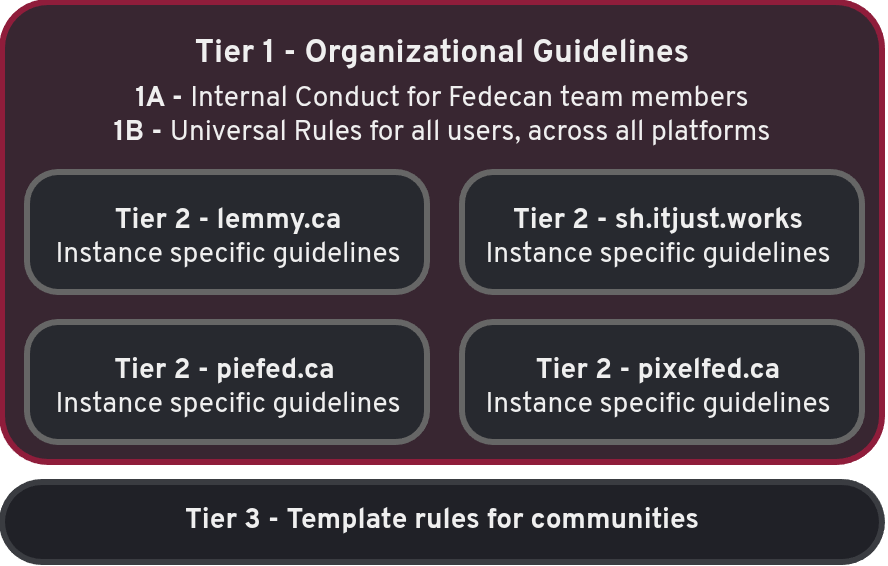
We plan to structure the guidelines as follows:

diagram of the tiers that are described below

Tier 1: Fedecan Rules

Internal Conduct

These rules apply to Fedecan team members (directors, officers, admins, and anyone with elevated access). They set expectations for how team members should act.

Universal Rules

These are the baseline rules that apply to every user on every Fedecan platform. They cover the things that are prohibited by Canadian law (threats, hate speech, CSAM, non-consensual intimate imagery) as well as universal policy rules (privacy/doxxing, harassment, fraud, content that could cause harm, labelling of sensitive content, etc.).

Tier 2: Platform-Specific

Each platform has different functionality and norms, so this is where we can be more specific with the rules. The threadiverse platforms (lemmy.ca, piefed.ca, sh.itjust.works) share similar rules around community creation, moderation, vote manipulation, and content labelling. Pixelfed has its own rules tailored to its platform.

Tier 3: Community-Level Rule Templates

These are optional templates that communities can link to, or use as a starting point for their own rules. The idea is that moderators can point users to a clearly written explanation of why a rule exists, and any relevant exceptions, rather than trying to fit everything into the sidebar. Additionally, if many communities are enforcing a particular rule in the same way, then users will have an easier time understanding and following them.

The post title standards template has been drafted, and we plan to add more as the need arises. I have a few others that are in the works, but they have some overlap with the other sections, so I thought that it would be better to let people discuss first.
cross-posted from: lemmy.ca/post/67952523

This is the first big step in the process to develop comprehensive guidelines for the Fedecan non-profit and the various platforms.

While this will mostly involve converting tacit knowledge and experience into an explicit written form, we expect that this process will inevitably bring up some points of disagreement on the best way to deal with different issues. We ask everyone participating in these discussions to please contribute constructively and in good faith. We encourage you to bring up any concerns or issues you have with the proposed structure and drafted guidelines, so that we can work together to fix them early on. However, in order to keep a productive environment for those discussions, we will be pruning any comment chains that devolve into personal attacks, slap fights, etc.

To help ground your feedback, consider these thought experiments when evaluating a potential guideline:

  • Veil of ignorance: Would it still feel fair to you if you switched places with someone else on the platform (ex. a new user, a moderator, an admin, a member of a vulnerable group, etc.)?
  • Equal Applicability: These rules will be enforced uniformly on everyone. A poorly written rule that helps “your side” today, can easily harm “your side” in the future as circumstances change.

The full guidelines, including governance details like the annual review cycle, can be found on the website: fedecan.ca/en/guidelines/

We plan to structure the guidelines as follows:

diagram of the tiers that are described below

Tier 1: Fedecan Rules

Internal Conduct

These rules apply to Fedecan team members (directors, officers, admins, and anyone with elevated access). They set expectations for how team members should act.

Universal Rules

These are the baseline rules that apply to every user on every Fedecan platform. They cover the things that are prohibited by Canadian law (threats, hate speech, CSAM, non-consensual intimate imagery) as well as universal policy rules (privacy/doxxing, harassment, fraud, content that could cause harm, labelling of sensitive content, etc.).

Tier 2: Platform-Specific

Each platform has different functionality and norms, so this is where we can be more specific with the rules. The threadiverse platforms (lemmy.ca, piefed.ca, sh.itjust.works) share similar rules around community creation, moderation, vote manipulation, and content labelling. Pixelfed has its own rules tailored to its platform.

Tier 3: Community-Level Rule Templates

These are optional templates that communities can link to, or use as a starting point for their own rules. The idea is that moderators can point users to a clearly written explanation of why a rule exists, and any relevant exceptions, rather than trying to fit everything into the sidebar. Additionally, if many communities are enforcing a particular rule in the same way, then users will have an easier time understanding and following them.

The post title standards template has been drafted, and we plan to add more as the need arises. I have a few others that are in the works, but they have some overlap with the other sections, so I thought that it would be better to let people discuss first.
0

Got any advice on graphics in posts?

preview

I just posted my first band interview with a bunch of pics.
sh.itjust.works/post/63544454

I’m pretty sure my graphics, while definitely not hi-rez, are too big. I’m choking the system when I upload them, and they don’t render during page view very well either.

I’m just taking pics with my crappy cell phone.
I upload them by opening the pic in MS Paint, select all, copy, and then paste it directly into the post.

Just given the results I’ve had so far, and my intent to post a LOT more pics, perhaps I should tune this process up.

How would you do it?

I just posted my first band interview with a bunch of pics.
sh.itjust.works/post/63544454

I’m pretty sure my graphics, while definitely not hi-rez, are too big. I’m choking the system when I upload them, and they don’t render during page view very well either.

I’m just taking pics with my crappy cell phone.
I upload them by opening the pic in MS Paint, select all, copy, and then paste it directly into the post.

Just given the results I’ve had so far, and my intent to post a LOT more pics, perhaps I should tune this process up.

How would you do it?

0

[DONE] Server Wartungsarbeiten am 24.07.26 16:00 - 18:00 MESZ // Server Maintenance on 07/24/26 16:00 - 18:00 CEST

preview

Update wurde soeben abgeschlossen und alles Services stehen wieder wie gehabt zur Verfügung.


The update has been finished and all services are available again as before.


Am 24.07.26 werden auf den feddit.org Serversystemen Wartungsarbeiten durchgeführt. Es werden Server Distributionsupdates sowie aktuelle Security und Kernel Fixes eingespielt, die u.a. einen Neustart des Datenbankservers erfordern. In der Zeit von 16:00 - 18:00 MESZ kann es daher zu kurzen Unterbrechungen kommen.

Dank der persistenten Föderationswarteschlange von Lemmy gehen uns keine Aktivitäten von anderen Lemmy-Instanzen verloren. Es kann jedoch einige Minuten länger dauern, bis wir wieder mit allen Instanzen synchronisiert sind. Bei anderer Fediverse-Software könnten möglicherweise Posts, Kommentare oder Votes verloren gehen, wenn diese nicht mit der Downtime auf der Empfängerseite umgehen können.


On July 24, 2026, maintenance will be conducted on the feddit.org server infrastructure. The servers will get distribution updates as well as security and kernel fixes which require a reboot of the database server. There may be brief interruptions between 4:00 PM and 6:00 PM CEST.

Thanks to Lemmy’s persistent federation queue, we will not lose any activity from other Lemmy instances. However, it may take a few minutes longer until we are synchronized with all instances again. Other Fediverse software may lose posts, comments or votes if they cannot handle the downtime on the receiving end.

Update wurde soeben abgeschlossen und alles Services stehen wieder wie gehabt zur Verfügung.


The update has been finished and all services are available again as before.


Am 24.07.26 werden auf den feddit.org Serversystemen Wartungsarbeiten durchgeführt. Es werden Server Distributionsupdates sowie aktuelle Security und Kernel Fixes eingespielt, die u.a. einen Neustart des Datenbankservers erfordern. In der Zeit von 16:00 - 18:00 MESZ kann es daher zu kurzen Unterbrechungen kommen.

Dank der persistenten Föderationswarteschlange von Lemmy gehen uns keine Aktivitäten von anderen Lemmy-Instanzen verloren. Es kann jedoch einige Minuten länger dauern, bis wir wieder mit allen Instanzen synchronisiert sind. Bei anderer Fediverse-Software könnten möglicherweise Posts, Kommentare oder Votes verloren gehen, wenn diese nicht mit der Downtime auf der Empfängerseite umgehen können.


On July 24, 2026, maintenance will be conducted on the feddit.org server infrastructure. The servers will get distribution updates as well as security and kernel fixes which require a reboot of the database server. There may be brief interruptions between 4:00 PM and 6:00 PM CEST.

Thanks to Lemmy’s persistent federation queue, we will not lose any activity from other Lemmy instances. However, it may take a few minutes longer until we are synchronized with all instances again. Other Fediverse software may lose posts, comments or votes if they cannot handle the downtime on the receiving end.

0

Is the API down for anybody else?

preview

My app (Thunder) has been having issues connecting for the past few hours, while the website has been up and running. Just wondering if anybody else is having issues.

Also not having any trouble connecting to other instances, just this one.

Edit: Seems to be back

My app (Thunder) has been having issues connecting for the past few hours, while the website has been up and running. Just wondering if anybody else is having issues.

Also not having any trouble connecting to other instances, just this one.

Edit: Seems to be back

0

youtube videos on sh.itjust.works

preview

What’s the detail with YouTube videos on this instance?
If I’m on this instance, videos in a post don’t render. Instead I see a big black window with this error text.

Watch video on YouTube
Error 153
Video player configuration error

You can just right click the link and go to youtube to see it, its not a complete disaster.
I do sort of need to figure this out tho. I’m doing my best to mod a music comm, so the videos are pretty important.

I’ve tried testing from other instances … and there’s no problem. I have accounts on eviltoast.org (regular lemmy) and moist.catsweat.com (mbin). No problem viewing those same posts from either of those instances. I didn’t even notice the issue until I started using my sh.itjust.works account regularly.

It doesn’t seem to matter who made the post or how old it is. When I’m logged into my sh.itjust.works account, all of the youtube posts show the black window.

I normally use firefox+adblockers, but I have sh.itjust.works whitelisted in ublock. I’ve also tested in my completely clean Vivaldi.

I’ve tested from various machines. I consistently see the empty black window only when I’m viewing these posts through the sh.itjust.works instance.

I’m a newbie mod, but this is not even a mod thing. I’m just reading a post here. Basic internet stuff. Got any help for me?

What’s the detail with YouTube videos on this instance?
If I’m on this instance, videos in a post don’t render. Instead I see a big black window with this error text.

Watch video on YouTube
Error 153
Video player configuration error

You can just right click the link and go to youtube to see it, its not a complete disaster.
I do sort of need to figure this out tho. I’m doing my best to mod a music comm, so the videos are pretty important.

I’ve tried testing from other instances … and there’s no problem. I have accounts on eviltoast.org (regular lemmy) and moist.catsweat.com (mbin). No problem viewing those same posts from either of those instances. I didn’t even notice the issue until I started using my sh.itjust.works account regularly.

It doesn’t seem to matter who made the post or how old it is. When I’m logged into my sh.itjust.works account, all of the youtube posts show the black window.

I normally use firefox+adblockers, but I have sh.itjust.works whitelisted in ublock. I’ve also tested in my completely clean Vivaldi.

I’ve tested from various machines. I consistently see the empty black window only when I’m viewing these posts through the sh.itjust.works instance.

I’m a newbie mod, but this is not even a mod thing. I’m just reading a post here. Basic internet stuff. Got any help for me?

0

Logging in on desktop: questions

preview

So I’m on my account and have no issues whilst logged in, but when I want to log in on desktop, I can’t change my password in case I forgot it. I use Voyager on mobile, which doesn’t let me change my password either ( @aeharding@vger.social ?).

I can’t add an email address either, since on Voyager that doesn’t seem possible. What do I do?

So I’m on my account and have no issues whilst logged in, but when I want to log in on desktop, I can’t change my password in case I forgot it. I use Voyager on mobile, which doesn’t let me change my password either ( @aeharding@vger.social ?).

I can’t add an email address either, since on Voyager that doesn’t seem possible. What do I do?

0

Currently in an on/off relationship with sh.itjust.works

preview

This is the first time I’m experiencing downtime for this instance, so I appreciate that a lot. Is anyone else currently experiencing troubles? Anyone know what is going on?

This is the first time I’m experiencing downtime for this instance, so I appreciate that a lot. Is anyone else currently experiencing troubles? Anyone know what is going on?

0

I would like to adopt stoner_rock@sh.itjust.works.

preview

I like posting to stoner_rock@sh.itjust.works.
It has subscribers, I’m not the only one there, but it’s been a bit stagnant. I think it could use a cleanup, maybe people might be more interested in it if there was more going on.
I’d like to adopt the com and do a few things with it.

The mod is niladmirari@sh.itjust.works. They last logged into lemmy 2024 and only ever posted a few things.
I messaged them, and was unsurprised to get no reply.

Do I need to have a sh.itjust.works account? I could sign up for one if that’s the case. I have 2 lemmy accounts already, and didn’t really want a 3rd, but if those are the rules, that’s fine.

I expect this to be an uncontroversial request. I clearly use the comm, and its clearly abandoned.
Give me some feedback here, and I’ll take whatever next steps are needed.

I like posting to stoner_rock@sh.itjust.works.
It has subscribers, I’m not the only one there, but it’s been a bit stagnant. I think it could use a cleanup, maybe people might be more interested in it if there was more going on.
I’d like to adopt the com and do a few things with it.

The mod is niladmirari@sh.itjust.works. They last logged into lemmy 2024 and only ever posted a few things.
I messaged them, and was unsurprised to get no reply.

Do I need to have a sh.itjust.works account? I could sign up for one if that’s the case. I have 2 lemmy accounts already, and didn’t really want a 3rd, but if those are the rules, that’s fine.

I expect this to be an uncontroversial request. I clearly use the comm, and its clearly abandoned.
Give me some feedback here, and I’ll take whatever next steps are needed.

0

Federation issues?

preview

I was browsing 196 recently and I noticed that stuff between slrpnk and blahaj weren’t federating between the 2 properly.

From slrpnk (another lemmy instance) there looks like there hasn’t been a post in 196 since yesterday but checking from blahaj it’s as alive as always.

I then checked from lemmy.world, beehaw, sopuli.xyz, and lemmy.zip to see if it was just an issue with slrpnk but it appears to be widespread as all of those other instances have the same issue.

Hopefully me making a post here isn’t an issue (and that it federates properly) but I figured reporting a bug wouldn’t be an issue.

I was browsing 196 recently and I noticed that stuff between slrpnk and blahaj weren’t federating between the 2 properly.

From slrpnk (another lemmy instance) there looks like there hasn’t been a post in 196 since yesterday but checking from blahaj it’s as alive as always.

I then checked from lemmy.world, beehaw, sopuli.xyz, and lemmy.zip to see if it was just an issue with slrpnk but it appears to be widespread as all of those other instances have the same issue.

Hopefully me making a post here isn’t an issue (and that it federates properly) but I figured reporting a bug wouldn’t be an issue.

0

Shout out to the people who hacked blahaj and reminded me to subscribe to their KoFi

preview

Sorry if this isn’t allowed/in the wrong place, but I wanted it to have a little visibility in case others found themselves in a position to chip in. Recovering from a breach is painful and soaks up resources that could be used elsewhere.

I mostly lurk and read Blahaj from a different instance, but when I saw the hacked announcement it reminded me what a great resource and community is here and I figured now would be a good time as any to let the Admins know I appreciate their efforts!

Link to their kofi: ko-fi.com/blahajzone (but to be security conscious, you shouldn’t click that, you should really go get the link from their sidebar :) ).

Sorry if this isn’t allowed/in the wrong place, but I wanted it to have a little visibility in case others found themselves in a position to chip in. Recovering from a breach is painful and soaks up resources that could be used elsewhere.

I mostly lurk and read Blahaj from a different instance, but when I saw the hacked announcement it reminded me what a great resource and community is here and I figured now would be a good time as any to let the Admins know I appreciate their efforts!

Link to their kofi: ko-fi.com/blahajzone (but to be security conscious, you shouldn’t click that, you should really go get the link from their sidebar :) ).

0

Does Blåhaj use Cloudflare? If so, should we also shift to another?

preview

cross-posted from: lemmy.ca/post/66634564

Cloudflare: Why I left lemmy.world to join another instance

Sad to see. We should all know cloudlfare decrypts our data before it reaches the service it protects. A perfect surveillance man-in-the-middle.

I was happy to find a home in the fediverse that uses Anubis instead.

anubis.techaro.lol

cross-posted from: lemmy.ca/post/66634564

Cloudflare: Why I left lemmy.world to join another instance

Sad to see. We should all know cloudlfare decrypts our data before it reaches the service it protects. A perfect surveillance man-in-the-middle.

I was happy to find a home in the fediverse that uses Anubis instead.

anubis.techaro.lol

0

Lemmy Release v0.19.19

preview

This version again includes a couple of security fixes. Thanks to the people who found and reported them!

The first one in particular requires manual action from instance admins. Lemmy’s default Nginx config uses $proxy_add_x_forwarded_for to set the X-Forwarded-For header, which does not override existing values. So clients can spoof the IP and bypass rate limits. The solution is to use $remote_addr instead. If you use Ansible this will be changed automatically during the upgrade, otherwise you will need to do it manually. If you dont use Nginx, ensure that any X-Forwarded-For headers sent by the client are overwritten.

The remaining security vulnerabilities are in the Lemmy code itself, and will be fixed simply by upgrading.

Security:

This version again includes a couple of security fixes. Thanks to the people who found and reported them!

The first one in particular requires manual action from instance admins. Lemmy’s default Nginx config uses $proxy_add_x_forwarded_for to set the X-Forwarded-For header, which does not override existing values. So clients can spoof the IP and bypass rate limits. The solution is to use $remote_addr instead. If you use Ansible this will be changed automatically during the upgrade, otherwise you will need to do it manually. If you dont use Nginx, ensure that any X-Forwarded-For headers sent by the client are overwritten.

The remaining security vulnerabilities are in the Lemmy code itself, and will be fixed simply by upgrading.

Security:

0

Blahaj zone hacked

preview

Firstly, apologies to everyone for the extended downtime. Unfortunately, it was for a pretty bad reason. We were hacked.

The bad news is that it was a comprehensive attack, and the attackers had privileged access to our database system, across all of our services (except for writefreely, which doesn’t use postgres). From what we can tell, the attacker did not do anything with that access, so we don’t believe any user data was accessed, but we can’t be certain of that. For lemmy, the impact of this should be minimal. If you registered with a real email address, they may have that. User passwords are encrypted in the database, so if you were using a secure, non trivial password, it should be safe, but you should still change it. You should also reset your 2 factor authentication if you had it enabled, as the seeds for these are not encrypted.

Our understanding is that the attacker used a peertube exploit, then a postgres exploit and then a kernel exploit to systematically gain access to different layers of our database server. A side effect of the hack was that it filled up our database servers hard drive, and caused it to fail over to our backup, which we believe mitigated some of the potential fall out.

We have had to reset activitypub keypairs for every account and community on lemmy, so there may be some federation hicoughs for a day or so, until remote servers have dropped any cached copies of our users public keys. This is uncharted territory though, so hopefully it’s as smooth as we think it will be, but we can’t be sure!

As stated earlier, our writefreely instance is still up and running as it wasn’t impacted by this attack. Vernissage (our pixelfed replacement) has been brought back online, as has our matrix server.

We will be bringing up Sharkey, and then Piefed hopefully later today, but we have to rotate keypairs on those services too, which is also uncharted territory, so the timelines are hopes, not guarantees. At this point in time, we don’t plan on bringing pixelfed back online, as it was slated for shutdown in August in any case. If people still need access to pixelfed to export data, we can spin it up briefly if needed, so please reach out if this is you. We also won’t be bringing peertube back up at this point. It was not heavily utilised, and it was the source of the attack, so Kaity is a bit gun shy about spinning it back up on shared database infrastructure. If there is a strong desire to bring peertube back, we can consider doing that on isolated hardware, but at the current utilisation level, it doesn’t seem worth the cost/effort to run it isolated.

in any case, you can read a fuller explanation of the attack by Kaity here pen.blahaj.zone/supakaity/weve-been-hacked

Edit - Piefed is back now!

Firstly, apologies to everyone for the extended downtime. Unfortunately, it was for a pretty bad reason. We were hacked.

The bad news is that it was a comprehensive attack, and the attackers had privileged access to our database system, across all of our services (except for writefreely, which doesn’t use postgres). From what we can tell, the attacker did not do anything with that access, so we don’t believe any user data was accessed, but we can’t be certain of that. For lemmy, the impact of this should be minimal. If you registered with a real email address, they may have that. User passwords are encrypted in the database, so if you were using a secure, non trivial password, it should be safe, but you should still change it. You should also reset your 2 factor authentication if you had it enabled, as the seeds for these are not encrypted.

Our understanding is that the attacker used a peertube exploit, then a postgres exploit and then a kernel exploit to systematically gain access to different layers of our database server. A side effect of the hack was that it filled up our database servers hard drive, and caused it to fail over to our backup, which we believe mitigated some of the potential fall out.

We have had to reset activitypub keypairs for every account and community on lemmy, so there may be some federation hicoughs for a day or so, until remote servers have dropped any cached copies of our users public keys. This is uncharted territory though, so hopefully it’s as smooth as we think it will be, but we can’t be sure!

As stated earlier, our writefreely instance is still up and running as it wasn’t impacted by this attack. Vernissage (our pixelfed replacement) has been brought back online, as has our matrix server.

We will be bringing up Sharkey, and then Piefed hopefully later today, but we have to rotate keypairs on those services too, which is also uncharted territory, so the timelines are hopes, not guarantees. At this point in time, we don’t plan on bringing pixelfed back online, as it was slated for shutdown in August in any case. If people still need access to pixelfed to export data, we can spin it up briefly if needed, so please reach out if this is you. We also won’t be bringing peertube back up at this point. It was not heavily utilised, and it was the source of the attack, so Kaity is a bit gun shy about spinning it back up on shared database infrastructure. If there is a strong desire to bring peertube back, we can consider doing that on isolated hardware, but at the current utilisation level, it doesn’t seem worth the cost/effort to run it isolated.

in any case, you can read a fuller explanation of the attack by Kaity here pen.blahaj.zone/supakaity/weve-been-hacked

Edit - Piefed is back now!

0

[update: it's fixed now! thank you!] i can't update my settings in the default lemmy UI, and can't change my profile pic anywhere

preview

pressing “save” in my settings page does nothing, not even show a popup telling me something failed. it’s been that way for a few months at least, since april of this year i think.

i’ve tried modifying and saving my profile in other clients, and it seems to work there! i can change my bio and username without issues.

however, something i can’t do, in any client, is change my profile picture, which is unfortunate since mine has been broken* for some time. in the default lemmy ui, as i said, pressing the save button does nothing. however, i’ve also tried to change my profile picture in tesseract and blorp, and both complain about an invalid url when trying to save the profile pic. both can save other settings tho, and image upload works fine, as the images i try to set appear in my uploads tab. using the js console, i can see that changing the profile pic does a PUT https://lemmy.blahaj.zone/api/v3/user/save_user_settings request, which fails (error 400). trying to change the banner image has the same problem. this happens no matter the browser or device i try this on.

is this also a problem for other people?

* (i’ve since removed my profile pic in blorp, which is why i’ve got the default lemmy profile pic now instead of a broken image icon)

(i’m sorry if this kind of post is not allowed, if not i’ll delete no worries 😅)

pressing “save” in my settings page does nothing, not even show a popup telling me something failed. it’s been that way for a few months at least, since april of this year i think.

i’ve tried modifying and saving my profile in other clients, and it seems to work there! i can change my bio and username without issues.

however, something i can’t do, in any client, is change my profile picture, which is unfortunate since mine has been broken* for some time. in the default lemmy ui, as i said, pressing the save button does nothing. however, i’ve also tried to change my profile picture in tesseract and blorp, and both complain about an invalid url when trying to save the profile pic. both can save other settings tho, and image upload works fine, as the images i try to set appear in my uploads tab. using the js console, i can see that changing the profile pic does a PUT https://lemmy.blahaj.zone/api/v3/user/save_user_settings request, which fails (error 400). trying to change the banner image has the same problem. this happens no matter the browser or device i try this on.

is this also a problem for other people?

* (i’ve since removed my profile pic in blorp, which is why i’ve got the default lemmy profile pic now instead of a broken image icon)

(i’m sorry if this kind of post is not allowed, if not i’ll delete no worries 😅)

0

The European Social Stack — An open declaration

The European Social Stack · An open declaration european.social
preview

Cross posted from feddit.org/post/30838291

Wäre das was, was die fediverse.foundation unterzeichnen würde?

Social media’s impact on society and citizens clearly shows the need for change. Europe has a strong ecosystem of social companies and a deep well of expertise in designing and operating social protocols. We are building on this to move away from large monopolistic platforms with their authoritarian governance and editorial positions, and are joining forces to establish a diverse and resilient information infrastructure in Europe. Together, we will protect people and institutions from interference by these platforms. What’s more, we will bring thousands of jobs and billions of euros that social media generates to our continent, to circulate that revenue in our own thriving business ecosystem.

From this perspective, open European platforms and protocols such as the Fediverse (Mastodon, PeerTube, or Mobilizon), the Atmosphere (Eurosky, Flashes, Tangled, or Web Tiles) and Private Messaging systems (like Matrix or XMPP) are complementary solutions for Europe, with shared common goals.

Cross posted from feddit.org/post/30838291

Wäre das was, was die fediverse.foundation unterzeichnen würde?

Social media’s impact on society and citizens clearly shows the need for change. Europe has a strong ecosystem of social companies and a deep well of expertise in designing and operating social protocols. We are building on this to move away from large monopolistic platforms with their authoritarian governance and editorial positions, and are joining forces to establish a diverse and resilient information infrastructure in Europe. Together, we will protect people and institutions from interference by these platforms. What’s more, we will bring thousands of jobs and billions of euros that social media generates to our continent, to circulate that revenue in our own thriving business ecosystem.

From this perspective, open European platforms and protocols such as the Fediverse (Mastodon, PeerTube, or Mobilizon), the Atmosphere (Eurosky, Flashes, Tangled, or Web Tiles) and Private Messaging systems (like Matrix or XMPP) are complementary solutions for Europe, with shared common goals.

0

Wie gehts der fediverse.foundation?

preview

Edit: Ich unterscheide nicht sauber zwischen der FediverseFoundation und der unabhängig moderierten Lemmy community feddit.org. Für die Benutzer hier dürfte jedoch die Gesundheit beider am Herzen liegen.

Die Geschichte mit feddit.de noch immer im Hinterkopf checke ich alle paar Monate die Webseite von fediverse.foundation ab, um zu schauen, wies so läuft. Auch um sicher zu sein, dass meine Accouns auf den verschiedenen Diensten (Für die ich übrigens auch regelmässig spende.) noch sicher sind. Gerade die Finanz-Updates fand ich wichtig und spannend zu sehen.

Leider ist der letzte Blogartikel der FediverseFoundation fast ein Jahr her. So habe ich recherchiert, wie es aussieht bezüglich Updates von Seiten Admin-Accounts:

Wer noch weitere Admin-Accounts kennt, gerne kommentieren, ich ergänze gerne.

die persönlichen Accounts der Admins, allesamt auf Mastodon:

  • Paula scheint aktiv
  • Michael bisschen weniger (April 2026)
  • fossie ist aktiv
  • b2c ebenfalls aktiv

Macht damit, was ihr wollt. Ich bin soweit zuversichtlich, dass nicht nur die Ebene der Nutzenden aktiv ist, sondern auch die Admins noch hinter dem Projekt stehen und es auch selber aktiv nutzen.

Einen schönen Tag allerseits!

Edit: Ich unterscheide nicht sauber zwischen der FediverseFoundation und der unabhängig moderierten Lemmy community feddit.org. Für die Benutzer hier dürfte jedoch die Gesundheit beider am Herzen liegen.

Die Geschichte mit feddit.de noch immer im Hinterkopf checke ich alle paar Monate die Webseite von fediverse.foundation ab, um zu schauen, wies so läuft. Auch um sicher zu sein, dass meine Accouns auf den verschiedenen Diensten (Für die ich übrigens auch regelmässig spende.) noch sicher sind. Gerade die Finanz-Updates fand ich wichtig und spannend zu sehen.

Leider ist der letzte Blogartikel der FediverseFoundation fast ein Jahr her. So habe ich recherchiert, wie es aussieht bezüglich Updates von Seiten Admin-Accounts:

Wer noch weitere Admin-Accounts kennt, gerne kommentieren, ich ergänze gerne.

die persönlichen Accounts der Admins, allesamt auf Mastodon:

  • Paula scheint aktiv
  • Michael bisschen weniger (April 2026)
  • fossie ist aktiv
  • b2c ebenfalls aktiv

Macht damit, was ihr wollt. Ich bin soweit zuversichtlich, dass nicht nur die Ebene der Nutzenden aktiv ist, sondern auch die Admins noch hinter dem Projekt stehen und es auch selber aktiv nutzen.

Einen schönen Tag allerseits!

0

New Blahaj Photo Sharing instance

preview

We’ve just spun up a brand new photo sharing instance, based on Vernissage. It’s similar to pixelfed, but more focused on photography (as opposed to general image and short video sharing).

Signups are open. Currently, it mandates an email address, but you can stick whatever you like in there, and it will be automatically verified. Signups do require approval, but you can also generate invites that (I believe) bypass the requirement for approval.

Anyway, you can check it out at photos.blahaj.zone

As a consequence, we will be taking down our pixelfed instance. We’ll leave it up until the end of August to give people a chance to migrate, but honestly, it had really low activity in any case, so it shouldn’t have too much of an impact on people.

Vernissage may also end up having low activity, but even if it does, I like it so much more than pixelfed, that we’ll keep it running even if it’s just me using it :)

We’ve just spun up a brand new photo sharing instance, based on Vernissage. It’s similar to pixelfed, but more focused on photography (as opposed to general image and short video sharing).

Signups are open. Currently, it mandates an email address, but you can stick whatever you like in there, and it will be automatically verified. Signups do require approval, but you can also generate invites that (I believe) bypass the requirement for approval.

Anyway, you can check it out at photos.blahaj.zone

As a consequence, we will be taking down our pixelfed instance. We’ll leave it up until the end of August to give people a chance to migrate, but honestly, it had really low activity in any case, so it shouldn’t have too much of an impact on people.

Vernissage may also end up having low activity, but even if it does, I like it so much more than pixelfed, that we’ll keep it running even if it’s just me using it :)

0

Update: Now resolved - Blahaj Piefed Down for security maintenance

preview

Edit - Piefed has been updated and returned to service

Thanks to someone posting a piefed security exploit without a disclosure period, we’ve had to pull blahaj piefed down without warning until a fix is implemented. This could take around 24 hours or so.

Edit - Piefed has been updated and returned to service

Thanks to someone posting a piefed security exploit without a disclosure period, we’ve had to pull blahaj piefed down without warning until a fix is implemented. This could take around 24 hours or so.

0

Now Fixed - Blahaj.zone latency across all services

preview

Edit - We’re back!

We’ve had an issue with our databases. One of our fast database servers ran out of space, and then the second fast server ran out of space whilst replicating to the first.

As a result, we have fallen over to our backup database server, which runs on spinny disks rather than SSDs. Spinny disks means that it’s got plenty of space to spare, but it’s not fast. The backup DB server is currently replicating to our two main servers to get things back up and running again, but whilst that’s happening, all of our services are running slow.

The good news is, we’ll be back up and running as if nothing happened because our backup server saved the day. The bad news is, it may take another 24 hours or so, because the backup server is reliable but not fast!

Edit - We’re back!

We’ve had an issue with our databases. One of our fast database servers ran out of space, and then the second fast server ran out of space whilst replicating to the first.

As a result, we have fallen over to our backup database server, which runs on spinny disks rather than SSDs. Spinny disks means that it’s got plenty of space to spare, but it’s not fast. The backup DB server is currently replicating to our two main servers to get things back up and running again, but whilst that’s happening, all of our services are running slow.

The good news is, we’ll be back up and running as if nothing happened because our backup server saved the day. The bad news is, it may take another 24 hours or so, because the backup server is reliable but not fast!

0

Blåhaj often down

preview

According to lestat.org, the Blåhaj instance is down notably more often. What is happening or causing this?

Is it server costs? If so, I’m willing to contribute, but how should I do so? And if not, what would it be? Host issues? Targeted attacks, perhaps?

According to lestat.org, the Blåhaj instance is down notably more often. What is happening or causing this?

Is it server costs? If so, I’m willing to contribute, but how should I do so? And if not, what would it be? Host issues? Targeted attacks, perhaps?

0

Update 2: Ich habe es nun auf 'keine Verbreitung von Desinformationen' herunter gebrochen; Update: Eindeutigere Formulierung; Neue Serverregel: Keine Diskreditierung von Instanzen/Admins

preview

English below.

Update 2:

Nach Kritik aus der Gemeinschaft, dass die Regel zu schwammig war und auch mißbraucht werden könnte, habe ich es auf ‘Keine Verbreitung von Desinformationen’ herunter gebrochen. Ich hoffe wir können damit leben.


In letzter Zeit kam es durch gezielter Desinformation und anderen diskreditierenden Posts zu viel Verstimmung in unseren kleinen Bubble. Bitte beachtet die neue Serverregel ‘Keine Diskreditierung von anderen Instanzen/Admins ohne eindeutige Beweise’.

Berechtigte Kritik zu einzelnen Instanzen oder Admins ist natürlich weiterhin erlaubt, aber achtet bitte darauf, dass es tatsächlich berechtigt ist und keine Desinformation enthält, um kein weiteres Fedidrama auszulösen.


Update 2:

Following criticism from the community that the rule was too vague and could be abused, I’ve narrowed it down to ‘No spreading of disinformation’. I hope we can live with that.


Recently, targeted disinformation and other discrediting posts have caused a lot of upset in our little bubble. Please note the new server rule: ‘No discrediting of other instances/admins without clear evidence’.

Legitimate criticism of individual instances or admins is of course still allowed, but please make sure that it is actually justified and does not contain disinformation, in order to avoid fedidrama.

Mit freundlichen Grüßen vom Admin Team.

English below.

Update 2:

Nach Kritik aus der Gemeinschaft, dass die Regel zu schwammig war und auch mißbraucht werden könnte, habe ich es auf ‘Keine Verbreitung von Desinformationen’ herunter gebrochen. Ich hoffe wir können damit leben.


In letzter Zeit kam es durch gezielter Desinformation und anderen diskreditierenden Posts zu viel Verstimmung in unseren kleinen Bubble. Bitte beachtet die neue Serverregel ‘Keine Diskreditierung von anderen Instanzen/Admins ohne eindeutige Beweise’.

Berechtigte Kritik zu einzelnen Instanzen oder Admins ist natürlich weiterhin erlaubt, aber achtet bitte darauf, dass es tatsächlich berechtigt ist und keine Desinformation enthält, um kein weiteres Fedidrama auszulösen.


Update 2:

Following criticism from the community that the rule was too vague and could be abused, I’ve narrowed it down to ‘No spreading of disinformation’. I hope we can live with that.


Recently, targeted disinformation and other discrediting posts have caused a lot of upset in our little bubble. Please note the new server rule: ‘No discrediting of other instances/admins without clear evidence’.

Legitimate criticism of individual instances or admins is of course still allowed, but please make sure that it is actually justified and does not contain disinformation, in order to avoid fedidrama.

Mit freundlichen Grüßen vom Admin Team.

0

Lemmyvision 3 - Vote for your favourite songs!

preview

cross-posted from: jlai.lu/post/37035115

Hey people,

Thank you again for coming together and submitting songs to Lemmyvision, it’s heartwarming to see different communities of the fediverse participate in sharing their musical interest.

The voting form is available here: tally.so/r/GxY0ze

Everyone is welcome to vote, even if your instance or community did not participate! This is a great opportunity to discover new music, and cultures.

@Ategon@programming.dev took the time to create a playlist over at d2jam.com/c/lemmyvision-3 feel free to check it out!

Here’s the full list of submitted songs:

The form will be available until around the 11th of May, I will then collect the results and publish them shortly after. I hope you’ll have a lot of fun listening to the 13 songs submitted for this edition. Don’t hesitate if you have any question!

cross-posted from: jlai.lu/post/37035115

Hey people,

Thank you again for coming together and submitting songs to Lemmyvision, it’s heartwarming to see different communities of the fediverse participate in sharing their musical interest.

The voting form is available here: tally.so/r/GxY0ze

Everyone is welcome to vote, even if your instance or community did not participate! This is a great opportunity to discover new music, and cultures.

@Ategon@programming.dev took the time to create a playlist over at d2jam.com/c/lemmyvision-3 feel free to check it out!

Here’s the full list of submitted songs:

The form will be available until around the 11th of May, I will then collect the results and publish them shortly after. I hope you’ll have a lot of fun listening to the 13 songs submitted for this edition. Don’t hesitate if you have any question!

0

Is anyone else experiencing federation issues with sh.itjust.works?

preview

Over the last several days, I’ve noticed significant delays with votes, comments, and notifications from that instance. The longest delay I’ve noticed was 2 days. Is this a known issue? Is anyone else experiencing this?

Over the last several days, I’ve noticed significant delays with votes, comments, and notifications from that instance. The longest delay I’ve noticed was 2 days. Is this a known issue? Is anyone else experiencing this?

0

Should we join the pledge to boycott lemmy.world?

preview

Context

TL;DR This is a pledge to defederate from lemmy.world if they end up defederating from any of the instances in the Fediverse Anarchist Flotilla (FAF), which consists of lemmy.dbzer0.com, anarchist.nexus, and quokk.au. Just want to see if the admins are aware of this situation, and see what others think.

Context

TL;DR This is a pledge to defederate from lemmy.world if they end up defederating from any of the instances in the Fediverse Anarchist Flotilla (FAF), which consists of lemmy.dbzer0.com, anarchist.nexus, and quokk.au. Just want to see if the admins are aware of this situation, and see what others think.

0

Is federation down for anyone else?

preview

since about yesterday I can’t see my own posts on lemmy.world or lemmy.blahaj.zone subs when I go to my accounts on those instances. Is this happening for anyone else?

I don’t see an announcement for maintenance or anything 🤷‍♀️

post for example:
sh.itjust.works/post/59231797 (lemmy.world)
sh.itjust.works/post/59232374 (lemmy.blahaj.zone)

since about yesterday I can’t see my own posts on lemmy.world or lemmy.blahaj.zone subs when I go to my accounts on those instances. Is this happening for anyone else?

I don’t see an announcement for maintenance or anything 🤷‍♀️

post for example:
sh.itjust.works/post/59231797 (lemmy.world)
sh.itjust.works/post/59232374 (lemmy.blahaj.zone)

0

Lemmy Release v0.19.18 - 2 security fixes

preview

With this version user badges are always shown next to usernames. There are also various bug fixes, and again security fixes

  • Display UserBadges for Bot, Banned and Deleted users in all PersonListings by @MrKaplan-lw in #4035
  • Increase timeouts for db pool by @nutomic in #6441
  • Add private IP check for webmention by @nutomic in #6444
  • Proper fix for nested comment fetch by @nutomic in #6451

Security

  • Lemmy allows an authenticated low-privileged user to create a link post through POST /api/v3/post. When a post is created in a public community, the backend asynchronously sends a Webmention to the attacker-controlled link target. The submitted URL is checked for syntax and scheme, but the audited code path does not reject loopback, private, or link-local destinations before the Webmention request is issued. This lets a normal user trigger server-side HTTP requests toward internal services. github.com/LemmyNet/lemmy/…/GHSA-3jvj-v6w2-h948
  • Lemmy fetches metadata for user-supplied post URLs and, under the default StoreLinkPreviews image mode, downloads the preview image through local pict-rs. While the top-level page URL is checked against internal IP ranges, the extracted og:image URL is not subject to the same restriction. As a result, an authenticated low-privileged user can submit an attacker-controlled public page whose Open Graph image points to an internal image endpoint. Lemmy will fetch that internal image server-side and store a local thumbnail that can then be served back to users. github.com/LemmyNet/lemmy/…/GHSA-h6hf-9846-xwrq

With this version user badges are always shown next to usernames. There are also various bug fixes, and again security fixes

  • Display UserBadges for Bot, Banned and Deleted users in all PersonListings by @MrKaplan-lw in #4035
  • Increase timeouts for db pool by @nutomic in #6441
  • Add private IP check for webmention by @nutomic in #6444
  • Proper fix for nested comment fetch by @nutomic in #6451

Security

  • Lemmy allows an authenticated low-privileged user to create a link post through POST /api/v3/post. When a post is created in a public community, the backend asynchronously sends a Webmention to the attacker-controlled link target. The submitted URL is checked for syntax and scheme, but the audited code path does not reject loopback, private, or link-local destinations before the Webmention request is issued. This lets a normal user trigger server-side HTTP requests toward internal services. github.com/LemmyNet/lemmy/…/GHSA-3jvj-v6w2-h948
  • Lemmy fetches metadata for user-supplied post URLs and, under the default StoreLinkPreviews image mode, downloads the preview image through local pict-rs. While the top-level page URL is checked against internal IP ranges, the extracted og:image URL is not subject to the same restriction. As a result, an authenticated low-privileged user can submit an attacker-controlled public page whose Open Graph image points to an internal image endpoint. Lemmy will fetch that internal image server-side and store a local thumbnail that can then be served back to users. github.com/LemmyNet/lemmy/…/GHSA-h6hf-9846-xwrq
0

Vorschlag: Alle feddit.DE Nutzer & Communities aus der Datenbank löschen.

preview

Hi,

aktuell ist es ja so, dass man die feddit.DE Accounts noch taggen kann: @wintermute@feddit.de - dasselbe mit den feddit.de communities: @mich_iel@feddit.de

Mein Bauchgefühl ist, dass diese Sachen in der lokalen lemmy Datenbank irgendwo gespeichert sein müssten. D.h. wenn man da alles mit feddit.de rauslöscht, müsste das auch nicht mehr in den auto-completion vorschlägen auftauchen?

Hi,

aktuell ist es ja so, dass man die feddit.DE Accounts noch taggen kann: @wintermute@feddit.de - dasselbe mit den feddit.de communities: @mich_iel@feddit.de

Mein Bauchgefühl ist, dass diese Sachen in der lokalen lemmy Datenbank irgendwo gespeichert sein müssten. D.h. wenn man da alles mit feddit.de rauslöscht, müsste das auch nicht mehr in den auto-completion vorschlägen auftauchen?

0

Lemmy updated to 0.19.18

preview

English version below.

Hallo,

Lemmy wurde soeben auf 0.19.18 aktualisiert.

Die vollständigen Änderungen könnt ihr hier finden:

Relevante Änderungen für Nutzer:

  • Arabische Benutzer- und Communitynamen funktionieren jetzt mit Lemmy UI
  • Post URLs können jetzt beim bearbeiten entfernt werden
  • Lemmy UI zeigt jetzt an mehr stellen an ob ein Benutzer ein Bot, gebannt, oder gelöscht ist

Hello,

Lemmy hast just been updated to 0.19.18.

The full list of changes are here:

Relevant changes for users:

  • Arabic user and community names now work with Lemmy UI
  • Post URLs can now be removed when editing a post
  • Lemmy UI now shows whether a user is a bot, banned, or deleted in more places

English version below.

Hallo,

Lemmy wurde soeben auf 0.19.18 aktualisiert.

Die vollständigen Änderungen könnt ihr hier finden:

Relevante Änderungen für Nutzer:

  • Arabische Benutzer- und Communitynamen funktionieren jetzt mit Lemmy UI
  • Post URLs können jetzt beim bearbeiten entfernt werden
  • Lemmy UI zeigt jetzt an mehr stellen an ob ein Benutzer ein Bot, gebannt, oder gelöscht ist

Hello,

Lemmy hast just been updated to 0.19.18.

The full list of changes are here:

Relevant changes for users:

  • Arabic user and community names now work with Lemmy UI
  • Post URLs can now be removed when editing a post
  • Lemmy UI now shows whether a user is a bot, banned, or deleted in more places
0

lemmy.org has been defederated

preview

We’ve seen a lot of spam come from lemmy.org and we have therefore defederated from their instance. For the moment they have open registrations which only require filling out a simple captcha to create an account which many people abuse.

The admin is active but rarely takes moderation actions, but I’ve sent a DM to them with our concerns. We’ll see how permanent this is.

We’ve seen a lot of spam come from lemmy.org and we have therefore defederated from their instance. For the moment they have open registrations which only require filling out a simple captcha to create an account which many people abuse.

The admin is active but rarely takes moderation actions, but I’ve sent a DM to them with our concerns. We’ll see how permanent this is.

0

Does anyone want to mod this community?

preview

I made an advice community for Swedish-speakers, and I happened to find one for Russian speakers. I’d mod, but I don’t speak Russian.

It’s called !advice_russian@lemmy.blahaj.zone

The moderator appears to have been banned

I made an advice community for Swedish-speakers, and I happened to find one for Russian speakers. I’d mod, but I don’t speak Russian.

It’s called !advice_russian@lemmy.blahaj.zone

The moderator appears to have been banned

0

Image posts created from lem.lemmy.blahaj.zone look weird only on lem.lemmy.blahaj.zone

preview

image to make my point. If I make an image post from blahaj (using the lem.lemmy.blahaj.zone app) it shows up as a link to an external source on the official app^[lem.lemmy.blahaj.zone/post/41085392], alexandrite^[alx.lemmy.blahaj.zone/…/41085392] and blorp^[…blahaj.zone/…/https%3A%2F%2Flemmy.blahaj.zone%2F…], i. e. it doesn’t embed. It looks normal everywhere else, i. e. from federated instances using the official web app^[lemmy.ml/post/45728815], and from the other web apps hosted locally^[phtn.lemmy.blahaj.zone/post/…/41085392] ^[mlmym.lemmy.blahaj.zone/post/41085392] ^[tes.lemmy.blahaj.zone/post/…/41085392].

Also alt text gets swallowed. It apparently doesn’t federate, I can see it when I click on edit, the box is prefilled with “I am beanis cupcake and I will eat you” but this alt-text doesnt show up when looking at this post from a federated instance. It does show up on local frontends that implement this functionality.

Thank you for your attention to this matter.

image to make my point. If I make an image post from blahaj (using the lem.lemmy.blahaj.zone app) it shows up as a link to an external source on the official app^[lem.lemmy.blahaj.zone/post/41085392], alexandrite^[alx.lemmy.blahaj.zone/…/41085392] and blorp^[…blahaj.zone/…/https%3A%2F%2Flemmy.blahaj.zone%2F…], i. e. it doesn’t embed. It looks normal everywhere else, i. e. from federated instances using the official web app^[lemmy.ml/post/45728815], and from the other web apps hosted locally^[phtn.lemmy.blahaj.zone/post/…/41085392] ^[mlmym.lemmy.blahaj.zone/post/41085392] ^[tes.lemmy.blahaj.zone/post/…/41085392].

Also alt text gets swallowed. It apparently doesn’t federate, I can see it when I click on edit, the box is prefilled with “I am beanis cupcake and I will eat you” but this alt-text doesnt show up when looking at this post from a federated instance. It does show up on local frontends that implement this functionality.

Thank you for your attention to this matter.

0

https://lemmy.dbzer0.com hat uns deföderiert

preview

Nachdem es ja in der Vergangenheit bereits eine Diskussion zum Stand von dbzer0 gegenüber feddit.org gab (Link), hat man in der Zwischenzeit feddit.org wohl komplett deföderiert (zu sehen hier bei “Blocked instances”).
Mir selbst ist es eben erst aufgefallen, als ich in !piracy@lemmy.dbzer0.com einen Post erstellen wollte, bzw. erstellt habe und dann gesehen habe, dass der letzte Post vor meinem in dieser sonst so aktiven Community vor sieben Tagen geschehen sein soll.

Mich persönlich fuckt das ganze riesig ab, da ich a) nicht der Meinung bin, dass die Vorwürfe gerechtfertigt sind und b) die dbzer0-Instanz einer der Gründe war, weswegen ich überhaupt erst ins Lemmyverse gekommen bin. Dass ich mir hierfür jetzt eigentlich einen Zweitaccount anlegen müsste, während kaum ein Lemmy-Client Multi-Account-Support hat, macht es leider auch nicht besser.

Gibt es irgendwas, was man diesbzgl. als feddit.org-Team versuchen könnte? (Will das Team das überhaupt?)

Nachdem es ja in der Vergangenheit bereits eine Diskussion zum Stand von dbzer0 gegenüber feddit.org gab (Link), hat man in der Zwischenzeit feddit.org wohl komplett deföderiert (zu sehen hier bei “Blocked instances”).
Mir selbst ist es eben erst aufgefallen, als ich in !piracy@lemmy.dbzer0.com einen Post erstellen wollte, bzw. erstellt habe und dann gesehen habe, dass der letzte Post vor meinem in dieser sonst so aktiven Community vor sieben Tagen geschehen sein soll.

Mich persönlich fuckt das ganze riesig ab, da ich a) nicht der Meinung bin, dass die Vorwürfe gerechtfertigt sind und b) die dbzer0-Instanz einer der Gründe war, weswegen ich überhaupt erst ins Lemmyverse gekommen bin. Dass ich mir hierfür jetzt eigentlich einen Zweitaccount anlegen müsste, während kaum ein Lemmy-Client Multi-Account-Support hat, macht es leider auch nicht besser.

Gibt es irgendwas, was man diesbzgl. als feddit.org-Team versuchen könnte? (Will das Team das überhaupt?)

0

Lemmy Release v0.19.17 fixes Arabic user/community names and internal host access security advisory

preview

Changes

This release addresses another security advisory related to internal host access. You can now bypass these checks for federation, in order to federate with instances over the local network by setting environment variable DANGER_FEDERATION_ALLOW_LOCAL_IP=1. There are also some bug fixes, and lemmy-ui now logs file requests.

  • Improve IP checks by @nutomic in #6411
  • Allow to bypass federation IP checks with env var DANGER_FEDERATION_ALLOW_LOCAL_IP by @nutomic in #158
  • Fix Arabic user/community names by @nutomic in #3968
  • Fix removing post.url by @nutomic in #3984
  • Add lemmy-ui request logs by @MrKaplan-lw in #3933

Changes

This release addresses another security advisory related to internal host access. You can now bypass these checks for federation, in order to federate with instances over the local network by setting environment variable DANGER_FEDERATION_ALLOW_LOCAL_IP=1. There are also some bug fixes, and lemmy-ui now logs file requests.

  • Improve IP checks by @nutomic in #6411
  • Allow to bypass federation IP checks with env var DANGER_FEDERATION_ALLOW_LOCAL_IP by @nutomic in #158
  • Fix Arabic user/community names by @nutomic in #3968
  • Fix removing post.url by @nutomic in #3984
  • Add lemmy-ui request logs by @MrKaplan-lw in #3933
0

Update zu / regarding archive.today/.is/.ph/etc. Links

preview

Erstmals möchte ich mich dafür entschuldigen, dass es solange gedauert hat.

Vorerst bitten wir darum die betroffenen Archive-Seiten zu vermeiden aufgrund des im vorigen Beitrag beschriebenen Problems. In der Regel bei Verstöße werden wir höflich darum bitten die Links zu entfernen. Es gilt auf zukünftige Beiträge. Wenn trotz Aufforderung die Links nicht rausgenommen werden, könnten die Beiträge gelöscht werden, da wir die Beiträge nicht eigenständig ändern können als Admins.

Betroffene Archive-Seiten sind wie folgt:

archive(.)today

archive(.)fo

archive(.)is

archive(.)li

archive(.)md

archive(.)ph

archive(.)vn

Falls sich an der Lage was ändern, werden wir euch informieren.

Wir bitten um Verständnis.

English:

First of all, I would like to apologize for the delay in regards to the decision on the Archive webpages.

For the time being, we ask you to not use the affected Archive webpages, due to the reasons mentioned in the previous pinned post. Generally in instances where the aforementioned Archive webpages are used, we will politely ask you to delete the links or change them to a different archiving provider. It applies to future posts from this point on. If the links are not removed or changed despite requests to do so, your post may be delete as we cannot edit your posts ourselves.

Affected archive webpages are:

archive(.)today

archive(.)fo

archive(.)is

archive(.)li

archive(.)md

archive(.)ph

archive(.)vn

We will inform you in case the situation changes.

We ask for you understanding.

Erstmals möchte ich mich dafür entschuldigen, dass es solange gedauert hat.

Vorerst bitten wir darum die betroffenen Archive-Seiten zu vermeiden aufgrund des im vorigen Beitrag beschriebenen Problems. In der Regel bei Verstöße werden wir höflich darum bitten die Links zu entfernen. Es gilt auf zukünftige Beiträge. Wenn trotz Aufforderung die Links nicht rausgenommen werden, könnten die Beiträge gelöscht werden, da wir die Beiträge nicht eigenständig ändern können als Admins.

Betroffene Archive-Seiten sind wie folgt:

archive(.)today

archive(.)fo

archive(.)is

archive(.)li

archive(.)md

archive(.)ph

archive(.)vn

Falls sich an der Lage was ändern, werden wir euch informieren.

Wir bitten um Verständnis.

English:

First of all, I would like to apologize for the delay in regards to the decision on the Archive webpages.

For the time being, we ask you to not use the affected Archive webpages, due to the reasons mentioned in the previous pinned post. Generally in instances where the aforementioned Archive webpages are used, we will politely ask you to delete the links or change them to a different archiving provider. It applies to future posts from this point on. If the links are not removed or changed despite requests to do so, your post may be delete as we cannot edit your posts ourselves.

Affected archive webpages are:

archive(.)today

archive(.)fo

archive(.)is

archive(.)li

archive(.)md

archive(.)ph

archive(.)vn

We will inform you in case the situation changes.

We ask for you understanding.

0

Werden jetzt Links zur Originalquelle gelöscht nur weil im Text auch noch ein archive.?? Link ist?

preview

Hab ich das nicht mitbekommen? Seit wann ist das verboten? Ich weiß nur, dass da irgendwas diskutiert wird.

Hab ich das nicht mitbekommen? Seit wann ist das verboten? Ich weiß nur, dass da irgendwas diskutiert wird.

0

Reading via /feeds/front.xml/

preview

Hi everyone,

I hope this is a proper channel to reach out to the maintainers of this instance.

I saw in the documentation (linked) that it is possible to read via RSS not only full content or entries in specific community, but also a single RSS feed that includes entries from all my subscribed communities. My front page in the RSS format.

Is this feature activated on feddit.org?

I followed the documentation: appended to the URL https://feddit.org/feeds/front.xml/ my JWT token extracted from the cookies, and this request produced a 404 Not Found error for me. Is there some mistake on my side, or is there another reason?

Hi everyone,

I hope this is a proper channel to reach out to the maintainers of this instance.

I saw in the documentation (linked) that it is possible to read via RSS not only full content or entries in specific community, but also a single RSS feed that includes entries from all my subscribed communities. My front page in the RSS format.

Is this feature activated on feddit.org?

I followed the documentation: appended to the URL https://feddit.org/feeds/front.xml/ my JWT token extracted from the cookies, and this request produced a 404 Not Found error for me. Is there some mistake on my side, or is there another reason?

0

Tor Exit List Service

preview

Can blahaj commit to either blocking all of the ips on the tor exit list, or white listing them. This “block only a few” makes for a dice roll for tor users. Specifically the pictrs service just doesn’t serve photos to banned ips but lemmy still works so it just partially breaks.

Asking for a friend.

Can blahaj commit to either blocking all of the ips on the tor exit list, or white listing them. This “block only a few” makes for a dice roll for tor users. Specifically the pictrs service just doesn’t serve photos to banned ips but lemmy still works so it just partially breaks.

Asking for a friend.

0

Lemmy v0.19.16 fixes moderate security advisory

preview

This release mitigates a potential security issue with the image endpoint. In short, an attacker can inject query parameters and make proxied requests to arbitrary URLs. See the security advisory for details.

Also there are fixes for the database connection pool. The pool size is now at least two, as a lower size can result in deadlocks. Additionally there are now connection timeouts added. If your server logs show pool timeout errors, you should increase database.pool_size in the Lemmy config.

  • Fix for image proxy filetypes by @dessalines in #6357
  • Enable DB connection timeout by @Nutomic in #6355
  • Use min database pool size of 2. by @dessalines in #6345

github.com/LemmyNet/lemmy/…/GHSA-jvxv-2jjp-jxc3

This release mitigates a potential security issue with the image endpoint. In short, an attacker can inject query parameters and make proxied requests to arbitrary URLs. See the security advisory for details.

Also there are fixes for the database connection pool. The pool size is now at least two, as a lower size can result in deadlocks. Additionally there are now connection timeouts added. If your server logs show pool timeout errors, you should increase database.pool_size in the Lemmy config.

  • Fix for image proxy filetypes by @dessalines in #6357
  • Enable DB connection timeout by @Nutomic in #6355
  • Use min database pool size of 2. by @dessalines in #6345

github.com/LemmyNet/lemmy/…/GHSA-jvxv-2jjp-jxc3

0

programming.dev has been defederated

preview

We’ve been seeing frequent spam waves of targeted harassment from accounts made on programming.dev over the course of several weeks, which has among other unacceptable things contained transphobia, obscene pictures of animals, calling for the victim to commit suicide, and other hateful rhetoric.

For these reasons we are defederating from programming.dev. We may refederate in the future if we have reason to believe there will be no further problems like these from their instance.

Edit: I’ve spoken with the admins there and I may refederate once I have more details on their application system. To be clear they don’t support anything posted by these accounts and are deleting them as they are detected.

Edit: We’ve refedereted.

We’ve been seeing frequent spam waves of targeted harassment from accounts made on programming.dev over the course of several weeks, which has among other unacceptable things contained transphobia, obscene pictures of animals, calling for the victim to commit suicide, and other hateful rhetoric.

For these reasons we are defederating from programming.dev. We may refederate in the future if we have reason to believe there will be no further problems like these from their instance.

Edit: I’ve spoken with the admins there and I may refederate once I have more details on their application system. To be clear they don’t support anything posted by these accounts and are deleting them as they are detected.

Edit: We’ve refedereted.

0

"Open links in a new tab" option doesn't do anything for me

preview

not sure if this is an issue just with this instance, or a general lemmy problem.

I have the options “Open links in a new tab” checked, but nothing ever opens in a new tab. this has been a problem for me for almost 3 years on this instance. i just assumed it would be fixed in an update some day.

using firefox on debian, if that makes a difference

not sure if this is an issue just with this instance, or a general lemmy problem.

I have the options “Open links in a new tab” checked, but nothing ever opens in a new tab. this has been a problem for me for almost 3 years on this instance. i just assumed it would be fixed in an update some day.

using firefox on debian, if that makes a difference

0

Is it possible to see only new post replies?

preview

I’m new to Lemmy, days not weeks. Liking it so far and I’m trying to contribute in a positive way to the instance.

I have one usability issue, trying to figure out which replies in a post are new since I last read it. I see the number like (4 New) telling me how many, but not which.

Sorting by “New” hardly helps because of the threaded display. Threading is a good thing, IMO, since it preserves the flow of the conversation. But new replies to older replies get buried with a “New” sort. When the post has only a few replies total, I can keep up simply by re-scanning the whole thread. On more popular posts that becomes infeasible.

Please don’t beat me up too bad if I’m missing an obvious thing! I saw the user settings, “Show Read Posts”, but that seems to be post level, not reply level.

Editing because I am an idiot: I use the web interface through sh.itjust.works.

I’m new to Lemmy, days not weeks. Liking it so far and I’m trying to contribute in a positive way to the instance.

I have one usability issue, trying to figure out which replies in a post are new since I last read it. I see the number like (4 New) telling me how many, but not which.

Sorting by “New” hardly helps because of the threaded display. Threading is a good thing, IMO, since it preserves the flow of the conversation. But new replies to older replies get buried with a “New” sort. When the post has only a few replies total, I can keep up simply by re-scanning the whole thread. On more popular posts that becomes infeasible.

Please don’t beat me up too bad if I’m missing an obvious thing! I saw the user settings, “Show Read Posts”, but that seems to be post level, not reply level.

Editing because I am an idiot: I use the web interface through sh.itjust.works.