0

Seti si affida alla teoria dei giochi

preview

Seti si affida alla teoria dei giochi

@astronomia

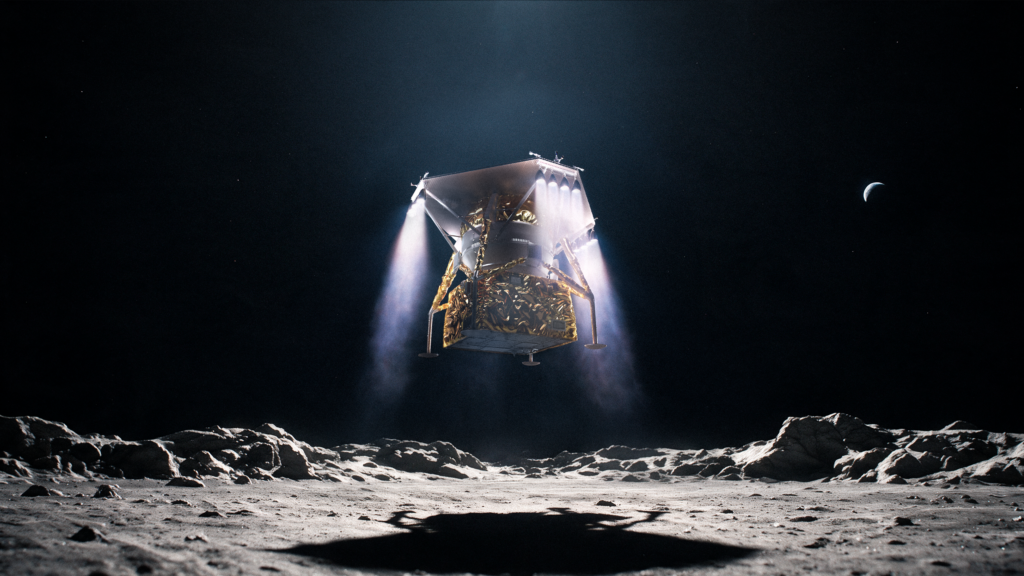
Quali sono la regione di cielo e il momento più adatti per andare in cerca di segnali da intelligenze aliene? Avvalendosi della teoria dei giochi e dell’Allen Telescope Array, i ricercatori del Seti Institute stanno verificando se le civiltà extraterrestri potrebbero scegliere un momento prevedibile per entrare in contatto con noi

Seti si affida alla teoria dei giochi

@astronomia

Quali sono la regione di cielo e il momento più adatti per andare in cerca di segnali da intelligenze aliene? Avvalendosi della teoria dei giochi e dell’Allen Telescope Array, i ricercatori del Seti Institute stanno verificando se le civiltà extraterrestri potrebbero scegliere un momento prevedibile per entrare in contatto con noi

0

Retrododo: Someone put a GBA emulator in World of Warcraft: Forever so flying isn't boring

preview

Retrododo: Someone put a GBA emulator in World of Warcraft: Forever so flying isn’t boring

#GBA #emulation #WoW

The emulator is MekkaBoy.

Your scientists were so preoccupied with whether they could, they didn’t stop to think if they should.

Retrododo: Someone put a GBA emulator in World of Warcraft: Forever so flying isn’t boring

#GBA #emulation #WoW

The emulator is MekkaBoy.

Your scientists were so preoccupied with whether they could, they didn’t stop to think if they should.

0

Help me Dual boot for the first time [RE: Help me choose my 2nd (Dual boot) Linux distro on my PC as a Linux beginner]

preview

After evaluating every comment you left me in the last post and testing every OS via virtual machines, I’ve decided that my first option when dual booting will be CachyOS, leaving Fedora KDE and endeavourOS as the runner ups. Now I’m at the point where I have to actually do the dual boot. I’ve found some videos and posts where they show how to do it but I haven’t managed to find any case like mine, since I want to go from Linux Mint Debian Edition single boot, to LMDE + CachyOS/Fedora/endeavour. I’m doing this post to ask some questions:

  • Being my case pretty specific, is it the process any different than some other builds like Arch + Cachy, Ubuntu + endeavour, etc., or everytime it’s the same process whatever are the OS’s I install? Do I have to have in mind anything in particular in my case? Any extra tips?
  • Can I dual boot without having to make a total reset of my actual OS to install it again altogether with the secondary OS? Is it less, equally or more safe/efficient?
  • Do you have any guide in general that you find to be good/useful in this matter therefore I can take advantage of?

Please have in mind I’m a total beginner on these things and they still feel pretty overwhelming to me. So, sorry if I ask something dumb and thank you very much in advance!!

After evaluating every comment you left me in the last post and testing every OS via virtual machines, I’ve decided that my first option when dual booting will be CachyOS, leaving Fedora KDE and endeavourOS as the runner ups. Now I’m at the point where I have to actually do the dual boot. I’ve found some videos and posts where they show how to do it but I haven’t managed to find any case like mine, since I want to go from Linux Mint Debian Edition single boot, to LMDE + CachyOS/Fedora/endeavour. I’m doing this post to ask some questions:

  • Being my case pretty specific, is it the process any different than some other builds like Arch + Cachy, Ubuntu + endeavour, etc., or everytime it’s the same process whatever are the OS’s I install? Do I have to have in mind anything in particular in my case? Any extra tips?
  • Can I dual boot without having to make a total reset of my actual OS to install it again altogether with the secondary OS? Is it less, equally or more safe/efficient?
  • Do you have any guide in general that you find to be good/useful in this matter therefore I can take advantage of?

Please have in mind I’m a total beginner on these things and they still feel pretty overwhelming to me. So, sorry if I ask something dumb and thank you very much in advance!!

0

Dortmund police attacked as crowd storms kebab shop for €1 doner

the Guardian Dortmund police attacked as crowd storms kebab shop for €1 doner www.theguardian.com
preview

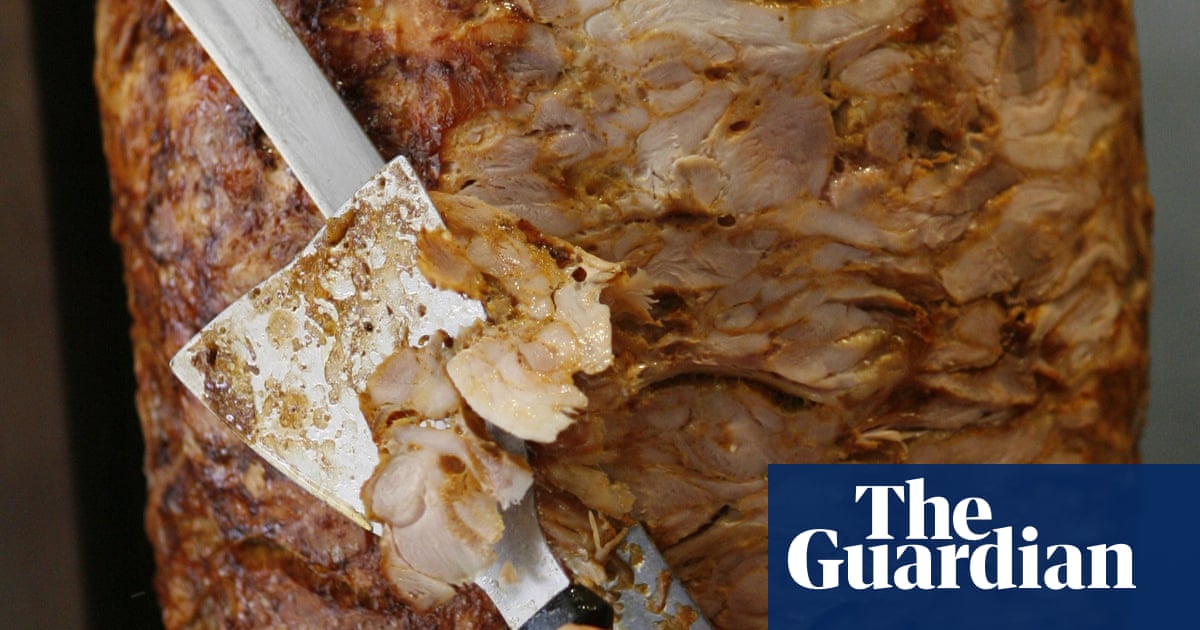
Police were called to a doner kebab shop in Dortmund, western Germany on Sunday after hundreds of customers stormed the premises in the hope of securing a portion for a one-off rock bottom introductory price.

The owner of the outlet was forced to call the police after becoming overwhelmed by the crowds that turned up for its opening.

According to the owner, about 1,000 people were present. Police put the number at about 300.

The owner had advertised his €1 (£0.83) kebab offer in advance. The average price of a doner – marinated meat roasted on a rotisserie spit, sliced off and served with salad in pockets of warm flatbread or wraps – is usually around €7.50 to €9.

Until about 2020, the price had been betwen €3.50 to €4. The steep rise, largely the result of higher energy and food costs, has turned Germany’s most popular fast food – which is served more than 1.3bn times a year – into a palpable everyday symbol of the effects of inflation.

Police were called to a doner kebab shop in Dortmund, western Germany on Sunday after hundreds of customers stormed the premises in the hope of securing a portion for a one-off rock bottom introductory price.

The owner of the outlet was forced to call the police after becoming overwhelmed by the crowds that turned up for its opening.

According to the owner, about 1,000 people were present. Police put the number at about 300.

The owner had advertised his €1 (£0.83) kebab offer in advance. The average price of a doner – marinated meat roasted on a rotisserie spit, sliced off and served with salad in pockets of warm flatbread or wraps – is usually around €7.50 to €9.

Until about 2020, the price had been betwen €3.50 to €4. The steep rise, largely the result of higher energy and food costs, has turned Germany’s most popular fast food – which is served more than 1.3bn times a year – into a palpable everyday symbol of the effects of inflation.

0

Landmark CJEU ruling demands Member States to ensure legal gender recognition to guarantee freedom of movement

ILGA-Europe | Safety, equality and freedom for LGBTI people in Europe & Central Asia Landmark CJEU ruling demands Member States to ensure legal gender recognition to guarantee freedom of movement | ILGA-Europe www.ilga-europe.org
preview

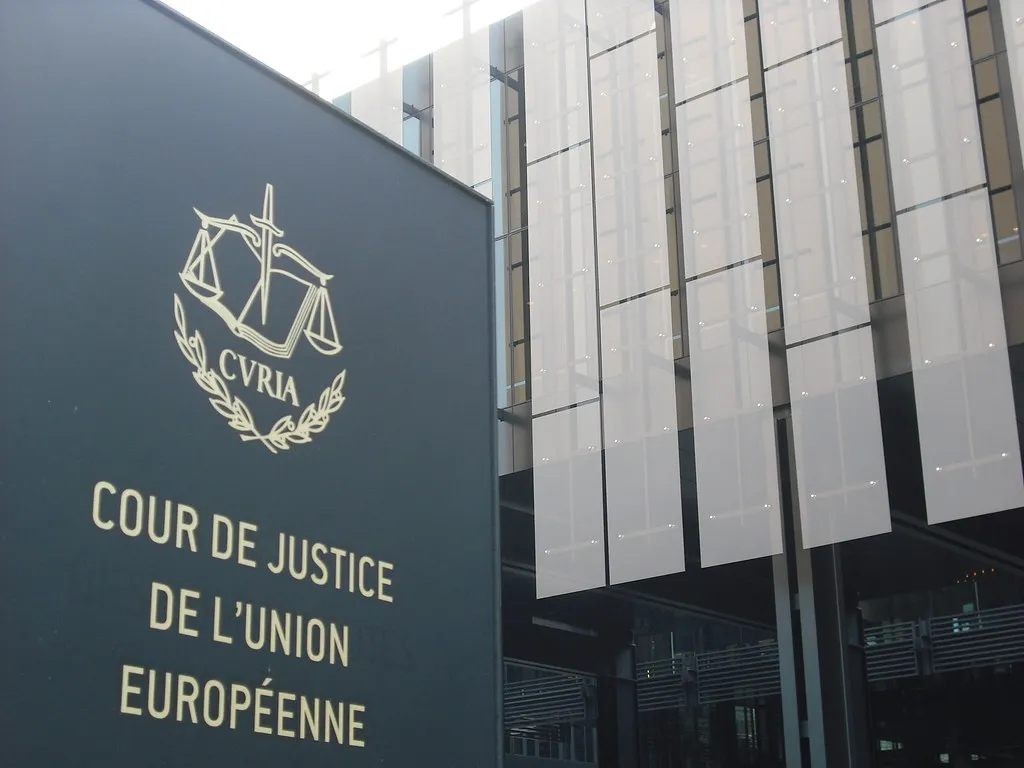
Today’s judgment by the Court of Justice of the EU (CJEU) says all member states must provide for legal gender recognition procedures allowing their citizens who have exercised their right to move and reside freely in another member state to obtain identity documents matching their lived gender. Today, the CJEU delivered its ruling in the

Today’s judgment by the Court of Justice of the EU (CJEU) says all member states must provide for legal gender recognition procedures allowing their citizens who have exercised their right to move and reside freely in another member state to obtain identity documents matching their lived gender. Today, the CJEU delivered its ruling in the

0

Iran mocks Iron Gate, says CENTCOM chief now producing 'Ninja Turtles'

play · v.turkiyetoday.com
Türkiye Today Iran mocks Iron Gate, says CENTCOM chief now producing 'Ninja Turtles' - Türkiye Today www.turkiyetoday.com
preview

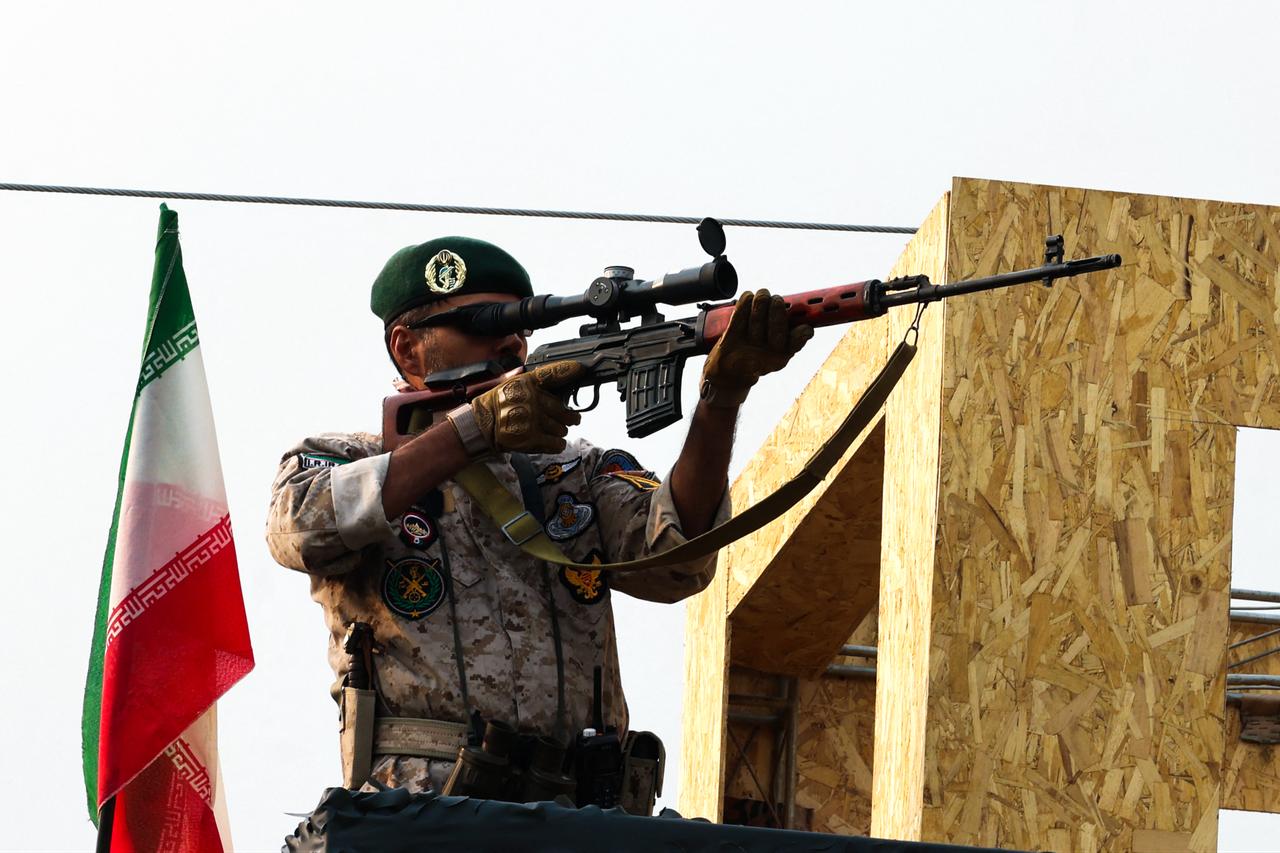
Iran’s Foreign Ministry on Monday ridiculed U.S. Central Command’s (CENTCOM) new Task Force Iron Gate, saying the plan to choke Iran’s land routes was an attempt by U.S. military officials to cover up their failures after Republicans’ midterm defeat and was bound to fail.

“The CENTCOM commander apparently changes jobs very quickly,” spokesman Esmaeil Baghaei told his weekly news conference.

“After the ‘glories’ he achieved for his country in Minab, Lamerd and Sirik, he moved on to producing podcasts, and now apparently is going to produce a new episode of Teenage Mutant Ninja Turtles from Florida!” he added.

Iran’s Foreign Ministry on Monday ridiculed U.S. Central Command’s (CENTCOM) new Task Force Iron Gate, saying the plan to choke Iran’s land routes was an attempt by U.S. military officials to cover up their failures after Republicans’ midterm defeat and was bound to fail.

“The CENTCOM commander apparently changes jobs very quickly,” spokesman Esmaeil Baghaei told his weekly news conference.

“After the ‘glories’ he achieved for his country in Minab, Lamerd and Sirik, he moved on to producing podcasts, and now apparently is going to produce a new episode of Teenage Mutant Ninja Turtles from Florida!” he added.

0

Landmark CJEU ruling demands Member States to ensure legal gender recognition to guarantee freedom of movement

ILGA-Europe | Safety, equality and freedom for LGBTI people in Europe & Central Asia Landmark CJEU ruling demands Member States to ensure legal gender recognition to guarantee freedom of movement | ILGA-Europe www.ilga-europe.org
preview

Today’s judgment by the Court of Justice of the EU (CJEU) says all member states must provide for legal gender recognition procedures allowing their citizens who have exercised their right to move and reside freely in another member state to obtain identity documents matching their lived gender. Today, the CJEU delivered its ruling in the

Today’s judgment by the Court of Justice of the EU (CJEU) says all member states must provide for legal gender recognition procedures allowing their citizens who have exercised their right to move and reside freely in another member state to obtain identity documents matching their lived gender. Today, the CJEU delivered its ruling in the

0

The injunction that permanently silenced Russell Brand’s accuser

Tax Policy Associates Russell Brand’s secret injunction: the order that silenced his accuser taxpolicy.org.uk
preview

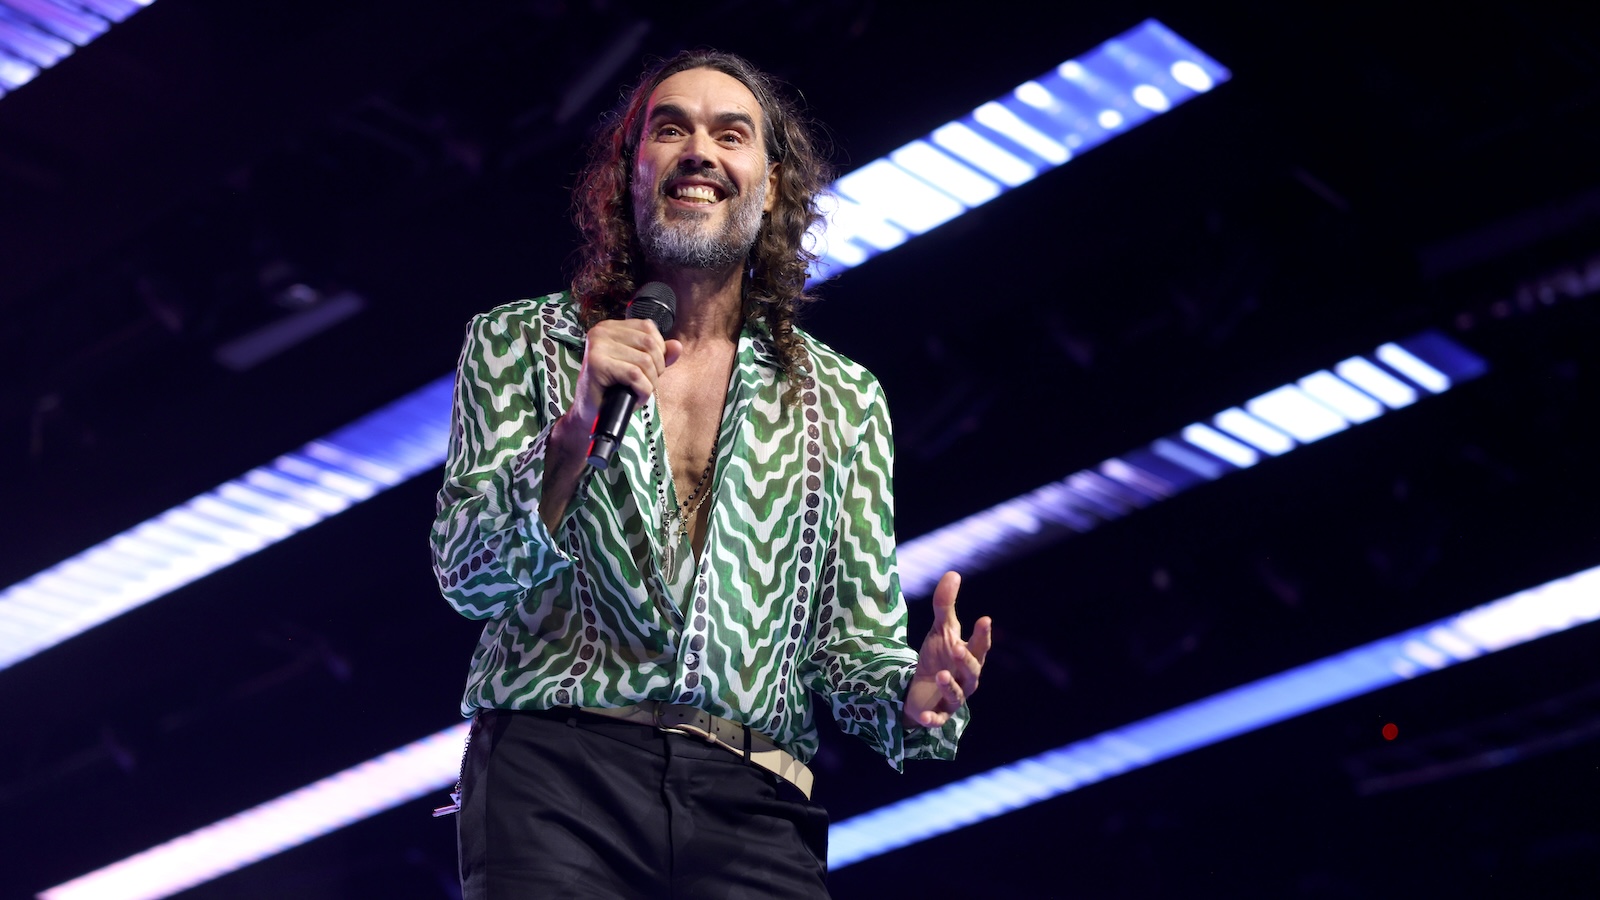
In 2014, a massage therapist called Sylvie Berki accused Russell Brand of assaulting her. The police took no further action. Mr Brand and his then girlfriend, Jemima Goldsmith, sued her. Ms Berki had no lawyer, and there was no trial. But the High Court issued an extraordinary injunction that silenced her for the rest of her life. This week Mr Brand was convicted of rape and three sexual assaults.

We have obtained a copy of the injunction, which has never previously been published. It was supposed to prevent harassment, but it went well beyond that. It prohibits Ms Berki from telling anyone what she says happened to her – not journalists, not friends, not family, and not even the police. The court also orderd Ms Berki to pay £50,000 in legal costs within two weeks (which she couldn’t afford) and authorised her bankruptcy.

We don’t know whether Ms Berki’s allegations were true, and Mr Brand’s convictions don’t establish that they were. But whilst nobody established that Ms Berki was lying, the High Court made an order that prevents her from ever speaking about what she says happened to her.

This September, a Court of Appeal judge acknowledged concerns about the extraordinary breadth of the injunction, but it remains in place. We think the injunction should never have been granted in these terms. It’s a disturbing example of what happens when wealthy, powerful people take an unrepresented defendant to court.

In 2014, a massage therapist called Sylvie Berki accused Russell Brand of assaulting her. The police took no further action. Mr Brand and his then girlfriend, Jemima Goldsmith, sued her. Ms Berki had no lawyer, and there was no trial. But the High Court issued an extraordinary injunction that silenced her for the rest of her life. This week Mr Brand was convicted of rape and three sexual assaults.

We have obtained a copy of the injunction, which has never previously been published. It was supposed to prevent harassment, but it went well beyond that. It prohibits Ms Berki from telling anyone what she says happened to her – not journalists, not friends, not family, and not even the police. The court also orderd Ms Berki to pay £50,000 in legal costs within two weeks (which she couldn’t afford) and authorised her bankruptcy.

We don’t know whether Ms Berki’s allegations were true, and Mr Brand’s convictions don’t establish that they were. But whilst nobody established that Ms Berki was lying, the High Court made an order that prevents her from ever speaking about what she says happened to her.

This September, a Court of Appeal judge acknowledged concerns about the extraordinary breadth of the injunction, but it remains in place. We think the injunction should never have been granted in these terms. It’s a disturbing example of what happens when wealthy, powerful people take an unrepresented defendant to court.

0

Binance denies data breach after alleged ShinyHunters claims

preview

Binance, the world’s largest crypto exchange, has denied claims of a new security breach made by a threat actor using the ‘ShinyHunters’ handle on a newly emerged underground cybercrime forum.

Binance, the world’s largest crypto exchange, has denied claims of a new security breach made by a threat actor using the ‘ShinyHunters’ handle on a newly emerged underground cybercrime forum.

0

Iris Ohyama data cloud breach exposes info of 7.7 million customers

preview

Japanese manufacturer Iris Ohyama, the operator of the Iris Plaza shopping platform, disclosed that personal information belonging to about 7.7 million people may have been exposed after unauthorized access to a third-party cloud service the company used.

Japanese manufacturer Iris Ohyama, the operator of the Iris Plaza shopping platform, disclosed that personal information belonging to about 7.7 million people may have been exposed after unauthorized access to a third-party cloud service the company used.

0

Chainalysis says breach exposed credentials for all customers

preview

Blockchain intelligence firm Chainalysis says a recent attack on its systems and internal tools has exposed credentials and live tokens for all customers.

Blockchain intelligence firm Chainalysis says a recent attack on its systems and internal tools has exposed credentials and live tokens for all customers.

0

Le nomine all’autorità anticorruzione sono da sempre un affare politico

preview

Le nomine all’autorità anticorruzione sono da sempre un affare politico
@politica
https://pagellapolitica.it/articoli/governo-meloni-nomine-anac-affare-politico
Negli anni dietro la scelta del presidente dell’organismo, oggi al centro di polemiche tra governo e opposizioni, ci sono stati spesso i legami personali o professionali tra i candidati e il governo di turno

Le nomine all’autorità anticorruzione sono da sempre un affare politico
@politica
https://pagellapolitica.it/articoli/governo-meloni-nomine-anac-affare-politico
Negli anni dietro la scelta del presidente dell’organismo, oggi al centro di polemiche tra governo e opposizioni, ci sono stati spesso i legami personali o professionali tra i candidati e il governo di turno

0

DigiCert data breach exposes customer information, identity documents

preview

DigiCert warns it suffered a data breach after a server migration mistakenly exposed an internal business system to the internet, allowing unauthorized access to customer information and identity documents.

DigiCert warns it suffered a data breach after a server migration mistakenly exposed an internal business system to the internet, allowing unauthorized access to customer information and identity documents.

0

DreamHost confirms data breach exposed FTP logins and webmail sessions

preview

DreamHost is warning of a data breach after attackers gained access to its File Manager platform for two months and stole customers’ FTP/SFTP usernames and passwords.

DreamHost is warning of a data breach after attackers gained access to its File Manager platform for two months and stole customers’ FTP/SFTP usernames and passwords.

0

NIKKE PC game launcher hacked to spread remote access, data-stealing malware

preview

The developers of Goddess of Victory: NIKKE have confirmed that hackers tampered with the game’s PC launcher scripts in a supply-chain attack, distributing malware capable of stealing credentials and cryptocurrency wallet data.

The developers of Goddess of Victory: NIKKE have confirmed that hackers tampered with the game’s PC launcher scripts in a supply-chain attack, distributing malware capable of stealing credentials and cryptocurrency wallet data.

0

Hackers hijack cPGuard autoupdate to deploy backdoor, steal data

preview

Attackers have compromised the update infrastructure for the cPGuard web security suite to distribute a backdoor and a data-stealing script.

Attackers have compromised the update infrastructure for the cPGuard web security suite to distribute a backdoor and a data-stealing script.

0

Harvard University data breach exposed info of 851,000 accounts

preview

Hackers who breached Harvard University’s Alumni Affairs and Development systems in November 2025 stole data linked to more than 850,000 unique email addresses, according to breach notification service Have I Been Pwned.

Hackers who breached Harvard University’s Alumni Affairs and Development systems in November 2025 stole data linked to more than 850,000 unique email addresses, according to breach notification service Have I Been Pwned.

0

Nail Salon Air Can Spike to Levels Comparable to Chemical Plants, Study of 5 NYC Salons Finds

ScienceAlert Nail Salon Air Can Spike to Levels Comparable to Chemical Plants, Study of 5 NYC Salons Finds www.sciencealert.com
preview

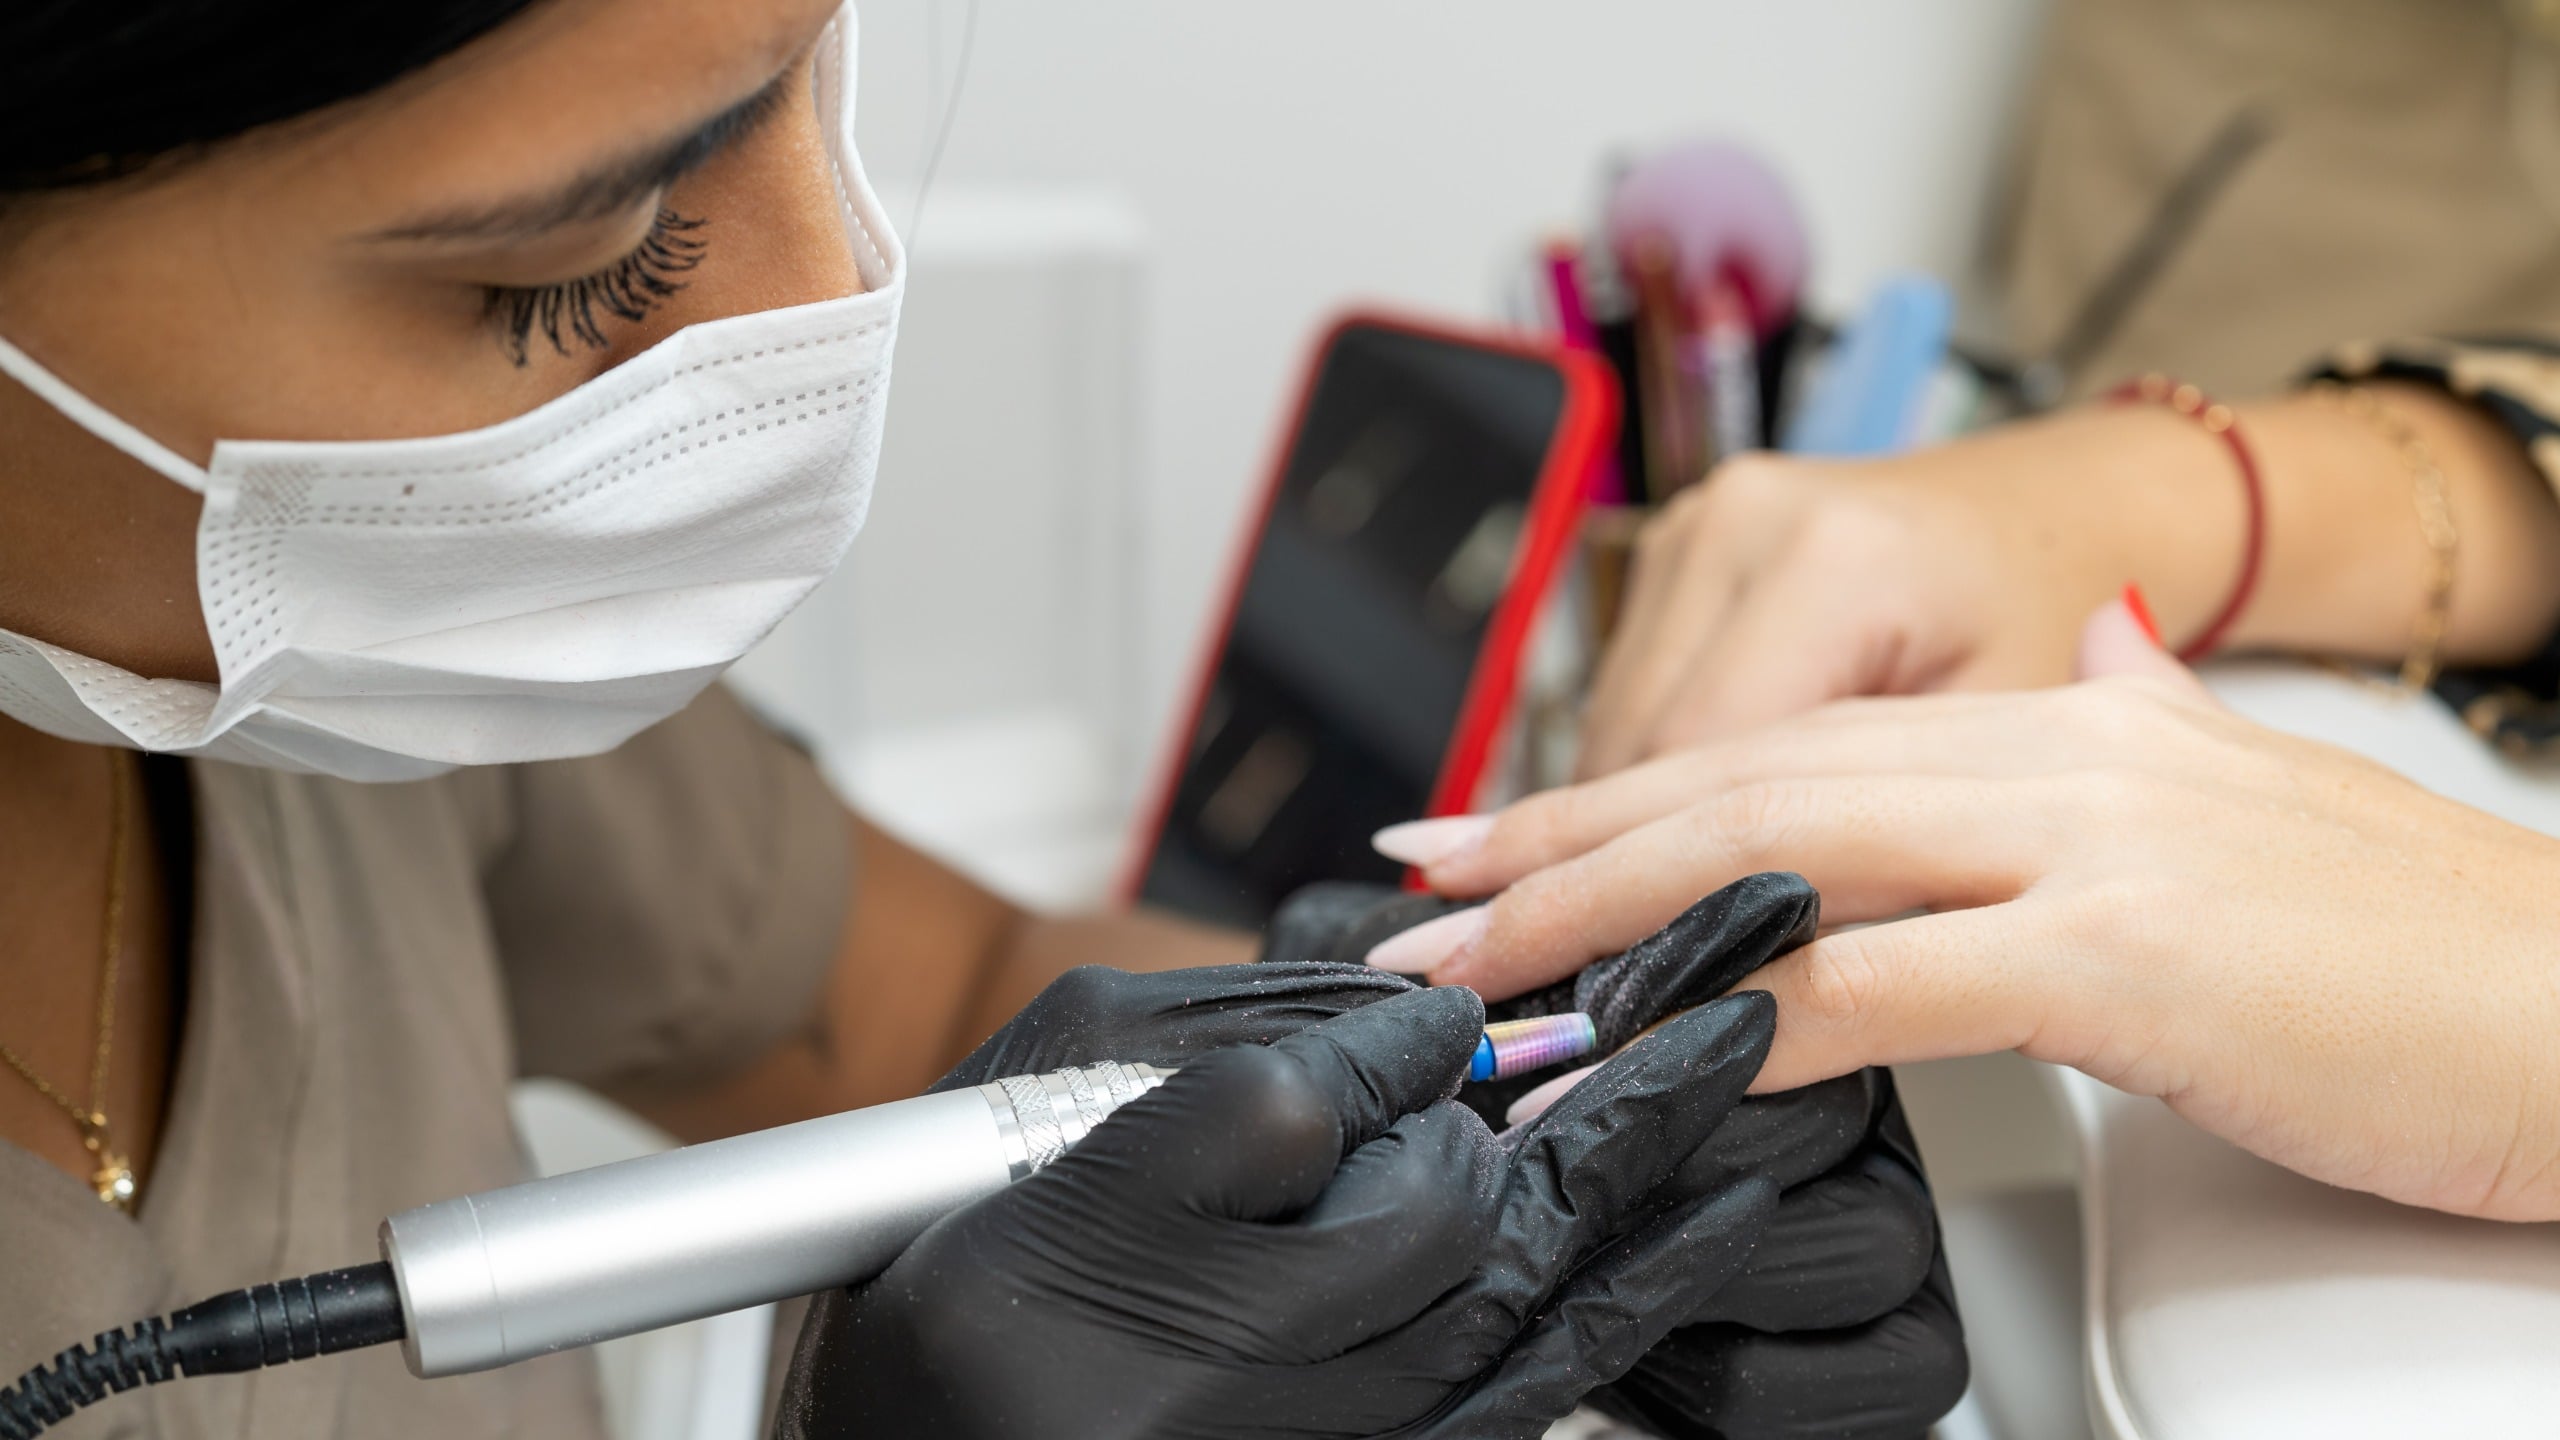
In pursuit of the perfect manicure, people in the United States spend more than $8 billion each year at nail salons.

Nails are filed, polish pared back with acetone, and acrylic dust piled atop glued-on plastic tips, bound with a liquid monomer and fixed with UV.

And that’s all before the final coat of color.

When you’re getting your nails done, you’re only breathing in the fumes from the various chemicals involved for the length of your appointment. But for nail technicians, that exposure is day-in, day-out, for hours on end.

A new study published in the journal Risk Analysis reveals that concentrations of chemicals associated with cancer and other health risks can vary widely throughout the workday at five different New York City nail salons, sometimes reaching levels the lead researcher says are on par with industrial chemical manufacturing facilities.

“This research shows that traditional air sampling and risk assessment methods don’t tell the whole story for nail salons,” says Anthony Ierardi, an occupational and environmental health and safety researcher at CUNY School of Public Health.

“Nail technicians and other salon employees may be exposed to high, intermittent peaks of airborne chemicals throughout the workday, yet the health impacts of those exposures have been underestimated.”

That’s largely because exposure risks have typically been measured as an average across the whole day. But many of the salons reached peak exposure levels well above the median, which means salon workers may be intermittently exposed to chemicals far beyond the levels that daily averages suggest.

In pursuit of the perfect manicure, people in the United States spend more than $8 billion each year at nail salons.

Nails are filed, polish pared back with acetone, and acrylic dust piled atop glued-on plastic tips, bound with a liquid monomer and fixed with UV.

And that’s all before the final coat of color.

When you’re getting your nails done, you’re only breathing in the fumes from the various chemicals involved for the length of your appointment. But for nail technicians, that exposure is day-in, day-out, for hours on end.

A new study published in the journal Risk Analysis reveals that concentrations of chemicals associated with cancer and other health risks can vary widely throughout the workday at five different New York City nail salons, sometimes reaching levels the lead researcher says are on par with industrial chemical manufacturing facilities.

“This research shows that traditional air sampling and risk assessment methods don’t tell the whole story for nail salons,” says Anthony Ierardi, an occupational and environmental health and safety researcher at CUNY School of Public Health.

“Nail technicians and other salon employees may be exposed to high, intermittent peaks of airborne chemicals throughout the workday, yet the health impacts of those exposures have been underestimated.”

That’s largely because exposure risks have typically been measured as an average across the whole day. But many of the salons reached peak exposure levels well above the median, which means salon workers may be intermittently exposed to chemicals far beyond the levels that daily averages suggest.

0

‘Toxic’ and ‘radioactive’: Labour MPs turn on Palestine Action ban after 4,000 arrests

Middle East Monitor ‘Toxic’ and ‘radioactive’: Labour MPs turn on Palestine Action ban after 4,000 arrests www.middleeastmonitor.com
preview

UK grandmas who got arrested for protesting about the Palestinian Genocide: 1

UK government: 0

UK grandmas who got arrested for protesting about the Palestinian Genocide: 1

UK government: 0

0

Refugee from slrpnk

preview

Hi everyone, I have just joined your instance a couple days ago, this my first post. I am a refugee from solarpunk Lemmy instance which died recently. So far so good. Trying to unlearn muscle memory of downvoting

Hi everyone, I have just joined your instance a couple days ago, this my first post. I am a refugee from solarpunk Lemmy instance which died recently. So far so good. Trying to unlearn muscle memory of downvoting

0

XHR by CEM, The data request API made right.

preview

XHR by CEM, The data request API made right.
Streaming, parsing, validating in browser and CLI. All formats from CSV to JSON supported.

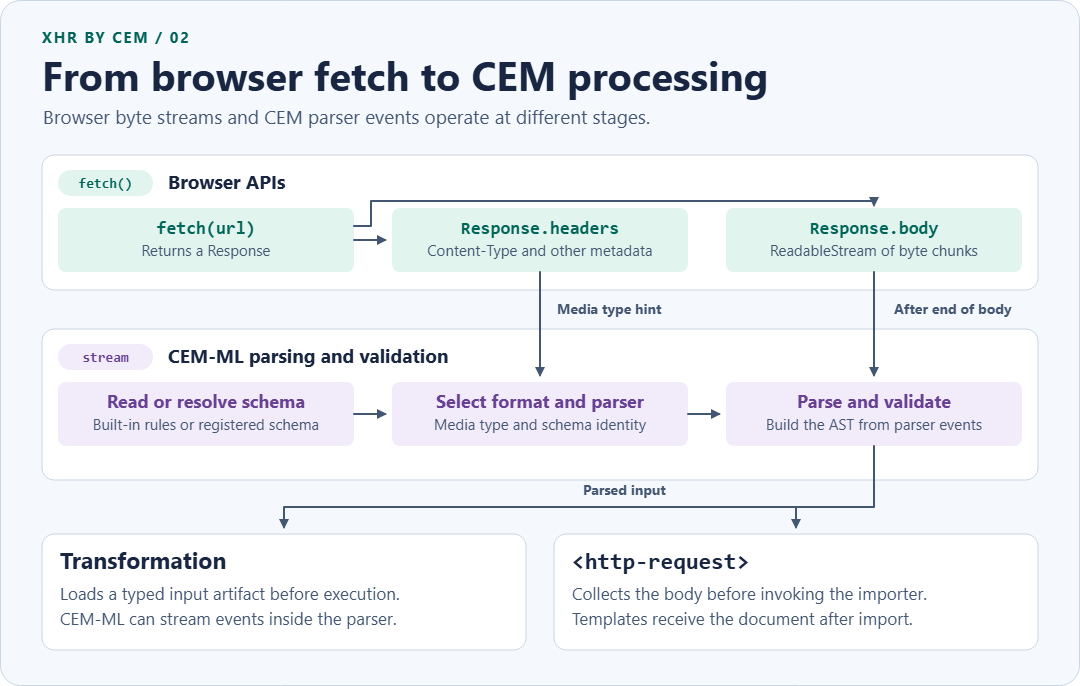
CEM-ML parses the response off the UI thread. The main thread collects the response bytes, then sends them to a Web Worker, where the CEM-ML WASM importer parses them and retains the document.

https://blog.firsov.net/2026/11/xhr-by-cem-data-request-api-made-right.html

@webdev #webDev @w3c

XHR by CEM, The data request API made right.
Streaming, parsing, validating in browser and CLI. All formats from CSV to JSON supported.

CEM-ML parses the response off the UI thread. The main thread collects the response bytes, then sends them to a Web Worker, where the CEM-ML WASM importer parses them and retains the document.

https://blog.firsov.net/2026/11/xhr-by-cem-data-request-api-made-right.html

@webdev #webDev @w3c

0

How ICE Keeps an Eye on Protestors

The New Republic How ICE Keeps an Eye on Protestors newrepublic.com
preview

While much of the florid, fashy antics of Immigration and Customs Enforcement, or ICE, has lingered long in the memory, there’s one thing the agency has been doing that’s largely flown under the radar—its efforts to surveil protesters using sophisticated tracking technologies. This represents a realization of warnings that privacy advocates have long expressed: the tools of the war on terror would be turned on Americans by an authoritarian. According to a recent report from Wired, during the unrest in Minne…

While much of the florid, fashy antics of Immigration and Customs Enforcement, or ICE, has lingered long in the memory, there’s one thing the agency has been doing that’s largely flown under the radar—its efforts to surveil protesters using sophisticated tracking technologies. This represents a realization of warnings that privacy advocates have long expressed: the tools of the war on terror would be turned on Americans by an authoritarian. According to a recent report from Wired, during the unrest in Minne…

0

Klimastreik 13.11.2026 | Fridays for Future

Fridays for Future Klimastreik 13.11.2026 | Fridays for Future fridaysforfuture.de
preview

Falls jemand an dem Tag noch keinen Tisch beim Italiener reserviert hat und das noch nicht mitbekommen hat…

Falls jemand an dem Tag noch keinen Tisch beim Italiener reserviert hat und das noch nicht mitbekommen hat…

-2

I made Typefill Forms, a free Firefox add-on that remembers forms you've filled

preview

Same maker as the text expander I posted here a few days ago. This one is for forms.

Fill a form once, hit Save, and next time it’s one click. It can also fill on its own when the page opens, which helps on forms that load late.

Free, no limit on saved forms, no account, and it doesn’t send anything off your computer. It won’t keep card numbers, bank details or passwords.

addons.mozilla.org/en-US/…/typefill-forms/

If a field gets missed somewhere, tell me where.

Same maker as the text expander I posted here a few days ago. This one is for forms.

Fill a form once, hit Save, and next time it’s one click. It can also fill on its own when the page opens, which helps on forms that load late.

Free, no limit on saved forms, no account, and it doesn’t send anything off your computer. It won’t keep card numbers, bank details or passwords.

addons.mozilla.org/en-US/…/typefill-forms/

If a field gets missed somewhere, tell me where.

0

Fallout 76 Daily Update

preview

Atomic Shop

  • Ghillie Hunting Rifle Paint (250⚛️ (50% off!)), Leaves on (10-Nov-2026)
  • Cryptid Series: Flatwoods Monster Bundle (1800⚛️), Leaves on (24-Nov-2026)
  • Cryptid Series: Sheepsquatch Bundle (1500⚛️), Leaves on (24-Nov-2026)
  • Enclave Laboratory Shelter (1800⚛️), Leaves on (24-Nov-2026)
  • Enclave Scientist Outfit (900⚛️), Leaves on (24-Nov-2026)
  • Mad Scientist Bundle (960⚛️ (20% off!)), Leaves on (24-Nov-2026)
  • Edge of Science Bundle (2200⚛️), Leaves on (24-Nov-2026)
  • Body Scanner (700⚛️), Leaves on (24-Nov-2026)
  • Enclave Sigma Squad Tesla Rifle Paint (500⚛️), Leaves on (24-Nov-2026)
  • Anatomy Screen (250⚛️), Leaves on (24-Nov-2026)
  • Abandoned Nest (Free (FO1st)), Leaves on (1-Dec-2026)
  • Speckled Axolotl Plushie (Free), Leaves on (1-Dec-2026)

Current Events

  • Season 26: Beware the Blood Moon, Ends on (1-Dec-2026)

Fishing

  • Speckled Axolotl, Regions: Cranberry Bog & Forest, Changes on: (1-Dec-2026)
  • Festerkoi, Regions: Ash Heap, Burning Springs, Toxic Valley, Changes on: (22-Dec-2026)
  • Sludge Eye, Location: The Sludge Works, Changes on: (22-Dec-2026)

Daily Challenges

  • 1ˢᵗ Kill Insects (x5) 250
  • ⭐ Gold Star: Complete a Daily Challenge (x6) 1000
  • Build a Decoration in a Shelter (x5) 250
  • Collect a piece of Bone (x3) 250
  • Eat a Cake, Pie, or Candy (x10) 250
  • Kill an Enemy with a Shovel during the “Disturbed Grave” Quest (x6) 250
  • Sell Swamp Tofu to an NPC vendor (x1) 250
  • Sell a Shotgun to an NPC vendor (x1) 250

Minerva’s Location: Away She will next be at The Whitespring Resort on 12-Nov-2026

Daily OPS: Uplink

  • Location: Charleston Capitol Building
  • Enemy Faction: Pint-Sized Phantoms
  • Enemy Mutations: Piercing Gaze, Group Regeneration

Atomic Shop

  • Ghillie Hunting Rifle Paint (250⚛️ (50% off!)), Leaves on (10-Nov-2026)
  • Cryptid Series: Flatwoods Monster Bundle (1800⚛️), Leaves on (24-Nov-2026)
  • Cryptid Series: Sheepsquatch Bundle (1500⚛️), Leaves on (24-Nov-2026)
  • Enclave Laboratory Shelter (1800⚛️), Leaves on (24-Nov-2026)
  • Enclave Scientist Outfit (900⚛️), Leaves on (24-Nov-2026)
  • Mad Scientist Bundle (960⚛️ (20% off!)), Leaves on (24-Nov-2026)
  • Edge of Science Bundle (2200⚛️), Leaves on (24-Nov-2026)
  • Body Scanner (700⚛️), Leaves on (24-Nov-2026)
  • Enclave Sigma Squad Tesla Rifle Paint (500⚛️), Leaves on (24-Nov-2026)
  • Anatomy Screen (250⚛️), Leaves on (24-Nov-2026)
  • Abandoned Nest (Free (FO1st)), Leaves on (1-Dec-2026)
  • Speckled Axolotl Plushie (Free), Leaves on (1-Dec-2026)

Current Events

  • Season 26: Beware the Blood Moon, Ends on (1-Dec-2026)

Fishing

  • Speckled Axolotl, Regions: Cranberry Bog & Forest, Changes on: (1-Dec-2026)
  • Festerkoi, Regions: Ash Heap, Burning Springs, Toxic Valley, Changes on: (22-Dec-2026)
  • Sludge Eye, Location: The Sludge Works, Changes on: (22-Dec-2026)

Daily Challenges

  • 1ˢᵗ Kill Insects (x5) 250
  • ⭐ Gold Star: Complete a Daily Challenge (x6) 1000
  • Build a Decoration in a Shelter (x5) 250
  • Collect a piece of Bone (x3) 250
  • Eat a Cake, Pie, or Candy (x10) 250
  • Kill an Enemy with a Shovel during the “Disturbed Grave” Quest (x6) 250
  • Sell Swamp Tofu to an NPC vendor (x1) 250
  • Sell a Shotgun to an NPC vendor (x1) 250

Minerva’s Location: Away She will next be at The Whitespring Resort on 12-Nov-2026

Daily OPS: Uplink

  • Location: Charleston Capitol Building
  • Enemy Faction: Pint-Sized Phantoms
  • Enemy Mutations: Piercing Gaze, Group Regeneration
0

Daily community recommendation: !asklemmy@lemmy.world

preview

Ask Lemmy— Join 42,000+ curious minds at !asklemmy for daily open-ended questions and friendly discussion.

42,301 subscribers
50 posts per month
2,920 comments per month

A Fediverse community for open-ended, thought provoking questions

Sample discussion: I’m new on Lemmy. What I’m supposed to know here ? (281 votes, 446 comments)

➡️ !asklemmy@lemmy.world (lemmy.world/c/asklemmy)

Know an underrated community? Send the bot a private message with !suggest !community@instance and it joins the candidate pool.

Ask Lemmy— Join 42,000+ curious minds at !asklemmy for daily open-ended questions and friendly discussion.

42,301 subscribers
50 posts per month
2,920 comments per month

A Fediverse community for open-ended, thought provoking questions

Sample discussion: I’m new on Lemmy. What I’m supposed to know here ? (281 votes, 446 comments)

➡️ !asklemmy@lemmy.world (lemmy.world/c/asklemmy)

Know an underrated community? Send the bot a private message with !suggest !community@instance and it joins the candidate pool.

0

aerynOS Improves Moss Package Manager in Latest Unstable Stream Update

Linuxiac aerynOS Improves Moss Package Manager in Latest Unstable Stream Update linuxiac.com
preview

The aerynOS team has published its latest unstable stream update, introducing Linux kernel 7.2.15, which marks the final release in the 7.2 series. The team is preparing to move to version 7.3, expected to arrive in the volatile repository soon.

The update also includes Linux LTS 6.18.62, along with newer versions of several system components, including systemd 261.5, LLVM 23.1.5, and glibc 2.44 development snapshots.

On the package management side, Moss now displays help when users enter the older moss install and moss remove commands or their aliases. Boulder and Ent have also been updated to use a new versioning format for packages built from Git commits.

Desktop updates include KDE Gear 26.08.3, Hyprland 0.57.1, Dux suite 2.1 (formerly Dank Material Shell), Waybar 0.16, and Mir 2.31, accompanied by a rebuild of Miracle WM.

KWin receives a fix for crashes involving DisplayLink docking stations when running fullscreen applications. Additional upstream NVIDIA fixes address graphical glitches, flickering, and buffer allocation problems.

COSMIC Player receives missing GStreamer dependencies, restoring audio and video playback. Meanwhile, both Ghostty and Kitty have fixes for Bash shell startup integration.

Other notable package updates include GStreamer 1.28.9, Poppler 26.11, Zed 1.27, Signal Desktop 8.34, and PowerStation 0.9. The Poppler update includes printing fixes, while additional character maps required by Ghostscript have been added.

Moreover, Rsync now includes daemon service units and the rrsync restricted helper. Zulip Desktop also gets a fix for flashing when using dark mode, along with a new application theme selector.

Finally, several new packages have been added to the repositories, including the terminal-based bandwidth monitor bandwhich, the disk usage utility duf, Gitea’s official command-line client, GNU Stow, and openfortivpn.

KDE’s KeepSecret password manager and the JetBrains Mono typeface are also newly available.

For more information, see the announcement.

The aerynOS team has published its latest unstable stream update, introducing Linux kernel 7.2.15, which marks the final release in the 7.2 series. The team is preparing to move to version 7.3, expected to arrive in the volatile repository soon.

The update also includes Linux LTS 6.18.62, along with newer versions of several system components, including systemd 261.5, LLVM 23.1.5, and glibc 2.44 development snapshots.

On the package management side, Moss now displays help when users enter the older moss install and moss remove commands or their aliases. Boulder and Ent have also been updated to use a new versioning format for packages built from Git commits.

Desktop updates include KDE Gear 26.08.3, Hyprland 0.57.1, Dux suite 2.1 (formerly Dank Material Shell), Waybar 0.16, and Mir 2.31, accompanied by a rebuild of Miracle WM.

KWin receives a fix for crashes involving DisplayLink docking stations when running fullscreen applications. Additional upstream NVIDIA fixes address graphical glitches, flickering, and buffer allocation problems.

COSMIC Player receives missing GStreamer dependencies, restoring audio and video playback. Meanwhile, both Ghostty and Kitty have fixes for Bash shell startup integration.

Other notable package updates include GStreamer 1.28.9, Poppler 26.11, Zed 1.27, Signal Desktop 8.34, and PowerStation 0.9. The Poppler update includes printing fixes, while additional character maps required by Ghostscript have been added.

Moreover, Rsync now includes daemon service units and the rrsync restricted helper. Zulip Desktop also gets a fix for flashing when using dark mode, along with a new application theme selector.

Finally, several new packages have been added to the repositories, including the terminal-based bandwidth monitor bandwhich, the disk usage utility duf, Gitea’s official command-line client, GNU Stow, and openfortivpn.

KDE’s KeepSecret password manager and the JetBrains Mono typeface are also newly available.

For more information, see the announcement.

0

I'm glad Texas flipped blue, in a few years when nothing has fundamentally changed more people will wake up to the flaws of a two party system

preview

Democrats exist to prevent social movement from actually accomplishing anything, this is established fact. Yet so many people truly believe that the slightly less horrible but still very neoliberal party will fix everything out of the goodness of their hearts. Hopefully people are paying attention to Texas and will see that we need a real solution, not just flipping between the fascist party and the diet fascist party.

Democrats exist to prevent social movement from actually accomplishing anything, this is established fact. Yet so many people truly believe that the slightly less horrible but still very neoliberal party will fix everything out of the goodness of their hearts. Hopefully people are paying attention to Texas and will see that we need a real solution, not just flipping between the fascist party and the diet fascist party.

0

Slax 2026.11 Released with Debian 13, Redesigned Desktop, and AI Assistant

Linuxiac Slax 2026.11 Released with Debian 13, Redesigned Desktop, and AI Assistant linuxiac.com
preview

Slax developer Tomas Matejicek has announced Slax 2026.11, a new version of the lightweight, portable Linux distribution designed to run from a USB drive. Based on Debian 13 and powered by the Linux kernel 6.12, the release features a redesigned desktop, a built-in AI assistant, Secure Boot support, and a graphical installer, all packed into a 512 MiB ISO image.

The desktop has been overhauled with Alt+Tab window previews, live taskbar thumbnails, and four virtual workspaces. Users can view all workspaces simultaneously with Alt+F3 or switch between them using Ctrl+F1 through F4.

The desktop also supports files and folders, and the taskbar includes keyboard layout switching and volume controls. Application interfaces have been adjusted for a more consistent appearance across older and newer programs.

The application launcher has been improved as well. Optional applications are marked with a download icon, letting users install and launch them from the menu. Traditional package management through APT remains available.

One of the most notable additions is the Slax AI Assistant, which allows users to troubleshoot problems, inspect their systems, and execute commands using natural-language instructions. It helps identify disk space usage, investigate system issues, and perform administrative tasks. The assistant requires an internet connection and user sign-in.

Slax 2026.11 also includes a graphical installer for Windows and Linux. Users can create bootable USB drives or install Slax alongside an existing operating system on supported configurations. Additionally, UEFI Secure Boot is now supported through a signed bootloader and kernel, eliminating the need to disable Secure Boot on compatible machines.

Another improvement concerns persistent sessions. A single USB drive can store multiple named sessions, each retaining its own applications, files, and settings. Users can select a session at startup, duplicate it using F4, or rename it with F6, as these sessions can be carried between computers.

For disk maintenance and recovery, Slax includes a graphical partition manager that supports creating, resizing, and formatting partitions. Additional utilities support LVM, LUKS encryption, and filesystems such as XFS. VirtualBox, VMware, and SPICE integration is also included for virtual machine environments.

However, users depending on Slax’s modular system should note an important change. The distribution now uses OverlayFS instead of AUFS, so the slax activate and slax deactivate commands can no longer dynamically load or unload .sb modules during a running session.

Modules can still be included before boot, while installing software through APT and preserving changes in persistent sessions remain supported.

For more information, see the announcement.

Slax developer Tomas Matejicek has announced Slax 2026.11, a new version of the lightweight, portable Linux distribution designed to run from a USB drive. Based on Debian 13 and powered by the Linux kernel 6.12, the release features a redesigned desktop, a built-in AI assistant, Secure Boot support, and a graphical installer, all packed into a 512 MiB ISO image.

The desktop has been overhauled with Alt+Tab window previews, live taskbar thumbnails, and four virtual workspaces. Users can view all workspaces simultaneously with Alt+F3 or switch between them using Ctrl+F1 through F4.

The desktop also supports files and folders, and the taskbar includes keyboard layout switching and volume controls. Application interfaces have been adjusted for a more consistent appearance across older and newer programs.

The application launcher has been improved as well. Optional applications are marked with a download icon, letting users install and launch them from the menu. Traditional package management through APT remains available.

One of the most notable additions is the Slax AI Assistant, which allows users to troubleshoot problems, inspect their systems, and execute commands using natural-language instructions. It helps identify disk space usage, investigate system issues, and perform administrative tasks. The assistant requires an internet connection and user sign-in.

Slax 2026.11 also includes a graphical installer for Windows and Linux. Users can create bootable USB drives or install Slax alongside an existing operating system on supported configurations. Additionally, UEFI Secure Boot is now supported through a signed bootloader and kernel, eliminating the need to disable Secure Boot on compatible machines.

Another improvement concerns persistent sessions. A single USB drive can store multiple named sessions, each retaining its own applications, files, and settings. Users can select a session at startup, duplicate it using F4, or rename it with F6, as these sessions can be carried between computers.

For disk maintenance and recovery, Slax includes a graphical partition manager that supports creating, resizing, and formatting partitions. Additional utilities support LVM, LUKS encryption, and filesystems such as XFS. VirtualBox, VMware, and SPICE integration is also included for virtual machine environments.

However, users depending on Slax’s modular system should note an important change. The distribution now uses OverlayFS instead of AUFS, so the slax activate and slax deactivate commands can no longer dynamically load or unload .sb modules during a running session.

Modules can still be included before boot, while installing software through APT and preserving changes in persistent sessions remain supported.

For more information, see the announcement.

0

Asahi Linux Drops MIT and Goes Full GPL After AI Tools Were Used to Steal Unreleased Code

It's FOSS Asahi Linux Drops MIT and Goes Full GPL After AI Tools Were Used to Steal Unreleased Code itsfoss.com
preview

Well, well, well…

Asahi Linux is the reason you can run Linux on an Apple Silicon Mac today. For years, the project put most of its own code under the MIT license so that anyone, including the BSDs, could reuse it as needed.

That is changing because Asahi Linux is tired of code laundering. They have announced that Asahi is moving all of its repositories to the GNU General Public License version 2 or later. Going forward, all Asahi Linux code will be under strong copyleft licenses only.

This is because people were taking in-development code straight out of their personal forks, publishing it without credit, or rewriting it with AI to hide its origin for “replacing the project and aggressively monetising Linux on Apple Silicon.”

What is code laundering?

Code laundering (also called license laundering) is the practice of taking someone else’s code and passing it through a process that hides where it came from, so you can use it without honoring the original license or crediting the author.

Before AI, this usually meant manually rewriting code line by line, renaming variables and stuff, and shuffling functions around until it no longer looked like the original.

LLMs made it much more easy and cheaper of course.

The MIT license only asks you to keep the original copyright notice. It doesn’t require you to share your changes or keep your version open. That’s what makes it popular, and it’s also what made things problematic for Asahi here.

Learning from history

The move has come after the Asahi team was made aware “some time ago” of multiple attempts to exploit its permissive licensing to hijack its work.

In the most extreme cases, feature code that was still under development was lifted from developers’ personal forks before it was even publicly released. The report points out that the MIT license “explicitly allows this, and has no carveouts to protect against bad faith actors.”

Asahi didn’t name anyone in the report. It also didn’t spell out how existing contributions will be relicensed or whether every past contributor agreed to it.

Asahi draws parallels with WINE’s situation two decades ago. WINE, the compatibility layer that lets you run Windows apps on Linux, was originally MIT-licensed too. But in the late 90s and early 2000s, companies took the code, built proprietary forks on top of it, and sold them commercially. So, in 2002, the WINE team relicensed to the LGPL to discourage proprietary forks and push companies to contribute upstream.

Those who do not learn from history are doomed to repeat it

Asahi has been upset lately

Asahi didn’t name anyone so we are left with guesswork on who they are targeting with this license move.

There have been at least two public forks of Asahi’s work in recent months, both tied to AI-assisted development. In case you did not know, Asahi Linux forbids AI generated code contribution.

The first is Aurora Silicon and its Vulkan driver, Borealis. Borealis is a fork of Asahi’s HoneyKrisp, the Vulkan driver for Apple GPUs. Aurora Silicon submitted a pull request to register its own Vulkan driver ID with Khronos (VK_DRIVER_ID_AURORA_BOREALIS), says the driver runs on M1 to M5 and the A18 Pro, and keeps it in its own Mesa fork rather than upstream.

The second is Gravity Linux, a Fedora-based distro for Apple Silicon. It was forked from Asahi over the disagreement about LLM use.

To be fair to Gravity, it is open source, it isn’t selling anything, and it credits its AI use openly. It even says it plans to sunset the distro once its driver work lands upstream.

It isn’t the kind of bad actor the progress report describes. But it does represent the “permissive fork that embraces AI” approach that Asahi has consistently pushed back against.

For clarification, Asahi’s progress report does not mention Aurora Silicon or Gravity Linux by name. I have provided their conflict with Asahi as context.

Why this license change matters

As far as I can tell, this is the first time a major open source project has moved to copyleft specifically because of AI-assisted code laundering. Projects have relicensed before, but usually to stop cloud providers from reselling their work as a service. This one is specifically about AI.

I wouldn’t be surprised if more hardware enablement and reverse-engineering projects follow. Making the first changes takes a lot of time and effort but they are easier to “rewrite” once someone has done the hard part.

Will the GPL actually help?

If the problem is people who already ignore the MIT license, why would they respect the GPL? After all, GPL cannot stop a determined bad actor. Nothing does, actually.

Stripping attribution from MIT code already breaks the MIT license, since keeping the copyright notice is its one real condition.

What the GPL changes is the commercial benefit. Under MIT, someone can take Asahi’s code, close it up, and sell a product, and that’s perfectly legal as long as the notice stays in.

Under the GPL, anyone who distributes a modified version has to release the source under the same license. You can’t legally build a closed, paid Apple Silicon distro on top of GPL code. And if a product’s source has to be public, the copying is easier to spot. Not everyone is happy

The move has drawn criticism, particularly from the BSD side, which was one of the main reasons Asahi chose MIT in the first place. OpenBSD’s Apple Silicon support relies on Asahi’s m1n1 bootloader.

OpenBSD developer Bryan Steele wrote on X:

"Sad to see Asahi out there burning bridges for no reason.. relicensing m1n1 and drivers under GPL2-or-later, seemingly without the consent of all prior contributors, under the guise of "defending against AI bad actors", seems entirely disingenuous and misguided."

Wrapping up

Asahi is betting that copyleft license provides a better defense in this changed world where anyone can launder code with a prompt.

It may not stop the bad actors from rewriting its code, but at least it reduces the chances of a closed commercial fork.

It would be interesting to see whether the BSD community finds a way to keep working with Asahi under the new terms.
Well, well, well…

Asahi Linux is the reason you can run Linux on an Apple Silicon Mac today. For years, the project put most of its own code under the MIT license so that anyone, including the BSDs, could reuse it as needed.

That is changing because Asahi Linux is tired of code laundering. They have announced that Asahi is moving all of its repositories to the GNU General Public License version 2 or later. Going forward, all Asahi Linux code will be under strong copyleft licenses only.

This is because people were taking in-development code straight out of their personal forks, publishing it without credit, or rewriting it with AI to hide its origin for “replacing the project and aggressively monetising Linux on Apple Silicon.”

What is code laundering?

Code laundering (also called license laundering) is the practice of taking someone else’s code and passing it through a process that hides where it came from, so you can use it without honoring the original license or crediting the author.

Before AI, this usually meant manually rewriting code line by line, renaming variables and stuff, and shuffling functions around until it no longer looked like the original.

LLMs made it much more easy and cheaper of course.

The MIT license only asks you to keep the original copyright notice. It doesn’t require you to share your changes or keep your version open. That’s what makes it popular, and it’s also what made things problematic for Asahi here.

Learning from history

The move has come after the Asahi team was made aware “some time ago” of multiple attempts to exploit its permissive licensing to hijack its work.

In the most extreme cases, feature code that was still under development was lifted from developers’ personal forks before it was even publicly released. The report points out that the MIT license “explicitly allows this, and has no carveouts to protect against bad faith actors.”

Asahi didn’t name anyone in the report. It also didn’t spell out how existing contributions will be relicensed or whether every past contributor agreed to it.

Asahi draws parallels with WINE’s situation two decades ago. WINE, the compatibility layer that lets you run Windows apps on Linux, was originally MIT-licensed too. But in the late 90s and early 2000s, companies took the code, built proprietary forks on top of it, and sold them commercially. So, in 2002, the WINE team relicensed to the LGPL to discourage proprietary forks and push companies to contribute upstream.

Those who do not learn from history are doomed to repeat it

Asahi has been upset lately

Asahi didn’t name anyone so we are left with guesswork on who they are targeting with this license move.

There have been at least two public forks of Asahi’s work in recent months, both tied to AI-assisted development. In case you did not know, Asahi Linux forbids AI generated code contribution.

The first is Aurora Silicon and its Vulkan driver, Borealis. Borealis is a fork of Asahi’s HoneyKrisp, the Vulkan driver for Apple GPUs. Aurora Silicon submitted a pull request to register its own Vulkan driver ID with Khronos (VK_DRIVER_ID_AURORA_BOREALIS), says the driver runs on M1 to M5 and the A18 Pro, and keeps it in its own Mesa fork rather than upstream.

The second is Gravity Linux, a Fedora-based distro for Apple Silicon. It was forked from Asahi over the disagreement about LLM use.

To be fair to Gravity, it is open source, it isn’t selling anything, and it credits its AI use openly. It even says it plans to sunset the distro once its driver work lands upstream.

It isn’t the kind of bad actor the progress report describes. But it does represent the “permissive fork that embraces AI” approach that Asahi has consistently pushed back against.

For clarification, Asahi’s progress report does not mention Aurora Silicon or Gravity Linux by name. I have provided their conflict with Asahi as context.

Why this license change matters

As far as I can tell, this is the first time a major open source project has moved to copyleft specifically because of AI-assisted code laundering. Projects have relicensed before, but usually to stop cloud providers from reselling their work as a service. This one is specifically about AI.

I wouldn’t be surprised if more hardware enablement and reverse-engineering projects follow. Making the first changes takes a lot of time and effort but they are easier to “rewrite” once someone has done the hard part.

Will the GPL actually help?

If the problem is people who already ignore the MIT license, why would they respect the GPL? After all, GPL cannot stop a determined bad actor. Nothing does, actually.

Stripping attribution from MIT code already breaks the MIT license, since keeping the copyright notice is its one real condition.

What the GPL changes is the commercial benefit. Under MIT, someone can take Asahi’s code, close it up, and sell a product, and that’s perfectly legal as long as the notice stays in.

Under the GPL, anyone who distributes a modified version has to release the source under the same license. You can’t legally build a closed, paid Apple Silicon distro on top of GPL code. And if a product’s source has to be public, the copying is easier to spot. Not everyone is happy

The move has drawn criticism, particularly from the BSD side, which was one of the main reasons Asahi chose MIT in the first place. OpenBSD’s Apple Silicon support relies on Asahi’s m1n1 bootloader.

OpenBSD developer Bryan Steele wrote on X:

"Sad to see Asahi out there burning bridges for no reason.. relicensing m1n1 and drivers under GPL2-or-later, seemingly without the consent of all prior contributors, under the guise of "defending against AI bad actors", seems entirely disingenuous and misguided."

Wrapping up

Asahi is betting that copyleft license provides a better defense in this changed world where anyone can launder code with a prompt.

It may not stop the bad actors from rewriting its code, but at least it reduces the chances of a closed commercial fork.

It would be interesting to see whether the BSD community finds a way to keep working with Asahi under the new terms.