
400

PSA: Recent Influx of LLM Bots

preview

Edit at the top:

If you see anything from a user at 1095.me, just report. Its pretty guaranteed to be a bot, usually with spam links embedded. They were cropping up a little bit back and seem to be going another round.


The Lemmy.world TOS requires that any bot account be set as such in their profile, and that any community they post to requires approval first.

Generically speaking, I won’t be approving any. What I mean by that is any bot request is going to need a valid and real reason for its use here, which I would then bring to the community to make that choice like I did for the rules discussion threads. I wish there were a better way than a basic upvote or downvote system for feedback, but its what we’ve got so its what I’ll use.

I have not posted about any new bots since I took over here a few months ago, so no new bots should be considered as having community approval.

If you see them, please just report and I’ll get to it as soon as possible. The current one seems to just be getting new accounts all over the fediverse, and tacking their home instance onto the end. They are banned, but I’ll have to ban again as things come up. I’ll bring this up to the lemmy.world admins as well. This also goes for any other new bot that begins flooding the community.

Thanks!

Edit at the top:

If you see anything from a user at 1095.me, just report. Its pretty guaranteed to be a bot, usually with spam links embedded. They were cropping up a little bit back and seem to be going another round.


The Lemmy.world TOS requires that any bot account be set as such in their profile, and that any community they post to requires approval first.

Generically speaking, I won’t be approving any. What I mean by that is any bot request is going to need a valid and real reason for its use here, which I would then bring to the community to make that choice like I did for the rules discussion threads. I wish there were a better way than a basic upvote or downvote system for feedback, but its what we’ve got so its what I’ll use.

I have not posted about any new bots since I took over here a few months ago, so no new bots should be considered as having community approval.

If you see them, please just report and I’ll get to it as soon as possible. The current one seems to just be getting new accounts all over the fediverse, and tacking their home instance onto the end. They are banned, but I’ll have to ban again as things come up. I’ll bring this up to the lemmy.world admins as well. This also goes for any other new bot that begins flooding the community.

Thanks!

150

Results: 2026 Self-Host User Survey (selfh.st)

selfh.st 2026 Self-Host User Survey Results selfh.st
preview

Hey, c/selfhosted! Thanks to all who participated in my recent ‘2026 Self-Host User Survey’. This community contributed a bunch to this year’s increase in respondents (+52%), and I’m incredibly grateful for the support.

The results are visualized as usual via Chart.js. Happy to talk through any of the results or provide more details where things might not be clear.

New this year is a section on AI usage, a Linux distribution question, and the ability to overlay prior year responses on the charts for easier year-over-year comparisons.

Thanks again!

Hey, c/selfhosted! Thanks to all who participated in my recent ‘2026 Self-Host User Survey’. This community contributed a bunch to this year’s increase in respondents (+52%), and I’m incredibly grateful for the support.

The results are visualized as usual via Chart.js. Happy to talk through any of the results or provide more details where things might not be clear.

New this year is a section on AI usage, a Linux distribution question, and the ability to overlay prior year responses on the charts for easier year-over-year comparisons.

Thanks again!

131

How do you solve email?

preview

This Microsoft outage being the last drop in the bucket, I'm looking to get my email/calendar/contacts somewhere under my control.

As I already self-host a number of things (e.g. my Linux ISO collection), and have services exposed to the internet, it would make sense to run it at home.

After all, it's not heavy lifting. It's not hosting 500+ mailboxes for 100+ people. It's just little old me, with a handful of domains, catch-all receiving and a few dedicated sending addresses.

However email is a bit more mission critical than my smarthome control or self hosted LLMs. Downtime could be critically bad, and I still don't trust my home setup to be truly 99.999999% available.

I don't mind paying for a service but if I do I'd prefer something European, given I'm based in the UK (and otherwise am an EU citizen).

I'm really curious how y'all solve it. I guess I'm interested in some kind of hybrid solution where there's my own server and a hosted service, latter which acts as a backup solution, but still fully synced, so if my internet or power goes out (or my server goes down), I can still get mail sent and delivered.

So I'm not only just interested in the stack you run for email but the entire infrastructure, especially if you've solved this sort of off-site fallback service.

This Microsoft outage being the last drop in the bucket, I'm looking to get my email/calendar/contacts somewhere under my control.

As I already self-host a number of things (e.g. my Linux ISO collection), and have services exposed to the internet, it would make sense to run it at home.

After all, it's not heavy lifting. It's not hosting 500+ mailboxes for 100+ people. It's just little old me, with a handful of domains, catch-all receiving and a few dedicated sending addresses.

However email is a bit more mission critical than my smarthome control or self hosted LLMs. Downtime could be critically bad, and I still don't trust my home setup to be truly 99.999999% available.

I don't mind paying for a service but if I do I'd prefer something European, given I'm based in the UK (and otherwise am an EU citizen).

I'm really curious how y'all solve it. I guess I'm interested in some kind of hybrid solution where there's my own server and a hosted service, latter which acts as a backup solution, but still fully synced, so if my internet or power goes out (or my server goes down), I can still get mail sent and delivered.

So I'm not only just interested in the stack you run for email but the entire infrastructure, especially if you've solved this sort of off-site fallback service.

85

Linkwarden 2.17 - open-source collaborative bookmark manager to collect, read, annotate, and fully preserve what matters (+20k GitHub stars) [AIP]

GitHub GitHub - linkwarden/linkwarden: ⚡️⚡️⚡️ Self-hosted collaborative bookmark manager to collect, read, annotate, and fully preserve what matters, all in one place. github.com
preview

Hello everyone! Daniel here, and I’m back with Linkwarden 2.17, with updates across the web app, the mobile app, and the browser extension.

For those who are wondering, Linkwarden is an open-source collaborative bookmarking tool that keeps a permanent snapshot of the content of the links you save, so you can still access them even if the original content is no longer available. Linkwarden is available as a Cloud offering, or you can get the source code on GitHub and self-host it on your own server with no strings attached. If you find it useful, consider starring the repo so others can discover it too!

So let’s get into it.

What’s new

Custom order for links

You can now drag the links inside a collection into any order you like. Custom Order is the new default sort for collections, and you can switch back to sorting by date or name from the sort menu at any time. The order is saved with the collection, and new links are added to the top.

Much faster rendering of huge lists

Links, collections, and tags now only render what’s on screen, so scrolling through thousands of links stays smooth. The collection page got the same treatment, which helps a lot if you have thousands of collections.

Choose the details when saving a link

The new link sheet in the mobile app now lets you set a link’s name, collection, tags, description, and banner before saving it, instead of editing the link afterwards.

Email verification with a 6-digit code

Instead of a sign-in link, Linkwarden now emails you a 6-digit code to verify your email address.

Other noticeable improvements

  • Password changes sign out other devices: Changing your password now signs you out on every other device and revokes your access tokens. Resetting a forgotten password signs you out everywhere. If you use the browser extension or integrations like Floccus with an access token, you’ll need to sign them back in afterwards.
  • Password rate limiting: After 15 wrong passwords in a row, an account accepts only one attempt every 25 seconds. This makes guessing a password much slower without locking you out of your own account.
  • More security fixes: This release also fixes a number of moderate-severity security issues, thanks to everyone who reported them responsibly. We recommend updating to 2.17.
  • Search from the address bar: With the browser extension installed, type lw, press space, then type what you’re looking for and press Enter to search your Linkwarden links straight from the address bar. This works in Chrome, Firefox, and other Chromium-based browsers.
  • Import fixes: Imported links now keep the order of their original dates no matter in what order they were imported, Wallabag dates are read correctly, and larger imports are more reliable.
  • Custom AI tagging prompts: Self-hosted instances can now replace the prompt sent to the model for each AI tagging method with the AI_GENERATE_TAGS_PROMPT, AI_PREDEFINED_TAGS_PROMPT, and AI_EXISTING_TAGS_PROMPT environment variables. Check it out in the docs!
  • And more: As always, there’s a long tail of smaller fixes and improvements across the web app, the mobile app, and the browser extension.

Full Changelog: github.com/linkwarden/…/v2.16.3...v2.17.0

Thanks!
Thanks to everyone using Linkwarden, reporting bugs, suggesting improvements, contributing to the project, responsibly disclosing security issues, and supporting its development. A special thanks to all the security researchers who reported the issues fixed in this release. 💙

If you’d like to try Linkwarden without dealing with server setup and maintenance, our Cloud offering is the easiest way to get started.

Hope you enjoy the latest updates!

Hello everyone! Daniel here, and I’m back with Linkwarden 2.17, with updates across the web app, the mobile app, and the browser extension.

For those who are wondering, Linkwarden is an open-source collaborative bookmarking tool that keeps a permanent snapshot of the content of the links you save, so you can still access them even if the original content is no longer available. Linkwarden is available as a Cloud offering, or you can get the source code on GitHub and self-host it on your own server with no strings attached. If you find it useful, consider starring the repo so others can discover it too!

So let’s get into it.

What’s new

Custom order for links

You can now drag the links inside a collection into any order you like. Custom Order is the new default sort for collections, and you can switch back to sorting by date or name from the sort menu at any time. The order is saved with the collection, and new links are added to the top.

Much faster rendering of huge lists

Links, collections, and tags now only render what’s on screen, so scrolling through thousands of links stays smooth. The collection page got the same treatment, which helps a lot if you have thousands of collections.

Choose the details when saving a link

The new link sheet in the mobile app now lets you set a link’s name, collection, tags, description, and banner before saving it, instead of editing the link afterwards.

Email verification with a 6-digit code

Instead of a sign-in link, Linkwarden now emails you a 6-digit code to verify your email address.

Other noticeable improvements

  • Password changes sign out other devices: Changing your password now signs you out on every other device and revokes your access tokens. Resetting a forgotten password signs you out everywhere. If you use the browser extension or integrations like Floccus with an access token, you’ll need to sign them back in afterwards.
  • Password rate limiting: After 15 wrong passwords in a row, an account accepts only one attempt every 25 seconds. This makes guessing a password much slower without locking you out of your own account.
  • More security fixes: This release also fixes a number of moderate-severity security issues, thanks to everyone who reported them responsibly. We recommend updating to 2.17.
  • Search from the address bar: With the browser extension installed, type lw, press space, then type what you’re looking for and press Enter to search your Linkwarden links straight from the address bar. This works in Chrome, Firefox, and other Chromium-based browsers.
  • Import fixes: Imported links now keep the order of their original dates no matter in what order they were imported, Wallabag dates are read correctly, and larger imports are more reliable.
  • Custom AI tagging prompts: Self-hosted instances can now replace the prompt sent to the model for each AI tagging method with the AI_GENERATE_TAGS_PROMPT, AI_PREDEFINED_TAGS_PROMPT, and AI_EXISTING_TAGS_PROMPT environment variables. Check it out in the docs!
  • And more: As always, there’s a long tail of smaller fixes and improvements across the web app, the mobile app, and the browser extension.

Full Changelog: github.com/linkwarden/…/v2.16.3...v2.17.0

Thanks!

Thanks to everyone using Linkwarden, reporting bugs, suggesting improvements, contributing to the project, responsibly disclosing security issues, and supporting its development. A special thanks to all the security researchers who reported the issues fixed in this release. 💙

If you’d like to try Linkwarden without dealing with server setup and maintenance, our Cloud offering is the easiest way to get started.

Hope you enjoy the latest updates!

13

[AIP] JustDNS: a self-hosted DNS filter that shows which companies your devices phone home to

preview

I’m the developer of JustDNS, a self-hosted filtering DNS resolver for your whole network. I built it because I wanted more than a block count. I wanted to see which companies my devices actually talk to.

What it does

  • Blocks ads, trackers and malware, like Pi-hole or AdGuard Home.
  • Privacy dashboard that attributes DNS traffic to the companies behind it, with a per-device breakdown and a world map of where answers resolve. You can block a company for a single device or the whole network.
  • Encrypted upstreams (DNS-over-TLS) by default, plus DNSSEC validation.
  • Per-device and per-group policies, user accounts with roles and TOTP.
  • Optional multi-node high availability.

Running it

  • Docker / docker compose, or a one-click Unraid Community Apps template.
  • AGPL-3.0, no cloud account, nothing phones home.

Repo: github.com/bonderaustriaAT/JustDNS

It’s still young, so I’d genuinely like feedback from people running Pi-hole or AdGuard today: what would make you switch, and what’s missing? Happy to answer questions.

EDIT:

AI Disclosure:

  • Design - No AI
  • Implementation - Hints
  • Testing - Assisted
  • Documentation - Pair
  • Review - Assisted
  • Deployment - Assisted

I’m the developer of JustDNS, a self-hosted filtering DNS resolver for your whole network. I built it because I wanted more than a block count. I wanted to see which companies my devices actually talk to.

What it does

  • Blocks ads, trackers and malware, like Pi-hole or AdGuard Home.
  • Privacy dashboard that attributes DNS traffic to the companies behind it, with a per-device breakdown and a world map of where answers resolve. You can block a company for a single device or the whole network.
  • Encrypted upstreams (DNS-over-TLS) by default, plus DNSSEC validation.
  • Per-device and per-group policies, user accounts with roles and TOTP.
  • Optional multi-node high availability.

Running it

  • Docker / docker compose, or a one-click Unraid Community Apps template.
  • AGPL-3.0, no cloud account, nothing phones home.

Repo: github.com/bonderaustriaAT/JustDNS

It’s still young, so I’d genuinely like feedback from people running Pi-hole or AdGuard today: what would make you switch, and what’s missing? Happy to answer questions.

EDIT:

AI Disclosure:

  • Design - No AI
  • Implementation - Hints
  • Testing - Assisted
  • Documentation - Pair
  • Review - Assisted
  • Deployment - Assisted
51

Would there be any benefit to switching from Fedora to NetBSD?

preview

The anti-AI stance is nice but I am not sure it can be proven beyond virtue signaling… I would support such a stance though. Not a fan of what Linus has been doing recently.

I should add that all of my stuff is containerized.

The anti-AI stance is nice but I am not sure it can be proven beyond virtue signaling… I would support such a stance though. Not a fan of what Linus has been doing recently.

I should add that all of my stuff is containerized.

57

OT: The MS issue and what caused it

preview

folks,i know this is OT but i decided to post here as i’m sure there are a lot of people here that work in IT and know what thay are talking about. The recent MS failure is what i would like your opinion on.

from what I’ve seen, MS declared that a bunch of servers went offline and the load had to be spread on remaining servers. They fail to identify what caused the first bunch of servers encountering issues and they claim it was mot related to a hacker attack (why would they, it would lead to massive panic and distrust). So, then what caused the issue in the first place? Could it have been a piloted denail of service attack?

I’m sure the truth will emerge in coming days but was interested in the more tech savy people’s opinione. In the meantime i rejoyce for not having to depend of third party infrastructure at home, thanks to my little homelab.

A further consideration is that this does once again prove that companies that put all their eggs in one basket, are at yhe mercy of big tech. i experienced this personally at works where comunication by Teams and Outlooks was pretty much halted for hours.

folks,i know this is OT but i decided to post here as i’m sure there are a lot of people here that work in IT and know what thay are talking about. The recent MS failure is what i would like your opinion on.

from what I’ve seen, MS declared that a bunch of servers went offline and the load had to be spread on remaining servers. They fail to identify what caused the first bunch of servers encountering issues and they claim it was mot related to a hacker attack (why would they, it would lead to massive panic and distrust). So, then what caused the issue in the first place? Could it have been a piloted denail of service attack?

I’m sure the truth will emerge in coming days but was interested in the more tech savy people’s opinione. In the meantime i rejoyce for not having to depend of third party infrastructure at home, thanks to my little homelab.

A further consideration is that this does once again prove that companies that put all their eggs in one basket, are at yhe mercy of big tech. i experienced this personally at works where comunication by Teams and Outlooks was pretty much halted for hours.

64

Hosting matrix or something else for normal people

preview

Hey y’all,

So I keep having this intrusive though that I SO BADLY want to get my anti slop, anti corporate brainwash friends off of fb and start our own social area (with blow and hookers. Actually forget the blow).

My issues: most of them aren’t tech savvy and my setup would have to be solid with little issues. I never post on fb but I basically would Make 1 post inviting everyone to it.

I have a couple synology nas setups. Neither are open to the internet. I have some spare computers as well that could run the server fine.

I know I could potentially just make a server from one of the public instances of matrix but I don’t trust that and it’d be a nightmare if that one went down or something and we had to move again.

Realistically I’d probably get like 10 people to join me. Just a place for local community to hang out and share events etc.

I keep getting stuck on how exactly to go about it. Like I think I’d need tailscale and docker (still dont get what docker really is). I have used tailscale briefly on mobile and it seems to work. But idk. I would also be fine paying a modest sum a year for some pro to host it if that is smarter…

Hey y’all,

So I keep having this intrusive though that I SO BADLY want to get my anti slop, anti corporate brainwash friends off of fb and start our own social area (with blow and hookers. Actually forget the blow).

My issues: most of them aren’t tech savvy and my setup would have to be solid with little issues. I never post on fb but I basically would Make 1 post inviting everyone to it.

I have a couple synology nas setups. Neither are open to the internet. I have some spare computers as well that could run the server fine.

I know I could potentially just make a server from one of the public instances of matrix but I don’t trust that and it’d be a nightmare if that one went down or something and we had to move again.

Realistically I’d probably get like 10 people to join me. Just a place for local community to hang out and share events etc.

I keep getting stuck on how exactly to go about it. Like I think I’d need tailscale and docker (still dont get what docker really is). I have used tailscale briefly on mobile and it seems to work. But idk. I would also be fine paying a modest sum a year for some pro to host it if that is smarter…

58

Custom domains and Tailscale

preview

Hey everyone. This is probably a super noob question, but I’m very much just an amateur when it comes to self-hosting.

I host several services that I access locally through 192.whatever:####, and when I occasionally need remote access, I use Tailscale and access through 100.whatever: ####. The duplicate bookmarks is mildly annoying though.

Can I just buy a personal domain, and have all my services be coolname.com:#### for both local and Tailscale access? Is that as simple a process as I want it to be?

Edit: I appreciate all the comments and I’ll probably just use Tailacale’s MagicDNS for simplicity, but one or my (unwritten, my bad) goals was to have one URL that works locally and remotely, regardless of Tailscale. I don’t leave Tailscale constantly connected because it overheats my phone (which already has terrible battery life).

Hey everyone. This is probably a super noob question, but I’m very much just an amateur when it comes to self-hosting.

I host several services that I access locally through 192.whatever:####, and when I occasionally need remote access, I use Tailscale and access through 100.whatever: ####. The duplicate bookmarks is mildly annoying though.

Can I just buy a personal domain, and have all my services be coolname.com:#### for both local and Tailscale access? Is that as simple a process as I want it to be?

Edit: I appreciate all the comments and I’ll probably just use Tailacale’s MagicDNS for simplicity, but one or my (unwritten, my bad) goals was to have one URL that works locally and remotely, regardless of Tailscale. I don’t leave Tailscale constantly connected because it overheats my phone (which already has terrible battery life).

57

Plasma Bigscreen - November 2026 App Releases

Plasma Bigscreen November 2026 App Releases plasma-bigscreen.org
preview

cross-posted from: programming.dev/post/59367100

I’m pretty excited about this project as a whole and figured I’d share their blog post from the other day.

This isn’t necessarily a “self hosted” thing but it compliments self hosting and data privacy so I figured it fits. If it doesn’t please remove.

cross-posted from: programming.dev/post/59367100

I’m pretty excited about this project as a whole and figured I’d share their blog post from the other day.

This isn’t necessarily a “self hosted” thing but it compliments self hosting and data privacy so I figured it fits. If it doesn’t please remove.

91

Dawarich 1.22.0 — Alternative to Google Timeline, OwnTracks and Life360 [AIP]

preview

Hello there, my dearest people of Selfhosted!

I’m Evgenii, the developer and maintainer of Dawarich, a free, open-source, self-hostable alternative to Google Timeline, and I brought you a fresh portion of updates we made in October 2026.


AI Disclosure (as per lemmy.world/post/49320548):

Implementation - Generated

Testing - Assisted

Design - Assisted


As always, our links:

Github: https://github.com/Freika/dawarich

Website: https://dawarich.app/

iOS app: https://apps.apple.com/us/app/dawarich/id6739544999

Android app: https://play.google.com/store/apps/details?id=app.dawarich.Dawarich


Less bugs

So, what we brought to Dawarich in October? First of all, A TON of bugfixes. I released fixes for and closed roughly ~150 bug reports, plus the stuff I discovered myself. For months, number of open issues on GitHub was somewhere between 100 and 150, and I was struggling to keep up with the new reports. But in October I was finally able to build a proper system around this and now reproducing, finding the root and fixing a bug is a lot faster process. As of today, we have ~40 open issues on Github, most of which are either feature requests (I usually convert them to Discussions on Github, under “Ideas” section) or bug reports related to our mobile apps. I hope to reduce this number further before the year ends. For the mobile apps development pace is naturally a bit slower, due to how releasing process works in AppStore and Google Play, but we’re addressing issues reported for them as well.

Made it faster and slimmer

Now, historically, due to tech stack of my choice, Dawarich consisted of 4 docker containers: the app itself, sidekiq for background jobs, redis for cache and sidekiq jobs queue, and postgresql for the database. I know it bothered some of our users, so I found the way to reduce number of docker containers to 3 by putting Sidekiq into the app container. It was introduced in 1.17.0 and works well, here’s your updating guide: dawarich.app/docs/self-hosting/updating/#one-cont…

Also, in the same release, thanks to one container less and some other optimizations, idling memory consumption went down, from ~480mb to ~230mb. Feels good, innit? And since we’re here talking performance, Trips pages are now a LOT faster, same as Points index page. Data imports and reverse geocoding speed were also improved, with more speed ups are being in progress right now.

No more Places and Areas mess. Also, Geofencing!

First, there were Areas, that you could draw on the map and detect visits within, then I added Places, that were created either from detected visits or manually by user. It was kinda inconvenient to have both, so I finally found the time to convert Areas to Places, add a radius to Places so the would act as Areas, and introduced geofencing as a cherry in top. Phew! So now you can create a place, set a radius to detect visits (upto 50km) and configure webhooks on enter-leave events. Enter the designated area -> Enter event triggered -> configured webhook is sent to your HomeAssistant, NodeRed, N8n, or whatever other service you prefer to use. Add some imagination and maybe you could configure push notifications. Complete freedom, yay!

Privacy zones

As much as I would love people to create videos about Dawarich (which they do, and they’re awesome!), it’s obvious nobody wants to doxx themselves by exposing their home location on a video. So a while ago I introduced Privacy zones for tags, and now updated them to work across all the maps in Dawarich, be it the Map page, Trips, Posters, Replays, publicly shared pages, you name it. Basically it works like this:

  1. Create a place you want to hide your location data around
  2. Create a tag with a privacy zone enabled, configure privacy radius
  3. Assign the tag to the place from step 1
  4. All done!

What’s important, the place tagged with a privacy zone’d tag is not in the middle of the radius, so it won’t be possible to establish exact location by simply putting a finger in the center of hidden radius. Here’s a short demo of how the feature works: youtu.be/CIl09RAVSBI

Some other notable changes:

  • Some features can be now disabled in the settings, for now it’s Family and Achievements
  • New Achievements were added: City explorer, National parks, Returning to a place after a while, and some more. This feature has a huge potential so the cards sets will be expanded further. If you don’t like, see the point one of this list :)
  • Stats were moved to Insights page for unification purposes
  • You can now import your checkins from Foursquare Swarm

Lots of other, smaller, things were introduced and/or changes, so as always, I’d recommend to keep your eyes on changelogs and create backups before updating :)

The mobile apps

We worked on them, too :) As always, some work was done to improve battery consumption and performance, on Android specifically, we added Photos and Hexagons layers to the map, some fixes for widgets, and a supporter badge in the web for those who purchased Self-Hoster Pro plan in the mobile app. Because every way of supporting matters and we would love to give back to the community.

Almost forgot: Dawarich is now available on your Apple Watch and WearOS :) Some screenshots below:


Stickers

We’ve sent first batch of stickers to our users from Germany, and I expect to send ~50 more envelopes to the rest of the world next week. If you’d like to receive some, leave your address in this form: tally.so/r/1A1DBg

Turns out, manually signing all the envelopes and postcards (I’m adding one to each envelope until they last) is a time-consuming job and a lot less fun than tapping buttons on a keyboard, but I managed to do it with the help of my lovely wife :D Gotta figure something out to simplify the process though, especially if there will be more people requesting stickers :)

Small reminder, the idea behind stickers is that you stick them in the place of your travels and (optionally) send me a picture of the place with the sticker with coordinates, so later I could put them together to a map, marking travelings of our users :)


Transportation modes experiment

In Dawarich, we have transportation mode detection for tracks. Based on speed, acceleration and some other parameters, an estimation is being done on backend, whether part of a track walked by foot, cycled, driven or flown. It’s pretty unreliable in its current form, so I have this idea, where you, the community, can help. I drafted a tool, where you can load your GPX files and mark track segments up, by providing information on what transportation mode the segment belongs to.

It all works in your browser and no coordinates nor timestamps being sent anywhere. When you finish, you can click “Review & Send” and only then features of the marked up track segments will be uploaded. You’ll be able to see what exactly is being sent before it’s sent to make sure no private data leaves your device.

Later on, when there is enough data for each transportation mode, I’ll try to compose a tool that will accept a gpx track and return most probable transportation mode for it. If all goes well and the tool works as intended, I will open source it under permissive license. It will also be distributed as part of Dawarich, which will benefit from more reliable transportation mode detection. Once it’s reliable enough, this opens some new possibilities for features long asked by the community.

Here’s the link, if you want to help: transportation-modes.dawarich.app

Thanks!


It’s fascinating, that after two years of Dawarich being in development I still have TONS of ideas, both for the web app and the mobile app. Kinda envy myself a bit, haha. Lots of stuff to port from our web to mobile, new features, improvements.

Thank you all for that. There would be no Dawarich without you, people using it, loving it and sharing it with your friends.

As always, more awesome stuff to come, see you in the next one!

P.S.

Links to save you a scroll:

GitHub

Website

iOS

Android

Support development: GitHub Sponsors / Patreon

Hello there, my dearest people of Selfhosted!

I’m Evgenii, the developer and maintainer of Dawarich, a free, open-source, self-hostable alternative to Google Timeline, and I brought you a fresh portion of updates we made in October 2026.


AI Disclosure (as per lemmy.world/post/49320548):

Implementation - Generated

Testing - Assisted

Design - Assisted


As always, our links:

Github: https://github.com/Freika/dawarich

Website: https://dawarich.app/

iOS app: https://apps.apple.com/us/app/dawarich/id6739544999

Android app: https://play.google.com/store/apps/details?id=app.dawarich.Dawarich


Less bugs

So, what we brought to Dawarich in October? First of all, A TON of bugfixes. I released fixes for and closed roughly ~150 bug reports, plus the stuff I discovered myself. For months, number of open issues on GitHub was somewhere between 100 and 150, and I was struggling to keep up with the new reports. But in October I was finally able to build a proper system around this and now reproducing, finding the root and fixing a bug is a lot faster process. As of today, we have ~40 open issues on Github, most of which are either feature requests (I usually convert them to Discussions on Github, under “Ideas” section) or bug reports related to our mobile apps. I hope to reduce this number further before the year ends. For the mobile apps development pace is naturally a bit slower, due to how releasing process works in AppStore and Google Play, but we’re addressing issues reported for them as well.

Made it faster and slimmer

Now, historically, due to tech stack of my choice, Dawarich consisted of 4 docker containers: the app itself, sidekiq for background jobs, redis for cache and sidekiq jobs queue, and postgresql for the database. I know it bothered some of our users, so I found the way to reduce number of docker containers to 3 by putting Sidekiq into the app container. It was introduced in 1.17.0 and works well, here’s your updating guide: dawarich.app/docs/self-hosting/updating/#one-cont…

Also, in the same release, thanks to one container less and some other optimizations, idling memory consumption went down, from ~480mb to ~230mb. Feels good, innit? And since we’re here talking performance, Trips pages are now a LOT faster, same as Points index page. Data imports and reverse geocoding speed were also improved, with more speed ups are being in progress right now.

No more Places and Areas mess. Also, Geofencing!

First, there were Areas, that you could draw on the map and detect visits within, then I added Places, that were created either from detected visits or manually by user. It was kinda inconvenient to have both, so I finally found the time to convert Areas to Places, add a radius to Places so the would act as Areas, and introduced geofencing as a cherry in top. Phew! So now you can create a place, set a radius to detect visits (upto 50km) and configure webhooks on enter-leave events. Enter the designated area -> Enter event triggered -> configured webhook is sent to your HomeAssistant, NodeRed, N8n, or whatever other service you prefer to use. Add some imagination and maybe you could configure push notifications. Complete freedom, yay!

Privacy zones

As much as I would love people to create videos about Dawarich (which they do, and they’re awesome!), it’s obvious nobody wants to doxx themselves by exposing their home location on a video. So a while ago I introduced Privacy zones for tags, and now updated them to work across all the maps in Dawarich, be it the Map page, Trips, Posters, Replays, publicly shared pages, you name it. Basically it works like this:

  1. Create a place you want to hide your location data around
  2. Create a tag with a privacy zone enabled, configure privacy radius
  3. Assign the tag to the place from step 1
  4. All done!

What’s important, the place tagged with a privacy zone’d tag is not in the middle of the radius, so it won’t be possible to establish exact location by simply putting a finger in the center of hidden radius. Here’s a short demo of how the feature works: youtu.be/CIl09RAVSBI

Some other notable changes:

  • Some features can be now disabled in the settings, for now it’s Family and Achievements
  • New Achievements were added: City explorer, National parks, Returning to a place after a while, and some more. This feature has a huge potential so the cards sets will be expanded further. If you don’t like, see the point one of this list :)
  • Stats were moved to Insights page for unification purposes
  • You can now import your checkins from Foursquare Swarm

Lots of other, smaller, things were introduced and/or changes, so as always, I’d recommend to keep your eyes on changelogs and create backups before updating :)

The mobile apps

We worked on them, too :) As always, some work was done to improve battery consumption and performance, on Android specifically, we added Photos and Hexagons layers to the map, some fixes for widgets, and a supporter badge in the web for those who purchased Self-Hoster Pro plan in the mobile app. Because every way of supporting matters and we would love to give back to the community.

Almost forgot: Dawarich is now available on your Apple Watch and WearOS :) Some screenshots below:


Stickers

We’ve sent first batch of stickers to our users from Germany, and I expect to send ~50 more envelopes to the rest of the world next week. If you’d like to receive some, leave your address in this form: tally.so/r/1A1DBg

Turns out, manually signing all the envelopes and postcards (I’m adding one to each envelope until they last) is a time-consuming job and a lot less fun than tapping buttons on a keyboard, but I managed to do it with the help of my lovely wife :D Gotta figure something out to simplify the process though, especially if there will be more people requesting stickers :)

Small reminder, the idea behind stickers is that you stick them in the place of your travels and (optionally) send me a picture of the place with the sticker with coordinates, so later I could put them together to a map, marking travelings of our users :)


Transportation modes experiment

In Dawarich, we have transportation mode detection for tracks. Based on speed, acceleration and some other parameters, an estimation is being done on backend, whether part of a track walked by foot, cycled, driven or flown. It’s pretty unreliable in its current form, so I have this idea, where you, the community, can help. I drafted a tool, where you can load your GPX files and mark track segments up, by providing information on what transportation mode the segment belongs to.

It all works in your browser and no coordinates nor timestamps being sent anywhere. When you finish, you can click “Review & Send” and only then features of the marked up track segments will be uploaded. You’ll be able to see what exactly is being sent before it’s sent to make sure no private data leaves your device.

Later on, when there is enough data for each transportation mode, I’ll try to compose a tool that will accept a gpx track and return most probable transportation mode for it. If all goes well and the tool works as intended, I will open source it under permissive license. It will also be distributed as part of Dawarich, which will benefit from more reliable transportation mode detection. Once it’s reliable enough, this opens some new possibilities for features long asked by the community.

Here’s the link, if you want to help: transportation-modes.dawarich.app

Thanks!


It’s fascinating, that after two years of Dawarich being in development I still have TONS of ideas, both for the web app and the mobile app. Kinda envy myself a bit, haha. Lots of stuff to port from our web to mobile, new features, improvements.

Thank you all for that. There would be no Dawarich without you, people using it, loving it and sharing it with your friends.

As always, more awesome stuff to come, see you in the next one!

P.S.

Links to save you a scroll:

GitHub

Website

iOS

Android

Support development: GitHub Sponsors / Patreon

51

recommendations for selfhosted trips?

preview

I stumbled upon trek, trip and AdventureLog. You can track your travels. They all look good but I’m not sure how to evaluate which one is good to use. Are they all save? Which do you use?

I stumbled upon trek, trip and AdventureLog. You can track your travels. They all look good but I’m not sure how to evaluate which one is good to use. Are they all save? Which do you use?

24

[AIP] Modern offline-first self-hosted open-source TickTick/Todoist alternative. Will Be Done v0.15 released, now with calendar, mindmap and openapi support

preview

New version of Will Be Done is released! Will Be Done is an offline-first, self-hosted task manager with a visual weekly timeline.

The main idea is simple: collect tasks, put them on a week timeline. I find that the week timeline helps me stay more organised and fits naturally into my workflow. It works offline-first with server sync, so tasks are stored locally in the browser/desktop app (like Linear), and it also gives an instant UI.

What changed since my last post (v0.10.0):

  • Added mindmap support
  • Added calendar support with readonly ical/caldav integration
  • Added markdown WYSIWYG editor, with collaborative edit support (yjs)
  • Added OpenAPI support
  • Added task recovery: deleted tasks go to Trash, and there’s an undo popup on accidental task/project/section delete
  • Added undo/redo
  • Added notes
  • Added multi-select

Links:

Demo: demo.will-be-done.app

GitHub: github.com/will-be-done/will-be-done

Download desktop app: github.com/will-be-done/will-be-done/releases

More info: will-be-done.app

Self-host with Docker:

docker run -d \
  -p 3000:3000 \
  -v will_be_done_storage:/var/lib/will-be-done \
  --restart unless-stopped \
  ghcr.io/will-be-done/will-be-done:latest

Then open localhost:3000.

Would love to hear feedback!

AI disclosure

  • Design - architecture, system design: no AI involved. I’ve been working on local-first apps for ~5y and have been a software engineer for ~10y. I even built HyperDB, a database for local-first apps, because existing solutions such as Dexie and RxDB didn’t meet my needs.
  • Implementation - Pair. From the start of the project it was Hint, but now it’s Pair.
  • Testing - Generated.
  • Documentation - Pair.
  • Review - Pair. I have coderabbit AI + greptile, but also do manual review.
  • Deployment - Pair.

New version of Will Be Done is released! Will Be Done is an offline-first, self-hosted task manager with a visual weekly timeline.

The main idea is simple: collect tasks, put them on a week timeline. I find that the week timeline helps me stay more organised and fits naturally into my workflow. It works offline-first with server sync, so tasks are stored locally in the browser/desktop app (like Linear), and it also gives an instant UI.

What changed since my last post (v0.10.0):

  • Added mindmap support
  • Added calendar support with readonly ical/caldav integration
  • Added markdown WYSIWYG editor, with collaborative edit support (yjs)
  • Added OpenAPI support
  • Added task recovery: deleted tasks go to Trash, and there’s an undo popup on accidental task/project/section delete
  • Added undo/redo
  • Added notes
  • Added multi-select

Links:

Demo: demo.will-be-done.app

GitHub: github.com/will-be-done/will-be-done

Download desktop app: github.com/will-be-done/will-be-done/releases

More info: will-be-done.app

Self-host with Docker:

docker run -d \
  -p 3000:3000 \
  -v will_be_done_storage:/var/lib/will-be-done \
  --restart unless-stopped \
  ghcr.io/will-be-done/will-be-done:latest

Then open localhost:3000.

Would love to hear feedback!

AI disclosure

  • Design - architecture, system design: no AI involved. I’ve been working on local-first apps for ~5y and have been a software engineer for ~10y. I even built HyperDB, a database for local-first apps, because existing solutions such as Dexie and RxDB didn’t meet my needs.
  • Implementation - Pair. From the start of the project it was Hint, but now it’s Pair.
  • Testing - Generated.
  • Documentation - Pair.
  • Review - Pair. I have coderabbit AI + greptile, but also do manual review.
  • Deployment - Pair.
14

Walkthrough for Self-Hosted Headscale on "Free-Tier" Cloud VM (GCI) [AIP]

preview

AI Disclosure:

  • Implementation - Hint. Syntax was reviewed and polished by AI.
  • Testing - Assisted. AI was used to troubleshoot whenever I got stuck
  • Documentation - Generated

I spent the last three months slowly tinkering with Headscale and trying to get it to run on one of Google’s “free-tier” cloud instances, while also learning about GCI’s strange setup. During that time I used Claude Sonnet to keep track of my progress and help me troubleshoot whenever I got stuck. I finally got it going and before I closed the project, I asked Claude to document my work along with all pertinent information and create and admin cheatsheet, just in case I forget. I liked the output, so I asked the LLM to sanitize my data and recreate my project as a step-by-step walktrhough in a single HTML page.

PROVIDED AS-IS!!! Do not copy and paste code blindly. Use this as a walkthough/guide and NOT as a recipe book. You WILL need to correct code.

EDIT: It looks like for this document, Claude also took it upon itself to further clean my configs, scripts, etc., and add a lot of comments to make it all easier to understand. I DO NOT work this cleanly. It looks correct though.

AI Disclosure:

  • Implementation - Hint. Syntax was reviewed and polished by AI.
  • Testing - Assisted. AI was used to troubleshoot whenever I got stuck
  • Documentation - Generated

I spent the last three months slowly tinkering with Headscale and trying to get it to run on one of Google’s “free-tier” cloud instances, while also learning about GCI’s strange setup. During that time I used Claude Sonnet to keep track of my progress and help me troubleshoot whenever I got stuck. I finally got it going and before I closed the project, I asked Claude to document my work along with all pertinent information and create and admin cheatsheet, just in case I forget. I liked the output, so I asked the LLM to sanitize my data and recreate my project as a step-by-step walktrhough in a single HTML page.

PROVIDED AS-IS!!! Do not copy and paste code blindly. Use this as a walkthough/guide and NOT as a recipe book. You WILL need to correct code.

EDIT: It looks like for this document, Claude also took it upon itself to further clean my configs, scripts, etc., and add a lot of comments to make it all easier to understand. I DO NOT work this cleanly. It looks correct though.

28

Opinions on Opnsense dec850 as router

preview

I asked this question about a week ago on homelab and didn’t get very much input, so I hope I can get more help here.

I have been looking at replacing my L3 switch at the gateway of my network & the OPNsense DEC850 seems to have all the features I want, mainly, vlans, 10 GB wan, multiple 2.5 GB lan, & open firmware. Does anyone have experience with this router/ are there better routers out there that do similar setups? I have experience with Cisco hardware and am willing to learn new syntax so I am not too worried about the CLI, but I heard that opnsense’s docs are a bit thin.

I asked this question about a week ago on homelab and didn’t get very much input, so I hope I can get more help here.

I have been looking at replacing my L3 switch at the gateway of my network & the OPNsense DEC850 seems to have all the features I want, mainly, vlans, 10 GB wan, multiple 2.5 GB lan, & open firmware. Does anyone have experience with this router/ are there better routers out there that do similar setups? I have experience with Cisco hardware and am willing to learn new syntax so I am not too worried about the CLI, but I heard that opnsense’s docs are a bit thin.

29

Anyone know of a FOSS type kids messenger?

preview

cross-posted from: lemmy.today/post/63107763

I’m looking for something like Snikket or Prosody, but kids-oriented. I DON’T want my <10 daughter using Meta Messenger Kids! I’ll tell my friends to setup for their kids, too. I’d have no access to anything, so it’s secure (mom and dad not snooping per se), but the downside is minimal parental controls. Though, no one to really add either.

I’ll host or pay for it, IDC. It doesn’t seem like there is much out there either.

JusTalk seemed nice when I found out but apparently China owned and so no more secure. I/we need better options!

cross-posted from: lemmy.today/post/63107763

I’m looking for something like Snikket or Prosody, but kids-oriented. I DON’T want my <10 daughter using Meta Messenger Kids! I’ll tell my friends to setup for their kids, too. I’d have no access to anything, so it’s secure (mom and dad not snooping per se), but the downside is minimal parental controls. Though, no one to really add either.

I’ll host or pay for it, IDC. It doesn’t seem like there is much out there either.

JusTalk seemed nice when I found out but apparently China owned and so no more secure. I/we need better options!

-26

[AIP] VpsPilot: managing my Linux VPS from my phone over SSH (feedback welcome)

preview

I used to be chained to my laptop all day just to manage my self-hosted servers or fix minor issues, and I hated waiting until I got back home to handle things. I wanted the freedom to manage my infrastructure from anywhere straight from my phone without trusting third-party cloud relays.

​I built VPSPilot as a native Kotlin Android SSH client for my own daily workflow. A few things I focused on:

  • Zero Proxies / Direct Connection: No middleman servers or cloud accounts—your phone talks directly to your own hosts over standard SSH.

  • ​Hardware Key Isolation: SSH private keys are locked inside Android’s hardware-backed Keystore/TEE chip so they aren’t exposed or handed over to anyone else.

  • ​Task Automation & Secret Handling: Automates my routine sysadmin tasks and custom workflows so I don’t have to keep typing repetitive commands on a phone keyboard, while keeping secrets from being typed raw into the console.

​AI Disclosure: Built by me as a solo project for my own daily server management workflow. I drove the core architecture, handled all testing, and managed the device/Keystore implementation, while using an AI assistant for syntax help, debugging routine exceptions, and cleaning up documentation.

I used to be chained to my laptop all day just to manage my self-hosted servers or fix minor issues, and I hated waiting until I got back home to handle things. I wanted the freedom to manage my infrastructure from anywhere straight from my phone without trusting third-party cloud relays.

​I built VPSPilot as a native Kotlin Android SSH client for my own daily workflow. A few things I focused on:

  • Zero Proxies / Direct Connection: No middleman servers or cloud accounts—your phone talks directly to your own hosts over standard SSH.

  • ​Hardware Key Isolation: SSH private keys are locked inside Android’s hardware-backed Keystore/TEE chip so they aren’t exposed or handed over to anyone else.

  • ​Task Automation & Secret Handling: Automates my routine sysadmin tasks and custom workflows so I don’t have to keep typing repetitive commands on a phone keyboard, while keeping secrets from being typed raw into the console.

​AI Disclosure: Built by me as a solo project for my own daily server management workflow. I drove the core architecture, handled all testing, and managed the device/Keystore implementation, while using an AI assistant for syntax help, debugging routine exceptions, and cleaning up documentation.

-16

what software fits this?

preview

well is there something like this or similar but self hostable:

1: it is not the heaviest thing on the world

2: it works similar to a forum, Mailing list, or BBS

3: it uses text like this for example:

user: whatever

<other info about the message/post>

<the message/post>

4: it is easy or medium to get running

5: Can use Tor

well is there something like this or similar but self hostable:

1: it is not the heaviest thing on the world

2: it works similar to a forum, Mailing list, or BBS

3: it uses text like this for example:

user: whatever

<other info about the message/post>

<the message/post>

4: it is easy or medium to get running

5: Can use Tor

88

Nest Thermostat in 2026

preview

Hey all, I spent the weekend updating my home’s thermostat to a smart model. I took a somewhat unusual path and went with a discontinued 2nd Gen Nest thermostat. Read about my journey - Nest Thermostat in 2026 - Artificially-Awesome

Hey all, I spent the weekend updating my home’s thermostat to a smart model. I took a somewhat unusual path and went with a discontinued 2nd Gen Nest thermostat. Read about my journey - Nest Thermostat in 2026 - Artificially-Awesome

13

Running OPNSense on existing Proxmox media server

preview

Lately my router seems to be struggling under all my devices and after some googling, it seems my Archer AX1800 isnt really meant for more than 20-40 devices and I’m currently sitting at 50 with heavy torrent traffic and a media server with 15-20 friends and family connected (typically not all at once of course).

I was looking at the Omada networking gear but then thought of trying OPNSense since I have pretty much everything I need on hand versus spending $400+ for the Omada stuff.

I’d like to run it on the media server since I have tons of compute/RAM available but my question is about the ethernet ports. My mobo has a dedicated 2.5Gb ethernet port built in and I have a second 2.5Gb card that I could toss in there as well, but my concern is that I may saturate the ports with all the additional traffic. My LAN is just 1Gb outside of these two PCs.

My other option is an unused Optiplex 3050 micro that I’ve installed a second ethernet port on but these would both be 1Gb ports.

Am I likely to run into saturation issues on the media server or should the 2.5Gb ports be more than enough to handle the load? Apart from the torrents and video streaming, the rest of the network is mostly typical devices like phones/tablets/consoles, 6 4K POE cameras connected to an NVR and frigate, and a bunch of IoT devices connected to Home Assistant.

I don’t necessarily mind using the Optiplex but I’d definitely prefer to keep everything in one place if I can. I realize that this means my network goes down if I restart the host but it has been a pretty rock solid setup and Proxmox means I can just restart individual containers/VMs rather than the host most of the time.

Edit: forgot to mention that I’m open to buying another quad port NIC for the server if recommended, but would definitely prefer to not spend money if possible. I was planning on using the current router in AP mode along with its ports for a switch and I have another 4 port 2.5Gb switch in the mix as well

Lately my router seems to be struggling under all my devices and after some googling, it seems my Archer AX1800 isnt really meant for more than 20-40 devices and I’m currently sitting at 50 with heavy torrent traffic and a media server with 15-20 friends and family connected (typically not all at once of course).

I was looking at the Omada networking gear but then thought of trying OPNSense since I have pretty much everything I need on hand versus spending $400+ for the Omada stuff.

I’d like to run it on the media server since I have tons of compute/RAM available but my question is about the ethernet ports. My mobo has a dedicated 2.5Gb ethernet port built in and I have a second 2.5Gb card that I could toss in there as well, but my concern is that I may saturate the ports with all the additional traffic. My LAN is just 1Gb outside of these two PCs.

My other option is an unused Optiplex 3050 micro that I’ve installed a second ethernet port on but these would both be 1Gb ports.

Am I likely to run into saturation issues on the media server or should the 2.5Gb ports be more than enough to handle the load? Apart from the torrents and video streaming, the rest of the network is mostly typical devices like phones/tablets/consoles, 6 4K POE cameras connected to an NVR and frigate, and a bunch of IoT devices connected to Home Assistant.

I don’t necessarily mind using the Optiplex but I’d definitely prefer to keep everything in one place if I can. I realize that this means my network goes down if I restart the host but it has been a pretty rock solid setup and Proxmox means I can just restart individual containers/VMs rather than the host most of the time.

Edit: forgot to mention that I’m open to buying another quad port NIC for the server if recommended, but would definitely prefer to not spend money if possible. I was planning on using the current router in AP mode along with its ports for a switch and I have another 4 port 2.5Gb switch in the mix as well

68

How do you isolate a printer in your homelab?

preview

Hi all, I’ve gotten a Brother machine (DCP series) that can do wifi printing/scanning over their proprietary app. However, I’d like to lock it down from my network, because having it on the same LAN as my other devices and the ability to phone out to the internet seem like room for mischievious activities.

For context, I have OpenWRT on my router, and my clients can access the Brother using their iPrint&Scan app and AirPrint on wifi, as well as the traditional USB port. But I’m not good in networking. In my research, I drafted out the following solutions:

  1. Create a firewall rule to block the printer itself from making outbound requests. Seems simple, but I’m not sure if this can persist after IP changes or not.
  2. Create a VLAN for “IoT devices” that cannot send outbound requests to my normal VLAN nor the internet. Inspiration from this video, I’d need to manage a new SSID but it may come in handy for more IoT devices later.
  3. Hook the Brother up to a Raspberry Pi via USB, and install CUPS + SANE on the Pi. Assuming the Pi cannot “phone home” on behalf of the printer, this makes it a local-only “print+scan service” on my normal network and doesn’t require an extra VLAN.

I’d like to ask: which solution above is best for “neutering” the Brother? Or are there any alternatives/details I might’ve missed? I’m not sure if blocking outbound requests this way is enough of a security hardening for an untrusted device, and if there are any usability issues I’ve overlooked so far.

Thanks for any advice, and please share any printer/scanner setup you have in your networks as well. So hopefully I can get more inspiration!

Hi all, I’ve gotten a Brother machine (DCP series) that can do wifi printing/scanning over their proprietary app. However, I’d like to lock it down from my network, because having it on the same LAN as my other devices and the ability to phone out to the internet seem like room for mischievious activities.

For context, I have OpenWRT on my router, and my clients can access the Brother using their iPrint&Scan app and AirPrint on wifi, as well as the traditional USB port. But I’m not good in networking. In my research, I drafted out the following solutions:

  1. Create a firewall rule to block the printer itself from making outbound requests. Seems simple, but I’m not sure if this can persist after IP changes or not.
  2. Create a VLAN for “IoT devices” that cannot send outbound requests to my normal VLAN nor the internet. Inspiration from this video, I’d need to manage a new SSID but it may come in handy for more IoT devices later.
  3. Hook the Brother up to a Raspberry Pi via USB, and install CUPS + SANE on the Pi. Assuming the Pi cannot “phone home” on behalf of the printer, this makes it a local-only “print+scan service” on my normal network and doesn’t require an extra VLAN.

I’d like to ask: which solution above is best for “neutering” the Brother? Or are there any alternatives/details I might’ve missed? I’m not sure if blocking outbound requests this way is enough of a security hardening for an untrusted device, and if there are any usability issues I’ve overlooked so far.

Thanks for any advice, and please share any printer/scanner setup you have in your networks as well. So hopefully I can get more inspiration!

9

Hardware advice request: smallest double 3.5" bay, double 2.5G port PC for routing and low-complexity hosting

preview

I have multiple remote locations where I currently use OpenWrt combo router/APs for purposes like connecting to network, running VPNs, extending LANs to these VPNs, adding Wi-Fi APs - you know, normal router stuff.

I recently came into possession of multiple 3.5" HDDs and was looking for ways to utilize them best. My servers run on NVMEs and I have plenty of storage already, so I was thinking that I’d like to replace the routers with something that can take the HDDs to have a more distributed backup infrastructure.

The requirements are:

  1. Be a normal PC with UEFI. I prefer ARM, but this is not realistic, so probably x64. I came to the conclusion that I hate OpenWrt and everything not normal GNU/systemd software.
  2. Have at least two Ethernet ports, preferably 2.5 gigabit - I intend to keep using the existing routers as Wi-Fi APs and those have 2.5G ports.
  3. Have a small physical footprint and be quiet, ideally something like the AirPort Extreme of the olden days - people are less likely to unplug something that looks more like a router than a server. The routers are extremely remote (think 3 days travel time), people who live nearby are elderly (more blinking lights must mean more expensive), Wi-Fi provided by my hardware is their only connection, no cellular or anything, they’d get completely cut off from the world, so calling them and saying they need to do some maintenance is not an option.
  4. Have two 3.5" bays - my normal servers reside on RAIDZ as root filesystem, here I’m thinking of mirroring the drives to have at least some hardware redundancy. Having more than two is bad due to the reason above.
  5. Be decently powerful - routing sounds like an easy task, but I need to keep a convoluted VPN setup (plus syncoid backups!) and that overwhelms 2 core celerons pretty quickly. Since I’m adding storage I also wanted to add some local mirrors for services as well, but that’s low priority.
  6. Be in the 200-300€ range. I need to buy at least 5 of these. Blowing through my entire 2027 hardware budget before the year even starts sounds a bit painful.

Web search gave me an AOOSTAR R7 small PC that looks like a perfect match (the ports, the bays, Ryzen 7 5825U and DDR4 RAM! for about 300€), but sadly I can’t find it in stock anywhere.

Small note about the Ethernet ports: one to the upstream network (an option to have more than 1 gigabit exists in some places), one to the AP, that is 2.5G. If there’s an option to have more ports, that would be mad, I’d replace even the hardware at my home.

I also kinda dislike the idea of having SFP ports, I can’t go pure fiber (the upstream networks use proprietary connectors that are a pain to source and setup, I just use the bridges provided by them; the AP has copper Ethernet) and had a bad experience with the SFP to copper adapters.

I’m sure someone in this community has already solved this problem, so hoping this discussion will be useful for someone else as well.

I have multiple remote locations where I currently use OpenWrt combo router/APs for purposes like connecting to network, running VPNs, extending LANs to these VPNs, adding Wi-Fi APs - you know, normal router stuff.

I recently came into possession of multiple 3.5" HDDs and was looking for ways to utilize them best. My servers run on NVMEs and I have plenty of storage already, so I was thinking that I’d like to replace the routers with something that can take the HDDs to have a more distributed backup infrastructure.

The requirements are:

  1. Be a normal PC with UEFI. I prefer ARM, but this is not realistic, so probably x64. I came to the conclusion that I hate OpenWrt and everything not normal GNU/systemd software.
  2. Have at least two Ethernet ports, preferably 2.5 gigabit - I intend to keep using the existing routers as Wi-Fi APs and those have 2.5G ports.
  3. Have a small physical footprint and be quiet, ideally something like the AirPort Extreme of the olden days - people are less likely to unplug something that looks more like a router than a server. The routers are extremely remote (think 3 days travel time), people who live nearby are elderly (more blinking lights must mean more expensive), Wi-Fi provided by my hardware is their only connection, no cellular or anything, they’d get completely cut off from the world, so calling them and saying they need to do some maintenance is not an option.
  4. Have two 3.5" bays - my normal servers reside on RAIDZ as root filesystem, here I’m thinking of mirroring the drives to have at least some hardware redundancy. Having more than two is bad due to the reason above.
  5. Be decently powerful - routing sounds like an easy task, but I need to keep a convoluted VPN setup (plus syncoid backups!) and that overwhelms 2 core celerons pretty quickly. Since I’m adding storage I also wanted to add some local mirrors for services as well, but that’s low priority.
  6. Be in the 200-300€ range. I need to buy at least 5 of these. Blowing through my entire 2027 hardware budget before the year even starts sounds a bit painful.

Web search gave me an AOOSTAR R7 small PC that looks like a perfect match (the ports, the bays, Ryzen 7 5825U and DDR4 RAM! for about 300€), but sadly I can’t find it in stock anywhere.

Small note about the Ethernet ports: one to the upstream network (an option to have more than 1 gigabit exists in some places), one to the AP, that is 2.5G. If there’s an option to have more ports, that would be mad, I’d replace even the hardware at my home.

I also kinda dislike the idea of having SFP ports, I can’t go pure fiber (the upstream networks use proprietary connectors that are a pain to source and setup, I just use the bridges provided by them; the AP has copper Ethernet) and had a bad experience with the SFP to copper adapters.

I’m sure someone in this community has already solved this problem, so hoping this discussion will be useful for someone else as well.

6

Title: Ethical + privacy-first outdoor camera setup (garden & garage) – looking for advice

preview

Hi all,

I’m planning to set up outdoor security cameras (garden and garage) and want to do it fully local, with no cloud.

My constraints:

  • 100% local storage, no vendor cloud or apps
  • PoE + ONVIF/RTSP, IP67, good night vision

Questions:

  1. Any better open or camera brands that work fully offline?
  2. Any firmware or hardening tips I might be missing?

Thanks!

Hi all,

I’m planning to set up outdoor security cameras (garden and garage) and want to do it fully local, with no cloud.

My constraints:

  • 100% local storage, no vendor cloud or apps
  • PoE + ONVIF/RTSP, IP67, good night vision

Questions:

  1. Any better open or camera brands that work fully offline?
  2. Any firmware or hardening tips I might be missing?

Thanks!

4

Question about using gluetun for other containers

preview

I use gluetun, my arr stack and bittorrent client in a single docker-compose. I use the syntax

    depends_on:
      gluetun:
        condition: service_healthy

in the stack to make sure that the bittorrent client doesn’t try to connect too early. All that works great.

I also use that same VPN connection for other containers too (not in the same docker-compose stack). I do that by simply using network_mode: “container:gluetun” in the second yaml file. But I’d like to use the same depends_on syntax. But it errors out because gluetun is undefined in the second stack.

So my question is, how do I make sure the containers in docker compose stack 2 start after docker compose stack 1 (the one with gluetun) is healthy?

I use gluetun, my arr stack and bittorrent client in a single docker-compose. I use the syntax

    depends_on:
      gluetun:
        condition: service_healthy

in the stack to make sure that the bittorrent client doesn’t try to connect too early. All that works great.

I also use that same VPN connection for other containers too (not in the same docker-compose stack). I do that by simply using network_mode: “container:gluetun” in the second yaml file. But I’d like to use the same depends_on syntax. But it errors out because gluetun is undefined in the second stack.

So my question is, how do I make sure the containers in docker compose stack 2 start after docker compose stack 1 (the one with gluetun) is healthy?

260

Check if you need to update all your stuff - again.

preview

are you affected?

  • is your sshd running on musl? (alpine, openwrt, buildroot, yocto)
  • is it not using pam? alpine’s openssh-server doesn’t by default, or maybe you set UsePAM no
  • are password logins still on? they are by default
  • is there an account with just * as its password? key-only users, ldap users, root on alpine
  • and some other account with a real password?
  • then that * account takes any password between 257 and 1024 characters

on alpine’s official aws and azure images that’s the default alpine user, and it has passwordless doas. so it’s root

on debian, ubuntu, fedora or anything else with glibc? going through pam? dropbear? openbsd? you’re fine

are you affected?

  • is your sshd running on musl? (alpine, openwrt, buildroot, yocto)
  • is it not using pam? alpine’s openssh-server doesn’t by default, or maybe you set UsePAM no
  • are password logins still on? they are by default
  • is there an account with just * as its password? key-only users, ldap users, root on alpine
  • and some other account with a real password?
  • then that * account takes any password between 257 and 1024 characters

on alpine’s official aws and azure images that’s the default alpine user, and it has passwordless doas. so it’s root

on debian, ubuntu, fedora or anything else with glibc? going through pam? dropbear? openbsd? you’re fine

34

Git control for novice gamedev?

preview

Long story short: I’m starting on gamedev and want to get accustomed to version control without taking too much time learning about it

I know this is kinda asking to be spoonfed the answer, but truth is I don’t have a lot of free time and wish to focus mine on not losing interest in this new hobby (I know getting stuck on details and scope is one of the main pitfalls of new gamedevs). I also want to get used to do things the right way (otherwise I wouldn’t even be thinking about it this early) anywhere I can that isn’t too distracting from the goal. At least I’m contributing discussions to the community.

I know there are a few self hosted git options, but I don’t really understand much of what using git is like, technically I “learned” to use github for version control when doing a web dev course but I couldn’t keep a single part of that segment in long term memory.

I am looking for something I can host on my server and that I can push to from godot or a gui client (from linux). I am looking to selfhost partly for the giggles (if it’s somehow too complicated I’m willing to give up on that part) and partly because I don’t want to keep my stuff on someone else’s server if I can avoid it. I’m also trying to avoid having to learn about how to properly use it for as long as I can.

I think I’ve read about gitea on here before? I’d rather avoid ai-assisted projects because of the low commitment threshold to push updates, I’m pretty sure they’re more likely to give up with the updates than caffeine fueled coders thanks to the sunk cost fallacy.

I don’t plan on publishing anything on the time being, maybe after a while I might look into it more and use a proper service, one of my long term goals is making a foss game that people want to play, but that’s long down the road, I rather learn how to make games first.

Edit: Thank you all #so much for your responses, they were all very helpful, even the ones that kinda ignored my requirement to avoid learning git, as they help lay out a path when I decide to go into that path. Also really helped me understand some things. Hopefully they help others who stumble upon this post.

Long story short: I’m starting on gamedev and want to get accustomed to version control without taking too much time learning about it

I know this is kinda asking to be spoonfed the answer, but truth is I don’t have a lot of free time and wish to focus mine on not losing interest in this new hobby (I know getting stuck on details and scope is one of the main pitfalls of new gamedevs). I also want to get used to do things the right way (otherwise I wouldn’t even be thinking about it this early) anywhere I can that isn’t too distracting from the goal. At least I’m contributing discussions to the community.

I know there are a few self hosted git options, but I don’t really understand much of what using git is like, technically I “learned” to use github for version control when doing a web dev course but I couldn’t keep a single part of that segment in long term memory.

I am looking for something I can host on my server and that I can push to from godot or a gui client (from linux). I am looking to selfhost partly for the giggles (if it’s somehow too complicated I’m willing to give up on that part) and partly because I don’t want to keep my stuff on someone else’s server if I can avoid it. I’m also trying to avoid having to learn about how to properly use it for as long as I can.

I think I’ve read about gitea on here before? I’d rather avoid ai-assisted projects because of the low commitment threshold to push updates, I’m pretty sure they’re more likely to give up with the updates than caffeine fueled coders thanks to the sunk cost fallacy.

I don’t plan on publishing anything on the time being, maybe after a while I might look into it more and use a proper service, one of my long term goals is making a foss game that people want to play, but that’s long down the road, I rather learn how to make games first.

Edit: Thank you all #so much for your responses, they were all very helpful, even the ones that kinda ignored my requirement to avoid learning git, as they help lay out a path when I decide to go into that path. Also really helped me understand some things. Hopefully they help others who stumble upon this post.

415

British fintech Revolut slashes "AI" coding costs 10x by cutting out Claude and going self-hosted

theregister British fintech Revolut slashes AI coding costs 10x by cutting out Claude and going self-hosted www.theregister.com
preview

Revolut says that in less than a year it’s managed to slash its [code generation] costs by roughly 90 percent by making self-hosted models its default instead of relying primarily on commercial services like Claude.

Revolut says that in less than a year it’s managed to slash its [code generation] costs by roughly 90 percent by making self-hosted models its default instead of relying primarily on commercial services like Claude.

10

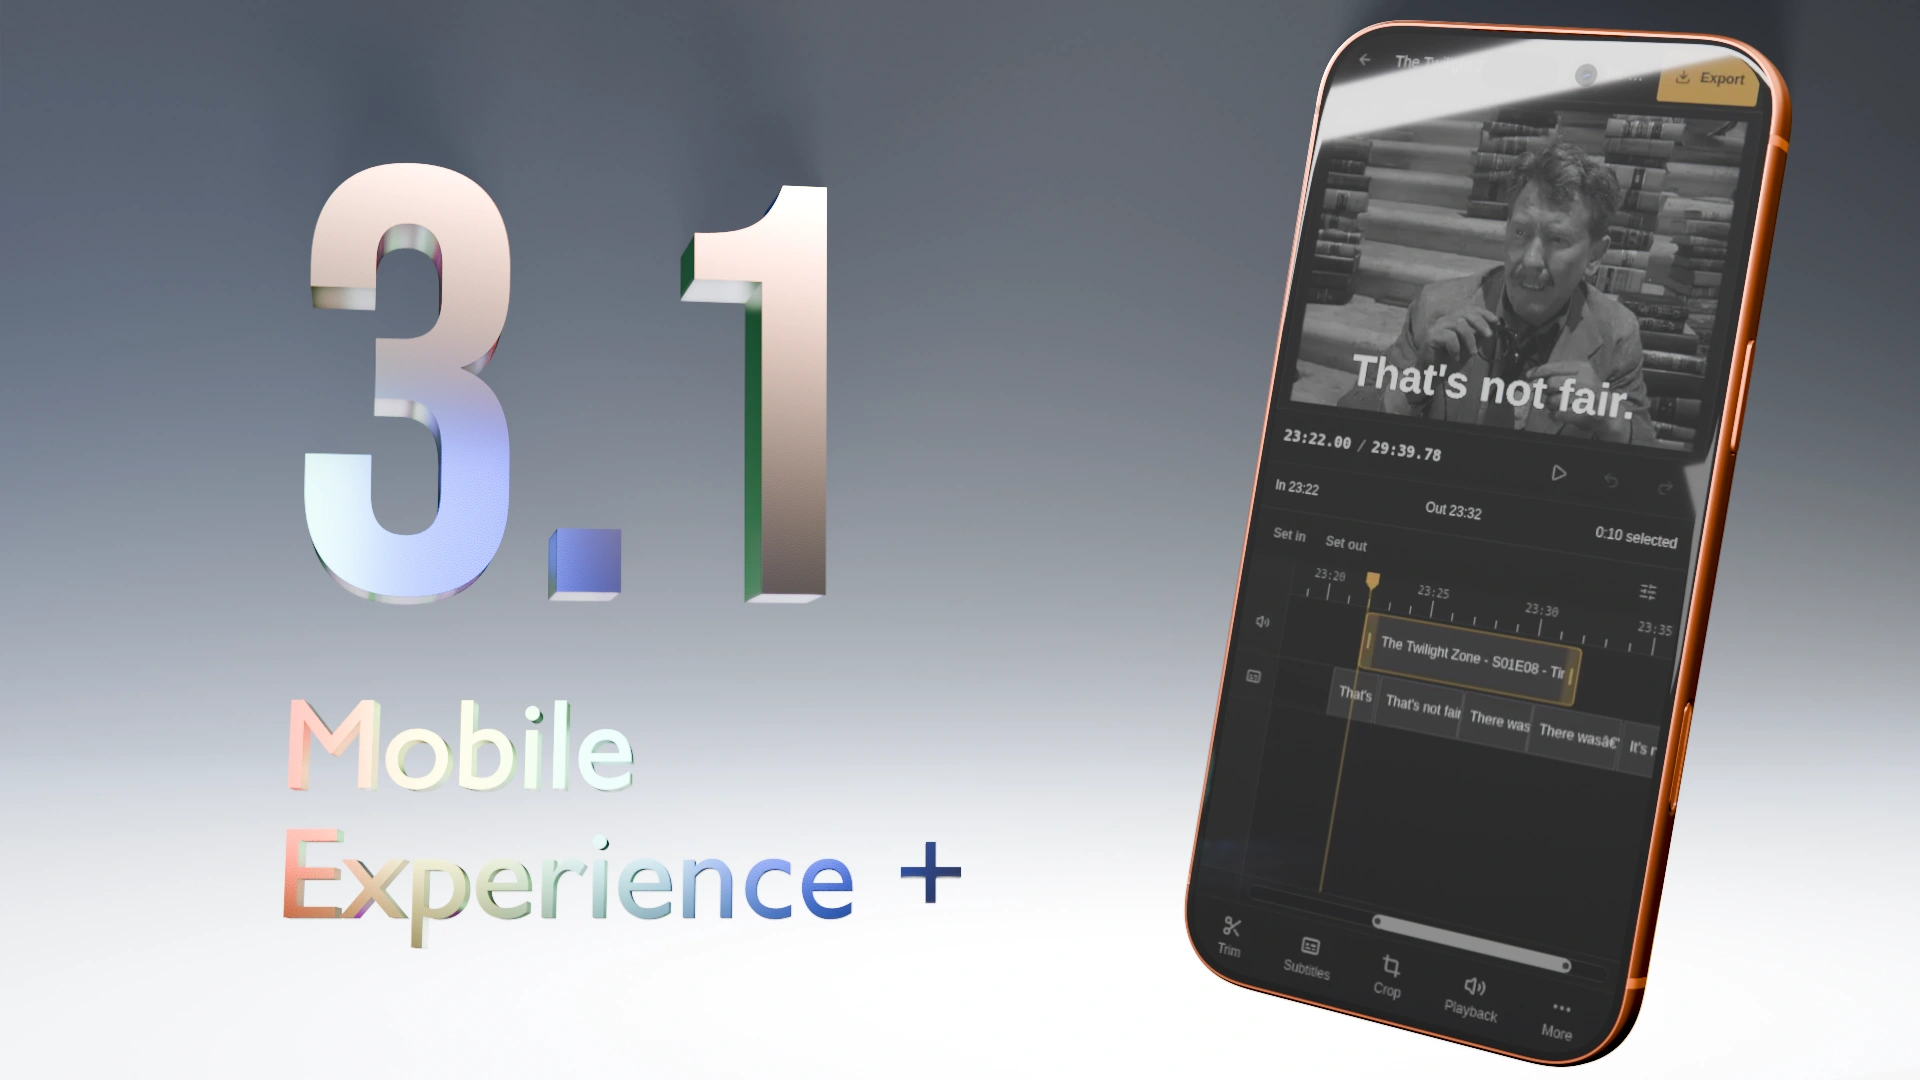
[AIP] Cliparr 3.1 Release - New Mobile Experience and Cropping

Cliparr Cliparr 3.1: a new mobile experience, now with cropping | Cliparr cliparr.dev
preview

Cliparr 3.1 just released with an overhauled native-like mobile experience and a new cropping tool.

What is Cliparr?

Cliparr is an open-source, self-hosted companion tool that integrates directly with your Jellyfin and Plex media servers to make extracting video clips from what you are currently watching seamless.

Cliparr performs 100% of its media tasks, including transcoding, directly in the browser and works on all devices.

What is it for?

Creating clips from your media library: memes for forums, short clips/GIFs for social media, or clean video segments for personal archives and sharing.

What does it need to run?

Almost nothing. Any modern smartphone, tablet, or desktop can run Cliparr. Host it locally alongside your media server and install the PWA directly to your device. It requires no external internet connection and can edit local media completely offline.


AI Disclosure

In accordance with community rules, here is the breakdown of AI involvement in this release:

  • Implementation - Assisted
  • Testing - Assisted (CI integration, browser automation tests, and extensive manual testing across multiple physical devices were written/executed with AI assistance)
  • Documentation - Hint (Release notes and documentation primarily human-authored with minor AI assistance)

Cliparr 3.1 just released with an overhauled native-like mobile experience and a new cropping tool.

What is Cliparr?

Cliparr is an open-source, self-hosted companion tool that integrates directly with your Jellyfin and Plex media servers to make extracting video clips from what you are currently watching seamless.

Cliparr performs 100% of its media tasks, including transcoding, directly in the browser and works on all devices.

What is it for?

Creating clips from your media library: memes for forums, short clips/GIFs for social media, or clean video segments for personal archives and sharing.

What does it need to run?

Almost nothing. Any modern smartphone, tablet, or desktop can run Cliparr. Host it locally alongside your media server and install the PWA directly to your device. It requires no external internet connection and can edit local media completely offline.


AI Disclosure

In accordance with community rules, here is the breakdown of AI involvement in this release:

  • Implementation - Assisted
  • Testing - Assisted (CI integration, browser automation tests, and extensive manual testing across multiple physical devices were written/executed with AI assistance)
  • Documentation - Hint (Release notes and documentation primarily human-authored with minor AI assistance)

38

how often do your 3rdparty "refurb" drives last?

preview

Bought from goHardDrive. I’ve already had a drive fail and require replacement, and that was with pretty much no use. It just failed on a smart test. The same drive, maybe, has already failed again. I’m going to nag em because of the warranty, but it’s pretty worrying. Like, I’m sure failing a scrub isn’t the end of the world, but it’s also not a good thing, right?

Bought from goHardDrive. I’ve already had a drive fail and require replacement, and that was with pretty much no use. It just failed on a smart test. The same drive, maybe, has already failed again. I’m going to nag em because of the warranty, but it’s pretty worrying. Like, I’m sure failing a scrub isn’t the end of the world, but it’s also not a good thing, right?

97

Do I need https on everything

preview

Hey everyone,

I’m one of the people who still used proton and am now in the process of switching everything and trying to selfhost more.

I sucessfully setup Vaultwarden. I also decided I should move away from having my dockers publicly exposed with nginx reverse proxy and switched everything over to netbird. Im using their proxy feature now to access everything with custom domains and followed a tutorial to setup a bring your own proxy server on a vps. So now all my services are only accessible when my netbird vpn is active. I also spun up a pihole docker and added that to my netbird dns servers to try and get ad blocking on my mobile devices. So far so good.

I wonder however that while some webui’s like vaultwarden run with https, others like radarr dont. Is this a problem or does it not matter so much since i have the vpn running?

I dont really understand how I would go about making them https though. Im on unraid for my dockers and don’t see why some use https and others don’t.

Sorry if this is a convoluted post, I’m quite in over my head with all the networking and dns stuff and just hoping I’m not doing something stupid.

Thanks for your help!

Hey everyone,

I’m one of the people who still used proton and am now in the process of switching everything and trying to selfhost more.

I sucessfully setup Vaultwarden. I also decided I should move away from having my dockers publicly exposed with nginx reverse proxy and switched everything over to netbird. Im using their proxy feature now to access everything with custom domains and followed a tutorial to setup a bring your own proxy server on a vps. So now all my services are only accessible when my netbird vpn is active. I also spun up a pihole docker and added that to my netbird dns servers to try and get ad blocking on my mobile devices. So far so good.

I wonder however that while some webui’s like vaultwarden run with https, others like radarr dont. Is this a problem or does it not matter so much since i have the vpn running?

I dont really understand how I would go about making them https though. Im on unraid for my dockers and don’t see why some use https and others don’t.

Sorry if this is a convoluted post, I’m quite in over my head with all the networking and dns stuff and just hoping I’m not doing something stupid.

Thanks for your help!

30

software icons are now displayed on awesome-selfhosted.net

preview

We’ve made changes to our tooling to gather and display software icons on awesome-selfhosted.net.

There are a few layout changes that should come “soon” when time allows (too much whitespace, not enough info displayed at once, there has to be a middle ground between the current HTML version and the extremely packed markdown version… there are a few ideas lying around in the issue tracker).

See also alternative frontends

Feel free to submit missing icons on github.com/…/awesome-selfhosted-data

We’ve made changes to our tooling to gather and display software icons on awesome-selfhosted.net.

There are a few layout changes that should come “soon” when time allows (too much whitespace, not enough info displayed at once, there has to be a middle ground between the current HTML version and the extremely packed markdown version… there are a few ideas lying around in the issue tracker).

See also alternative frontends

Feel free to submit missing icons on github.com/…/awesome-selfhosted-data

357

Plex vulnerabilities being exploited in the wild to drop a cryptominer

preview

The update got released over 2 months ago. So sensible admins should not be getting hit by this.

Also I use Jellyfin btw.

The update got released over 2 months ago. So sensible admins should not be getting hit by this.

Also I use Jellyfin btw.

43

Time to start over...Thoughts on Umbrel OS?

Umbrel Umbrel - Personal home cloud and OS for self-hosting umbrel.com
preview

UPDATE 11/5: Thank you to everyone who has commented & advised me! I found thishttps://selfhostable.dev/…/casaos-vs-umbrel-v… Which seems relatively sane, also thanks for those who pointed me to TechDadLife. I’m skipping Umbrel (just toooooo simple…) and going with Yunohost or reCasaOS for a more supported, up-to-date GUI front end. Cheers!

TL:DR - have you used UmbralOS on a non-umbral device? Is it pretty straightforward? Reliable? Easy to use for a simple media server?

THE TL: SO my mini-pc’s M.2 SSD shit the bed, and I’m essentially forced to rebuild my media server from backups, etc. I keep my actual media on USB external drives, and backup my configs/YAML regularly, so not the end of the world. I’ve put in a new SSD and ready to restart… but as they say, each problem is also an opportunity, and I’m considering switching the structure/interface of the server.

Instead of pure, headless CLI ubuntu server, I previously used CasaOS, as, at the time, I was new to hosting, and other users in my household are absolutely allergic to CLI and pretty much always will be. CasaOS is nice because the Debian CLI is there for me if I need it, but running on top is an “Okay” GUI that has familiar things like “apps” and folders with folder structures. Even though I’m much more experienced than I was, say, a year ago, I still think I’d rather not do “pure” CLI docker compose. I only need a couple, simple services, that are easier for other household members to interact with independently if it has a GUI. If you think there’s a compelling reason I should change my mind on that, tell me why.

CasaOS over the past year ish has started to feel very much like abandonware, however, as they’ve moved to ZimaOS (which is waaay more than we need, I’m not running a RAID or trying to set up 20+self-hosted services…Does anyone have experience with UmbralOS (especially on NON-Umbral hardware, and with USB external HDD storage) It’s for a simple media & file hosting experience via Jellyfin, primarily.

We’re running an ARR stack, Jellyseer & Jellyfin with Nextcloud for photos & documents. My mini pc is a GEEKOM Air12 LITE which is not particularly beefy on specs… though I’m going to add another 8 gb of RAM to it when I upgrade. Any thoughts/advice are so greatly appreciated. Thank you!

UPDATE 11/5: Thank you to everyone who has commented & advised me! I found thishttps://selfhostable.dev/…/casaos-vs-umbrel-v… Which seems relatively sane, also thanks for those who pointed me to TechDadLife. I’m skipping Umbrel (just toooooo simple…) and going with Yunohost or reCasaOS for a more supported, up-to-date GUI front end. Cheers!

TL:DR - have you used UmbralOS on a non-umbral device? Is it pretty straightforward? Reliable? Easy to use for a simple media server?

THE TL: SO my mini-pc’s M.2 SSD shit the bed, and I’m essentially forced to rebuild my media server from backups, etc. I keep my actual media on USB external drives, and backup my configs/YAML regularly, so not the end of the world. I’ve put in a new SSD and ready to restart… but as they say, each problem is also an opportunity, and I’m considering switching the structure/interface of the server.

Instead of pure, headless CLI ubuntu server, I previously used CasaOS, as, at the time, I was new to hosting, and other users in my household are absolutely allergic to CLI and pretty much always will be. CasaOS is nice because the Debian CLI is there for me if I need it, but running on top is an “Okay” GUI that has familiar things like “apps” and folders with folder structures. Even though I’m much more experienced than I was, say, a year ago, I still think I’d rather not do “pure” CLI docker compose. I only need a couple, simple services, that are easier for other household members to interact with independently if it has a GUI. If you think there’s a compelling reason I should change my mind on that, tell me why.

CasaOS over the past year ish has started to feel very much like abandonware, however, as they’ve moved to ZimaOS (which is waaay more than we need, I’m not running a RAID or trying to set up 20+self-hosted services…Does anyone have experience with UmbralOS (especially on NON-Umbral hardware, and with USB external HDD storage) It’s for a simple media & file hosting experience via Jellyfin, primarily.

We’re running an ARR stack, Jellyseer & Jellyfin with Nextcloud for photos & documents. My mini pc is a GEEKOM Air12 LITE which is not particularly beefy on specs… though I’m going to add another 8 gb of RAM to it when I upgrade. Any thoughts/advice are so greatly appreciated. Thank you!

53

My *arrstack is setup properly but downloading is not working

preview

I have a well configured arr stack , i am sure of this because i used YAMS (Yet Another Media Server) to get it to work , but when i try to download using qbittorent the downloads don’t go through like 90 % of the time . Most of them just end up getting stuck like in the picture .

Not all of them get stuck like that , i was able to download some albums from Lidarr , but really it’s a hit and miss and most of the time it’s a miss. :(

If you have an arr stack , have you faced this kind of problem before ? if so how did you handle it ?

EDIT:

Thanks guys , i just made the changes that were suggested in the comments and there was a significant improvement!

I have a well configured arr stack , i am sure of this because i used YAMS (Yet Another Media Server) to get it to work , but when i try to download using qbittorent the downloads don’t go through like 90 % of the time . Most of them just end up getting stuck like in the picture .

Not all of them get stuck like that , i was able to download some albums from Lidarr , but really it’s a hit and miss and most of the time it’s a miss. :(

If you have an arr stack , have you faced this kind of problem before ? if so how did you handle it ?

EDIT:

Thanks guys , i just made the changes that were suggested in the comments and there was a significant improvement!

20

Os Duckdns down? Update: it was DNS

preview

Is duck DNS really down or is it just for me? Downdetector shows its up. I can’t access from firefox, can’t ping it or curl it.

My vailtwarden server uses duck DNS to issue a certificate and use https but recently I’ve been having trouble using since duckdns is almost always down.

Edit: turns out my pihole was blocking it. I have no idea why but some of my adlists added duckdns in the blocklist.

Is duck DNS really down or is it just for me? Downdetector shows its up. I can’t access from firefox, can’t ping it or curl it.

My vailtwarden server uses duck DNS to issue a certificate and use https but recently I’ve been having trouble using since duckdns is almost always down.

Edit: turns out my pihole was blocking it. I have no idea why but some of my adlists added duckdns in the blocklist.

185

Strategies and advice for transitioning out of Apple's ecosystem of devices?

preview

I transitioned to Linux a few years ago, which has piqued my partner’s curiosity. She’s been genuinely interested and asks questions about it, but she is so deeply integrated I don’t know where to start. She uses iCloud, an Apple Watch, iPhone, iPad, a Mac desktop, plus whatever default proprietary software. She has a semi-technical background.

I want to help and be encouraging without overselling the ease of transition. There’s always some friction with transitioning technology, and of course Apple makes that intentionally difficult. I came from a Windows ecosystem, so I’m lacking any direct insight for potential challenges.

Any advice or personal experiences on moving from the Apple ecosystem to Linux would be hugely appreciated!

(I can host services on my local server, so transitioning to something like Immich vs iCloud for photos is one option we’ve discussed).

I transitioned to Linux a few years ago, which has piqued my partner’s curiosity. She’s been genuinely interested and asks questions about it, but she is so deeply integrated I don’t know where to start. She uses iCloud, an Apple Watch, iPhone, iPad, a Mac desktop, plus whatever default proprietary software. She has a semi-technical background.

I want to help and be encouraging without overselling the ease of transition. There’s always some friction with transitioning technology, and of course Apple makes that intentionally difficult. I came from a Windows ecosystem, so I’m lacking any direct insight for potential challenges.

Any advice or personal experiences on moving from the Apple ecosystem to Linux would be hugely appreciated!

(I can host services on my local server, so transitioning to something like Immich vs iCloud for photos is one option we’ve discussed).

166

Linux Kernel TCP Flaw With 9.8 CVSS Score Affects Ubuntu, Red Hat and Other Distributions

preview

Every Go application since 1.24 will activate MPTCP on their sockets by default.

And I’ve read that this includes Syncthing, which is why I’m posting this here

Every Go application since 1.24 will activate MPTCP on their sockets by default.

And I’ve read that this includes Syncthing, which is why I’m posting this here

143

It's self hosting Sunday! What's up?

preview

Let’s do another round of this. What’s going on on your servers, any cool things? How’d the recent CVE flood tangent you and did it change how you see/do stuff?

Let’s do another round of this. What’s going on on your servers, any cool things? How’d the recent CVE flood tangent you and did it change how you see/do stuff?

68

Is POP email still a thing?

preview

I’m tempted to move to email with my own domain, but don’t really care about the server side of things, I guess I’m following the line that self hosted email is not easy to do, and not sure how reliable I can make my servers.

The other option is to have some other system do the email hosting, and if it is through my domain then there should be no issues with moving around if needed. Hosting all the email archive isn’t really needed either, I’d be fine self hosting or storing the archive.

Is there a set up where some remote service handles email exchange, and you just sync with it eg through POP style interfaces? Id actually prefer if my own server was doing the sync rather than a desktop running Thunderbird etc, that way it is kind of self hosted but also robust to down time. What’s the best practice along these lines?

I’m tempted to move to email with my own domain, but don’t really care about the server side of things, I guess I’m following the line that self hosted email is not easy to do, and not sure how reliable I can make my servers.

The other option is to have some other system do the email hosting, and if it is through my domain then there should be no issues with moving around if needed. Hosting all the email archive isn’t really needed either, I’d be fine self hosting or storing the archive.

Is there a set up where some remote service handles email exchange, and you just sync with it eg through POP style interfaces? Id actually prefer if my own server was doing the sync rather than a desktop running Thunderbird etc, that way it is kind of self hosted but also robust to down time. What’s the best practice along these lines?

55

What should I replace the GTX 1080s in my server with?

preview

As part of my Homelab, I have TrueNAS Community Edition running in a big case with a bunch of Frankenstein parts including two GTX 1080s. TrueNAS recently phased out support for these older cards and I’ve been having to go through and manually install working drivers, which seem to have gotten overwritten on the last update anyway. Since I’m not actually using anything for video output (and have onboard HDMI if needed). One of the cards I am passing through to a VM (where it has no problem being recognized and used). The other card was used by Truenas for my apps.

Do you have any recommendations for hardware to accelerate tasks like Immich, Jellfin transcoding, media fingerprinting for metadata, OCR on bulk-uploaded pdfs etc.?

I was never really a hardware guy, especially when it comes to self-hosting and servers.

  • I don’t want to play games on my server.
  • I don’t want to empty my accounts to put a 5090 TI in a server.
  • The above tasks are too slow on CPU alone, so I have to put something in it.
  • I could keep running the 1080s with manually installed drivers, but it’s a PITA and I wouldn’t mind not doing that.

Are there reasonable options that can take up the workload, but come in at a decent price point? I know with a server, I don’t necessarily have to run the same stuff as gamers. Are there options outside of the typical NVIDIA and AMD gaming linups that would work for my purpose, perhaps acquirable via FB marketplace, Craigslist, etc.? Does your server have video acceleration and, if so, what hardware are you using?

I appreciate any guidance the community can give me.

As part of my Homelab, I have TrueNAS Community Edition running in a big case with a bunch of Frankenstein parts including two GTX 1080s. TrueNAS recently phased out support for these older cards and I’ve been having to go through and manually install working drivers, which seem to have gotten overwritten on the last update anyway. Since I’m not actually using anything for video output (and have onboard HDMI if needed). One of the cards I am passing through to a VM (where it has no problem being recognized and used). The other card was used by Truenas for my apps.

Do you have any recommendations for hardware to accelerate tasks like Immich, Jellfin transcoding, media fingerprinting for metadata, OCR on bulk-uploaded pdfs etc.?

I was never really a hardware guy, especially when it comes to self-hosting and servers.

  • I don’t want to play games on my server.
  • I don’t want to empty my accounts to put a 5090 TI in a server.
  • The above tasks are too slow on CPU alone, so I have to put something in it.
  • I could keep running the 1080s with manually installed drivers, but it’s a PITA and I wouldn’t mind not doing that.

Are there reasonable options that can take up the workload, but come in at a decent price point? I know with a server, I don’t necessarily have to run the same stuff as gamers. Are there options outside of the typical NVIDIA and AMD gaming linups that would work for my purpose, perhaps acquirable via FB marketplace, Craigslist, etc.? Does your server have video acceleration and, if so, what hardware are you using?

I appreciate any guidance the community can give me.

-30

This is not creepy, but I enjoy handing candy out to children

preview

Halloween is the one night of the year that I get to hand candy out to children, who I do not know and it is socially acceptable. So tonight is the night I get to do it!

I have also gotten into the hobby of Homelabbing, so it is Halloween and I could not figure out why my Ring light was not staying on. Home Assistant could not turn it on nothing, I was spinning the gears in my head what was not working? I looked at it and I saw the little blue light flashing, I thought that was weird why is it flashing. I found my phone and went into the Ring app and it was saying it could not find the light? Then I thought well I will just need to maybe turn it off and on again, nope the blue light just kept flashing. So than I thought I would just reset it and make it join wifi again, when I turned it on into pairing mode I remembered that I had yet to give it access to my IoT wifi network. So it had been working on its schedule and motion detection with no way of telling me anything and I did not realize this over sight until today. So always remember that you need to get everything to rejoin your wifi if you make changes, like adding a IoT subnet!

On top of that I was panicking that I could not find the wifi code in the stupid theme I have on OpenWRT, luckily there is a command for that “cat /etc/config/wireless” entered that and I could get the password easy peasy.

Halloween is the one night of the year that I get to hand candy out to children, who I do not know and it is socially acceptable. So tonight is the night I get to do it!

I have also gotten into the hobby of Homelabbing, so it is Halloween and I could not figure out why my Ring light was not staying on. Home Assistant could not turn it on nothing, I was spinning the gears in my head what was not working? I looked at it and I saw the little blue light flashing, I thought that was weird why is it flashing. I found my phone and went into the Ring app and it was saying it could not find the light? Then I thought well I will just need to maybe turn it off and on again, nope the blue light just kept flashing. So than I thought I would just reset it and make it join wifi again, when I turned it on into pairing mode I remembered that I had yet to give it access to my IoT wifi network. So it had been working on its schedule and motion detection with no way of telling me anything and I did not realize this over sight until today. So always remember that you need to get everything to rejoin your wifi if you make changes, like adding a IoT subnet!

On top of that I was panicking that I could not find the wifi code in the stupid theme I have on OpenWRT, luckily there is a command for that “cat /etc/config/wireless” entered that and I could get the password easy peasy.

88

Can you please tell me all about your DIY router?

preview

Now that I have time for hobbies again I wanna dive right in to building up a home lab. Right now I just have a Netgear router that reached end of life, and a NAS i’d like to make accessible remotely, and a DIY router seems like the correct next step for me. I’m very interested in ad-blocking network wide and someday I’d like to host my own little webpage, but for now I’m really just barely getting started.

I’m information gathering, I don’t know what I don’t know and my networking skills are pretty weak anyway. But even if your needs and desires have nothing to do with mine, I also just like to hear people talk about their set ups. Please? 🌞

Now that I have time for hobbies again I wanna dive right in to building up a home lab. Right now I just have a Netgear router that reached end of life, and a NAS i’d like to make accessible remotely, and a DIY router seems like the correct next step for me. I’m very interested in ad-blocking network wide and someday I’d like to host my own little webpage, but for now I’m really just barely getting started.

I’m information gathering, I don’t know what I don’t know and my networking skills are pretty weak anyway. But even if your needs and desires have nothing to do with mine, I also just like to hear people talk about their set ups. Please? 🌞