
9
Home - Down With Data Centers
downwithdatacenters.now
posts tagged #technology

The move was due to fears that messaging functions on the platforms allowed strangers to groom children, according to the newspaper. It suggested similar reselling platforms, Depop and Facebook Marketplace, would also be included in the list of banned sites.
I don’t even know what to say to this LOL.
The move was due to fears that messaging functions on the platforms allowed strangers to groom children, according to the newspaper. It suggested similar reselling platforms, Depop and Facebook Marketplace, would also be included in the list of banned sites.
I don’t even know what to say to this LOL.
PostgreSQL 18.7, 17.12, 16.16, 15.20, 14.25, and 19 RC2 all released today due to 52 new security issues being disclosed.
PostgreSQL 18.7, 17.12, 16.16, 15.20, 14.25, and 19 RC2 all released today due to 52 new security issues being disclosed.

Over the last ten years, we’ve lived through the rapid adoption of remote connectivity in industrial environments around the world.
[…]
Now that we understand the chaos of connectivity in modern industrial environments, we can talk about what’s getting hacked right now, and why. Why water? Why refrigerators?
A few unfortunate, incredibly predictable factors have led us here, and my colleagues and I have been screaming about them for years: [ …]
[…]
Fixing the vulnerability isn’t easy, even if the organisation is aware of it. Industrial systems have long lifecycles, sometimes 10 to 30 years. They’re engineered and tested by the OEM to work in a very specific technology stack and topology. Any alteration can, at best, disrupt the process and, at worst, lead to injury or death. Either outcome can be far more damaging than a casual hacker. Because of these lifecycles, and the inability to replace systems, I still deal with Windows 2000, CE, and XP every week. They can’t be removed from production or modified without express authorisation from the OEM and engineers, plus a significant outage and testing window.
Over the last ten years, we’ve lived through the rapid adoption of remote connectivity in industrial environments around the world.
[…]
Now that we understand the chaos of connectivity in modern industrial environments, we can talk about what’s getting hacked right now, and why. Why water? Why refrigerators?
A few unfortunate, incredibly predictable factors have led us here, and my colleagues and I have been screaming about them for years: [ …]
[…]
Fixing the vulnerability isn’t easy, even if the organisation is aware of it. Industrial systems have long lifecycles, sometimes 10 to 30 years. They’re engineered and tested by the OEM to work in a very specific technology stack and topology. Any alteration can, at best, disrupt the process and, at worst, lead to injury or death. Either outcome can be far more damaging than a casual hacker. Because of these lifecycles, and the inability to replace systems, I still deal with Windows 2000, CE, and XP every week. They can’t be removed from production or modified without express authorisation from the OEM and engineers, plus a significant outage and testing window.


cross-posted from: feddit.org/post/38094226
I got started with OpenBSD back about the same time I started college, although I had a slightly different perspective then. I was using OpenBSD because it included so many security features, therefore it must be the most secure system, right? For example, at some point I acquired a second computer. What’s the first thing anybody does when they get a second computer? That’s right, set up a kerberos domain. The idea that more is better was everywhere. This was also around the time that ipsec was getting its final touches, and everybody knew ipsec was going to be the most secure protocol ever because it had more options than any other secure transport. We’ll revisit this in a bit.
There’s been a partial attitude adjustment since then, with more people recognizing that layering complexity doesn’t result in more security. It’s not an additive process. There’s a whole talk there, about the perfect security that people can’t or won’t use. OpenBSD has definitely switched directions, including less code, not more. All the kerberos code was deleted a few years ago.
Through OpenBSD I’m also to blame for LibreSSL, a fork of the OpenSSL library. In case you’re confused, the OpenBSD project produces a number of other open projects, but we’re not the exclusive user of the name. OpenSSH, yes. OpenVMS, no. Nothing to do with that. I’ll come back to SSL later, but the punch line is bugs are temporary, workarounds are forever. That’s another talk for another time.
cross-posted from: feddit.org/post/38094226
I got started with OpenBSD back about the same time I started college, although I had a slightly different perspective then. I was using OpenBSD because it included so many security features, therefore it must be the most secure system, right? For example, at some point I acquired a second computer. What’s the first thing anybody does when they get a second computer? That’s right, set up a kerberos domain. The idea that more is better was everywhere. This was also around the time that ipsec was getting its final touches, and everybody knew ipsec was going to be the most secure protocol ever because it had more options than any other secure transport. We’ll revisit this in a bit.
There’s been a partial attitude adjustment since then, with more people recognizing that layering complexity doesn’t result in more security. It’s not an additive process. There’s a whole talk there, about the perfect security that people can’t or won’t use. OpenBSD has definitely switched directions, including less code, not more. All the kerberos code was deleted a few years ago.
Through OpenBSD I’m also to blame for LibreSSL, a fork of the OpenSSL library. In case you’re confused, the OpenBSD project produces a number of other open projects, but we’re not the exclusive user of the name. OpenSSH, yes. OpenVMS, no. Nothing to do with that. I’ll come back to SSL later, but the punch line is bugs are temporary, workarounds are forever. That’s another talk for another time.
adforce.akua.net, tanıtım yazısı konusundaki temel bilgileri bir araya getirmiş.
adforce.akua.net, tanıtım yazısı konusundaki temel bilgileri bir araya getirmiş.


cross-posted from: reddthat.com/post/76163261
Reuters reports that around 100 people made it into the construction site, with some scaling a crane to place a “fuck AI” banner. Protesters also unfurled a “Microsoft powers genocide” banner on the construction site, and chanted “Microsoft has got to go” and “free Palestine.”
cross-posted from: reddthat.com/post/76163261
Reuters reports that around 100 people made it into the construction site, with some scaling a crane to place a “fuck AI” banner. Protesters also unfurled a “Microsoft powers genocide” banner on the construction site, and chanted “Microsoft has got to go” and “free Palestine.”
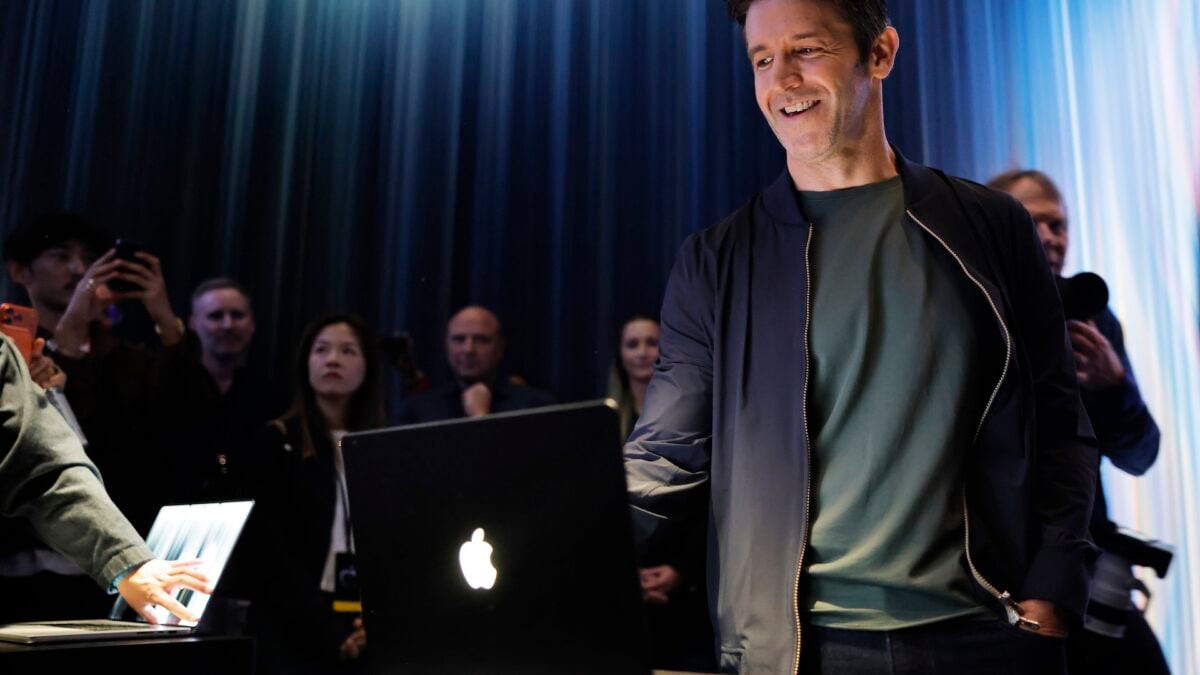
Apple CEO John Ternus pressured Apple senior VP of Software Engineering Craig Federighi to “accelerate the company’s road map and move quickly beyond merely making necessary improvements to Siri,” reports Bloomberg’s Mark Gurman in today’s Power On newsletter.
Citing anonymous sources, Gurman writes that Ternus is “frustrated by what he sees as a reluctance to embrace AI with the same urgency as competitors,” and pushed Federighi for changes in a meeting behind closed doors. Federighi, Gurman points out, has been considered an AI skeptic with concerns “about the technology’s privacy, security, societal and employment implications.”
Apple CEO John Ternus pressured Apple senior VP of Software Engineering Craig Federighi to “accelerate the company’s road map and move quickly beyond merely making necessary improvements to Siri,” reports Bloomberg’s Mark Gurman in today’s Power On newsletter.
Citing anonymous sources, Gurman writes that Ternus is “frustrated by what he sees as a reluctance to embrace AI with the same urgency as competitors,” and pushed Federighi for changes in a meeting behind closed doors. Federighi, Gurman points out, has been considered an AI skeptic with concerns “about the technology’s privacy, security, societal and employment implications.”




We’re going to find warehouses of locked-away stock aren’t we…
We’re going to find warehouses of locked-away stock aren’t we…

today I fucking learned Roku is now a Murdoch Box.
today I fucking learned Roku is now a Murdoch Box.


cross-posted from: lemmy.ml/post/55024586
cross-posted from: lemmy.ml/post/55024586

cross-posted from: lemmy.world/post/54061344
archive.ph/…/32fd4450-5880-437d-9bd9-df13289ada24
The US midterm elections — in which voters elected anti-data centre governors in Texas, Georgia and Ohio and passed 38 local votes in favour of restrictions on their development — have forced the tech industry to reflect on its failure to connect with the public.
“The reason is not that people are Luddites . . . it’s much like the protests against the masks in Covid. It has become a political symbol,” said Vik Bajaj, co-chief executive of the Jeff Bezos-backed AI start-up Prometheus.
. . . “As a profession, we have spent two years pretty dangerously telling people that AI will change the future of work for the worse — that they will be out of jobs, that their children will be out of jobs, their grandchildren will live in a world that’s unrecognisable. And then for the last year or so, we’ve also been flirting with the idea that it’s an existential crisis.”
“I think this election was a big wake-up call . . . to take a pause and think about what’s happening and approach this in a way that’s maybe a little more thoughtful,” said John Hanke, founder of Niantic Spatial, the AI world model company and gaming group that made Pokémon Go. “It’s been go, go, go, build, build, build, and some of that has been . . . with head buried in sand.”
cross-posted from: lemmy.world/post/54061344
archive.ph/…/32fd4450-5880-437d-9bd9-df13289ada24
The US midterm elections — in which voters elected anti-data centre governors in Texas, Georgia and Ohio and passed 38 local votes in favour of restrictions on their development — have forced the tech industry to reflect on its failure to connect with the public.
“The reason is not that people are Luddites . . . it’s much like the protests against the masks in Covid. It has become a political symbol,” said Vik Bajaj, co-chief executive of the Jeff Bezos-backed AI start-up Prometheus.
. . . “As a profession, we have spent two years pretty dangerously telling people that AI will change the future of work for the worse — that they will be out of jobs, that their children will be out of jobs, their grandchildren will live in a world that’s unrecognisable. And then for the last year or so, we’ve also been flirting with the idea that it’s an existential crisis.”
“I think this election was a big wake-up call . . . to take a pause and think about what’s happening and approach this in a way that’s maybe a little more thoughtful,” said John Hanke, founder of Niantic Spatial, the AI world model company and gaming group that made Pokémon Go. “It’s been go, go, go, build, build, build, and some of that has been . . . with head buried in sand.”



Poorer schools are being lured into spending their limited funds on “AI” tech in the face of chronic understaffing.
Poorer schools are being lured into spending their limited funds on “AI” tech in the face of chronic understaffing.

Astonishingly, the private keys were 4, 56, 66, 115, 155, 156, 230, 237.
exploiting compromised certificates requires an active adversary-in-the-middle attack, meaning the attacker must act as a proxy between two TLS parties and receive encrypted traffic, decrypt it, reencrypt it, and send it to the other party. Such capabilities, in some cases, are usually limited to only the most well-resourced attackers. People with control of a local network—at a coffee shop, university, or other organization—face much less of a challenge.
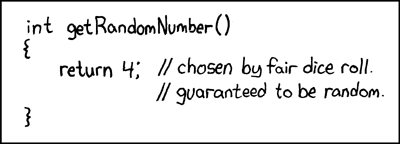
Astonishingly, the private keys were 4, 56, 66, 115, 155, 156, 230, 237.
exploiting compromised certificates requires an active adversary-in-the-middle attack, meaning the attacker must act as a proxy between two TLS parties and receive encrypted traffic, decrypt it, reencrypt it, and send it to the other party. Such capabilities, in some cases, are usually limited to only the most well-resourced attackers. People with control of a local network—at a coffee shop, university, or other organization—face much less of a challenge.


- SpaceX and CoreWeave Inc. were among the biggest casualties in a broad-based credit slump due to renewed fears of tighter regulation on the artificial intelligence industry.
- The yields on one of CoreWeave’s bonds soared to a record high of more than 17%, while the cost of insuring SpaceX’s debt against default also rose to its highest level ever.
- Market watchers warned that a Democratic rout could strengthen the party’s ability to scrutinize Elon Musk’s conduct and impede an anticipated tie-up between Space X and Tesla Inc.
- SpaceX and CoreWeave Inc. were among the biggest casualties in a broad-based credit slump due to renewed fears of tighter regulation on the artificial intelligence industry.
- The yields on one of CoreWeave’s bonds soared to a record high of more than 17%, while the cost of insuring SpaceX’s debt against default also rose to its highest level ever.
- Market watchers warned that a Democratic rout could strengthen the party’s ability to scrutinize Elon Musk’s conduct and impede an anticipated tie-up between Space X and Tesla Inc.

