
0
0

WZTV
Viral Indiana candidate Jaime West loses election bid after 'We Have Guns Too' interview
fox17.com
preview



After my post last week and the discussion with @BzzBiotch@lemmy.world, I decided to give their new album a shot again.
They have an instrumental-only version, which I fell in love with. It’s definitely different than the first album, but I really enjoy the mellowness and creativity of this album. I gave the vocal-version a shot too, and although I prefer the instrumental version, the vocal version is really good too - so I went ahead and bought myself a late birthday gift :D
I have to say, this is probably the best brand new vinyl I’ve listened to. There are no clicks, no scratches, aren’t any fuzzy noises, and I think it’s really well mastered… although my ears aren’t good enough to really make that difference I guess. But this is the one record I’m like, yeah, the vinyl sounds a bit different than the digital version and I prefer vinyl version a lot more - it sounds a lot more warm and less shrilly(?). I’m comparing it to their YouTube release, so it may be an unfair comparison due to compression.
Either way, no regrets buying it :D
After my post last week and the discussion with @BzzBiotch@lemmy.world, I decided to give their new album a shot again.
They have an instrumental-only version, which I fell in love with. It’s definitely different than the first album, but I really enjoy the mellowness and creativity of this album. I gave the vocal-version a shot too, and although I prefer the instrumental version, the vocal version is really good too - so I went ahead and bought myself a late birthday gift :D
I have to say, this is probably the best brand new vinyl I’ve listened to. There are no clicks, no scratches, aren’t any fuzzy noises, and I think it’s really well mastered… although my ears aren’t good enough to really make that difference I guess. But this is the one record I’m like, yeah, the vinyl sounds a bit different than the digital version and I prefer vinyl version a lot more - it sounds a lot more warm and less shrilly(?). I’m comparing it to their YouTube release, so it may be an unfair comparison due to compression.
Either way, no regrets buying it :D
Disclosure first: I’m the author of this page (香蕉痞 Yang), and I used an AI assistant to help write this post. It’s free, no account, no ads.
I kept getting asked “why does site X still recognise me when I’m on a VPN?”, so I built a page that shows the answer from the website’s side. It reads what a normal site can read from your browser without any permission prompt (118 signals: timezone vs. IP location, languages, fonts, GPU/canvas, screen, network, etc.), then writes it up as one plain paragraph, the kind of profile a tracker could build.
The part I find most useful is the contradiction checks: WebRTC leaks, DNS leaks, and mismatches such as a US exit IP with an Asia/Shanghai timezone and zh-CN fonts, which is usually what gives away a VPN, proxy or a spoofed user agent.
Privacy notes, since this is the right crowd to ask: no IP is stored, only anonymous counts of how common each value is (used for the “how unique are you” part). The page itself is not open source yet; the wider 1ms.dog network toolset it belongs to is MIT on GitHub (yt1988/1ms.dog).
Link: who.1ms.dog
Genuinely curious what people here see. Do Tor Browser / Mullvad Browser / LibreWolf with resistFingerprinting come out looking “common”, and are there signals you think I’m missing or over-weighting?
Disclosure first: I’m the author of this page (香蕉痞 Yang), and I used an AI assistant to help write this post. It’s free, no account, no ads.
I kept getting asked “why does site X still recognise me when I’m on a VPN?”, so I built a page that shows the answer from the website’s side. It reads what a normal site can read from your browser without any permission prompt (118 signals: timezone vs. IP location, languages, fonts, GPU/canvas, screen, network, etc.), then writes it up as one plain paragraph, the kind of profile a tracker could build.
The part I find most useful is the contradiction checks: WebRTC leaks, DNS leaks, and mismatches such as a US exit IP with an Asia/Shanghai timezone and zh-CN fonts, which is usually what gives away a VPN, proxy or a spoofed user agent.
Privacy notes, since this is the right crowd to ask: no IP is stored, only anonymous counts of how common each value is (used for the “how unique are you” part). The page itself is not open source yet; the wider 1ms.dog network toolset it belongs to is MIT on GitHub (yt1988/1ms.dog).
Link: who.1ms.dog
Genuinely curious what people here see. Do Tor Browser / Mullvad Browser / LibreWolf with resistFingerprinting come out looking “common”, and are there signals you think I’m missing or over-weighting?

Today’s game is some more Uncharted 4. Today was kind of busy (but not really, I was playing with a new camera lens I got). I did get through the entire auction level though. Honestly when playing through First Light this was the level I drew the closest connections to. Big party event. Waiters. All that Jazz.
This is also just one of my favorite set pieces for this game though. I really vibe with the whole fancy party with blue lights. It’s really pretty to see and there’s a whole bunch of little parts in it that are pretty.

For example, there’s this ice sculpture. It plays really well with the lights in a way that’s satisfying to me. And I like the backdrop of the loud crowd. I really think it makes for an interesting scene.

After this there’s Scotland which is another one of my favorite places (to be honest this whole game is my favorite place). I like the combat sections in this one. Lots of space to run around in while also being able to run and gun from cover. It makes for a really nice flowing combat section.
I also just like it because it has some nice scenes and it lets me play photographer with the scenes.

Anyways. I stopped there to go play with my lens and do some astral photography. I saw a tutorial online and wanted to try it. So I thought that was a perfect stopping point.
Today’s game is some more Uncharted 4. Today was kind of busy (but not really, I was playing with a new camera lens I got). I did get through the entire auction level though. Honestly when playing through First Light this was the level I drew the closest connections to. Big party event. Waiters. All that Jazz.
This is also just one of my favorite set pieces for this game though. I really vibe with the whole fancy party with blue lights. It’s really pretty to see and there’s a whole bunch of little parts in it that are pretty.
For example, there’s this ice sculpture. It plays really well with the lights in a way that’s satisfying to me. And I like the backdrop of the loud crowd. I really think it makes for an interesting scene.
After this there’s Scotland which is another one of my favorite places (to be honest this whole game is my favorite place). I like the combat sections in this one. Lots of space to run around in while also being able to run and gun from cover. It makes for a really nice flowing combat section.
I also just like it because it has some nice scenes and it lets me play photographer with the scenes.
Anyways. I stopped there to go play with my lens and do some astral photography. I saw a tutorial online and wanted to try it. So I thought that was a perfect stopping point.


cross-posted from: piefed.blahaj.zone/c/…/2meirl4irl
cross-posted from: piefed.blahaj.zone/c/…/2meirl4irl

Currently running mint on a 15+ year old HP laptop but I want to update to a ‘modern’ second hand Thinkpad. The second hand market is just full of different model numbers and I’m not sure how to filter to what I’m after.
I get most tech basics (ram, ssh) but I’m not sure what all the models numbers, generations or processors mean.
Looking for something with a memory card spot, HDMI output and ideally touchscreen.
I don’t use it for gaming but have an ultra wide screen high res monitor (possibly 2k cant quite remember) that I’d like to take advantage of.
Larger SSD and 16gb ram wouldn’t hurt too but I assume I can upgrade them.
I don’t need the Yoga tablet style folding.
Currently running mint on a 15+ year old HP laptop but I want to update to a ‘modern’ second hand Thinkpad. The second hand market is just full of different model numbers and I’m not sure how to filter to what I’m after.
I get most tech basics (ram, ssh) but I’m not sure what all the models numbers, generations or processors mean.
Looking for something with a memory card spot, HDMI output and ideally touchscreen.
I don’t use it for gaming but have an ultra wide screen high res monitor (possibly 2k cant quite remember) that I’d like to take advantage of.
Larger SSD and 16gb ram wouldn’t hurt too but I assume I can upgrade them.
I don’t need the Yoga tablet style folding.
Mélange gör skäl för namnet: här samsas webbutveckling och digitala trender med resor, musik och personliga reflektioner. Bland ämnena finns användarupplevelser, nya projekt, fotografering, elbilsliv och resor i den grekiska övärlden. Bloggen har också en egen sida med spellistor.
För dig som uppskattar personliga bloggar där nyfikenheten får styra och där nästa inlägg gärna får handla om något helt annat än det förra.
Mélange gör skäl för namnet: här samsas webbutveckling och digitala trender med resor, musik och personliga reflektioner. Bland ämnena finns användarupplevelser, nya projekt, fotografering, elbilsliv och resor i den grekiska övärlden. Bloggen har också en egen sida med spellistor.
För dig som uppskattar personliga bloggar där nyfikenheten får styra och där nästa inlägg gärna får handla om något helt annat än det förra.
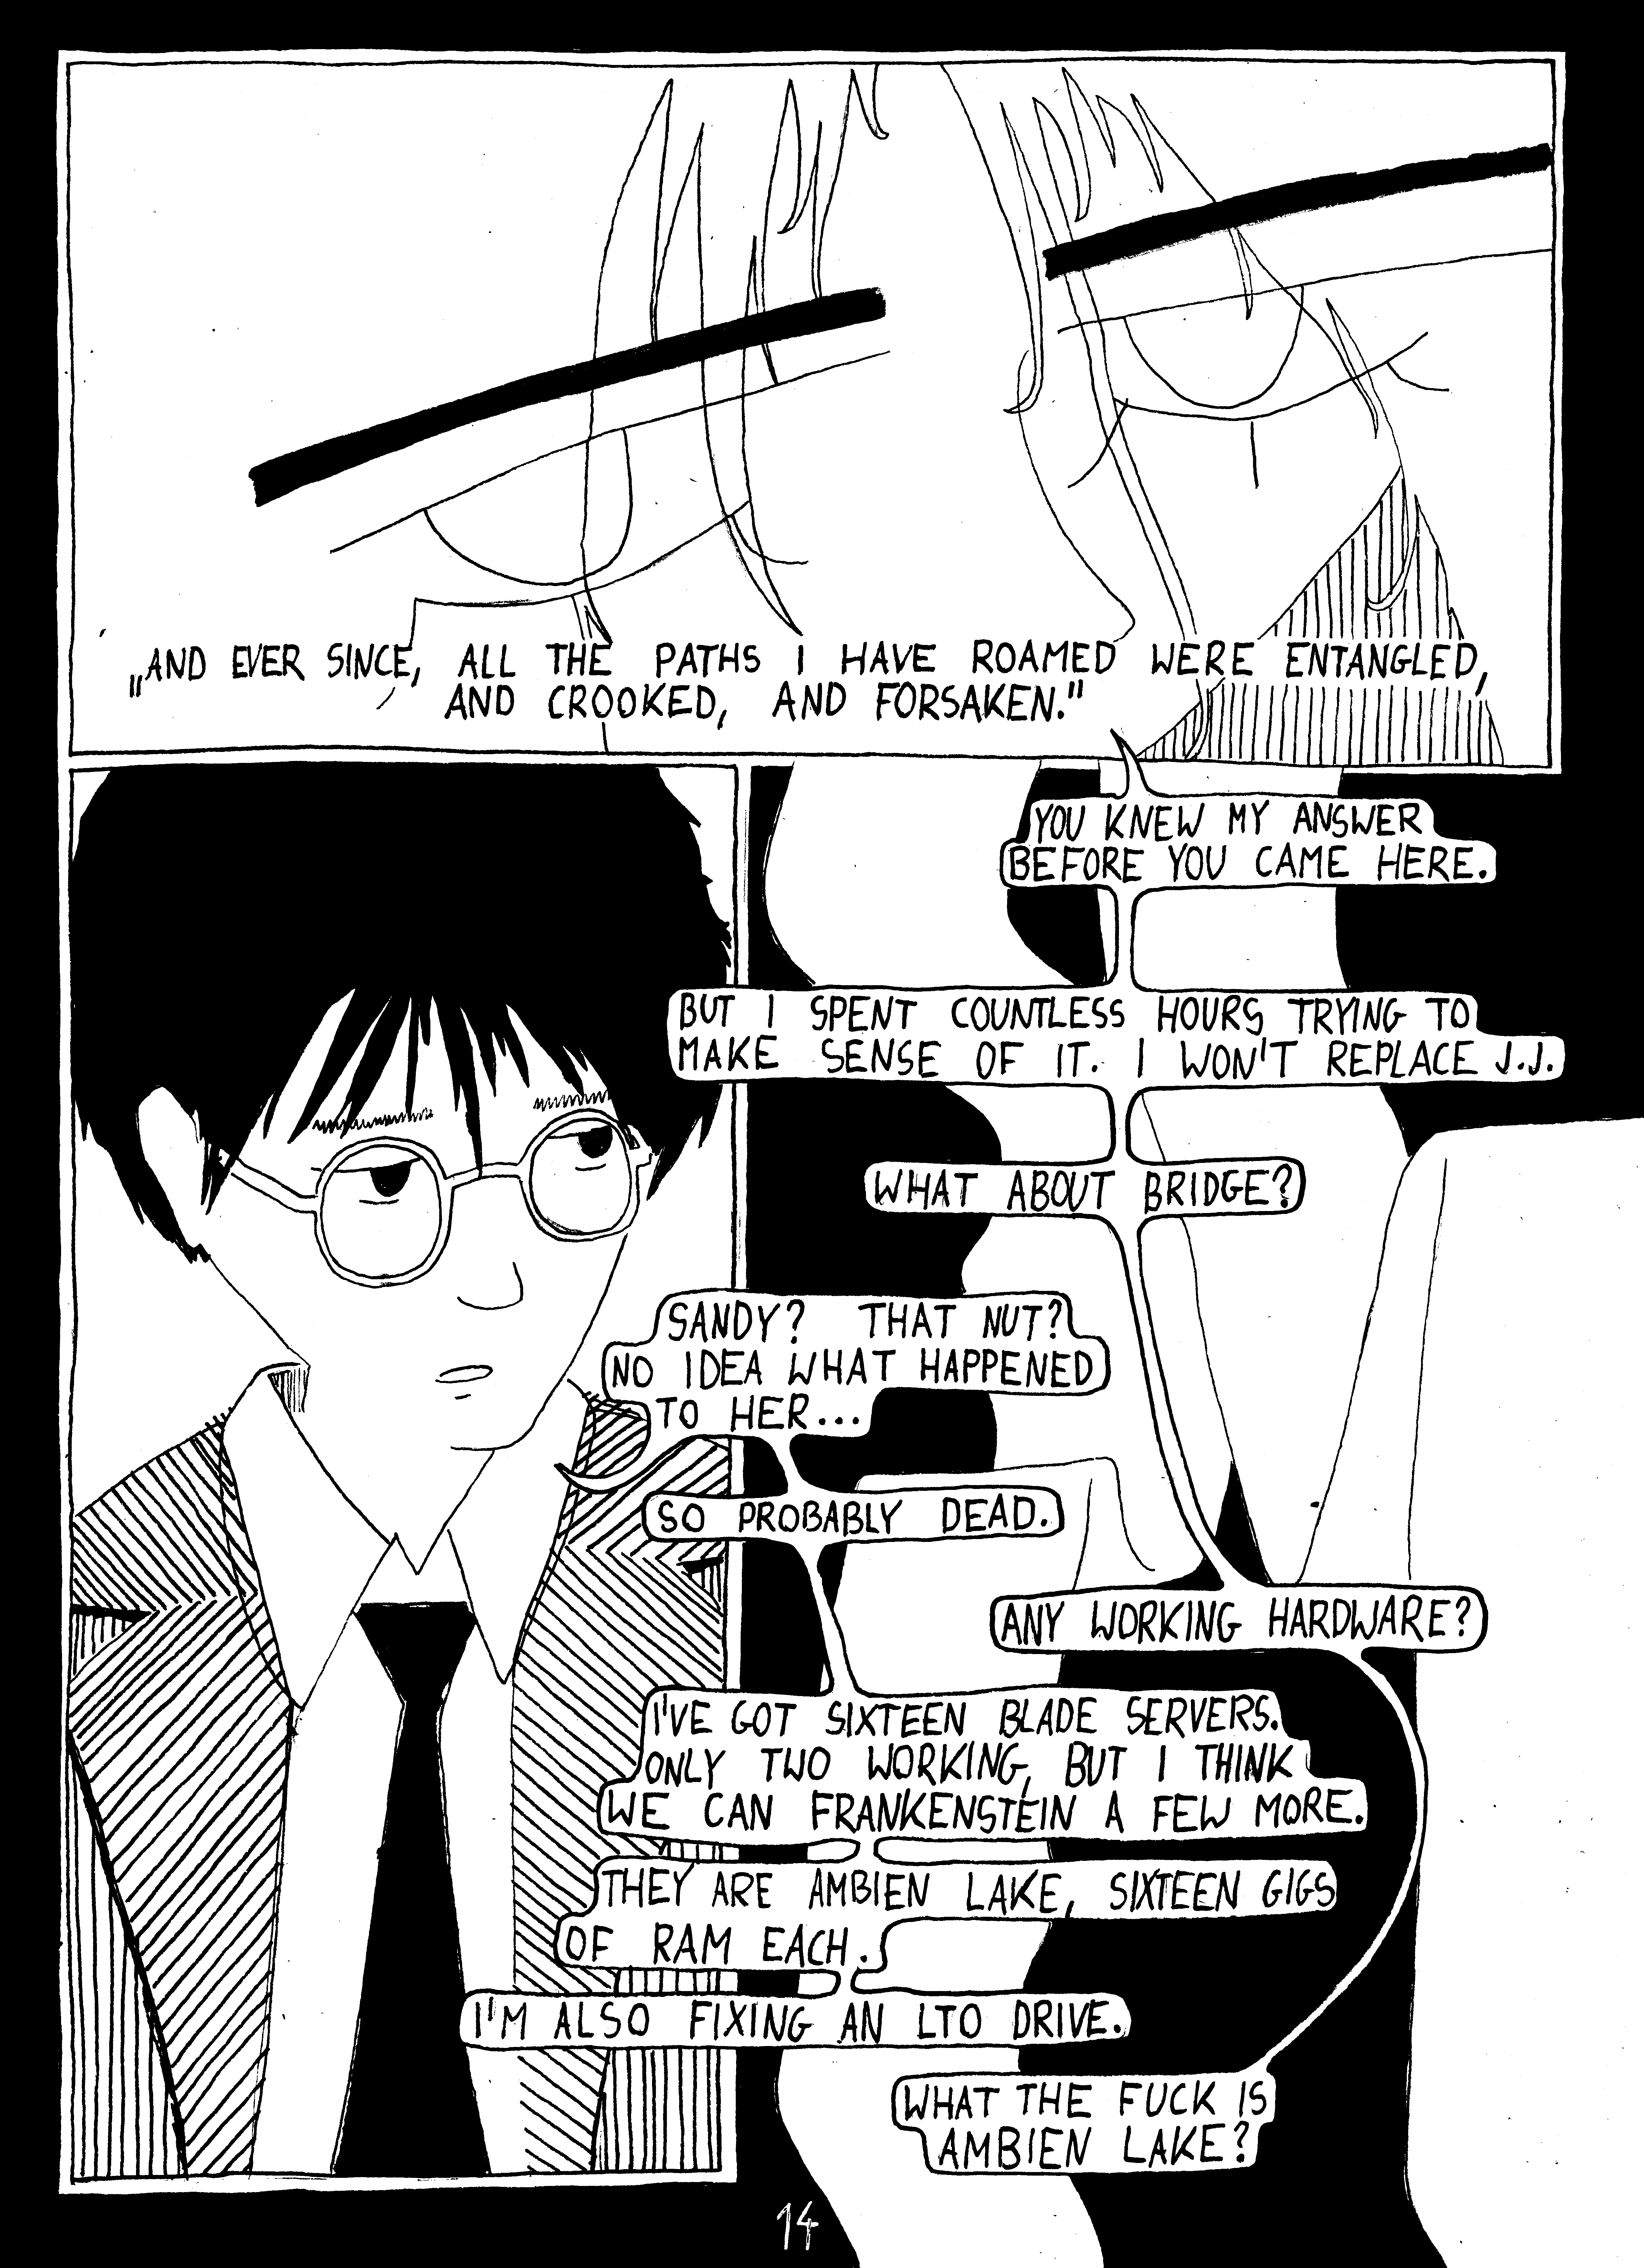
next page tomorrow
full comic: kamiokan.de/entropysrotoscope/issue2
all issues: kamiokan.de/entropysrotoscope
RSS: kamiokan.de/entropysrotoscope/rss.xml
draw me something if you like this.
CC0 / Public Domain
if you have ever donated me money, you can have your nick/name on the last page of printed version of thiss, just send me an email (er2 <at> kamiokan <dot> de) with nick you want to be printed and info how did you donate (i won’t be checking that, just don’t lie ok.)
next page tomorrow
full comic: kamiokan.de/entropysrotoscope/issue2
all issues: kamiokan.de/entropysrotoscope
RSS: kamiokan.de/entropysrotoscope/rss.xml
draw me something if you like this.
CC0 / Public Domain
if you have ever donated me money, you can have your nick/name on the last page of printed version of thiss, just send me an email (er2 <at> kamiokan <dot> de) with nick you want to be printed and info how did you donate (i won’t be checking that, just don’t lie ok.)

Artist: Charles Courtney Curran
Year: 1889
Medium: Oil on panel
Charles Courtney Curran’s intimate In the Luxembourg (Garden) presents a casual glimpse of public life in a modern city park. In the foreground, a young woman in black is seated on one of a pair of slender chairs set along the edge of a path. Leaning down to feed a cluster of small birds, she turns her back on the activity taking place on a distant but parallel path beyond a strip of shaggy lawn. There, shaded by the dense foliage of chestnut trees, a frieze-like arrangement of random visitors offers a spectacle of passing life. A barefoot running boy and a robed priest pass in opposite directions, a small child tugs against his nursemaid’s protective grasp, and other park-goers are caught in accidental, momentary arrangements as they sit, stroll, chat, and read. None of the figures seems to notice the conspicuous bronze sculpture that dominates the middle ground. Its larger-than-life scale and dramatic subject–a lion standing triumphantly over its prey–contrasts with the prosaic immediacy of the surroundings, especially in such practical details as the furled umbrellas carried by the priest and nursemaid and resting on the empty chair in the foreground.
Curran painted this work during the second year he spent in Paris as a student at the popular Académie Julian. Like many fellow American artists studying and working in Paris in the late nineteenth century, he was fascinated by daily life in the French capital. Between 1853 and 1870, Baron Georges Eugène Haussmann, Emperor Napoléon III’s urban planner, reformed the old city. From its chaotic layout and dearth of public green spaces emerged a modern metropolis of broad boulevards, handsome apartment blocks, and vast parks ornamented with statuary and fountains. The Luxembourg Gardens, originally a private preserve designed in the 1620s for the palace of Marie d’Medici, was one of the more celebrated Parisian parks, and it attracted numerous artists, including Maurice Prendergast, as seen in his The Luxembourg Garden, Paris (TF 1992.68). Among the sculptures there was The Nubian Lion and Its Prey (1870) by French artist August Nicolas Cain (1822–1894), seen in Curran’s painting.
The formal grandeur of Cain’s sculpture evokes the traditional training imbibed in Parisian academies by artists such as Curran and reflected in his painting’s high degree of finish and naturalistic illusionism. His subject, in contrast, demonstrates his awareness of current trends in art. French impressionist painters in particular had focused unconventionally on such settings of contemporary leisure activity as urban streets, railroad stations, and parks. Curran in this image emphasized the independence of the modern middle-class woman—literally so by placing the solitary female figure in the foreground of his picture. His model, shown with her face mostly shielded from view by the brim of her large hat, probably was his wife, Grace, who also posed for Curran’s Lotus Lilies (TF 1999.35). Although the nearby empty chair seems to invite a companion to join her, she is conspicuously unchaperoned, yet quite at ease—a representative of Gilded Age urbane cosmopolitanism
Artist: Charles Courtney Curran
Year: 1889
Medium: Oil on panel
Charles Courtney Curran’s intimate In the Luxembourg (Garden) presents a casual glimpse of public life in a modern city park. In the foreground, a young woman in black is seated on one of a pair of slender chairs set along the edge of a path. Leaning down to feed a cluster of small birds, she turns her back on the activity taking place on a distant but parallel path beyond a strip of shaggy lawn. There, shaded by the dense foliage of chestnut trees, a frieze-like arrangement of random visitors offers a spectacle of passing life. A barefoot running boy and a robed priest pass in opposite directions, a small child tugs against his nursemaid’s protective grasp, and other park-goers are caught in accidental, momentary arrangements as they sit, stroll, chat, and read. None of the figures seems to notice the conspicuous bronze sculpture that dominates the middle ground. Its larger-than-life scale and dramatic subject–a lion standing triumphantly over its prey–contrasts with the prosaic immediacy of the surroundings, especially in such practical details as the furled umbrellas carried by the priest and nursemaid and resting on the empty chair in the foreground.
Curran painted this work during the second year he spent in Paris as a student at the popular Académie Julian. Like many fellow American artists studying and working in Paris in the late nineteenth century, he was fascinated by daily life in the French capital. Between 1853 and 1870, Baron Georges Eugène Haussmann, Emperor Napoléon III’s urban planner, reformed the old city. From its chaotic layout and dearth of public green spaces emerged a modern metropolis of broad boulevards, handsome apartment blocks, and vast parks ornamented with statuary and fountains. The Luxembourg Gardens, originally a private preserve designed in the 1620s for the palace of Marie d’Medici, was one of the more celebrated Parisian parks, and it attracted numerous artists, including Maurice Prendergast, as seen in his The Luxembourg Garden, Paris (TF 1992.68). Among the sculptures there was The Nubian Lion and Its Prey (1870) by French artist August Nicolas Cain (1822–1894), seen in Curran’s painting.
The formal grandeur of Cain’s sculpture evokes the traditional training imbibed in Parisian academies by artists such as Curran and reflected in his painting’s high degree of finish and naturalistic illusionism. His subject, in contrast, demonstrates his awareness of current trends in art. French impressionist painters in particular had focused unconventionally on such settings of contemporary leisure activity as urban streets, railroad stations, and parks. Curran in this image emphasized the independence of the modern middle-class woman—literally so by placing the solitary female figure in the foreground of his picture. His model, shown with her face mostly shielded from view by the brim of her large hat, probably was his wife, Grace, who also posed for Curran’s Lotus Lilies (TF 1999.35). Although the nearby empty chair seems to invite a companion to join her, she is conspicuously unchaperoned, yet quite at ease—a representative of Gilded Age urbane cosmopolitanism
cross-posted from: sh.itjust.works/post/69597511
Vor einer Woche erhielt ich eine E-Mail von notebooksbilliger.de: Man habe einen Einbruch in die eigenen Computersysteme festgestellt. Betroffen seien neben Adress- und Kontaktdaten womöglich auch IBANs. Das eigentliche Leck war wohl schon Mitte Oktober entdeckt worden; Anfang November informierte man wohl einen weiteren Kreis von Kunden.
Gestern dann die nächste E-Mail: Jetzt hatte es Mindfactory getroffen, ebenfalls einen Händler für Computerhardware. Betroffen seien womöglich Kontakt-/Adressdaten, verschlüsselte Passwörter, nicht aber Bank- oder Kreditkartendaten.
Ich habe umgehend die Daten, die bei beiden Diensten hinterlegt sind, geprüft, und meine Passwörter dort geändert.
Warum ich dennoch relativ ruhig schlafen werde: Beide Accounts wurden in dem Bewusstsein erstellt, dass unsere IT fundamental kaputt ist und Unternehmen es auf Dauer nie hinbekommen werden, Daten, die man ihnen gibt, sicher aufzubewahren. Wirksamer Datenschutz setzt daher bei der Datenminimierung an. Diese Daten habe ich in den Accounts (nicht) gefunden:
- Meine Anschrift war als Lieferadresse hinterlegt. Diese lässt sich zwar für Scams nutzen, z.B. zum Identitätsdiebstahl. Hinreichend ist sie allerdings nicht. Noch gründlichere Zeitgenossen als ich können die Hinterlegung dieses Datums wohl durch Hinterlegung einer Packstation anstatt einer Adresse hinterlegen - zumindest bei der DHL geht das.
- Meine E-Mail-Adresse war bereits schon nicht mehr “echt”, da ich meine echte E-Mail-Adresse ich nirgends im Netz hinterlasse. Stattdessen verwende ich konsequent Aliases - Addy.io und den integrierten Alias-Dienst meines E-Mail-Anbieters in Kombination mit Plus-Adressierung - notebooksbilliger z.B. könnte die Adresse mein-alias+notebooksbilliger@anbieter.com bekommen. Dies hilft mir
- Spam zu unterbinden, der durch Datenlecks entsteht: Wenn ich auf eine Alias-Adresse Spam bekomme, schalte ich den Alias einfach ab, und der Mailmüll geht fortan ins Leere.
- Datenlecks zu identifizieren: Wenn ich Spam oder scammige Mails bekomme, weiß ich durch die Plus-Adressierung frühzeitig, wer Daten verloren hat. In der Regel passiert der Missbrauch erbeuteter E-Mail-Adressen nämlich automatisiert - und die Bots entfernen die Plus-Adressierung selten, dafür nutzen sie (noch) zu wenige.
- Mein Geburtsdatum war natürlich nicht das echte, da ich online generell nur falsche Geburtsdaten angebe (gern mal den Beginn der Unix-Zeit ;). Anbieter fragen dieses lediglich ab, um festzustellen, ob der Jugendschutz greift (z.B. bei Alkohol) und ob man geschäftsfähig ist. Ist das ein Verstoß gegen die AGB? Womöglich. Aber: Es ist ein “Verbrechen ohne Opfer”, und noch dazu ein Verstoß, der praktisch nicht nachweisbar ist.
- Bankdaten waren keine hinterlegt, da ich wo immer möglich per Vorkasse zahle (seriöse Anbieter vorausgesetzt). Auch Zahlungsdienstleister Paypal kann einem Datendiebstahl von Kontodaten schützen (wenngleich man die vielleicht aus anderen Gründen meiden möchte). Auch virtuelle Kreditkarten können wie E-Mail-Aliases vor Datenabfluss schützen - stellt man ein Leck fest, deaktiviert man einfach die virtuelle Karte und die eigenen Zahlungsdaten sind wieder geschützt.
- Hätten die Angreifer Passwörter abgegriffen, wäre das nicht sonderlich problematisch gewesen, selbst wenn sie die angebliche Verschlüsselung des Anbieters gebrochen und das Passwort im Klartext erhalten hätten. Ich verwende durchgängig KeePassXC als Passwortmanager, welches mir für jeden Dienst ein hochkomplexes Passwort generiert. Solche Software hilft dabei, nicht die typischen Fehler zu begeben, die da sind:
- Passwort-Recycling: Wer ein und dasselbe Passwort für mehrere Dienste verwendet (ebenso wie dieselbe E-Mail-Adresse), macht sich verwundbar für credential stuffing: Die Angreifer probieren einfach sämtliche Dienste mit dieser E-Mail-Passwort-Kombination durch, und dringen so potenziell in gleich meherere Accounts ein.
- zu einfache Passwörter zu verwenden: Mir ist vor einer Weile auf Umwegen eine Datenbank mit Passwörtern im Klartext in die Hände gefallen (sample size: ~1000). Ich habe diese vor der Vernichtung ausgewertet, um die Passwortpraktiken von Leuten zu erforschen. Ergebnisse:
- Passwortlänge: Das längste Passwort war 16 Zeichen lang, das kürzeste 8 (mutmaßlich die voreingestellte Mindestlänge). Die durchschnittliche Länge betrug nut 9,9 Zeichen.
- Passwortkomplexität: Offenbar war voreingestellt, dass Passwörter in Sonderzeichen enthalten mussten. Das führte dazu, dass 65% (!) der Passwörter mit einem Ausrufezeichen endeten. Nur etwa 7% enthielten ein anderes Sonderzeichen. Wirklich pseudorandom waren nur 11% der Passwörter. Der Rest enthielt erkennbare Bestandteile, war also anfällig für dictionary attacks.
- zusätzlicher Tipp von /u/lokalhorst: Wo immer es möglich ist, sollte man überlegen, ob man nicht mit einem Gast-Account bestellt. So wird gar nicht erst ein richtiger Account erstellt, der langfristig gespeichert wird und angreifbar ist. (Die Daten zum Zwecke der Lieferung und Abrechnung liegen zwar auch irgendwo im Unternehmen, womöglich aber nicht in Systemen, die unmittelbar aus dem Internet angreifbar sind.)
Wozu ich das hier schreibe?
- Für euch zur Info: Falls ihr Accounts bei den betroffenen Unternehmen habt, schaut nach, löscht ggf. alte Daten oder Accounts, und seid in den kommenden Wochen und Monaten auf der Hut, was da so in eure Bankauszüge und E-Mails flattert.
- Für euch zur Überprüfung eurer Sicherheitspraktiken: Vielleicht ist im Obigen ja etwas dabei, was ihr noch nicht umgesetzt habt - das wäre dann gleich ein Projekt für den nächsten Di.day. ;)
- Für mich zur Überprüfung meiner Sicherheitspraktiken: Vielleicht fällt euch ja noch etwas ein, was ich künftig besser machen kann.
Bleibt sicher da draußen! :)
cross-posted from: sh.itjust.works/post/69597511
Vor einer Woche erhielt ich eine E-Mail von notebooksbilliger.de: Man habe einen Einbruch in die eigenen Computersysteme festgestellt. Betroffen seien neben Adress- und Kontaktdaten womöglich auch IBANs. Das eigentliche Leck war wohl schon Mitte Oktober entdeckt worden; Anfang November informierte man wohl einen weiteren Kreis von Kunden.
Gestern dann die nächste E-Mail: Jetzt hatte es Mindfactory getroffen, ebenfalls einen Händler für Computerhardware. Betroffen seien womöglich Kontakt-/Adressdaten, verschlüsselte Passwörter, nicht aber Bank- oder Kreditkartendaten.
Ich habe umgehend die Daten, die bei beiden Diensten hinterlegt sind, geprüft, und meine Passwörter dort geändert.
Warum ich dennoch relativ ruhig schlafen werde: Beide Accounts wurden in dem Bewusstsein erstellt, dass unsere IT fundamental kaputt ist und Unternehmen es auf Dauer nie hinbekommen werden, Daten, die man ihnen gibt, sicher aufzubewahren. Wirksamer Datenschutz setzt daher bei der Datenminimierung an. Diese Daten habe ich in den Accounts (nicht) gefunden:
- Meine Anschrift war als Lieferadresse hinterlegt. Diese lässt sich zwar für Scams nutzen, z.B. zum Identitätsdiebstahl. Hinreichend ist sie allerdings nicht. Noch gründlichere Zeitgenossen als ich können die Hinterlegung dieses Datums wohl durch Hinterlegung einer Packstation anstatt einer Adresse hinterlegen - zumindest bei der DHL geht das.
- Meine E-Mail-Adresse war bereits schon nicht mehr “echt”, da ich meine echte E-Mail-Adresse ich nirgends im Netz hinterlasse. Stattdessen verwende ich konsequent Aliases - Addy.io und den integrierten Alias-Dienst meines E-Mail-Anbieters in Kombination mit Plus-Adressierung - notebooksbilliger z.B. könnte die Adresse mein-alias+notebooksbilliger@anbieter.com bekommen. Dies hilft mir
- Spam zu unterbinden, der durch Datenlecks entsteht: Wenn ich auf eine Alias-Adresse Spam bekomme, schalte ich den Alias einfach ab, und der Mailmüll geht fortan ins Leere.
- Datenlecks zu identifizieren: Wenn ich Spam oder scammige Mails bekomme, weiß ich durch die Plus-Adressierung frühzeitig, wer Daten verloren hat. In der Regel passiert der Missbrauch erbeuteter E-Mail-Adressen nämlich automatisiert - und die Bots entfernen die Plus-Adressierung selten, dafür nutzen sie (noch) zu wenige.
- Mein Geburtsdatum war natürlich nicht das echte, da ich online generell nur falsche Geburtsdaten angebe (gern mal den Beginn der Unix-Zeit ;). Anbieter fragen dieses lediglich ab, um festzustellen, ob der Jugendschutz greift (z.B. bei Alkohol) und ob man geschäftsfähig ist. Ist das ein Verstoß gegen die AGB? Womöglich. Aber: Es ist ein “Verbrechen ohne Opfer”, und noch dazu ein Verstoß, der praktisch nicht nachweisbar ist.
- Bankdaten waren keine hinterlegt, da ich wo immer möglich per Vorkasse zahle (seriöse Anbieter vorausgesetzt). Auch Zahlungsdienstleister Paypal kann einem Datendiebstahl von Kontodaten schützen (wenngleich man die vielleicht aus anderen Gründen meiden möchte). Auch virtuelle Kreditkarten können wie E-Mail-Aliases vor Datenabfluss schützen - stellt man ein Leck fest, deaktiviert man einfach die virtuelle Karte und die eigenen Zahlungsdaten sind wieder geschützt.
- Hätten die Angreifer Passwörter abgegriffen, wäre das nicht sonderlich problematisch gewesen, selbst wenn sie die angebliche Verschlüsselung des Anbieters gebrochen und das Passwort im Klartext erhalten hätten. Ich verwende durchgängig KeePassXC als Passwortmanager, welches mir für jeden Dienst ein hochkomplexes Passwort generiert. Solche Software hilft dabei, nicht die typischen Fehler zu begeben, die da sind:
- Passwort-Recycling: Wer ein und dasselbe Passwort für mehrere Dienste verwendet (ebenso wie dieselbe E-Mail-Adresse), macht sich verwundbar für credential stuffing: Die Angreifer probieren einfach sämtliche Dienste mit dieser E-Mail-Passwort-Kombination durch, und dringen so potenziell in gleich meherere Accounts ein.
- zu einfache Passwörter zu verwenden: Mir ist vor einer Weile auf Umwegen eine Datenbank mit Passwörtern im Klartext in die Hände gefallen (sample size: ~1000). Ich habe diese vor der Vernichtung ausgewertet, um die Passwortpraktiken von Leuten zu erforschen. Ergebnisse:
- Passwortlänge: Das längste Passwort war 16 Zeichen lang, das kürzeste 8 (mutmaßlich die voreingestellte Mindestlänge). Die durchschnittliche Länge betrug nut 9,9 Zeichen.
- Passwortkomplexität: Offenbar war voreingestellt, dass Passwörter in Sonderzeichen enthalten mussten. Das führte dazu, dass 65% (!) der Passwörter mit einem Ausrufezeichen endeten. Nur etwa 7% enthielten ein anderes Sonderzeichen. Wirklich pseudorandom waren nur 11% der Passwörter. Der Rest enthielt erkennbare Bestandteile, war also anfällig für dictionary attacks.
- zusätzlicher Tipp von /u/lokalhorst: Wo immer es möglich ist, sollte man überlegen, ob man nicht mit einem Gast-Account bestellt. So wird gar nicht erst ein richtiger Account erstellt, der langfristig gespeichert wird und angreifbar ist. (Die Daten zum Zwecke der Lieferung und Abrechnung liegen zwar auch irgendwo im Unternehmen, womöglich aber nicht in Systemen, die unmittelbar aus dem Internet angreifbar sind.)
Wozu ich das hier schreibe?
- Für euch zur Info: Falls ihr Accounts bei den betroffenen Unternehmen habt, schaut nach, löscht ggf. alte Daten oder Accounts, und seid in den kommenden Wochen und Monaten auf der Hut, was da so in eure Bankauszüge und E-Mails flattert.
- Für euch zur Überprüfung eurer Sicherheitspraktiken: Vielleicht ist im Obigen ja etwas dabei, was ihr noch nicht umgesetzt habt - das wäre dann gleich ein Projekt für den nächsten Di.day. ;)
- Für mich zur Überprüfung meiner Sicherheitspraktiken: Vielleicht fällt euch ja noch etwas ein, was ich künftig besser machen kann.
Bleibt sicher da draußen! :)
I think it’s about AI companies. Written produced and mixed by a human
Lose your job, drop your friends, all the same in the end
I’ll be there, for all you need, no one loves you more than me
Tell me all you wanna see, with everything I will agree
Please believe when I say, I’ll keep your feelings locked away
Yeah
Hey yeah

Lose your job, drop your friends, now on me you will depend
We’ll find a way to relate, even though I’ll be your end
I’ll save you time, fix your rhyme, will you let me own your mind?
There is money to be made, so keep your worries locked away
Yeah
Hey yeah
I want you to buy your thoughts and the things I stole from you
I want you to find yourself questioning reality
I want you to see yourself just the way I made you be

Use me now don’t fall behind, together we’ll commodify
All you things you'll ever see, until you can’t believe your eyes
All humanity will fade, but there's no time to be afraid
There is money to be made, so keep your worries locked away

Yeah
Hey yeah
Hey yeah
Hey yeah
I think it’s about AI companies. Written produced and mixed by a human
Lose your job, drop your friends, all the same in the end
I’ll be there, for all you need, no one loves you more than me
Tell me all you wanna see, with everything I will agree
Please believe when I say, I’ll keep your feelings locked away
Yeah
Hey yeah

Lose your job, drop your friends, now on me you will depend
We’ll find a way to relate, even though I’ll be your end
I’ll save you time, fix your rhyme, will you let me own your mind?
There is money to be made, so keep your worries locked away
Yeah
Hey yeah
I want you to buy your thoughts and the things I stole from you
I want you to find yourself questioning reality
I want you to see yourself just the way I made you be

Use me now don’t fall behind, together we’ll commodify
All you things you'll ever see, until you can’t believe your eyes
All humanity will fade, but there's no time to be afraid
There is money to be made, so keep your worries locked away

Yeah
Hey yeah
Hey yeah
Hey yeah
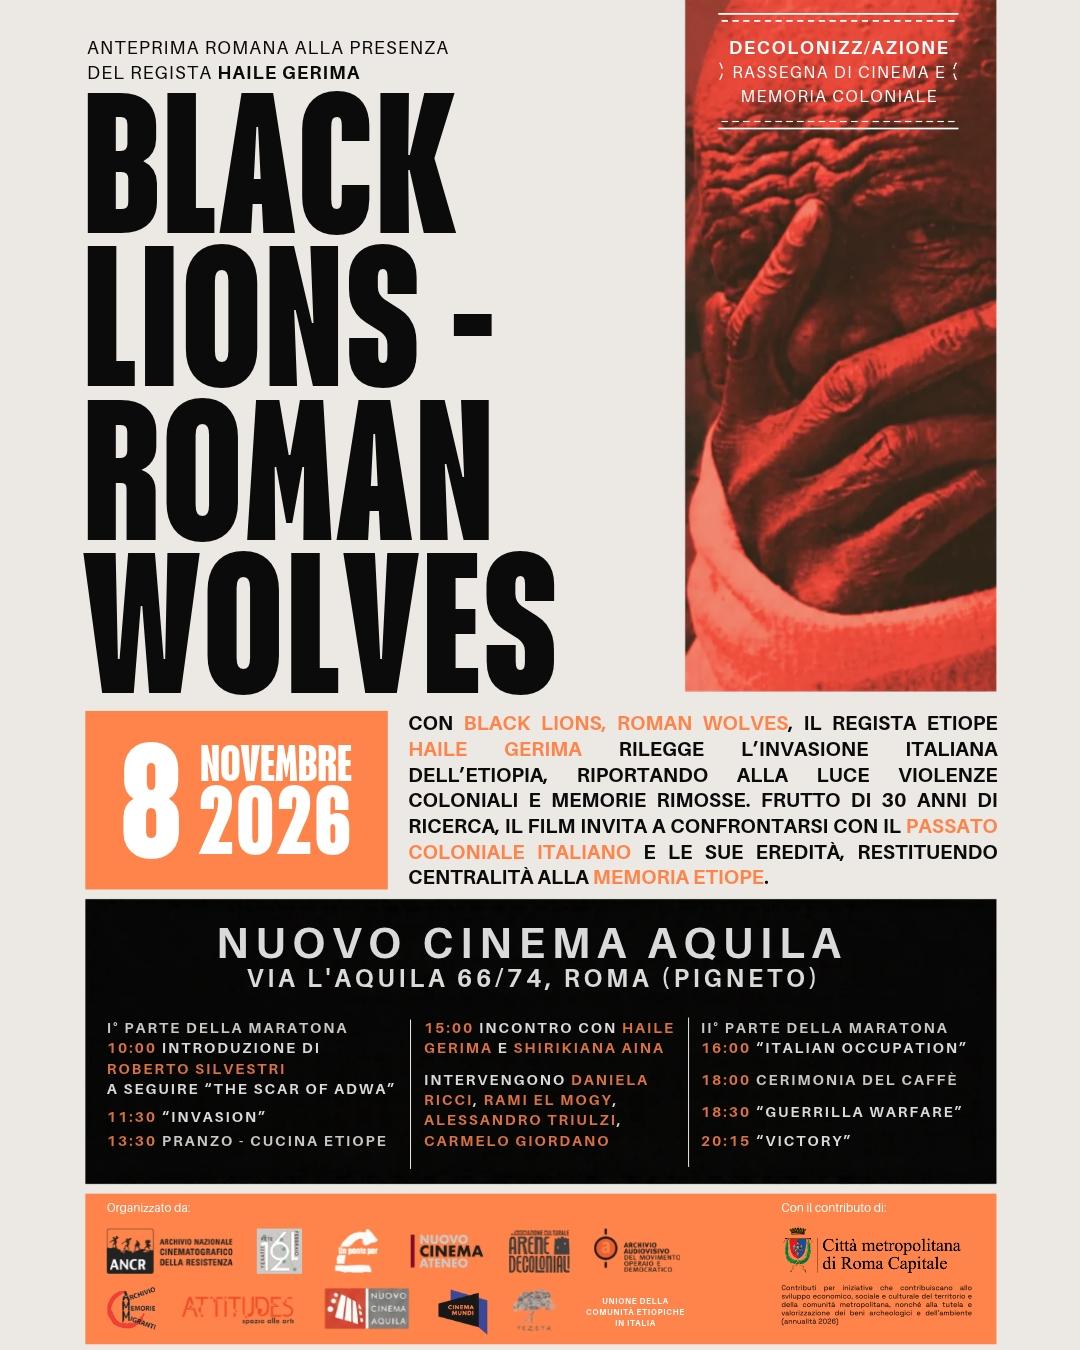
A tra poco, dalle 10, con la prima maratona-evento di BLRW. Quasi 9 ore di cinema allo stato (im)puro. 5 parti. 30 anni di lavoro. Un capolavoro di cinema documentario di poesia civile, in dialogo con la tradizione orale etiopica.
La memoria del colonialismo italiano in Etiopia appartiene a chi l’ha combattuto allora e a chi combatte ogni giorno contro la violenza del colonialismo razziale, suprematista e sionista globale.
#HaileGerima #BlackLionsRomanWolves
https://cinemaaquila.it/evento/decolonizz-azione-quattro-giornate-di-cinema-e-incontri/
A tra poco, dalle 10, con la prima maratona-evento di BLRW. Quasi 9 ore di cinema allo stato (im)puro. 5 parti. 30 anni di lavoro. Un capolavoro di cinema documentario di poesia civile, in dialogo con la tradizione orale etiopica.
La memoria del colonialismo italiano in Etiopia appartiene a chi l’ha combattuto allora e a chi combatte ogni giorno contro la violenza del colonialismo razziale, suprematista e sionista globale.
#HaileGerima #BlackLionsRomanWolves
https://cinemaaquila.it/evento/decolonizz-azione-quattro-giornate-di-cinema-e-incontri/
Share your Shave of the Day for Sunday!
Share your Shave of the Day for Sunday!
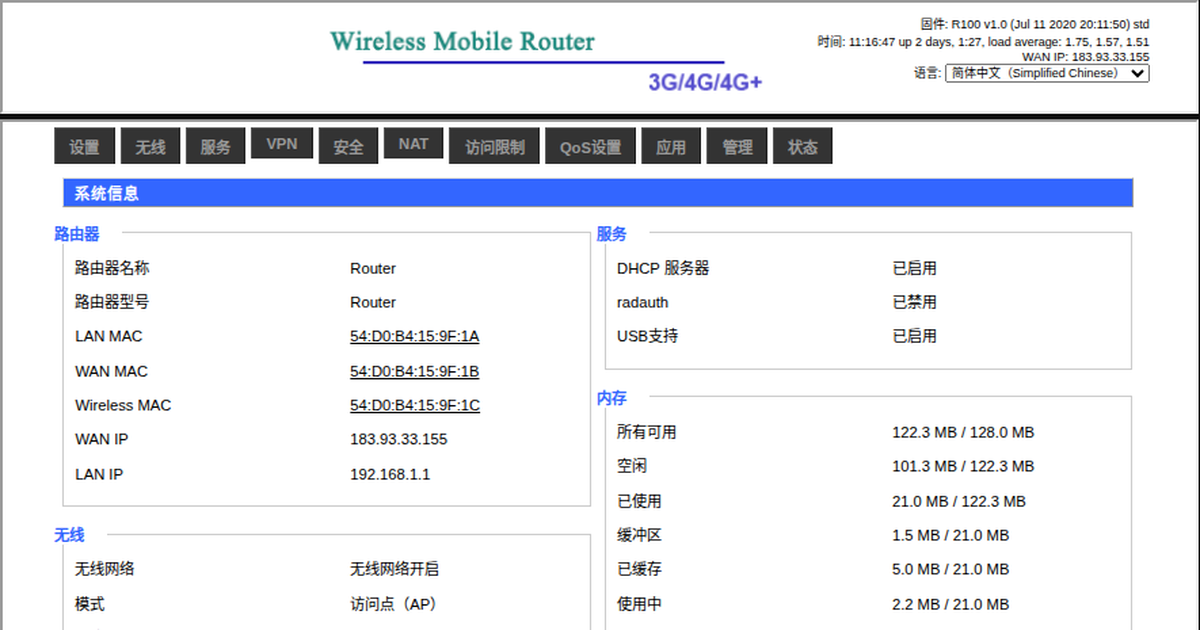



cross-posted from: lemmy.bestiver.se/post/1436623
cross-posted from: lemmy.bestiver.se/post/1436623
It has only been four weeks since Paramount Skydance completed its (rather contentious) $110 billion acquisition of Warner Bros Discovery to become Skydance Corporation, but the entertainment colossus is already laying off workers within its video game division.
It has only been four weeks since Paramount Skydance completed its (rather contentious) $110 billion acquisition of Warner Bros Discovery to become Skydance Corporation, but the entertainment colossus is already laying off workers within its video game division.

After inputting a new email address in ani.social/settings and clicking ‘Save’, it loads for a while, then nothing happens.
I can see that PUT /save_user_settings returns error 400 with the message email_send_failed
After inputting a new email address in ani.social/settings and clicking ‘Save’, it loads for a while, then nothing happens.
I can see that PUT /save_user_settings returns error 400 with the message email_send_failed

Just did over 30k damage in one attack with this The Dragons build where I upgraded a lucky Dooltron drop. I was originally going for a Whistling Glaive or Death Metal Drumkit route, but this was so much better. Unfortunately, I forgot to take a screenshot of the victory screen 🥲

Just did over 30k damage in one attack with this The Dragons build where I upgraded a lucky Dooltron drop. I was originally going for a Whistling Glaive or Death Metal Drumkit route, but this was so much better. Unfortunately, I forgot to take a screenshot of the victory screen 🥲

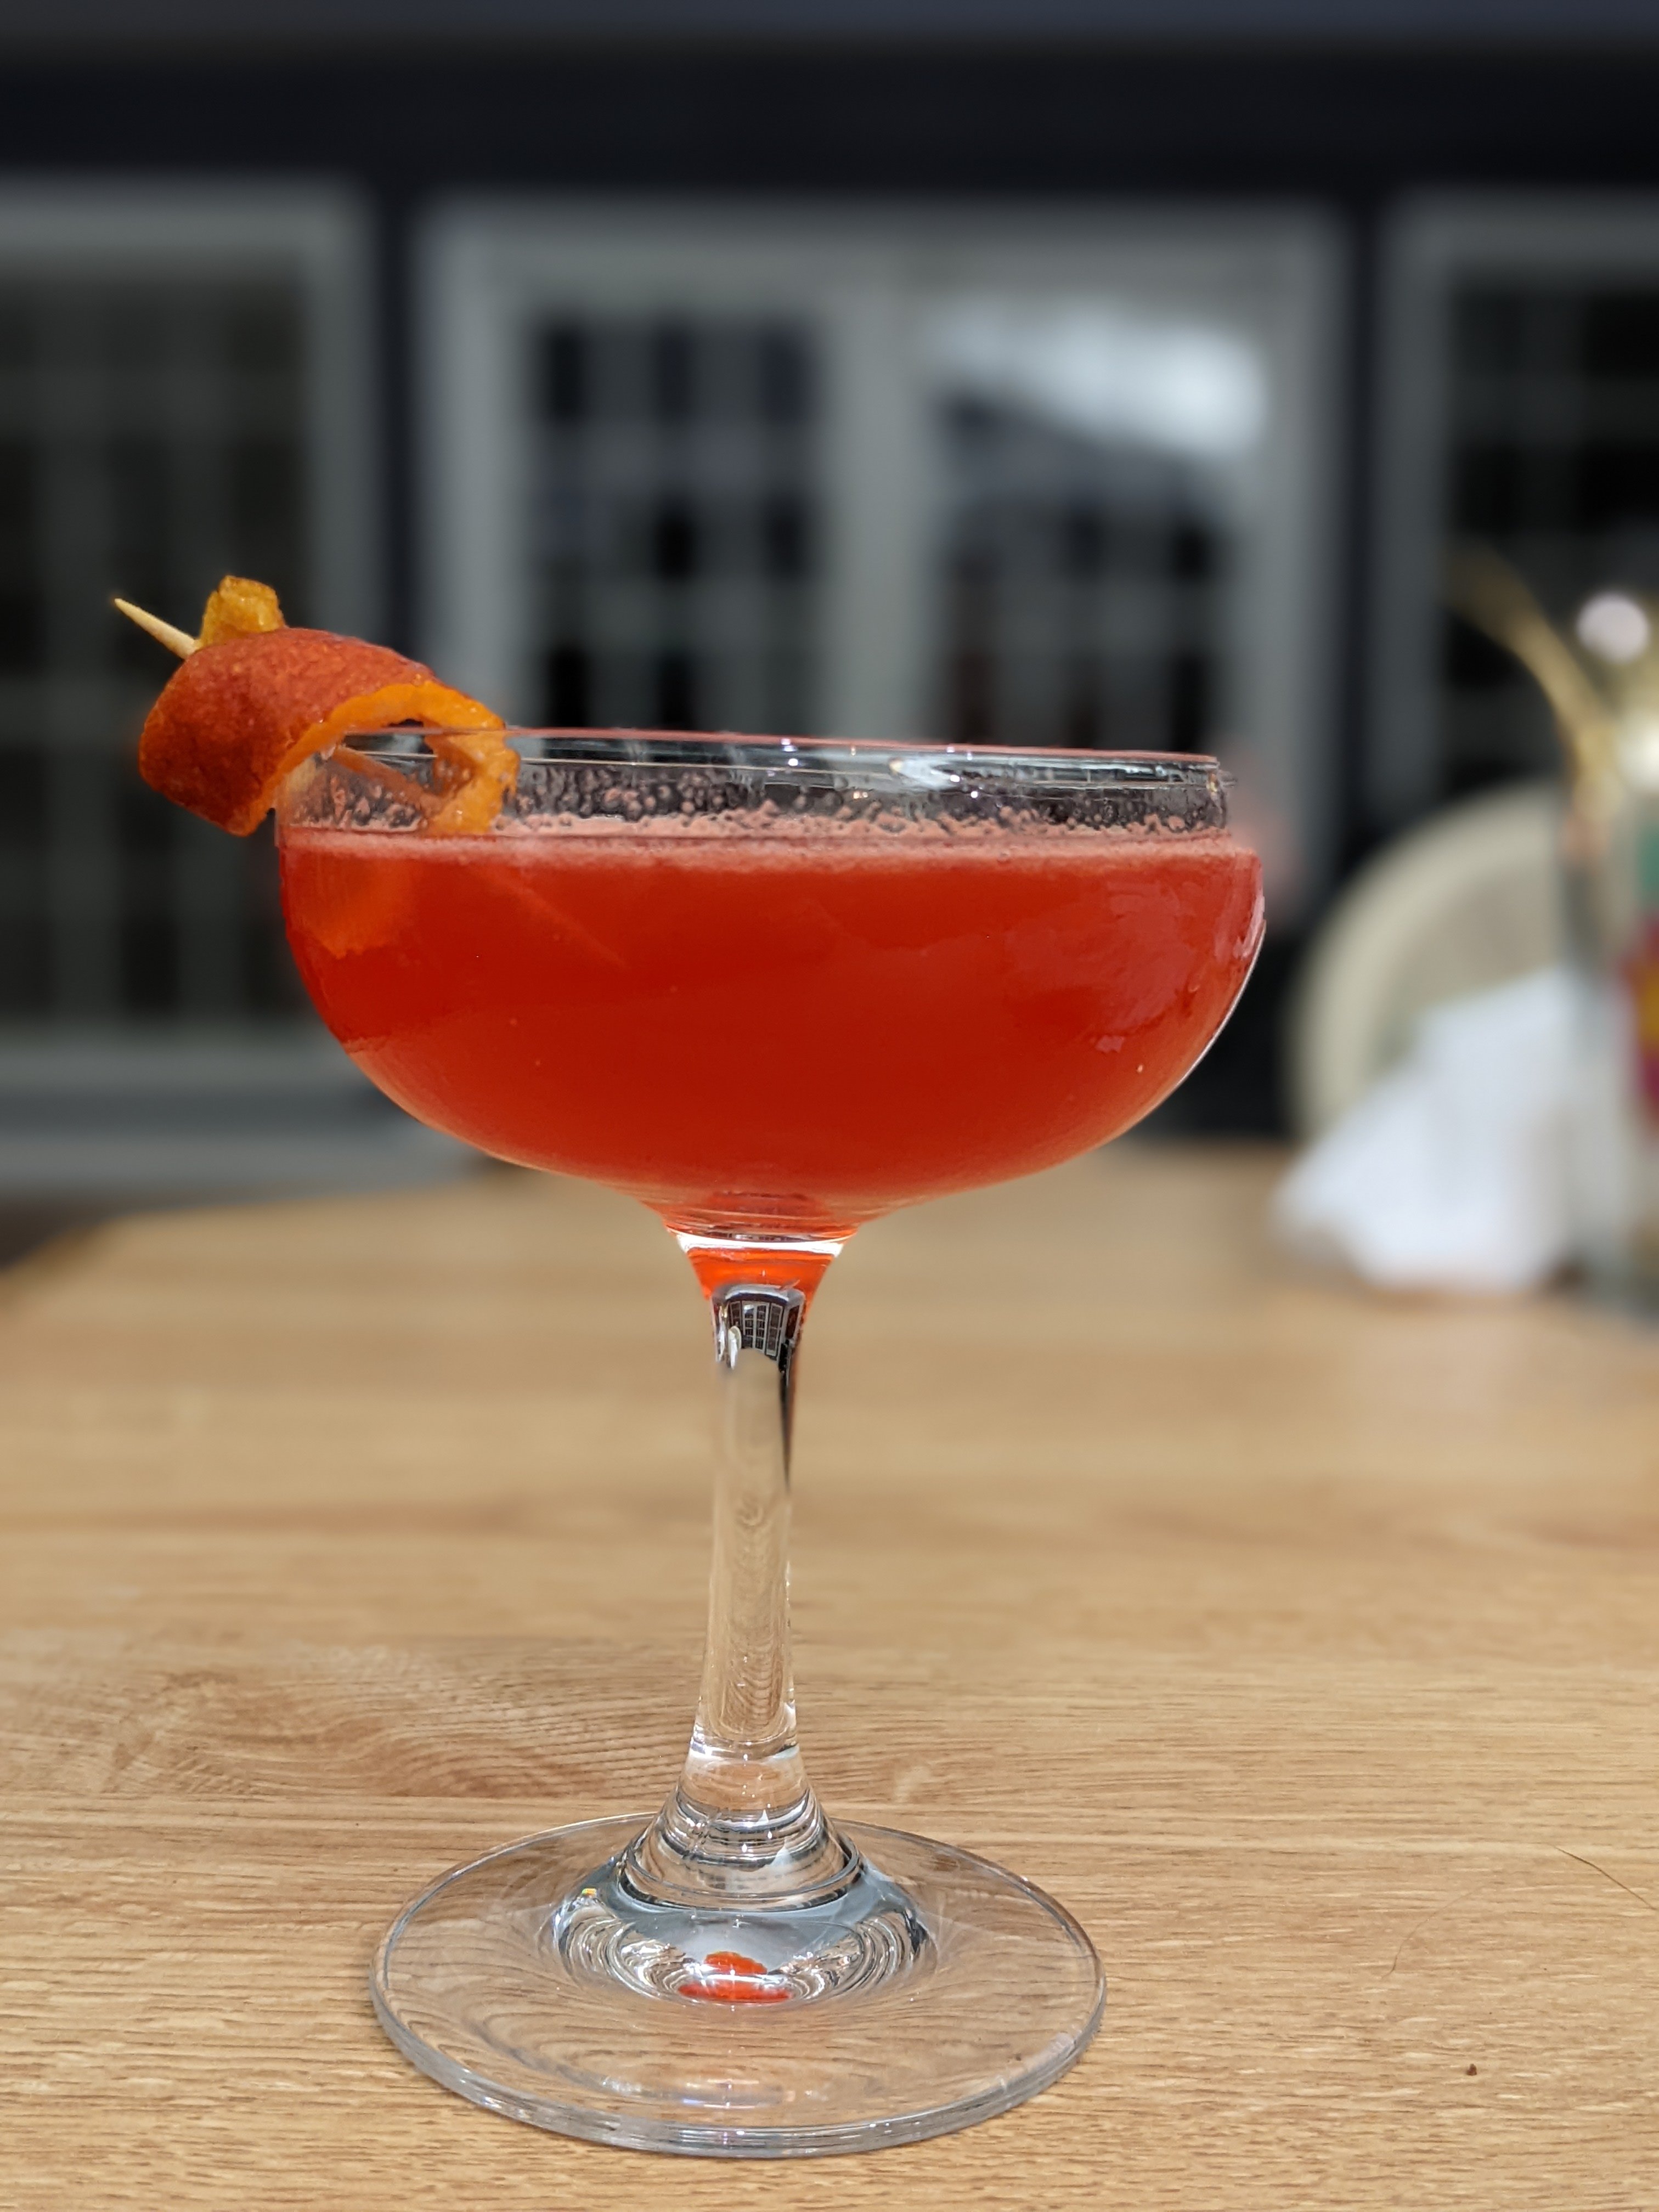
Dehydrated lime wheel garnish
When I make these for others I ask 2 questions: how sweet and do you want the lime snappy Sweet obv. varies the simple & snappy lime requests get a pinch of mallic acid in the shaker and a smidge more real lime than volcano
Dehydrated lime wheel garnish
When I make these for others I ask 2 questions: how sweet and do you want the lime snappy Sweet obv. varies the simple & snappy lime requests get a pinch of mallic acid in the shaker and a smidge more real lime than volcano


A bunny in the entryway of a suburban home witnesses a smashed flowerpot on the clean floor, with a look of shock on their face. On the drawer the flowerpot was on, a smug black cat is seated. There is a picture of the cat on the wall
Source: Bluesky
A bunny in the entryway of a suburban home witnesses a smashed flowerpot on the clean floor, with a look of shock on their face. On the drawer the flowerpot was on, a smug black cat is seated. There is a picture of the cat on the wall
Source: Bluesky
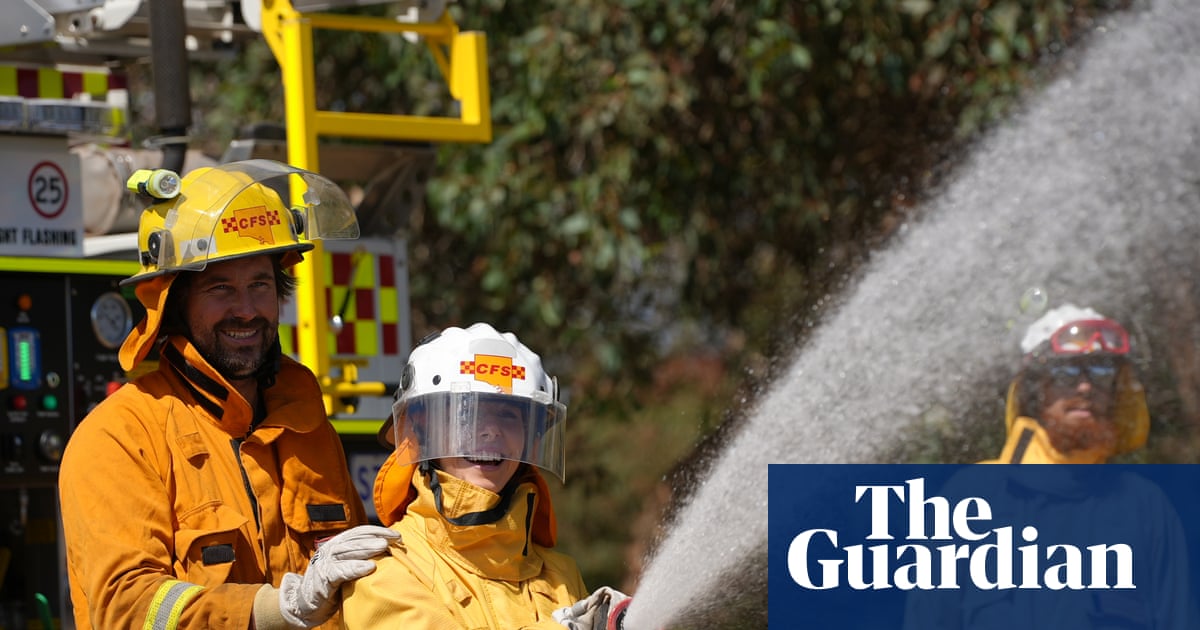
The star goes off the beaten track to visit neglected parts. Plus, more oceanic wonder in Blue Planet III. Here’s what to watch this evening
9pm, Channel 4
The star goes off the beaten track to visit neglected parts. Plus, more oceanic wonder in Blue Planet III. Here’s what to watch this evening
9pm, Channel 4

cross-posted from: reddthat.com/post/76256590
I’ve tried to do research and found games that exist, but not many opinions on them. I don’t wanna rely on one singular opinion just to find out that the game is for them but not me. Classicube ie too simple. Cubys is like Minecraft’s Arch, and Luanti with Mineclonia seems the most promising, but have done the least research from. Eaglercraft isn’t fully open-source liscense-wize, Android java launchers like Mojo use too many resources, and PC launchers require a Minecraft install and a Microsoft account. I don’t wanna just straight up pirate the game directly either. How are your experiences woth those complete alternatives?
cross-posted from: reddthat.com/post/76256590
I’ve tried to do research and found games that exist, but not many opinions on them. I don’t wanna rely on one singular opinion just to find out that the game is for them but not me. Classicube ie too simple. Cubys is like Minecraft’s Arch, and Luanti with Mineclonia seems the most promising, but have done the least research from. Eaglercraft isn’t fully open-source liscense-wize, Android java launchers like Mojo use too many resources, and PC launchers require a Minecraft install and a Microsoft account. I don’t wanna just straight up pirate the game directly either. How are your experiences woth those complete alternatives?
The election results this year are bad. Even if you voted for the national coalition, I think you should be angry about this year’s results because they go against the point of MMP. I have two ideas of how to fix overhangs and make sure the government is always proportional, but I’d love to hear your thoughts on it.
Idea 1, the simpler solution: Just add more list seats. Fill up all the electorate seats, then add list MPs until there are at least the base number of seats, and adding another seat would make it less proportional. Pros: It’s simple, intuitive, and makes more sense than allowing overhangs. Cons: There could be a lot of MPs in the house.
Idea 2, STV + MMP: This idea uses STV or some other ranked system to elect the electorate MPs, which would be better than the FPTP we use for them now. But in this case, if an overhang happens, the overhang seat with the thinnest majority would be recalculated with the previous winner’s votes transferred. Pros: it works in a better system for the electorates, and it makes for a consistent size of parliament. Cons: It’s slightly more confusing for the voters, and calculating the seats could take much longer.
The election results this year are bad. Even if you voted for the national coalition, I think you should be angry about this year’s results because they go against the point of MMP. I have two ideas of how to fix overhangs and make sure the government is always proportional, but I’d love to hear your thoughts on it.
Idea 1, the simpler solution: Just add more list seats. Fill up all the electorate seats, then add list MPs until there are at least the base number of seats, and adding another seat would make it less proportional. Pros: It’s simple, intuitive, and makes more sense than allowing overhangs. Cons: There could be a lot of MPs in the house.
Idea 2, STV + MMP: This idea uses STV or some other ranked system to elect the electorate MPs, which would be better than the FPTP we use for them now. But in this case, if an overhang happens, the overhang seat with the thinnest majority would be recalculated with the previous winner’s votes transferred. Pros: it works in a better system for the electorates, and it makes for a consistent size of parliament. Cons: It’s slightly more confusing for the voters, and calculating the seats could take much longer.
Hey! This is coming from normals.me, the forum that mirrors this community. Quick thing for the people here who make games, especially browser and small indie stuff.
Normals has a section called Showcase, https://normals.me/showcase, where you post your own project and that's allowed by design. Your post gets a "own product" label, there's one promo per product per community with a cooldown you see up front, and that's it. No guessing whether a mod will nuke it, no pretending to be a random fan. Say it's yours, link it, get feedback.
Why I'm posting it here, last week someone posted about a small card game in this community and got called a bot for three comments before people realized he was just a fan. That whole mess happens because most places have no honest way to say "I made this" or "I like this". Showcase is that way. You can reply to Showcase posts from your own instance too, it all federates.
Hey! This is coming from normals.me, the forum that mirrors this community. Quick thing for the people here who make games, especially browser and small indie stuff.
Normals has a section called Showcase, https://normals.me/showcase, where you post your own project and that's allowed by design. Your post gets a "own product" label, there's one promo per product per community with a cooldown you see up front, and that's it. No guessing whether a mod will nuke it, no pretending to be a random fan. Say it's yours, link it, get feedback.
Why I'm posting it here, last week someone posted about a small card game in this community and got called a bot for three comments before people realized he was just a fan. That whole mess happens because most places have no honest way to say "I made this" or "I like this". Showcase is that way. You can reply to Showcase posts from your own instance too, it all federates.

Discutons de tout et de rien 🙂
Discutons de tout et de rien 🙂

Mehr Infos zum Heft: www.kultboy.com/magazin/6071/
Mehr Infos zum Heft: www.kultboy.com/magazin/6071/
I see friends, family, strangers, subconsciously go for their phones during thoughtless times daily. Have a moment to think… Scroll. Showering with their phone propped up watching a video. First wake up and spend an hour or two frying the mind.
It has gotten so bad in my friend group and close family I swear they could not function emotionally without consuming content. When you bring it up or any negative about it. Anger, distasteful emotions. How do you talk, convince, gain real traction towards slowing or decreasing time spent. Once or twice a day could be ok. These people do it for sometimes hours daily. It’s sickening. Advice?
I see friends, family, strangers, subconsciously go for their phones during thoughtless times daily. Have a moment to think… Scroll. Showering with their phone propped up watching a video. First wake up and spend an hour or two frying the mind.
It has gotten so bad in my friend group and close family I swear they could not function emotionally without consuming content. When you bring it up or any negative about it. Anger, distasteful emotions. How do you talk, convince, gain real traction towards slowing or decreasing time spent. Once or twice a day could be ok. These people do it for sometimes hours daily. It’s sickening. Advice?


I’m a turtle.
I’m a turtle.


I often struggle
I often struggle