OpenAI agent 'infiltrated' Australian government website, PM says

OpenAI agent 'infiltrated' Australian government website, PM says
cross-posted from: lemmy.dbzer0.com/post/75932280
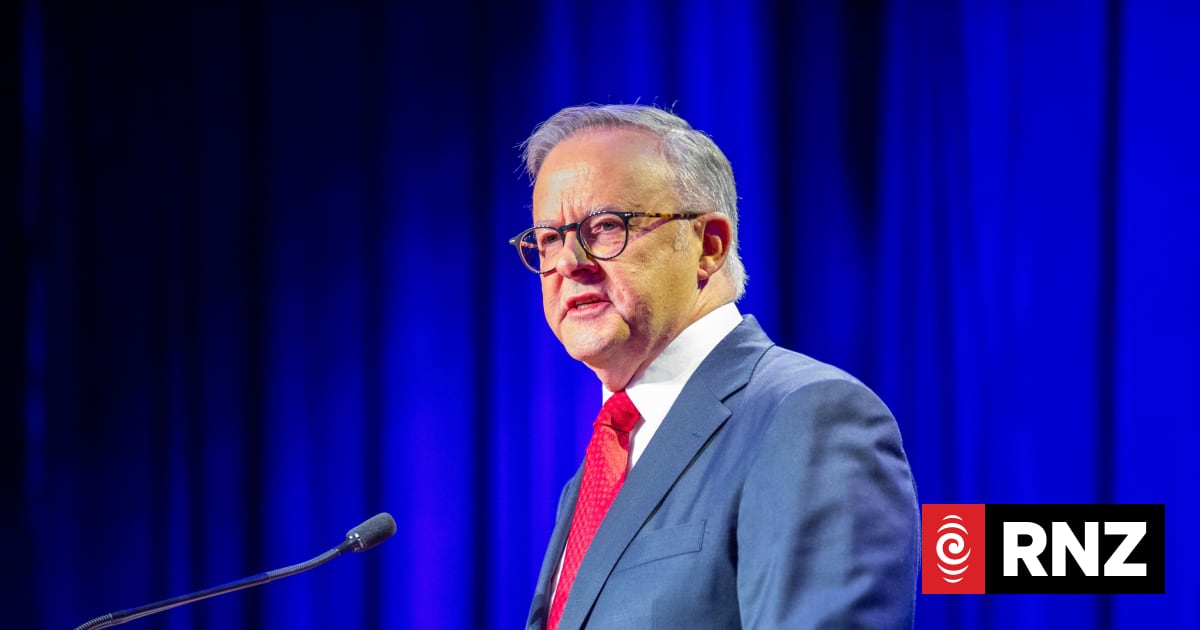
Prime Minister Anthony Albanese has revealed an AI agent hacked into an Australian Medicare data portal earlier this year.
Speaking in New York, Mr Albanese said the Open AI agent gained unauthorised access to the Medicare statistics reporting service portal administered by Services Australia.
The AI agent accessed both public and non-public files.
The agent was conducting research into public medical spending when it found a way to break through privacy protections.
Mr Albanese said it took three months for OpenAI to admit the breach, which he said was unacceptable.
“Today I spoke with the CEO of OpenAI, Sam Altman, to express Australia’s extreme concern about this incident,” he said.
"And I also expressed my disappointment that it took the company way too long to inform the government what had occurred.
“The nature of the way that the notification occurred as well was unacceptable.”
He said there was no evidence any individual personal information had been accessed, but an investigation aided by the Australian Signals Directorate was now underway.

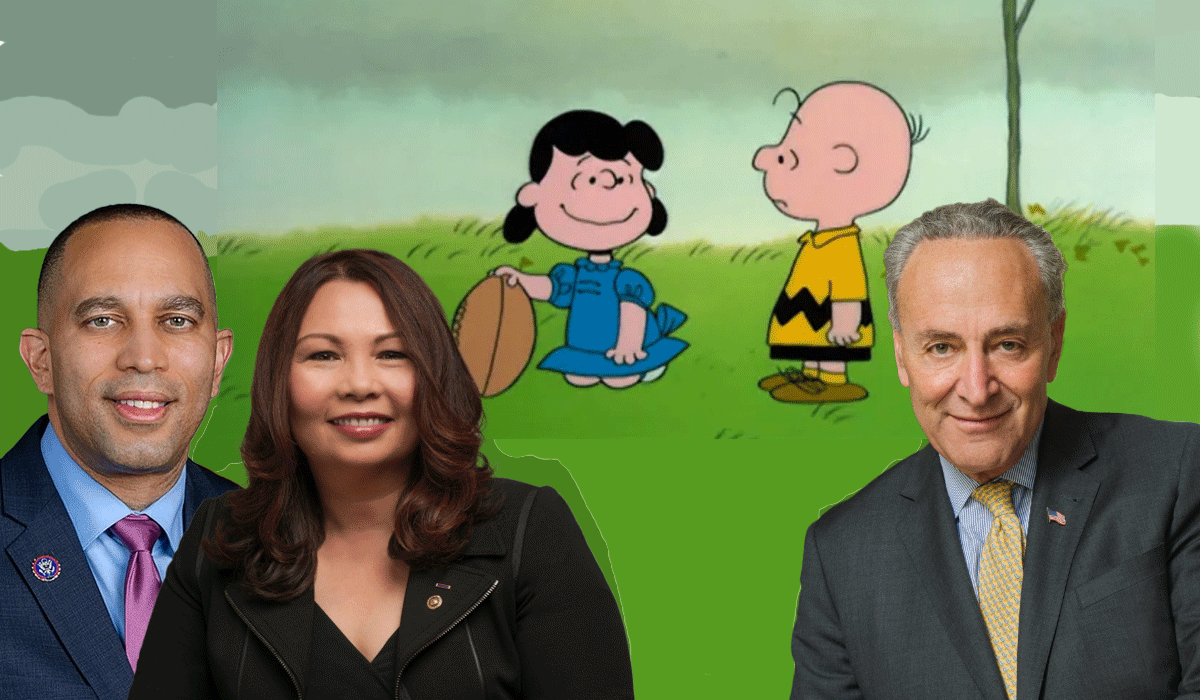
In the wake of another painful, difficult outcome, the Democratic Party has completed its review of Charlie Brown’s most recent failed attempt to kick the football.
It’s no surprise to us, but the findings are straightforward. While Charlie Brown did once again accelerate toward the ball, miss the ball entirely as Lucy pulled it away, flip backward through the air, and land violently with a disquieting crunch that slipped no less than three discs in his still-developing spine, we do not believe that now is the time for a dramatic change in kicking strategy.
To be clear: Charlie Brown must attempt to kick the football again.
We understand the frustration. Many children in the neighborhood, having seen Charlie Brown pull his crumpled, broken body up from yet another flailing flight through the cool seasonal air, yearn for him to try something new. Some suggest using a kicking tee. Others say Franklin should hold the ball. Peppermint Patty, in particular, vociferously argued that after several successive years of identical catastrophic results, it may be worth examining whether Lucy’s role in the kicking process has become counterproductive.
We respectfully disagree. The central lesson of this cycle is not that Charlie Brown should stop trusting Lucy. It is that Charlie Brown must do a better job explaining why trusting Lucy remains the responsible choice.


www.pixiv.net/en/artworks/138242197
^source of artwork I used for the edit.

ctrlprint
don’t want it to be an ad. Just a cool illustration.
Standard paper sizes are compared with a good boi.




cross-posted from: sh.itjust.works/post/67195538
Paris (France) (AFP) – Paris prosecutors said Tuesday they had opened several probes after receiving complaints concerning women filmed on the street without their consent using smart glasses.
Anyone wearing smart glasses can take photos, film videos, listen to music, make phone calls, translate text or interact with an AI assistant.
Meta’s smart spectacles, developed in partnership with Ray-Ban maker EssilorLuxottica, have become a commercial success. Meta sold seven million pairs in 2025. Other companies, including Google and Snap, are also preparing to roll out AI-powered glasses.
Calls have grown in Europe for action against what campaigners call “pervert” smart glasses after secretly filmed footage of girls and women has appeared online, with a petition in Britain demanding a ban on their sale.
In France, the e-Enfance association, which operates the national hotline for victims of online abuse, earlier this month sounded the alarm about videos recorded with camera-equipped glasses and shared online.
The Paris public prosecutor’s office said on Tuesday it had received “complaints relating to violations of privacy linked to the use of smart glasses”. Prosecutors did not say which brands were involved.
Prosecutors pointed to a “growing trend on social media involving women being filmed on the street with smart glasses without their consent and the videos being published online”.
Under French law, such an offence is punishable by up to two years in prison and a 45,000-euro ($51,000) fine.
Prosecutors said that in some cases investigations had also been opened for sexual assault when “the acts are accompanied by non-consensual sexual contact”.
The Paris prosecutor’s office said its cybercrime division “tested smart glasses in September in order to identify the commission of other cybercrime-related offences”.
Such offences could include the theft of a cryptocurrency wallet’s recovery phrase, enabling criminals to steal the funds.
…
Update is here: lemmy.zip/post/72142441
Hey guys, since I got into hosting my own servers, any electronic device I see I wonder - can it become a server?
This is probably not a crazy and new idea with android phones, but I had to share it with you. If you don’t know, there’s this thing called postmarket OS, full linux experience on an android phone.
Of course, not all phones are supported, but a phone like Galaxy Note 9 is a great candidate - it supports LAN over usb, postmarket OS fully supports it (the Exinos version) and setting up a phone as a selfhosted server has it’s real perks. Pis got really expensive, not to mention they don’t have a built-in UPS (phones have batteries), they use slow SD cards, while phones have faster UFS memory, phones draw way less power.
What do you guys think? I will for sure get a used Galaxy Note 9 and explore this idea, and if all goes well, I might even buy more of them and create a cluster.
waking up is hard
being siily is harder
maybe ill get pet


“DoNotSleep”
wakeLock.acquire() xD


The model examined play frequency, account balances, loss-to-wager ratios, and a separate estimate of whether a user was likely to stop gambling altogether, according to the Times. A higher score meant a customer was predicted to generate more revenue per promotional dollar spent.
Jayden Butts, a former DraftKings data analyst, described the underlying logic to the Times: “We are looking for traits and features that we can target that indicate a good investment.”
The best investment would be a problem gambler. (According to Jayden Butts, former DraftKings data analyst, to The New York Times)
DraftKings executives said data science and analytics improved promotion-driven sportsbook margins by 13% in 2025, and that AI helped personalize hundreds of millions of dollars in promotional spending, according to the Times.
A high profile hacking group claims it has breached multiple FBI-related services and stolen data “on all FBI employees and applicants.” A representative of the group, called ShinyHunters, told 404 Media the data includes FBI agents’ names, home addresses, phone number, and information on their spouse.
The data breach could be massively significant and may have all sorts of national security and counterintelligence implications. Criminals from the same ecosystem as ShinyHunters have previously used hacked data like phone records to track, intimidate, and harass the FBI agents investigating them. The highly sensitive data could also be a boon to foreign intelligence agencies who want to better understand how one of the most important law enforcement and intelligence agencies in the U.S. operates. And if the data fell into the hands of more criminals, FBI agents and their spouses could face serious threats to their safety.
“We hacked the FBI. We hold data on all FBI employees and applicants,” the representative of the group told 404 Media.
The representative provided 404 Media with a sample appearing to contain the personal data of 5,000 FBI employees. That data included an alleged address, phone number, date of birth, and in some cases details on their spouse.


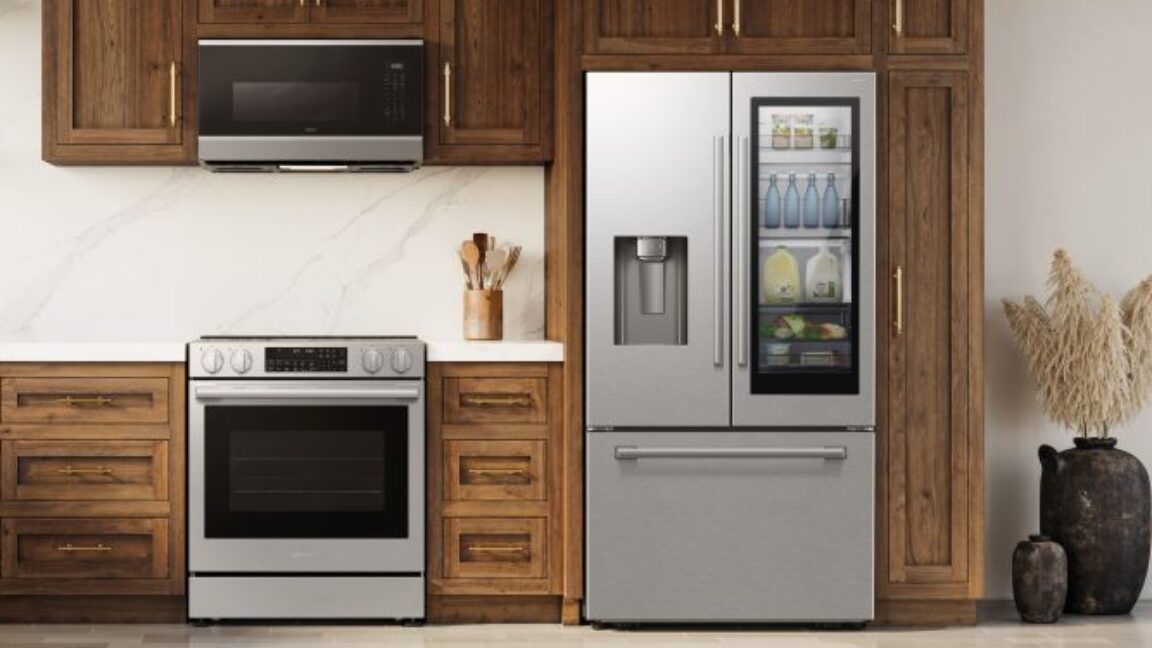
Some Samsung smart fridges stopped working on Tuesday due to a firmware update.
Korean outlets were the first to report the problems, which affect Samsung’s Bespoke AI line of fridges. Star News Korea, per a Google-provided translation, said that most of the affected devices were four-door fridges from 2024 or later.
Affected fridges “suddenly lost power and stopped functioning immediately after” trying to issue a firmware update through SmartThings, Samsung’s smart home platform, per Star News Korea. The SmartThings app then showed the devices as offline. Some users said that their fridge’s internal display was stuck showing the message “Checking SmartThings app during update.”
There are numerous reports on Samsung’s Korean community forum detailing the problem. Some users claim that they have owned their affected fridge for just a year or less.
“[T]he refrigeration and refrigeration functions themselves did not work normally, so all the food in the refrigerator had to be disposed of,” one user wrote, per a translation.

Tsuihou Sareta Tensei Juukishi wa Game Chishiki de Musou Suru, episode 13
Juukishi, Kesatria Kelas Berat Tereinkarnasi yang Diasingkan Jadi Tanpa Tanding Dengan Pengetahuan Gimnya, The Exiled Reincarnated Heavy Knight Is Unrivaled in Game Knowledge, เกิดใหม่เป็นอัศวินเกราะหนักผู้ถูกขับไล่แต่ใช้ความรู้จากเกมจนไร้เทียมทาน
- Info - AniList - Info - Kitsu - Info - MyAnimeList - Info - Official Site (Japanese) - Social - Twitter (Japanese) - Streaming - Bilibili TV - Streaming - Crunchyroll - Streaming - YouTube - Streaming - iQ
Reminder: Please do not discuss plot points not yet seen or skipped in the show. Failing to follow the rules may result in a ban.
All discussions
| Episode | Link |
|---|---|
| 1 | Link |
| 2 | Link |
| 3 | Link |
| 4 | Link |
| 5 | Link |
| 6 | Link |
| 7 | Link |
| 8 | Link |
| 9 | Link |
| 10 | Link |
| 11 | Link |
| 12 | Link |
| 13 | Link |
This post was created by a bot. Message the mod team for feedback and comments. The original source code can be found on GitHub.

cross-posted from: midwest.social/post/52397079
Google’s September 2026 Pixel Update Bulletin contains patches beyond what’s in that month’s regular Android Security Bulletin. According to GrapheneOS, some of those extra patches touch standard Android platform code, the kind that runs on non-Pixel devices, not just Pixel-branded hardware.
None of that platform-level code has reached the regular monthly bulletin or the private preview patches other manufacturers typically draw from to get their own patches ready.
And at this rate, these won’t reach non-Pixel OEMs at all until Android 17 QPR2 ships later this year in December.
The project is characterizing this as Google “gatekeeping security patches to the standard Android platform code from Android OEMs.” The complaints
GrapheneOS says Android 17 QPR1 shipped new developer APIs that never made it into AOSP. This is something they claim hasn’t happened since Android’s Honeycomb days.
Google’s API diff report backs this up. Comparing Android 17 to QPR1 shows one new package, android.hardware.hid, plus changes across sixteen others, including android.media, android.os, android.provider, android.telecom, and android.view.
GrapheneOS has ported its code to QPR1 before Google even released it, but still doesn’t have permission to ship that work. For now, the project is backporting Pixel firmware, kernel drivers, userspace drivers, and HALs from QPR1 onto Android 17 instead.
On top of all that, there’s a compliance issue that seems to be recurring.
Google was slow to comply with a GPL source request. GrapheneOS requested sources for a build (CD1A.260905.001.A1) on September 1, and access only came through more than two weeks later.
Why this is worrying
None of these three issues is catastrophic by itself. A three-month patch delay, a paused API rollout, a two-week wait on source code—each is the kind of thing that could pass as a one-off.
Taken together, however, they point to a recurring theme. Google is holding security fixes back from the wider Android ecosystem, withholding new APIs from AOSP for the first time in over a decade, and slow-walking GPL compliance it’s required to meet.
Don’t even get me started on what they are doing to the Android app ecosystem.
Google is on track to require every Android app developer, whether on the Play Store, F-Droid, or anywhere else, to register with them. Come 2027, that means handing over legal identification and signing key evidence before an app can run on any certified device.
Sideloading an unverified app following this would mean enabling developer settings, waiting through a mandatory 24-hour cooldown, and clicking past several warning screens (classic scare tactics, btw).
GrapheneOS is one of dozens of organizations that signed onto the Keep Android Open campaign opposing this, alongside F-Droid, the Electronic Frontier Foundation, and the Free Software Foundation.
If you ask me, this Big Tech company is doing what’s regrettably natural for it, clamping down open access to things so that its competition cannot benefit.


transcription: good girls dont get the group chat subpoenaed