Honestly with the level of incompetence in The White House, it could be anything. A streaming TV box, some sort of IoT device, a phone/tablet/PC, just about anything.
No place is too remote
The White House is not the only surprise in the observatory. Residential proxies also reach some of the most isolated places on the planet.
Saint Helena, Ascension and Tristan da Cunha is the South Atlantic territory that includes the most remote inhabited island in the world. We recorded 413 addresses and more than 32,000 observations there, split between Starlink and the island’s local internet provider, Sure Saint Helena.
We also recorded three observations from Antarctica. All of them come from a Cloudflare WARP address that points to McMurdo Station.
Svalbard: 1 Starlink address in Longyearbyen, 3 observations.
Also seen: the Falklands (388 addresses), the Chagos Islands (43), Tokelau (21) and South Georgia (7).
Residential proxies have infected every corner of the world, and it looks like there is no place they cannot reach. Layer3 Intel tracks residential proxy and anonymization infrastructure worldwide. Even when the proxies hide in networks on the farthest corners of the planet, we can still observe them, leaving threat actors no place to hide.
So, like, here I am, on my phone, playing games and browsing the internet. Sometimes my connection is a little slow, but that's just the nature of things because sometimes it just takes a tiny bit longer to get a response and sometimes my phone just runs a little slow.
What I don't know is that my phone is infected with malware. And that malware lets other people access whatever internet I have access to; and that whatever those other people are doing looks like it's coming from my IP address and my device. I am the unwitting exit node for an unscrupulous VPN service (or driving similar).
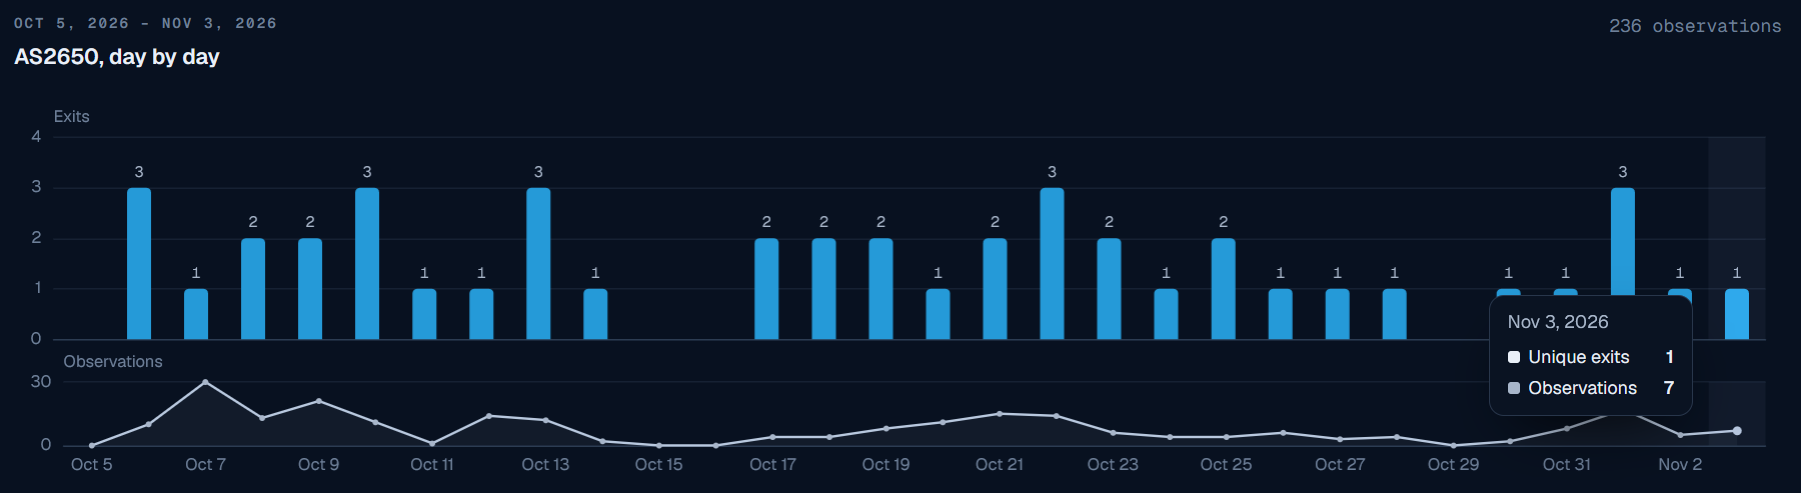
Someone working in the White House has an infected phone and doesn't know it. They are at the White House most days, work late afternoon to around midnight.
If the person in charge of the botnet knew the phone of a White House worked was compromised, they could use that access to appear as a legitimate user and bypass security protocols, have accounts and passwords compromised, and have their data scraped and stolen.
I would assume most normal people working in the White House have their phones regularly checked for malware, or use special phones for government work. However, higher ups in the Trump White House have routinely violated and ignored security protocols; they could abuse their power to use their own personal phones and to ignore security checks.
Given that the times the node was used are so consistent, I think it's unlikely that there are two infected phones involved.
Given that this happened on most days in October, it's unlikely to be Trump or anyone who regularly travels with him, because he spends a lot of time not at the White House. There was no exit node activity on two Thursdays, one Friday and one Monday; activity was recorded every other day in October. Meaning this isn't someone who comes into the office M-F with weekends off; days off seem to be somewhat rare for this person, and don't occur on normal weekends. I have no idea who the person is, but security should probably make more of an effort to re-secure all phones permitted on the premises.
However, higher ups in the Trump White House have routinely violated and ignored security protocols; they could abuse their power to use their own personal phones and to ignore security checks.
They’re so dumb that they probably just hired the hacker so hacking could be unnecessary.
A botnet implies a level of control over the compromised device, normally achieved through exploits. A residential proxy is done through taking advantage of technically naive users, rather than exploits (proxyware, sort of like spyware/adaware) and doesn’t aim to give control over the target device just over their internet connection. Botnets are run by individuals/hacking groups, and residential proxies are provided by “legitimate” businesses. In theory, they can both be used for the same purpose of DDOSing a target, but as most residential proxy resellers try and position themselves as legitimate, they are less likely to support a client that is using their service to DDOS people
‘Control over the device’ in botnets is practically also just the network. Bots are also created due to users being naive, like positioning iot devices open to the internet, running insecure stuff etc
The exploit route for RPs is also malicious, social engineering. Get stuff for free. Nobody is actually aware of what they are doing here.
I agree on the superficial legality. Like a share hoster deleting links in stead of content etc.
13 comments
log in to comment.
Just to make sure I got this right, this sounds like someone is running around with a (potentially) breached phone in the white house?
From the headline I assumed it was someone bringing their own streaming box in and hooking it up in the White House so they could watch Mormon Wives.
Honestly with the level of incompetence in The White House, it could be anything. A streaming TV box, some sort of IoT device, a phone/tablet/PC, just about anything.
now get this, imagine just for a moment: some one tries to spy on the PRESIDENT OF THE UNITED STATES.
I read through this whole article and still don’t really understand it. Can anyone ELI5?
So, like, here I am, on my phone, playing games and browsing the internet. Sometimes my connection is a little slow, but that's just the nature of things because sometimes it just takes a tiny bit longer to get a response and sometimes my phone just runs a little slow.
What I don't know is that my phone is infected with malware. And that malware lets other people access whatever internet I have access to; and that whatever those other people are doing looks like it's coming from my IP address and my device. I am the unwitting exit node for an unscrupulous VPN service (or driving similar).
Someone working in the White House has an infected phone and doesn't know it. They are at the White House most days, work late afternoon to around midnight.
If the person in charge of the botnet knew the phone of a White House worked was compromised, they could use that access to appear as a legitimate user and bypass security protocols, have accounts and passwords compromised, and have their data scraped and stolen.
I would assume most normal people working in the White House have their phones regularly checked for malware, or use special phones for government work. However, higher ups in the Trump White House have routinely violated and ignored security protocols; they could abuse their power to use their own personal phones and to ignore security checks.
Given that the times the node was used are so consistent, I think it's unlikely that there are two infected phones involved.
Given that this happened on most days in October, it's unlikely to be Trump or anyone who regularly travels with him, because he spends a lot of time not at the White House. There was no exit node activity on two Thursdays, one Friday and one Monday; activity was recorded every other day in October. Meaning this isn't someone who comes into the office M-F with weekends off; days off seem to be somewhat rare for this person, and don't occur on normal weekends. I have no idea who the person is, but security should probably make more of an effort to re-secure all phones permitted on the premises.
They’re so dumb that they probably just hired the hacker so hacking could be unnecessary.
Thanks for that!
Yesterday I read google disabled 1.3M devices that were part of a botnet.
What is the difference between a botnet and residential proxies?
Those proxies (SDKs) need to ne banned by the respective app stores.
A botnet implies a level of control over the compromised device, normally achieved through exploits. A residential proxy is done through taking advantage of technically naive users, rather than exploits (proxyware, sort of like spyware/adaware) and doesn’t aim to give control over the target device just over their internet connection. Botnets are run by individuals/hacking groups, and residential proxies are provided by “legitimate” businesses. In theory, they can both be used for the same purpose of DDOSing a target, but as most residential proxy resellers try and position themselves as legitimate, they are less likely to support a client that is using their service to DDOS people
‘Control over the device’ in botnets is practically also just the network. Bots are also created due to users being naive, like positioning iot devices open to the internet, running insecure stuff etc The exploit route for RPs is also malicious, social engineering. Get stuff for free. Nobody is actually aware of what they are doing here.
I agree on the superficial legality. Like a share hoster deleting links in stead of content etc.