



14
264



Post by UnluckyMireille
Socials: FurAffinity

Post by UnluckyMireille
Socials: FurAffinity

Hey all, I spent the weekend updating my home’s thermostat to a smart model. I took a somewhat unusual path and went with a discontinued 2nd Gen Nest thermostat. Read about my journey - Nest Thermostat in 2026 - Artificially-Awesome
Hey all, I spent the weekend updating my home’s thermostat to a smart model. I took a somewhat unusual path and went with a discontinued 2nd Gen Nest thermostat. Read about my journey - Nest Thermostat in 2026 - Artificially-Awesome

cross-posted from: reddthat.com/post/76847055
cross-posted from: reddthat.com/post/76847055



Ah, Schwarz Bruder, practitioner of that most traditional of German arts, ninjitsu…
Anyway, this arrived from P-Bandai last week. Like all the other P-Bandai HGFC kits, it comes with a custom color action base 5, but I’ve got it on a rotating base that also comes with the kit instead of the normal action base display arms. It’s supposed to be for recreating the Sturm and Drang attack, but as you can see I opted to go with the ninja scroll display.
As with the other HGFC kits, this was a pretty easy build with good color separation. Aside from the eyes and head sensor stickers common to most gunpla, the only other stickers used are for the core lander canopy and some yellow bits on the back skirt. Almost everything else works as is, with the sole exception of the kunai. They’re actually a extra pair of hands unique to this kit, so the kunai are the same color as the hands and needed to be painted. In addition, the kit comes with the normal gripping hands, a pair of open claw hands, a pair of kung fu knife hands (because G Gundam) and another unique hand for holding a rolled up scroll.
Which brings me to my one complaint with this kit. The scrolls. They’re cool, don’t get me wrong. Each one is themed around a different element (fire, water, wind, earth, wood) with a unique German koan of some sort for each element and a drawing of a different elemental (salamander, undine, silph, gnome, dryad respectively). And the whole unfurling scrolls display looks amazing. But the frames that you’re supposed to attach the scrolls to only have some tiny tabs to hold the paper in place, and they suck at it. I got tired of the scrolls repeatedly popping out and used Scotch tape to stick the paper to the frames. So, if you’ve got this kit on order, that’s something to keep in mind.
All in all, though, I do like the kit. That said, Rising Gundam when, Bandai?
Ah, Schwarz Bruder, practitioner of that most traditional of German arts, ninjitsu…
Anyway, this arrived from P-Bandai last week. Like all the other P-Bandai HGFC kits, it comes with a custom color action base 5, but I’ve got it on a rotating base that also comes with the kit instead of the normal action base display arms. It’s supposed to be for recreating the Sturm and Drang attack, but as you can see I opted to go with the ninja scroll display.
As with the other HGFC kits, this was a pretty easy build with good color separation. Aside from the eyes and head sensor stickers common to most gunpla, the only other stickers used are for the core lander canopy and some yellow bits on the back skirt. Almost everything else works as is, with the sole exception of the kunai. They’re actually a extra pair of hands unique to this kit, so the kunai are the same color as the hands and needed to be painted. In addition, the kit comes with the normal gripping hands, a pair of open claw hands, a pair of kung fu knife hands (because G Gundam) and another unique hand for holding a rolled up scroll.
Which brings me to my one complaint with this kit. The scrolls. They’re cool, don’t get me wrong. Each one is themed around a different element (fire, water, wind, earth, wood) with a unique German koan of some sort for each element and a drawing of a different elemental (salamander, undine, silph, gnome, dryad respectively). And the whole unfurling scrolls display looks amazing. But the frames that you’re supposed to attach the scrolls to only have some tiny tabs to hold the paper in place, and they suck at it. I got tired of the scrolls repeatedly popping out and used Scotch tape to stick the paper to the frames. So, if you’ve got this kit on order, that’s something to keep in mind.
All in all, though, I do like the kit. That said, Rising Gundam when, Bandai?
What’s the best alternative to Proton Drive for privacy and security that won’t delete my account for inactivity?
What’s the best alternative to Proton Drive for privacy and security that won’t delete my account for inactivity?
Hehe :3
To be fair, I have no idea who’s corrupting who in this relationship…we’re both kinda freaky. And that’s good ❤️
Hehe :3
To be fair, I have no idea who’s corrupting who in this relationship…we’re both kinda freaky. And that’s good ❤️
Not like anybody else is gonna do it
Not like anybody else is gonna do it

Made with this: pixelframe.design/umamusume-font-generator/
Remember, if the AI is doing things the wrong way, it’s because you forgot the “make no mistakes” prompt, and not using the latest model!
Made with this: pixelframe.design/umamusume-font-generator/
Remember, if the AI is doing things the wrong way, it’s because you forgot the “make no mistakes” prompt, and not using the latest model!
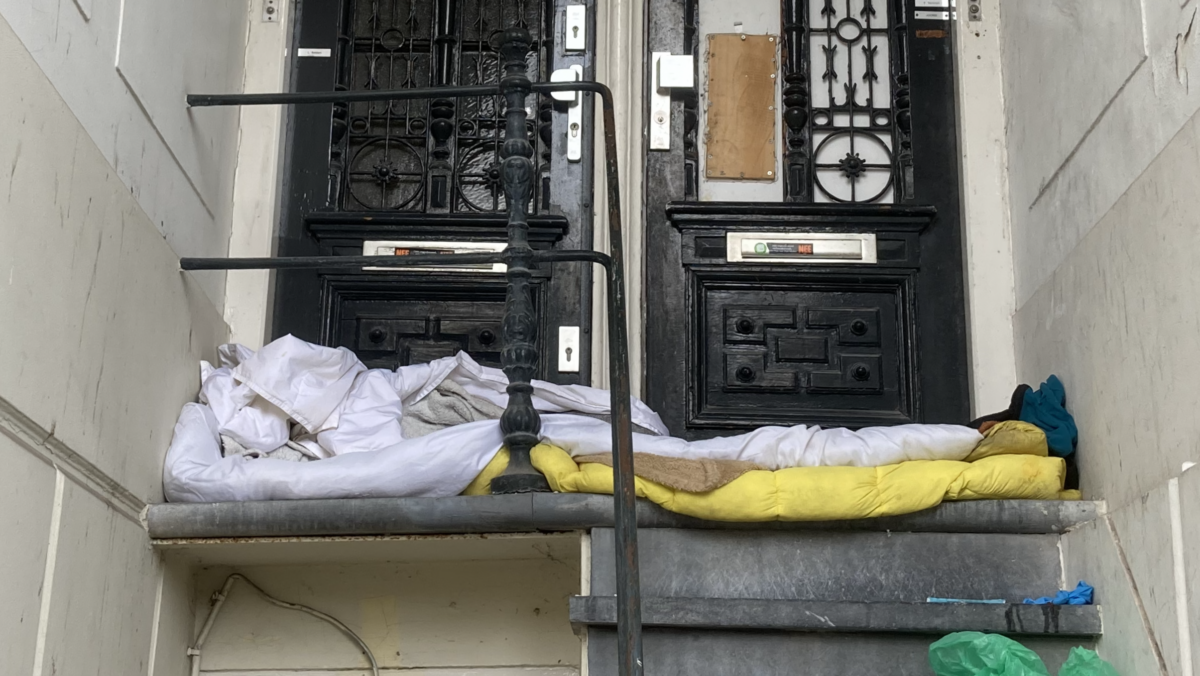
Some 33,000 people aged between 18 and 65 in the Netherlands currently have no permanent place to live, most of them in the big cities, where it is relatively easy to earn money. The real figure may be higher, as it is not known how many people are staying with family or friends.
Some 33,000 people aged between 18 and 65 in the Netherlands currently have no permanent place to live, most of them in the big cities, where it is relatively easy to earn money. The real figure may be higher, as it is not known how many people are staying with family or friends.

Hi all,
If any of you remember the old EmpireAttack that shutdown in 2017, there is a working clone called tessera.
Screenshot:

It’s a very simple tile based strategy game with modes to have different numbers of players and game durations lasting from 15 minutes to 10 days.
Needs a few more active players.
Thought I’d share since I could find any posts related to the original within Lemmy.
It’s made by this guy, not me. Jason
Hi all,
If any of you remember the old EmpireAttack that shutdown in 2017, there is a working clone called tessera.
Screenshot:
It’s a very simple tile based strategy game with modes to have different numbers of players and game durations lasting from 15 minutes to 10 days.
Needs a few more active players.
Thought I’d share since I could find any posts related to the original within Lemmy.
It’s made by this guy, not me. Jason

Lately my router seems to be struggling under all my devices and after some googling, it seems my Archer AX1800 isnt really meant for more than 20-40 devices and I’m currently sitting at 50 with heavy torrent traffic and a media server with 15-20 friends and family connected (typically not all at once of course).
I was looking at the Omada networking gear but then thought of trying OPNSense since I have pretty much everything I need on hand versus spending $400+ for the Omada stuff.
I’d like to run it on the media server since I have tons of compute/RAM available but my question is about the ethernet ports. My mobo has a dedicated 2.5Gb ethernet port built in and I have a second 2.5Gb card that I could toss in there as well, but my concern is that I may saturate the ports with all the additional traffic. My LAN is just 1Gb outside of these two PCs.
My other option is an unused Optiplex 3050 micro that I’ve installed a second ethernet port on but these would both be 1Gb ports.
Am I likely to run into saturation issues on the media server or should the 2.5Gb ports be more than enough to handle the load? Apart from the torrents and video streaming, the rest of the network is mostly typical devices like phones/tablets/consoles, 6 4K POE cameras connected to an NVR and frigate, and a bunch of IoT devices connected to Home Assistant.
I don’t necessarily mind using the Optiplex but I’d definitely prefer to keep everything in one place if I can. I realize that this means my network goes down if I restart the host but it has been a pretty rock solid setup and Proxmox means I can just restart individual containers/VMs rather than the host most of the time.
Edit: forgot to mention that I’m open to buying another quad port NIC for the server if recommended, but would definitely prefer to not spend money if possible. I was planning on using the current router in AP mode along with its ports for a switch and I have another 4 port 2.5Gb switch in the mix as well
Lately my router seems to be struggling under all my devices and after some googling, it seems my Archer AX1800 isnt really meant for more than 20-40 devices and I’m currently sitting at 50 with heavy torrent traffic and a media server with 15-20 friends and family connected (typically not all at once of course).
I was looking at the Omada networking gear but then thought of trying OPNSense since I have pretty much everything I need on hand versus spending $400+ for the Omada stuff.
I’d like to run it on the media server since I have tons of compute/RAM available but my question is about the ethernet ports. My mobo has a dedicated 2.5Gb ethernet port built in and I have a second 2.5Gb card that I could toss in there as well, but my concern is that I may saturate the ports with all the additional traffic. My LAN is just 1Gb outside of these two PCs.
My other option is an unused Optiplex 3050 micro that I’ve installed a second ethernet port on but these would both be 1Gb ports.
Am I likely to run into saturation issues on the media server or should the 2.5Gb ports be more than enough to handle the load? Apart from the torrents and video streaming, the rest of the network is mostly typical devices like phones/tablets/consoles, 6 4K POE cameras connected to an NVR and frigate, and a bunch of IoT devices connected to Home Assistant.
I don’t necessarily mind using the Optiplex but I’d definitely prefer to keep everything in one place if I can. I realize that this means my network goes down if I restart the host but it has been a pretty rock solid setup and Proxmox means I can just restart individual containers/VMs rather than the host most of the time.
Edit: forgot to mention that I’m open to buying another quad port NIC for the server if recommended, but would definitely prefer to not spend money if possible. I was planning on using the current router in AP mode along with its ports for a switch and I have another 4 port 2.5Gb switch in the mix as well
EFF and 27 other human rights organizations today called on the European Commission to retract a dangerous proposal granting its border agency Frontex to request that national authorities issue take-down orders for social media content and giving it so-called “trusted flagger” status under the Digital Services Act (DSA), the EU regulation governing online platforms and content moderation in the region.The extraordinarily improper proposal not only disregards the provisions of the DSA but also places a me…
EFF and 27 other human rights organizations today called on the European Commission to retract a dangerous proposal granting its border agency Frontex to request that national authorities issue take-down orders for social media content and giving it so-called “trusted flagger” status under the Digital Services Act (DSA), the EU regulation governing online platforms and content moderation in the region.The extraordinarily improper proposal not only disregards the provisions of the DSA but also places a me…
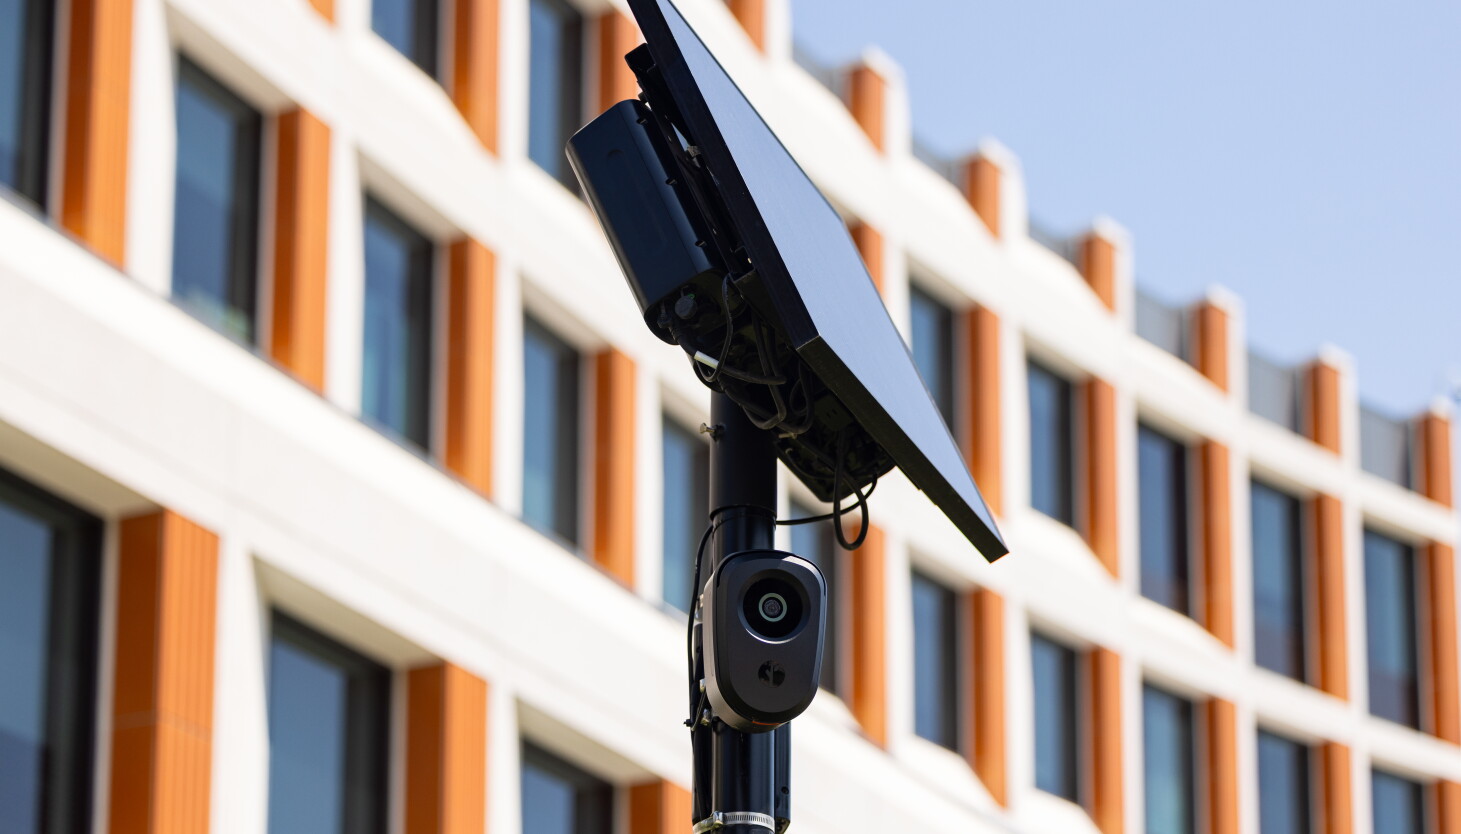
Among the recipients of the money: Cicero Town President Larry Dominick and Lake County Sheriff John Idleburg, both of whose government agencies use the technology from the Atlanta company.
Among the recipients of the money: Cicero Town President Larry Dominick and Lake County Sheriff John Idleburg, both of whose government agencies use the technology from the Atlanta company.


sent by a friend signing up for something (i don’t know what) in canada of all places!
sent by a friend signing up for something (i don’t know what) in canada of all places!


Names, addresses, dates of birth and security answers were accessed, Transport for London says.
Names, addresses, dates of birth and security answers were accessed, Transport for London says.
A German state data regulator has opened an investigation on Wednesday into Deutsche Bank following a massive data leak. The authority is investigating possible data protection violations.
A German state data regulator has opened an investigation on Wednesday into Deutsche Bank following a massive data leak. The authority is investigating possible data protection violations.
A reported cyberattack on Wellington IT has exposed sensitive information belonging to members of 50 credit unions, the majority of which are located in Ireland.
A reported cyberattack on Wellington IT has exposed sensitive information belonging to members of 50 credit unions, the majority of which are located in Ireland.
Ride-hailing company Uber is notifying nearly 150,000 drivers that attackers stole their data after breaching AI infrastructure provider Fireworks in early October.
Ride-hailing company Uber is notifying nearly 150,000 drivers that attackers stole their data after breaching AI infrastructure provider Fireworks in early October.

(u/BottleGoblin)
(u/BottleGoblin)
Hi all, I’ve gotten a Brother machine (DCP series) that can do wifi printing/scanning over their proprietary app. However, I’d like to lock it down from my network, because having it on the same LAN as my other devices and the ability to phone out to the internet seem like room for mischievious activities.
For context, I have OpenWRT on my router, and my clients can access the Brother using their iPrint&Scan app and AirPrint on wifi, as well as the traditional USB port. But I’m not good in networking. In my research, I drafted out the following solutions:
I’d like to ask: which solution above is best for “neutering” the Brother? Or are there any alternatives/details I might’ve missed? I’m not sure if blocking outbound requests this way is enough of a security hardening for an untrusted device, and if there are any usability issues I’ve overlooked so far.
Thanks for any advice, and please share any printer/scanner setup you have in your networks as well. So hopefully I can get more inspiration!
Hi all, I’ve gotten a Brother machine (DCP series) that can do wifi printing/scanning over their proprietary app. However, I’d like to lock it down from my network, because having it on the same LAN as my other devices and the ability to phone out to the internet seem like room for mischievious activities.
For context, I have OpenWRT on my router, and my clients can access the Brother using their iPrint&Scan app and AirPrint on wifi, as well as the traditional USB port. But I’m not good in networking. In my research, I drafted out the following solutions:
I’d like to ask: which solution above is best for “neutering” the Brother? Or are there any alternatives/details I might’ve missed? I’m not sure if blocking outbound requests this way is enough of a security hardening for an untrusted device, and if there are any usability issues I’ve overlooked so far.
Thanks for any advice, and please share any printer/scanner setup you have in your networks as well. So hopefully I can get more inspiration!

source: Bodysuit 23, #877
source: Bodysuit 23, #877

Rude of you to assume :P
I will! And I have! And also, my titty pics are literally on Lemmy for everyone to see 😂️
For science! :3
Source is diogenes.sanjuro
Rude of you to assume :P
I will! And I have! And also, my titty pics are literally on Lemmy for everyone to see 😂️
For science! :3
Source is diogenes.sanjuro

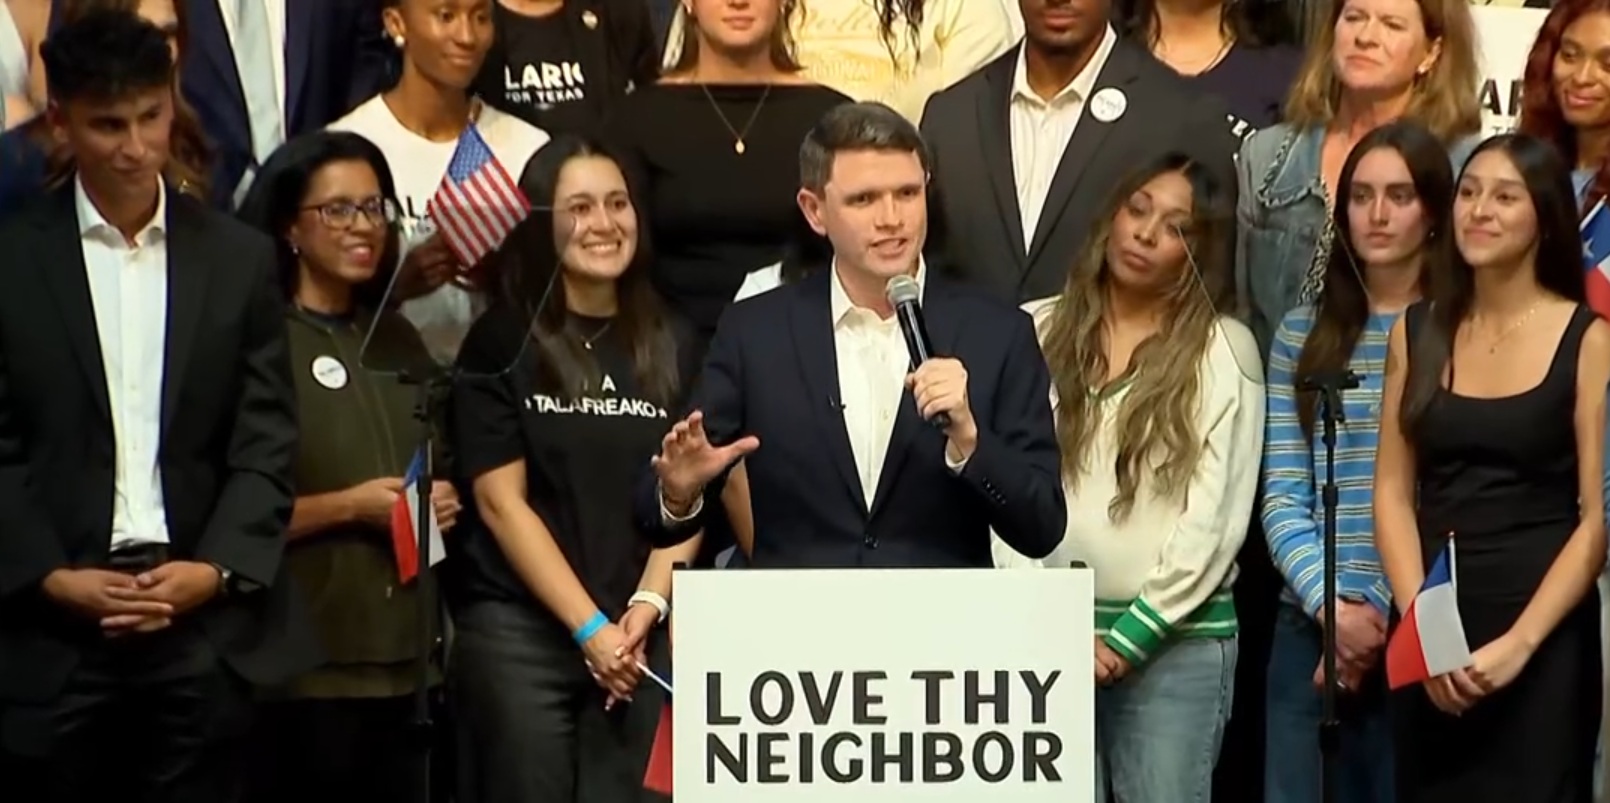
The banner on the podium during James Talarico’s victory speech Nov. 3, read “Love Thy Neighbor,” and the Senator-elect has made outreach rather than triumph his primary focus since that historic night, his campaign says.
On the night of his victory, one of the first people the Senator-elect spoke to was his new colleague Sen. Ted Cruz. Talarico and Cruz had a phone conversation about working together for Texans, according to a person close to the campaign. The morning after the election, his first television appearance was on Fox News, rather than the friendlier territory of CNN or MSNow (though he has made subsequent appearances there). And, the following Monday, Talarico met with Sen. John Cornyn, the man whose seat he is taking.
“He has served our state honorably, and I’m grateful for his advice and guidance,” Talarico wrote of Cornyn on social media after the meeting. "Now is the time for us to come together — Democrats and Republicans — to deliver for Texas.”
Talarico has even pledged to work with X owner Elon Musk, the man who put a $200 million bounty on his political head, if the opportunity arises.
The banner on the podium during James Talarico’s victory speech Nov. 3, read “Love Thy Neighbor,” and the Senator-elect has made outreach rather than triumph his primary focus since that historic night, his campaign says.
On the night of his victory, one of the first people the Senator-elect spoke to was his new colleague Sen. Ted Cruz. Talarico and Cruz had a phone conversation about working together for Texans, according to a person close to the campaign. The morning after the election, his first television appearance was on Fox News, rather than the friendlier territory of CNN or MSNow (though he has made subsequent appearances there). And, the following Monday, Talarico met with Sen. John Cornyn, the man whose seat he is taking.
“He has served our state honorably, and I’m grateful for his advice and guidance,” Talarico wrote of Cornyn on social media after the meeting. "Now is the time for us to come together — Democrats and Republicans — to deliver for Texas.”
Talarico has even pledged to work with X owner Elon Musk, the man who put a $200 million bounty on his political head, if the opportunity arises.

A new experiment demonstrates how quantum devices could verify a person’s position extremely securely, making it much harder to hack sensitive messages.
A new experiment demonstrates how quantum devices could verify a person’s position extremely securely, making it much harder to hack sensitive messages.

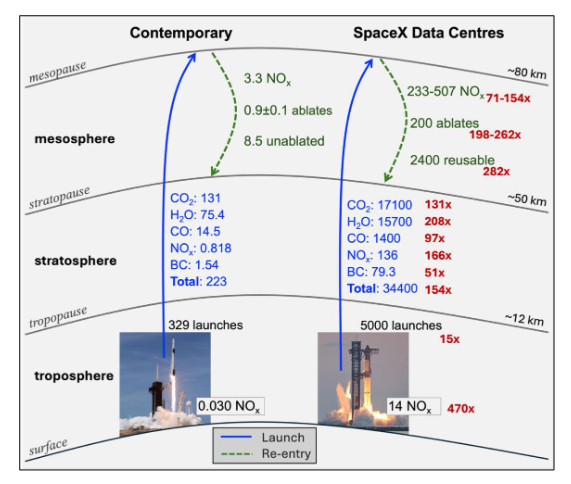
Let’s pretend that it was possible to do a data centre in space, for a minute. What would that do to the atmosphere?
Related: here’s what it would do to the night sky: https://arxiv.org/pdf/2608.02757. Commentary by the author adds:
Many times more visible satellites than stars in the sky, and many of them brighter than most/all stars. This is a conservative estimate, SpaceX actually wants to make their satellites even bigger than we modelled.
Oh and:
“Fortunately,” even with the most generous possible assumptions on sizes, stationkeeping, and collision avoidance maneuvers, and ignoring ALL OTHER SATELLITES AND DEBRIS, this megaconstellation is above the runaway collision threshold all by itself and would put us into full, fast-timescale Kessler Syndrome. https://arxiv.org/pdf/2607.29644
Let’s pretend that it was possible to do a data centre in space, for a minute. What would that do to the atmosphere?
Related: here’s what it would do to the night sky: https://arxiv.org/pdf/2608.02757. Commentary by the author adds:
Many times more visible satellites than stars in the sky, and many of them brighter than most/all stars. This is a conservative estimate, SpaceX actually wants to make their satellites even bigger than we modelled.
Oh and:
“Fortunately,” even with the most generous possible assumptions on sizes, stationkeeping, and collision avoidance maneuvers, and ignoring ALL OTHER SATELLITES AND DEBRIS, this megaconstellation is above the runaway collision threshold all by itself and would put us into full, fast-timescale Kessler Syndrome. https://arxiv.org/pdf/2607.29644
@giornalismo
articolo21.org/2026/11/cgil-il…
Articolo21 aderisce convintamente alle numerose manifestazioni promosse dalla Cgil nella
@giornalismo
articolo21.org/2026/11/cgil-il…
Articolo21 aderisce convintamente alle numerose manifestazioni promosse dalla Cgil nella

Based on a true story and takes place in 1907 in New York as real-life bankers J. P. Morgan and Charles Barney grapple with a financial crisis sparked by Barney’s failed attempt to manipulate the copper market. As Morgan strives to safeguard his empire he becomes entangled in a clandestine struggle involving his brilliant mistress, Belle de Costa Greene, who ran his world-famous library.
Based on a true story and takes place in 1907 in New York as real-life bankers J. P. Morgan and Charles Barney grapple with a financial crisis sparked by Barney’s failed attempt to manipulate the copper market. As Morgan strives to safeguard his empire he becomes entangled in a clandestine struggle involving his brilliant mistress, Belle de Costa Greene, who ran his world-famous library.

Over the last ten years, we’ve lived through the rapid adoption of remote connectivity in industrial environments around the world.
[…]
Now that we understand the chaos of connectivity in modern industrial environments, we can talk about what’s getting hacked right now, and why. Why water? Why refrigerators?
A few unfortunate, incredibly predictable factors have led us here, and my colleagues and I have been screaming about them for years: [ …]
[…]
Fixing the vulnerability isn’t easy, even if the organisation is aware of it. Industrial systems have long lifecycles, sometimes 10 to 30 years. They’re engineered and tested by the OEM to work in a very specific technology stack and topology. Any alteration can, at best, disrupt the process and, at worst, lead to injury or death. Either outcome can be far more damaging than a casual hacker. Because of these lifecycles, and the inability to replace systems, I still deal with Windows 2000, CE, and XP every week. They can’t be removed from production or modified without express authorisation from the OEM and engineers, plus a significant outage and testing window.
Over the last ten years, we’ve lived through the rapid adoption of remote connectivity in industrial environments around the world.
[…]
Now that we understand the chaos of connectivity in modern industrial environments, we can talk about what’s getting hacked right now, and why. Why water? Why refrigerators?
A few unfortunate, incredibly predictable factors have led us here, and my colleagues and I have been screaming about them for years: [ …]
[…]
Fixing the vulnerability isn’t easy, even if the organisation is aware of it. Industrial systems have long lifecycles, sometimes 10 to 30 years. They’re engineered and tested by the OEM to work in a very specific technology stack and topology. Any alteration can, at best, disrupt the process and, at worst, lead to injury or death. Either outcome can be far more damaging than a casual hacker. Because of these lifecycles, and the inability to replace systems, I still deal with Windows 2000, CE, and XP every week. They can’t be removed from production or modified without express authorisation from the OEM and engineers, plus a significant outage and testing window.