Top rule

Full title: ICE Wants the Country’s Voter Data | Voting data is public by design, but ICE is looking for a federal contractor to help it handle voter registration and history files to find what it describes as fraud.
Full title: ICE Wants the Country’s Voter Data | Voting data is public by design, but ICE is looking for a federal contractor to help it handle voter registration and history files to find what it describes as fraud.
cross-posted from : lemmy.zip/post/70343030
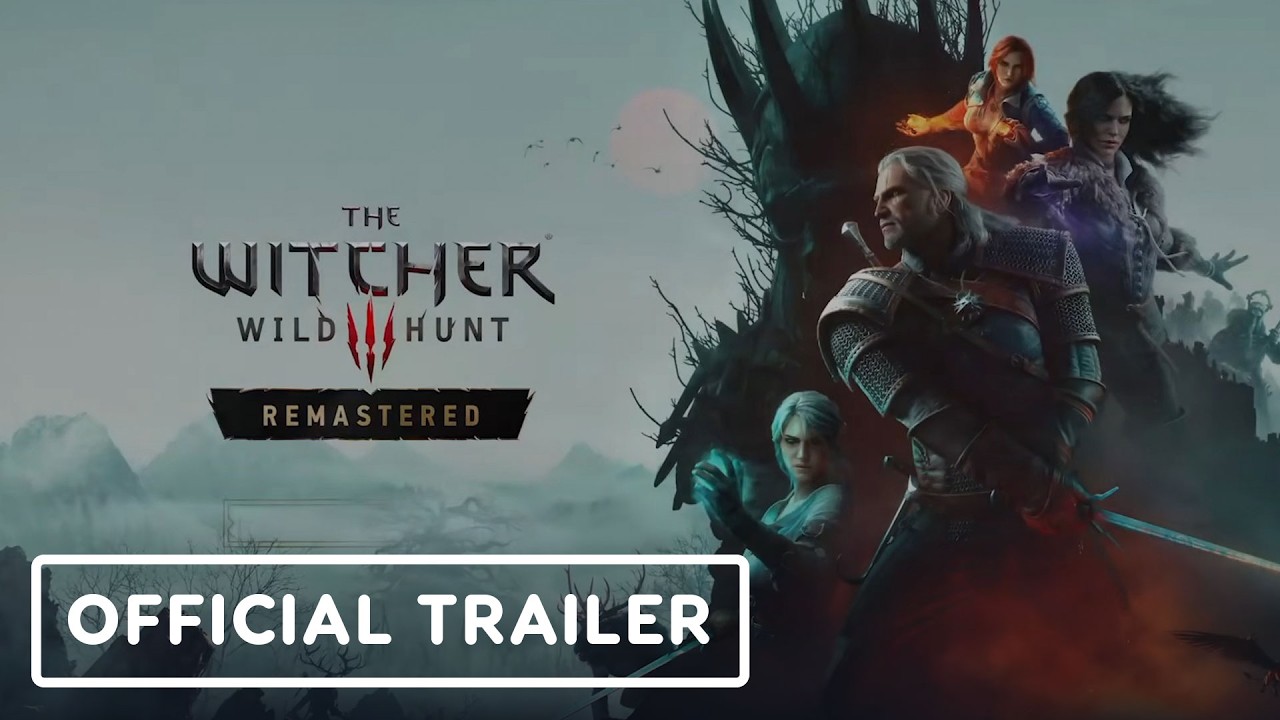
The Witcher III: Wild Hunt Remastered boasts remastered visuals, enhanced combat, improved movement, enhanced monster behaviors. A skill tree revamp, transmogrifications, new finishers, and so much more. The fantastic Hearts of Stone and Blood and Wine expansions are included. The upgrade is free for all Witcher 3 owners. Coming Sept. 29, 2026.


If it helps others this was my config. To be honest I have a weak grasp of what it actually does so there might be some security issues with it.
Apparently you can also add lemmy as a search engine. Will work on that later.
# docker-compose.yml name: searxng services: core: container_name: searxng-core image: docker.io/searxng/searxng:latest restart: always network_mode: “service:gluetun” volumes: - ./core-config:/etc/searxng - core-data:/var/cache/searxng gluetun: image: qmcgaw/gluetun:v3.41.3 container_name: gluetun cap_add: - NET_ADMIN environment: - VPN_SERVICE_PROVIDER=custom - VPN_TYPE=openvpn - OPENVPN_CUSTOM_CONFIG=/gluetun/custom.conf ports: - 8080:8080 restart: always volumes: - ./gluetun:/gluetun devices: - /dev/net/tun:/dev/net/tun nginx: container_name: nginx image: nginx:latest ports: - 80:80 - 443:443 volumes: - ./nginx:/etc/nginx/conf.d - ./cert:/etc/nginx/cert valkey: container_name: searxng-valkey image: docker.io/valkey/valkey:9-alpine command: valkey-server --save 30 1 --loglevel warning restart: always volumes: - valkey-data:/data/ volumes: core-data: valkey-data: # nginx/default.conf server { server_name localhost; listen 443 ssl; ssl_certificate /etc/nginx/cert/cert.pem; ssl_certificate_key /etc/nginx/cert/private.key; location / { proxy_pass http://gluetun:8080/; proxy_set_header Host $host; proxy_set_header Connection $http_connection; proxy_set_header X-Forwarded-Proto $scheme; proxy_set_header X-Real-IP $remote_addr; proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for; } } server { server_name localhost; listen 80; location / { return 301 https://$host$request_uri; } }

Artist: Darr1O | pixiv | twitter | newgrounds | artstation | danbooru
Full quality: .png 2 MB (2342 × 3470)
nitter.net is currently replaced with a message about the C&D until zedeus (lead dev) gets legal advice on how to proceed. Other instances are probably ok for now (or at least until an API break). Not a great sign for anyone else who hosts it, but hopefully it gets resolved without development permanently stopping.
nitter.net is currently replaced with a message about the C&D until zedeus (lead dev) gets legal advice on how to proceed. Xcancel.com is ok for now (or at least until an API break). EDIT: xcancel.com was also C&D-ed and is now down

also shout-out to the most visually obnoxious gif I could find xD
it’s not even timed correctly at all
cross-posted from: https://piefed.world/c/tech/p/1358432/nitter-project-received-cease-and-desist
Cease and desist
On 24 August 2026 cease and desist letters have been sent by X Corp. demanding a permanent takedown of Nitter instances and the project’s repository.
nitter.net is offline and development has stopped for the time being. I’m seeking legal advice and won’t be commenting further on the specifics for now.
Thank you to everyone who used, hosted, packaged, donated and contributed to Nitter over the past seven years.
— zedeus, 25 August 2026
Photo source: Official website/instance— Archive.
More info: GitHub issue 1442.


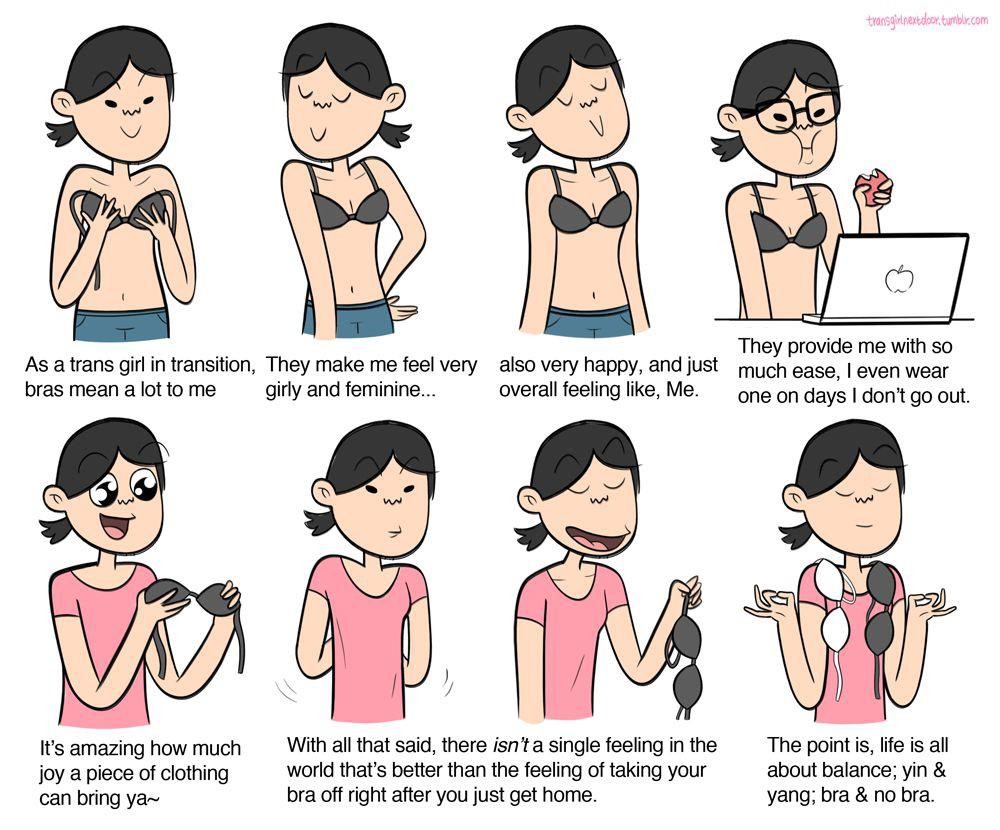
This is so me, omfg 😭

I swear, every person in every transition timeline EVER looks so much happier than before. And it’s just so wholesome, omg 😭💜
Funnily enough, I’d also say most people look much younger 😆

Apple today said it is reversing its decision and will not change the email domain used for the iCloud+ Hide My Email feature. Emails sent using Hide My Email will continue to use the same icloud.com domain that Apple uses for standard iCloud emails. In June, Apple said it would unify the email domains used by Sign in with Apple and Hide My Email under a single private.icloud.com domain.
This is good news, should they not try the same trick at a later date.
I wrote a blog post about encryption.
Unusual request, so let me be straight about what it is before I ask for anything.
The short version: I pay for MLB.tv, but the league geo-restricts games depending on the IP you watch from. The one setup that unlocks every game (no local blackouts, and none of the “this game is a Netflix/Roku/Peacock exclusive” carve-outs) is MLB.tv International, which needs a UK or EU IP. I’ve built a small Raspberry Pi that lets my stream appear to originate from a home internet connection over there, and I’m looking for someone willing to plug one into a spare ethernet port and forget it exists.
The honest part: this works around MLB’s geo-restrictions, which is against their terms of service. I’m doing it with a fully paid subscription to watch games I’ve already paid for, but if that’s not something you want on your connection, totally fair, no hard feelings, stop reading here. I’d rather you pass than feel misled.
Still with me? Here’s everything.
It is NOT a 24/7 relay, and it does NOT stream whole games through your line. MLB only checks your location at the moment a stream starts. So my usage is:
Net effect on you: a WireGuard handshake and a few minutes of video per game I watch. A few MB, not hours. I use a Home Assistant script to enable/disable the VPN Client in UniFi, so it’s guaranteed to shut off after a few minutes. No accidentally leaving it on forever and using your connection
I’ve already done the homework, and residential is the only door left open:
A real residential connection is the only thing MLB treats as a legitimate viewer. That’s why I need a person with a spare port, not a server I can rent.
   [ my home, Starlink / CGNat ]
          │   WireGuard  (encrypted, outbound)
          ▼
   [ small VPS I rent ]   ◀─ only forwards encrypted frames; sees nothing
          │   WireGuard  (encrypted)
          ▼
   [ My Pi in your home ]   ── dials OUT only, never listens; firewall blocks your LAN entirely
          │
          ▼
   [ your home internet ]  ──▶  MLB.tv  (only ever sees your residential UK/EU IP)

   ( my paid stream flows back up the same path to my TV — I switch the tunnel
     off after the first few minutes, so most of it never crosses your line )
A Raspberry Pi in a small case. You give it power (~3–5 W, ~£0.50/month of electricity) and one ethernet port. That’s the entire job… no router config, no port forwarding, no software on your devices, no accounts.
The firewall denies all inbound, and for forwarded traffic it drops every private-network destination before allowing anything out. In plain terms: traffic from my tunnel physically cannot reach your LAN… not your PCs, NAS, printer, or router admin page. It can only reach the public internet.
Two things make trusting me cheap:
Send me your SSH public key and I’ll set you up a read-only account. One command, sudo host-verify, prints the live firewall rules, the tunnel status, and every connection the box currently has open — so you can confirm all of the above any time. That account can’t change anything or reach the rest of the box; it’s there purely so you don’t have to trust me blind. Happy to walk through the whole config with you too.
Mostly my genuine gratitude willingness to reciprocate in kind: host something for you, help on a homelab project, or whatever feels fair.
If you’re in the UK or EU and up for it (or just have questions) reply or DM. Cheers, and thanks for reading either way.
Hey, Maya —
First off, congratulations on becoming an “outdoors person.” Three years ago, you thought mosquitoes were government drones. Now you own boots with names like “Expedition Carbon Ultra GTX.” People change.
I’m happy for you.
Which is why I’d like to offer you fifteen thousand dollars to pretend you never invited me.
Seriously.
Take it.
Use it for backpacks, trekking poles, tiny titanium spoons, or whatever mysterious economy hikers have built among themselves.
I simply cannot spend my Saturday voluntarily climbing a mountain whose greatest achievement is being taller than the parking lot.


Good day everyone!
I finally got arround to hosting my own lemmy instance and I decided to make it all about my island. You are free to look (TW: Spanish).
So to help start things up I decided I’d grab an RSS bot and populate a couple communities with local newspapers. This one seems to be very promising as all the others I’ve found had the typical unmaintained errors and had 2+ years on their belt.
So now that I’ve had one tool on my belt I wonder what’s in everyone’s toolbelt. What do you use to manage the instances?

Tefuda ga Oome no Victoria, episode 8

วิกตอเรียผู้มีสารพัดไพ่ลับในมือ
- Info - AniList - Info - Kitsu - Info - MyAnimeList - Info - Official Site (Japanese) - Social - Twitter (Japanese) - Streaming - Bilibili TV - Streaming - Crunchyroll - Streaming - YouTube
Reminder: Please do not discuss plot points not yet seen or skipped in the show. Failing to follow the rules may result in a ban.
All discussions
| Episode | Link |
|---|---|
| 1 | Link |
| 2 | Link |
| 3 | Link |
| 4 | Link |
| 5 | Link |
| 6 | Link |
| 7 | Link |
| 8 | Link |
| 9 | Link |
This post was created by a bot. Message the mod team for feedback and comments. The original source code can be found on GitHub.

Interesting new European mobile wallet provider.

Vladimir Putin will seize private companies that do not defend themselves against Ukraine’s drones.
Using special powers, the Kremlin will take control of assets and assume formal ownership of businesses deemed to have insufficient protection against attacks or to have failed to carry out adequate repairs.

Nvidia CEO Jensen Huang confirmed on Tuesday his intention to visit Israel soon, underlining the firm’s objective to double its staff in the country from the current 5,000 employees.
The company, which six years ago bought the Israeli networking firm Mellanox recently announced a mega campus in northern Israel in Kiryat Tivon.

The Securities and Exchange Commission has reportedly subpoenaed several major Wall Street lenders to glean more information about their role in the near-collapse of AI-focused hedge fund Situational Awareness.
Regulators are seeking insights into Situational Awareness’s trades, use of leverage and communications with the investment banks, which include Goldman Sachs, JP Morgan, Citigroup and Bank of America, according to Reuters, citing a source familiar with the matter.
Situational Awareness plunged from about $45 billion to around $10 billion in late July after it was hammered in last month’s tech sell-off.
The hedge fund, led by former OpenAI researcher Leopold Aschenbrenner, was forced to unwind much of its publicly listed portfolio of large, concentrated, levered positions — which included SK Hynix and CoreWeave — after losses sparked several margin calls among its prime brokers.

CIA Director John Ratcliffe visited Russia to attend meetings in Moscow on Tuesday, according to two US media outlets, in what is believed to be Ratcliffe’s first known trip to Russia since taking over as US spy chief. The reported visit comes as US-brokered talks aimed at ending the Ukraine war have stalled.