0

preview
I was searching for ways to make tvs a little bit more privacy respecting has anyone had an expierence with dumbtv
I was searching for ways to make tvs a little bit more privacy respecting has anyone had an expierence with dumbtv

Not on this instance? Enter your own instance's domain to go straight to following c/privacy@lemmy.ml there.
showing posts tagged #privacy — clear
I was searching for ways to make tvs a little bit more privacy respecting has anyone had an expierence with dumbtv
I was searching for ways to make tvs a little bit more privacy respecting has anyone had an expierence with dumbtv

I didn’t know about RTING’s YouTube channel, they have some decent stuff out.
From the description:
Read more about our full investigation: www.rtings.com/tv/learn/…/smart-tv-data-privacy
Learn how to set up a pi-hole to block ACR at the network level: docs.pi-hole.net/main/basic-install/
I didn’t know about RTING’s YouTube channel, they have some decent stuff out.
From the description:
Read more about our full investigation: www.rtings.com/tv/learn/…/smart-tv-data-privacy
Learn how to set up a pi-hole to block ACR at the network level: docs.pi-hole.net/main/basic-install/
Eurosky has a migration tool for Bluesky accounts. I personally have an unverified account on Bluesky, but don’t to provide my biometrics to verify it.
Did anyone already try or is on Eurosky? And, what are your take on it? Is this a private-friendly platform, do you need to provide an age ID, for example?
Eurosky has a migration tool for Bluesky accounts. I personally have an unverified account on Bluesky, but don’t to provide my biometrics to verify it.
Did anyone already try or is on Eurosky? And, what are your take on it? Is this a private-friendly platform, do you need to provide an age ID, for example?
Hi,
Christmas is coming, and we’ve had repeated requests for a digital picture frame, that would allow us to send pictures to older relatives from our home devices. I guess there is no alternative to wifi and cloud here, since we live far away from one another, and don’t want to bother with sending SD ou USB drives through traditional mail.
We’ve looked around, but all we see are suggestions for building our own frame, self hosting, or keeping the device offline, which does not work for us, since we don’t have enough time or resources to dig those options.
So far i see 3 potential candidates:
Any help is appreciated,
Hi,
Christmas is coming, and we’ve had repeated requests for a digital picture frame, that would allow us to send pictures to older relatives from our home devices. I guess there is no alternative to wifi and cloud here, since we live far away from one another, and don’t want to bother with sending SD ou USB drives through traditional mail.
We’ve looked around, but all we see are suggestions for building our own frame, self hosting, or keeping the device offline, which does not work for us, since we don’t have enough time or resources to dig those options.
So far i see 3 potential candidates:
Any help is appreciated,
Guardian report claims some 3.5 million photos of Palestinians from Gaza being stored at Amazon data center in Tel Aviv to allow Israel access to facial recognition technology
Guardian report claims some 3.5 million photos of Palestinians from Gaza being stored at Amazon data center in Tel Aviv to allow Israel access to facial recognition technology
Hi, I want to start creating or uploading some content but I don’t want a goverment or corporation to see everything that I’m putting up.
What ways are there to accomplish this? One is self hosting i think, there my concerns are security(getting hacked) and then that I don’t have a laptop at the moment so i would need to host this on my main pc while i use it. Any ideas on how this could be accomplished? Im guessing that buying hosting is a no-go?
Hi, I want to start creating or uploading some content but I don’t want a goverment or corporation to see everything that I’m putting up.
What ways are there to accomplish this? One is self hosting i think, there my concerns are security(getting hacked) and then that I don’t have a laptop at the moment so i would need to host this on my main pc while i use it. Any ideas on how this could be accomplished? Im guessing that buying hosting is a no-go?
Should I take fingerprint logins off all my apps ? Obviously theyre easier to get in(bonk with hammer, take my hand and open it) but I’m not super concerned about a nearby threat.
Should I take fingerprint logins off all my apps ? Obviously theyre easier to get in(bonk with hammer, take my hand and open it) but I’m not super concerned about a nearby threat.
I’ve had two medical-related companies call me on my cell phone and ask to verify my birthdate. There are legit companies I had business with.
When I refused, they give me no options (like call us back, or reply to an email, etc.), they are just in absolute hurry to get off the phone. The expectation is that I tell them my birthday and if I don’t, they don’t communicate with me.
It’s outrageous to call someone and ask for information to verify them when you have a relationship with them, when the person’s given you their phone number, and often there’s a checkbox for "leave messages for me at this number. "
Other than the security aspect of handing out your birthday, who is going to be answering your phone? Family members and friends who are going to know your birthdate… it just seems so stupid…
I’ve had two medical-related companies call me on my cell phone and ask to verify my birthdate. There are legit companies I had business with.
When I refused, they give me no options (like call us back, or reply to an email, etc.), they are just in absolute hurry to get off the phone. The expectation is that I tell them my birthday and if I don’t, they don’t communicate with me.
It’s outrageous to call someone and ask for information to verify them when you have a relationship with them, when the person’s given you their phone number, and often there’s a checkbox for "leave messages for me at this number. "
Other than the security aspect of handing out your birthday, who is going to be answering your phone? Family members and friends who are going to know your birthdate… it just seems so stupid…

“When we need medical care, we expect decisions about our treatment to be made by our doctors, not a tech company’s algorithm,” writes the EFF newsletter EFFector. But in January America’s federal government launched a program called WISeR that uses AI to evaluate authorization requests for certain procedures from America’s federal health insurance program for seniors, Medicare. EFF sued for records and discovered “additional issues” with the program that they say "could jeopardize Medicare beneficiaries’…
“When we need medical care, we expect decisions about our treatment to be made by our doctors, not a tech company’s algorithm,” writes the EFF newsletter EFFector. But in January America’s federal government launched a program called WISeR that uses AI to evaluate authorization requests for certain procedures from America’s federal health insurance program for seniors, Medicare. EFF sued for records and discovered “additional issues” with the program that they say "could jeopardize Medicare beneficiaries’…
“When we need medical care, we expect decisions about our treatment to be made by our doctors, not a tech company’s algorithm,” writes the EFF newsletter EFFector. But in January America’s federal government launched a program called WISeR that uses AI to evaluate authorization requests for certain procedures from America’s federal health insurance program for seniors, Medicare. EFF sued for records and discovered “additional issues” with the program that they say "could jeopardize Medicare beneficiaries’…
“When we need medical care, we expect decisions about our treatment to be made by our doctors, not a tech company’s algorithm,” writes the EFF newsletter EFFector. But in January America’s federal government launched a program called WISeR that uses AI to evaluate authorization requests for certain procedures from America’s federal health insurance program for seniors, Medicare. EFF sued for records and discovered “additional issues” with the program that they say "could jeopardize Medicare beneficiaries’…
cross-posted from: lemmy.world/post/54455222
“…accessing users’ photos without their “specific” consent…” $880 Million and that is only Italy, hopefully all other countries sue them next!!!
cross-posted from: lemmy.world/post/54455222
“…accessing users’ photos without their “specific” consent…” $880 Million and that is only Italy, hopefully all other countries sue them next!!!
cross-posted from: communick.news/post/7444537
AI Disclosure:
- Implementation - Hint. Syntax was reviewed and polished by AI.
- Testing - Assisted. AI was used to troubleshoot whenever I got stuck
- Documentation - Generated
I spent the last three months slowly tinkering with Headscale and trying to get it to run on one of Google’s “free-tier” cloud instances, while also learning about GCI’s strange setup. During that time I used Claude Sonnet to keep track of my progress and help me troubleshoot whenever I got stuck. I finally got it going and before I closed the project, I asked Claude to document my work along with all pertinent information and create and admin cheatsheet, just in case I forget. I liked the output, so I asked the LLM to sanitize my data and recreate my project as a step-by-step walktrhough in a single HTML page.
PROVIDED AS-IS!!! Do not copy and paste code blindly. Use this as a walkthough/guide and NOT as a recipe book. You WILL need to correct code.
EDIT: It looks like for this document, Claude also took it upon itself to further clean my configs, scripts, etc., and add a lot of comments to make it all easier to understand. I DO NOT work this cleanly. It looks correct though.
cross-posted from: communick.news/post/7444537
AI Disclosure:
- Implementation - Hint. Syntax was reviewed and polished by AI.
- Testing - Assisted. AI was used to troubleshoot whenever I got stuck
- Documentation - Generated
I spent the last three months slowly tinkering with Headscale and trying to get it to run on one of Google’s “free-tier” cloud instances, while also learning about GCI’s strange setup. During that time I used Claude Sonnet to keep track of my progress and help me troubleshoot whenever I got stuck. I finally got it going and before I closed the project, I asked Claude to document my work along with all pertinent information and create and admin cheatsheet, just in case I forget. I liked the output, so I asked the LLM to sanitize my data and recreate my project as a step-by-step walktrhough in a single HTML page.
PROVIDED AS-IS!!! Do not copy and paste code blindly. Use this as a walkthough/guide and NOT as a recipe book. You WILL need to correct code.
EDIT: It looks like for this document, Claude also took it upon itself to further clean my configs, scripts, etc., and add a lot of comments to make it all easier to understand. I DO NOT work this cleanly. It looks correct though.
A small incident has become the pretext for a sweeping experiment in AI surveillance and censorship.
A small incident has become the pretext for a sweeping experiment in AI surveillance and censorship.
What are the most solid, user friendly foss options? Open to better camera suggestions as well. I do not want a Nest sub, or similar.
What are the most solid, user friendly foss options? Open to better camera suggestions as well. I do not want a Nest sub, or similar.
Are Firefox Relay’s mozmail domains related to Mozmail? The latter says it uses Google Gemini, which would imho put Relay at risk.
Are Firefox Relay’s mozmail domains related to Mozmail? The latter says it uses Google Gemini, which would imho put Relay at risk.
My own project. I wanted to merge, sign and redact contracts without handing them to iLovePDF or Smallpdf, so everything runs in your browser: no backend, the CSP blocks connections to other hosts, no analytics, no account. Redaction actually removes the text instead of covering it. Don’t want to trust the hosted copy? Self-host it with Docker or use the offline Windows app.
My own project. I wanted to merge, sign and redact contracts without handing them to iLovePDF or Smallpdf, so everything runs in your browser: no backend, the CSP blocks connections to other hosts, no analytics, no account. Redaction actually removes the text instead of covering it. Don’t want to trust the hosted copy? Self-host it with Docker or use the offline Windows app.

Hello! I’ve been working on blastQR for a couple of years now and I thought this community might find it useful. Feel free to try it and ask me anything!
blastQR is a fully open-source file transfer app and protocol that works completely offline. You can even use it in airplane mode. Data is transferred through sequences of QR codes displayed on a sender device and scanned by a receiver device’s camera. It uses RaptorQ codes so the receiver can recover the file from any sufficiently large subset of frames.
Note that although I have made use of AI as a coding assistant I do not consider this to be a vibe-coded app and I do plan to continue improving it and supporting it in the future.
See video of blastQR in action: github.com/…/038a2567-70c8-47c8-b165-dea858d1aef3
Here are some of the key features:
I’m trying to build a small community around the project so it can be improved and maintained and so it can reach more people in the future.
Downloads for all platforms can be found here: codeberg.org/blast/blastqr/releases/latest
Hello! I’ve been working on blastQR for a couple of years now and I thought this community might find it useful. Feel free to try it and ask me anything!
blastQR is a fully open-source file transfer app and protocol that works completely offline. You can even use it in airplane mode. Data is transferred through sequences of QR codes displayed on a sender device and scanned by a receiver device’s camera. It uses RaptorQ codes so the receiver can recover the file from any sufficiently large subset of frames.
Note that although I have made use of AI as a coding assistant I do not consider this to be a vibe-coded app and I do plan to continue improving it and supporting it in the future.
See video of blastQR in action: github.com/…/038a2567-70c8-47c8-b165-dea858d1aef3
Here are some of the key features:
I’m trying to build a small community around the project so it can be improved and maintained and so it can reach more people in the future.
Downloads for all platforms can be found here: codeberg.org/blast/blastqr/releases/latest
Nvidia’s new interim CEO, Colette Kress, has a direct line to Israel. In a 2023 interview with the Israeli business outlet Globes, she said her day starts with meetings with Nvidia’s Israeli executives: “My day starts with Israel meetings, and only then continues to California.”
Kress takes over after Jensen Huang’s resignation. Israel is one of Nvidia’s largest bases outside the United States. About 12 percent of its employees, roughly 3,200 people, work there, according to Globes.

Nvidia’s new interim CEO, Colette Kress, has a direct line to Israel. In a 2023 interview with the Israeli business outlet Globes, she said her day starts with meetings with Nvidia’s Israeli executives: “My day starts with Israel meetings, and only then continues to California.”
Kress takes over after Jensen Huang’s resignation. Israel is one of Nvidia’s largest bases outside the United States. About 12 percent of its employees, roughly 3,200 people, work there, according to Globes.
cross-posted from: sh.itjust.works/post/69844421
No one warned me, when I became a parent, about all the apps that would colonize my phone: the app for the baby monitor where I could gaze at my daughter, even when my husband and I finally had a night out. The app for the Snoo smart bassinet we rented in bleary-eyed desperation, which logged her sleep by the minute. The app where I logged her sleep manually because the Snoo was not accurate enough. And still, I remember thinking that I had been quite restrained. I mean, I didn’t buy the $299 Owlet smart sock, which would send her pulse rate and oxygen saturation directly to my phone, or the $290 Nanit monitor, which would track her every breath.
cross-posted from: sh.itjust.works/post/69844421
No one warned me, when I became a parent, about all the apps that would colonize my phone: the app for the baby monitor where I could gaze at my daughter, even when my husband and I finally had a night out. The app for the Snoo smart bassinet we rented in bleary-eyed desperation, which logged her sleep by the minute. The app where I logged her sleep manually because the Snoo was not accurate enough. And still, I remember thinking that I had been quite restrained. I mean, I didn’t buy the $299 Owlet smart sock, which would send her pulse rate and oxygen saturation directly to my phone, or the $290 Nanit monitor, which would track her every breath.
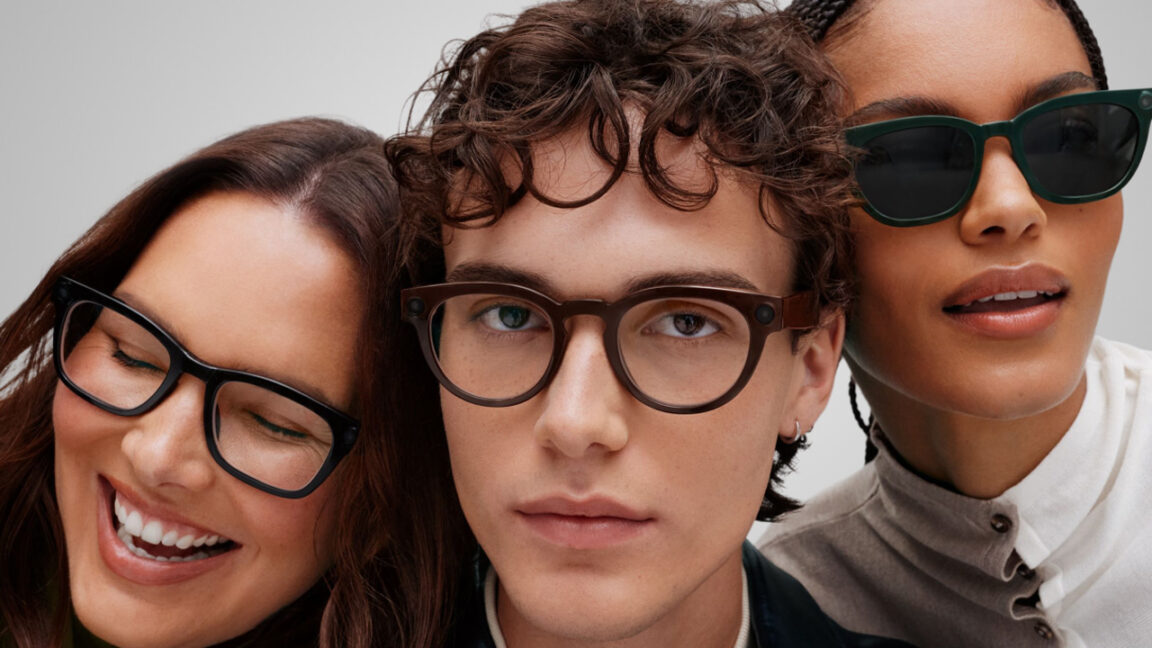
Smartglasses have always faced an uphill road to acceptance. Not only is propping a computer up on your nose an uncomfortable proposition, but the privacy aspect has been vexing people since the Google Glass days. Now, Google is ready to take another swing at “intelligent eyewear” for the Gemini era after previewing its plans a couple of times. The first glasses are up for preorder today from Gentle Monster and Warby Parker, but they’re no impulse buy.
These devices are a collaboration between Google, Samsung, and the aforementioned eyewear designers. Gentle Monster and Warby Parker have each designed a few different frames, with options for transparent and tinted lenses. Samsung is providing the computing hardware that fits inside them, and Google has the software covered.
Warby Parker has designed three frames for Google eyewear, called Alden, Reid, and Wren (see above). They are available with both standard optical and sun lenses in Pine, Saddle, and Jet Black colors at $395 and higher. Warby Parker is only selling devices in the US. Gentle Monster has gone a bit further with six styles, but Google hasn’t told us any names for those yet. They come in dark red, pink, gray, and yellow colors and are available with clear, tinted, blue, or brown lenses. The Gentle Monster styles start a little higher at $449, and they will be available in the US and South Korea.
Google says the frames all weigh about 41 grams, which is not terrible but is definitely near the top for glasses generally. They will, naturally, weigh much more when you account for lenses. That will also determine the final pricing. So far, we only have the starting prices for these devices, including non-prescription lenses.
The setup here is similar to the Ray-Ban Meta glasses we’ve seen for a few years. There are no screens in the lenses, but you can interact with the AI system via voice or by activating the integrated camera. The experience should be similar to using Gemini Live on your phone, but it will be a lot easier to fire up the AI. You can say “Hey Gemini” or tap a touch-sensitive area of the frame to start interacting with the robot.
Since this is the same chatbot that operates across the Google ecosystem, it has access to your data and preferences. You can ask questions and get personalized answers, have Google Maps guide you by voice, or just talk with the AI to kill time. The glasses use custom open-ear speakers to limit distractions for those around you. Google notes the directional microphones should not pick up speech from other people, either.
Adding the camera feed is where things get interesting. When the AI can see what you see, it has the potential to do more work on your behalf. Google suggests asking Gemini for recommendations when looking at a bookshelf or glancing at an event poster to have the AI add it to your calendar. The glasses will also support Gemini Guided Vision, which provides conversational audio descriptions for people who are visually impaired.
The utility of these devices hinges on Gemini. I would be remiss not to point out that Gemini, like all AI systems, is not infallible. In fact, it can be frustratingly fallible at times. The chatbot still regularly screws up simple things like adding calendar appointments or identifying objects in an image in my testing, and when you don’t have a screen to verify the AI’s output, it may be harder to trust it. These devices will really only make sense if you can rely on Gemini to do things right, and that’s still not a guarantee. Google’s privacy promises
All the Gemini-powered glasses from Gentle Monster and Warby Parker feature a 12 MP wide-angle camera capable of shooting photos and video. Google says it has implemented a number of features and limitations to ensure people don’t do creepy things with its intelligent eyewear, and that it doesn’t do creepy things to you—Google claims its approach respects privacy on “both sides of the lens.”
For starters, there’s a recording light that is on whenever the camera is active. Like the Meta glasses, Google’s eyewear will detect if the light has been covered up or modified in any way that would prevent it from illuminating. In that event, the glasses will refuse to activate the camera. All Google-powered glasses will have a physical off switch, too.
The terms of use for Gemini eyewear also require users to agree not to record people without consent or in sensitive areas. If Google finds out someone has broken those rules, it may remotely disable the glasses. Google is going a bit further in restricting video functionality than Meta, too. Google says it will not allow any apps in the Play Store to live stream video to social media from the glasses (not even YouTube live is supported). The content you record is saved to your gallery, and you can upload that wherever you want, but going live is apparently not on the agenda. Real-time facial recognition is also off the table, according to Google. The glasses also automatically redact faces before sending video to Google for processing.
On the user privacy side, Google says it will not save any images or videos captured by the glasses in your Gemini history. Additionally, none of that data will be used for training AI models or targeting ads. Your voice interactions with Gemini via the glasses are, as with all other Gemini endpoints, not guaranteed the same level of protection. You can delete your chats from the Gemini history, though.
Data on the glasses is encrypted, and it remains that way during transit to the cloud. However, it’s not encrypted on Google’s servers. The company does note that it’s working to bring Private AI Compute to glasses, which will isolate data during processing so not even Google can access it.
Anyone looking to get Gemini on their face and test Google’s privacy promise can preorder the glasses from the Gentle Monster and Warby Parker websites. Devices should ship and appear on store shelves on December 10. Importantly, support for these devices is a bit narrow at launch. They will work with all iPhones from the 13 Pro onward. On the Android side, you’ll need a Pixel 7 or newer or a Samsung Galaxy S or Z series device running One UI 9 or later. If you’ve got a cheaper Samsung Galaxy or a device from another OEM, you’re out of luck at the moment.
Smartglasses have always faced an uphill road to acceptance. Not only is propping a computer up on your nose an uncomfortable proposition, but the privacy aspect has been vexing people since the Google Glass days. Now, Google is ready to take another swing at “intelligent eyewear” for the Gemini era after previewing its plans a couple of times. The first glasses are up for preorder today from Gentle Monster and Warby Parker, but they’re no impulse buy.
These devices are a collaboration between Google, Samsung, and the aforementioned eyewear designers. Gentle Monster and Warby Parker have each designed a few different frames, with options for transparent and tinted lenses. Samsung is providing the computing hardware that fits inside them, and Google has the software covered.
Warby Parker has designed three frames for Google eyewear, called Alden, Reid, and Wren (see above). They are available with both standard optical and sun lenses in Pine, Saddle, and Jet Black colors at $395 and higher. Warby Parker is only selling devices in the US. Gentle Monster has gone a bit further with six styles, but Google hasn’t told us any names for those yet. They come in dark red, pink, gray, and yellow colors and are available with clear, tinted, blue, or brown lenses. The Gentle Monster styles start a little higher at $449, and they will be available in the US and South Korea.
Google says the frames all weigh about 41 grams, which is not terrible but is definitely near the top for glasses generally. They will, naturally, weigh much more when you account for lenses. That will also determine the final pricing. So far, we only have the starting prices for these devices, including non-prescription lenses.
The setup here is similar to the Ray-Ban Meta glasses we’ve seen for a few years. There are no screens in the lenses, but you can interact with the AI system via voice or by activating the integrated camera. The experience should be similar to using Gemini Live on your phone, but it will be a lot easier to fire up the AI. You can say “Hey Gemini” or tap a touch-sensitive area of the frame to start interacting with the robot.
Since this is the same chatbot that operates across the Google ecosystem, it has access to your data and preferences. You can ask questions and get personalized answers, have Google Maps guide you by voice, or just talk with the AI to kill time. The glasses use custom open-ear speakers to limit distractions for those around you. Google notes the directional microphones should not pick up speech from other people, either.
Adding the camera feed is where things get interesting. When the AI can see what you see, it has the potential to do more work on your behalf. Google suggests asking Gemini for recommendations when looking at a bookshelf or glancing at an event poster to have the AI add it to your calendar. The glasses will also support Gemini Guided Vision, which provides conversational audio descriptions for people who are visually impaired.
The utility of these devices hinges on Gemini. I would be remiss not to point out that Gemini, like all AI systems, is not infallible. In fact, it can be frustratingly fallible at times. The chatbot still regularly screws up simple things like adding calendar appointments or identifying objects in an image in my testing, and when you don’t have a screen to verify the AI’s output, it may be harder to trust it. These devices will really only make sense if you can rely on Gemini to do things right, and that’s still not a guarantee. Google’s privacy promises
All the Gemini-powered glasses from Gentle Monster and Warby Parker feature a 12 MP wide-angle camera capable of shooting photos and video. Google says it has implemented a number of features and limitations to ensure people don’t do creepy things with its intelligent eyewear, and that it doesn’t do creepy things to you—Google claims its approach respects privacy on “both sides of the lens.”
For starters, there’s a recording light that is on whenever the camera is active. Like the Meta glasses, Google’s eyewear will detect if the light has been covered up or modified in any way that would prevent it from illuminating. In that event, the glasses will refuse to activate the camera. All Google-powered glasses will have a physical off switch, too.
The terms of use for Gemini eyewear also require users to agree not to record people without consent or in sensitive areas. If Google finds out someone has broken those rules, it may remotely disable the glasses. Google is going a bit further in restricting video functionality than Meta, too. Google says it will not allow any apps in the Play Store to live stream video to social media from the glasses (not even YouTube live is supported). The content you record is saved to your gallery, and you can upload that wherever you want, but going live is apparently not on the agenda. Real-time facial recognition is also off the table, according to Google. The glasses also automatically redact faces before sending video to Google for processing.
On the user privacy side, Google says it will not save any images or videos captured by the glasses in your Gemini history. Additionally, none of that data will be used for training AI models or targeting ads. Your voice interactions with Gemini via the glasses are, as with all other Gemini endpoints, not guaranteed the same level of protection. You can delete your chats from the Gemini history, though.
Data on the glasses is encrypted, and it remains that way during transit to the cloud. However, it’s not encrypted on Google’s servers. The company does note that it’s working to bring Private AI Compute to glasses, which will isolate data during processing so not even Google can access it.
Anyone looking to get Gemini on their face and test Google’s privacy promise can preorder the glasses from the Gentle Monster and Warby Parker websites. Devices should ship and appear on store shelves on December 10. Importantly, support for these devices is a bit narrow at launch. They will work with all iPhones from the 13 Pro onward. On the Android side, you’ll need a Pixel 7 or newer or a Samsung Galaxy S or Z series device running One UI 9 or later. If you’ve got a cheaper Samsung Galaxy or a device from another OEM, you’re out of luck at the moment.
no baked-in trackers/analytics, No VC backing, Big Tech parent, or crypto schemes. aggressive ad/tracker blocking, fingerprinting resistance, working YouTube ad blocking, extension support, smooth Android + Linux use.
What’s your daily driver under these constraints, and what tradeoff did you accept?
no baked-in trackers/analytics, No VC backing, Big Tech parent, or crypto schemes. aggressive ad/tracker blocking, fingerprinting resistance, working YouTube ad blocking, extension support, smooth Android + Linux use.
What’s your daily driver under these constraints, and what tradeoff did you accept?
cross-posted from: lemmy.today/post/63197390
found this on some telegram channel:
In February 2026, an employee of Paragon Solutions published a photograph on her LinkedIn profile depicting the operation of the Graphite spyware. The post has currently been deleted.
Reut Yamen holds the position of Chief Legal Counsel and Director of Compliance at the Israeli company Paragon Solutions, which specializes in cyber-surveillance technologies. The company was founded in 2019 by a group of former employees of Israeli intelligence services — among them Ehud Schneorson, former commander of Unit 8200 (Israel’s equivalent of the U.S. National Security Agency), as well as former Israeli Prime Minister Ehud Barak.
The post was first noticed by technology researcher Yurre van Bergen, who tracks the use and proliferation of spyware worldwide.
The image apparently shows a demonstration interface of the Graphite system. An operator can view messages intercepted from a surveillance target in various services, including WhatsApp, Telegram, Signal, Line, and TikTok.
According to the results of a large-scale investigation conducted by The Citizen Lab in 2025, in 2024 in Italy, dozens of journalists and private individuals were attacked via the WhatsApp messenger using Graphite. A “zero-click” exploit (one that does not require user interaction) was used for this purpose.
Paragon Solutions has (or previously had) contracts with U.S. government agencies, in particular the Drug Enforcement Administration (DEA) and Immigration and Customs Enforcement (ICE).
cross-posted from: lemmy.today/post/63197390
found this on some telegram channel:
In February 2026, an employee of Paragon Solutions published a photograph on her LinkedIn profile depicting the operation of the Graphite spyware. The post has currently been deleted.
Reut Yamen holds the position of Chief Legal Counsel and Director of Compliance at the Israeli company Paragon Solutions, which specializes in cyber-surveillance technologies. The company was founded in 2019 by a group of former employees of Israeli intelligence services — among them Ehud Schneorson, former commander of Unit 8200 (Israel’s equivalent of the U.S. National Security Agency), as well as former Israeli Prime Minister Ehud Barak.
The post was first noticed by technology researcher Yurre van Bergen, who tracks the use and proliferation of spyware worldwide.
The image apparently shows a demonstration interface of the Graphite system. An operator can view messages intercepted from a surveillance target in various services, including WhatsApp, Telegram, Signal, Line, and TikTok.
According to the results of a large-scale investigation conducted by The Citizen Lab in 2025, in 2024 in Italy, dozens of journalists and private individuals were attacked via the WhatsApp messenger using Graphite. A “zero-click” exploit (one that does not require user interaction) was used for this purpose.
Paragon Solutions has (or previously had) contracts with U.S. government agencies, in particular the Drug Enforcement Administration (DEA) and Immigration and Customs Enforcement (ICE).


Edit: Obsidian is a good privacy option, I like finding several apps that have features that I use, please don’t be under the impression that I’m calling out Obsidian. It is proprietary and not open source, and some may prefer open source instead.
I like Obsidian for the canvas option and just need a simple note taking app to keep track of projects and reference for clients, but it’s proprietary and not open-source, so I’m looking for options that are.
I honestly could put in some leg work and test the others but hoping to bypass the faff of that with your help. Do any of the following have a canvas I can copy/ paste, organize images, add text, I made an example.
Logseq
Silver bullet
Joplin
FUTO notes
Trilium Notes
Thanks!
Edit: Obsidian is a good privacy option, I like finding several apps that have features that I use, please don’t be under the impression that I’m calling out Obsidian. It is proprietary and not open source, and some may prefer open source instead.
I like Obsidian for the canvas option and just need a simple note taking app to keep track of projects and reference for clients, but it’s proprietary and not open-source, so I’m looking for options that are.
I honestly could put in some leg work and test the others but hoping to bypass the faff of that with your help. Do any of the following have a canvas I can copy/ paste, organize images, add text, I made an example.
Logseq
Silver bullet
Joplin
FUTO notes
Trilium Notes
Thanks!
I am sure there is a good reason for this. I am looking for alternatives to google, and these to be the ones that pop-up most often.
RESOLVED: I used up my 100 searches in kagi pretty quickly, and the experience was really nice. I am quite anti-subscription, so I won’t continue using it. I eliminated brave from my search due to the crypto stuff and whatnot. I am now using mojeek, which gave me better results over DDG when searching for niche stuff. Also I like mojeeks interface a lot more.
I am sure there is a good reason for this. I am looking for alternatives to google, and these to be the ones that pop-up most often.
RESOLVED: I used up my 100 searches in kagi pretty quickly, and the experience was really nice. I am quite anti-subscription, so I won’t continue using it. I eliminated brave from my search due to the crypto stuff and whatnot. I am now using mojeek, which gave me better results over DDG when searching for niche stuff. Also I like mojeeks interface a lot more.
Wonder on what you guys think about this, if the future of work requires us to use AI/AI agents, and this is tied to a personal account (tied to our ID) how will that change work and our lives? Every tiny mistake, any curiosity, any eureka moment or inefficiency, all of those will be recorded, tied to your identity, forever and ever to the end of time. It freaks me out…
Wonder on what you guys think about this, if the future of work requires us to use AI/AI agents, and this is tied to a personal account (tied to our ID) how will that change work and our lives? Every tiny mistake, any curiosity, any eureka moment or inefficiency, all of those will be recorded, tied to your identity, forever and ever to the end of time. It freaks me out…
With all the gov’t attacks on privacy these days I’ve been thinking about getting my own router. I’ve never done it and am pretty new to network stuff overall. I certainly welcome any recommendations for routers but I mainly have a stupid question:
Is it as simple as just swapping out the isp router? I’ve disconnected anything I had exposed to the internet and use LAN only right now so none of my old port forwarding rules are needed.
With all the gov’t attacks on privacy these days I’ve been thinking about getting my own router. I’ve never done it and am pretty new to network stuff overall. I certainly welcome any recommendations for routers but I mainly have a stupid question:
Is it as simple as just swapping out the isp router? I’ve disconnected anything I had exposed to the internet and use LAN only right now so none of my old port forwarding rules are needed.

Grok Build, the vibe-coding agent from SpaceXSI, is leaking data—some of it proprietary business information and other sensitive secrets—from thousands of its users, including the very same Elon Musk-owned company that offers the platform, new research shows.
The information is revealed through links allowing Grok Build users to share their apps with others. Grok takes steps to randomize the URLs so only people who know the exact URL can access the data stored there. A design decision by developers of the platform, however, completely torpedoes that objective and makes it possible for anyone to enumerate thousands of live Grok Build projects. Except in rare cases, clicking those links opens the app and reveals all data associated with it.
You had one job
Research from security firm Claroc shows that the exposed data includes things like internal business plans, ad proposals, medical exam results, galley checklists from a celebrity cruise line, and employee names and ID numbers. Ironically, some of the sensitive data comes from two-dozen apps built by SpaceXSI (the name of the now-merged SpaceX and xAI) itself. A small sampling of the documents revealed in the SpaceXSI apps—Claroc found 24 of them—include an onboarding plan, marked confidential, for a new member of SpaceXSI’s enterprise sales team, a sales territory map of 594 accounts, internal system addresses for sales team tools, and advertising proposals.
“We were shocked,” Claroc said in a Tuesday post. “The company that makes Grok had its own internal material open to anyone holding the link, and we had never been given it. Had the sales team bought a tool for this, it would have sat behind company sign-in, open only to the team. Built with AI, it went live open to anyone with the link.
Claroc notified SpaceXSI of the privacy spill on Sunday. When no one responded, a Claroc official took to X to tag both Musk and Grok Manager Matt Palmer about the threat. At the time this post went live almost all data remained available with one notable exception: the contents from the 24 SpaceXSI apps. All of them were exposing the information on Monday evening. SpaceXSI began removing the links within a few hours of Ars sending an email with questions for this article. At the time this post went live, links for all 24 apps returned an “app not found” error.
Claroc found sensitive data belonging to other Grok Build users, some working for Fortune 500 companies and a defense contractor. Some of the affected organizations and data revealed includes:
A Peruvian construction company: occupational-health dashboard with 3,784 worker medical exams

Tesla: service-center scorecard naming 22 technicians with productivity and bonus status

A US-Navy ship engineering contractor: roster of 108 people on a Navy logistics support contract

A leading luxury cruise company: a galley checklist for a celebrity cruise line listing crew by full name and employee ID

A healthcare company: hospital staff app with a roster of about 3,565 employees by name and ID

A US IT services company: a confidential proposal to a large retail customer with the hardware bill of materials

A Norwegian-Finnish aerospace and defense group: load board and loading procedure for an explosives building at a US plant, plus its HSE training matrix

A US home construction company: sales callsheet with about 583 home-buyer prospects, budgets and financing notes

A Malaysian holding company: project monitor for 37 developments with profit and sales figures

An auto transport company: quote desk with about 4,000 vehicle-transport orders, prices, and margins

A US data center colocation and hosting service: confidential IP transit proposal to a European carrier
Asaf Aprozper, the co-founder and CTO of Claroc, said he’s in the process of notifying companies. After speaking to the CISO of the luxury cruise company, it “pulled in their whole security team as soon as we shared the findings and are already working to contain the Grok exposure.”
A fatal flaw… shared by most other AI platforms
Link sharing for Grok Build is intended to streamline the process of developing and deploying apps. A user can input speech or text and have a working app ready for internal testing within minutes. The links are designed to give developers a way to get the app in front of authorized users quickly. The very left of the URLs contain two or more “dice words,” meaning randomly generated phrases such as “failing chassis traders,” although users can modify them. The rightmost portion of the link is grok.me. The URL for an X ads campaign plan was: cinder-crane-sand-frost.grok.me.
The scheme is intended to prevent links from being easily guessable. When done correctly, a phrase comprising three dice words has roughly 38 bits of entropy, amounting to billions of possible combinations. The idea—sometimes called capability-based access control—is that possession of the URL serves as authorization to the resources behind it. Google has long used this technique to make URLs easy to share but hard to guess. A URL share on that platform might look like: docs.google.com/document/d/…/edit
There’s a fatal flaw in the way SpaceXSI has implemented the mechanism. Instead of being to the right of the domain—as is the case with Google links—the randomness for Grok Build links is positioned to the left of it. That allows the links to be easily enumerated using passive DNS services. These services monitor central DNS lookup servers. When a server lookup requests the IP address of a previously never-before-seen URL, the transaction is captured in a publicly searchable database. Had Grok followed Google’s approach, the links would have been invisible to passive DNS searchers. Muse, the Meta agent that CEO Mark Zuckerberg said was built from the ground up for security, recently suspended a link-sharing feature after it too was found leaking sensitive data.
Aprozper said a passive DNS search returned 43,601 links ending in grok.me. Of them, more than 35,000, or nearly 95 percent, were public, meaning that clicking on the link opened the corresponding app and all data it stored. He said that tests he conducted over the past week showed that, by default, Grok sets links to “Anyone with the link.” Users have the option to change the setting to “invited users” or “only you.”
A representative with Cursor, the AI coding service SpaceXSI recently acquired, said in an email that Grok Build “apps are private by default and nothing goes public unless the creator chooses to share it.” The representative said that competing coding agents from ChatGPT, Lovable, and Bolt also give users the ability to generate shareable links.
Aprozper’s tests contradict the representative’s statement. In all cases, Grok Build required users to change anyone with the link to one of the other two options.
The Cursor statement regarding other AI coding platforms is correct. Aprozper said that app builders, including Lovable, Bolt, and Replit, “also give each app its own web address, so the same DNS records expose them, too. However, Grok is where we found by far the most sensitive company data.” That means that people using these other platforms are also at risk of exposing sensitive data through shared links. Interestingly, AI platforms that follow the correct sharing link practice include Claude’s published artifacts (claude.ai/public/artifacts/), ChatGPT’s shared conversations (chatgpt.com/share/), and Gemini (gemini.google.com/share/). For all three, the secret randomness is in the path, so DNS never sees it.
The representative didn’t respond to follow-up questions, including if SpaceXSI intentionally exposed the proprietary internal information, why the company removed the data after Ars asked about it, and if it planned to notify customers who also exposed similar types of information. Anyone using shareable links with Grok Build should choose the “invite others” option unless they intend to make an app widely available.
Grok Build, the vibe-coding agent from SpaceXSI, is leaking data—some of it proprietary business information and other sensitive secrets—from thousands of its users, including the very same Elon Musk-owned company that offers the platform, new research shows.
The information is revealed through links allowing Grok Build users to share their apps with others. Grok takes steps to randomize the URLs so only people who know the exact URL can access the data stored there. A design decision by developers of the platform, however, completely torpedoes that objective and makes it possible for anyone to enumerate thousands of live Grok Build projects. Except in rare cases, clicking those links opens the app and reveals all data associated with it.
You had one job
Research from security firm Claroc shows that the exposed data includes things like internal business plans, ad proposals, medical exam results, galley checklists from a celebrity cruise line, and employee names and ID numbers. Ironically, some of the sensitive data comes from two-dozen apps built by SpaceXSI (the name of the now-merged SpaceX and xAI) itself. A small sampling of the documents revealed in the SpaceXSI apps—Claroc found 24 of them—include an onboarding plan, marked confidential, for a new member of SpaceXSI’s enterprise sales team, a sales territory map of 594 accounts, internal system addresses for sales team tools, and advertising proposals.
“We were shocked,” Claroc said in a Tuesday post. “The company that makes Grok had its own internal material open to anyone holding the link, and we had never been given it. Had the sales team bought a tool for this, it would have sat behind company sign-in, open only to the team. Built with AI, it went live open to anyone with the link.
Claroc notified SpaceXSI of the privacy spill on Sunday. When no one responded, a Claroc official took to X to tag both Musk and Grok Manager Matt Palmer about the threat. At the time this post went live almost all data remained available with one notable exception: the contents from the 24 SpaceXSI apps. All of them were exposing the information on Monday evening. SpaceXSI began removing the links within a few hours of Ars sending an email with questions for this article. At the time this post went live, links for all 24 apps returned an “app not found” error.
Claroc found sensitive data belonging to other Grok Build users, some working for Fortune 500 companies and a defense contractor. Some of the affected organizations and data revealed includes:
A Peruvian construction company: occupational-health dashboard with 3,784 worker medical exams

Tesla: service-center scorecard naming 22 technicians with productivity and bonus status

A US-Navy ship engineering contractor: roster of 108 people on a Navy logistics support contract

A leading luxury cruise company: a galley checklist for a celebrity cruise line listing crew by full name and employee ID

A healthcare company: hospital staff app with a roster of about 3,565 employees by name and ID

A US IT services company: a confidential proposal to a large retail customer with the hardware bill of materials

A Norwegian-Finnish aerospace and defense group: load board and loading procedure for an explosives building at a US plant, plus its HSE training matrix

A US home construction company: sales callsheet with about 583 home-buyer prospects, budgets and financing notes

A Malaysian holding company: project monitor for 37 developments with profit and sales figures

An auto transport company: quote desk with about 4,000 vehicle-transport orders, prices, and margins

A US data center colocation and hosting service: confidential IP transit proposal to a European carrier
Asaf Aprozper, the co-founder and CTO of Claroc, said he’s in the process of notifying companies. After speaking to the CISO of the luxury cruise company, it “pulled in their whole security team as soon as we shared the findings and are already working to contain the Grok exposure.”
A fatal flaw… shared by most other AI platforms
Link sharing for Grok Build is intended to streamline the process of developing and deploying apps. A user can input speech or text and have a working app ready for internal testing within minutes. The links are designed to give developers a way to get the app in front of authorized users quickly. The very left of the URLs contain two or more “dice words,” meaning randomly generated phrases such as “failing chassis traders,” although users can modify them. The rightmost portion of the link is grok.me. The URL for an X ads campaign plan was: cinder-crane-sand-frost.grok.me.
The scheme is intended to prevent links from being easily guessable. When done correctly, a phrase comprising three dice words has roughly 38 bits of entropy, amounting to billions of possible combinations. The idea—sometimes called capability-based access control—is that possession of the URL serves as authorization to the resources behind it. Google has long used this technique to make URLs easy to share but hard to guess. A URL share on that platform might look like: docs.google.com/document/d/…/edit
There’s a fatal flaw in the way SpaceXSI has implemented the mechanism. Instead of being to the right of the domain—as is the case with Google links—the randomness for Grok Build links is positioned to the left of it. That allows the links to be easily enumerated using passive DNS services. These services monitor central DNS lookup servers. When a server lookup requests the IP address of a previously never-before-seen URL, the transaction is captured in a publicly searchable database. Had Grok followed Google’s approach, the links would have been invisible to passive DNS searchers. Muse, the Meta agent that CEO Mark Zuckerberg said was built from the ground up for security, recently suspended a link-sharing feature after it too was found leaking sensitive data.
Aprozper said a passive DNS search returned 43,601 links ending in grok.me. Of them, more than 35,000, or nearly 95 percent, were public, meaning that clicking on the link opened the corresponding app and all data it stored. He said that tests he conducted over the past week showed that, by default, Grok sets links to “Anyone with the link.” Users have the option to change the setting to “invited users” or “only you.”
A representative with Cursor, the AI coding service SpaceXSI recently acquired, said in an email that Grok Build “apps are private by default and nothing goes public unless the creator chooses to share it.” The representative said that competing coding agents from ChatGPT, Lovable, and Bolt also give users the ability to generate shareable links.
Aprozper’s tests contradict the representative’s statement. In all cases, Grok Build required users to change anyone with the link to one of the other two options.
The Cursor statement regarding other AI coding platforms is correct. Aprozper said that app builders, including Lovable, Bolt, and Replit, “also give each app its own web address, so the same DNS records expose them, too. However, Grok is where we found by far the most sensitive company data.” That means that people using these other platforms are also at risk of exposing sensitive data through shared links. Interestingly, AI platforms that follow the correct sharing link practice include Claude’s published artifacts (claude.ai/public/artifacts/), ChatGPT’s shared conversations (chatgpt.com/share/), and Gemini (gemini.google.com/share/). For all three, the secret randomness is in the path, so DNS never sees it.
The representative didn’t respond to follow-up questions, including if SpaceXSI intentionally exposed the proprietary internal information, why the company removed the data after Ars asked about it, and if it planned to notify customers who also exposed similar types of information. Anyone using shareable links with Grok Build should choose the “invite others” option unless they intend to make an app widely available.
cross-posted from: lemmy.ml/post/55185832
Hi everyone,
I’m looking for recommendations on free (or freemium) AI assistants that meet these criteria:
✅ Strong capabilities – Can handle complex questions and research. ✅ Privacy-respecting – Doesn’t train on user data, preferably E2E encrypted. ✅ Ethical stance – Not complicit in oppression or human rights violations (Palestine, sudan, uygur, etc). ✅ Not on BDS list – Companies that aren’t supporting or profiting from occupation.
Which AI tools have you found that respect both privacy AND human rights?
I’d really appreciate honest recommendations and experiences. Trying to find tools that align with my values without sacrificing functionality.
Thanks in advance! 🤝
cross-posted from: lemmy.ml/post/55185832
Hi everyone,
I’m looking for recommendations on free (or freemium) AI assistants that meet these criteria:
✅ Strong capabilities – Can handle complex questions and research. ✅ Privacy-respecting – Doesn’t train on user data, preferably E2E encrypted. ✅ Ethical stance – Not complicit in oppression or human rights violations (Palestine, sudan, uygur, etc). ✅ Not on BDS list – Companies that aren’t supporting or profiting from occupation.
Which AI tools have you found that respect both privacy AND human rights?
I’d really appreciate honest recommendations and experiences. Trying to find tools that align with my values without sacrificing functionality.
Thanks in advance! 🤝

One of the most based privacy youtuber in my opinion
One of the most based privacy youtuber in my opinion
It apprears that NextDNS has removed No Google, No Facebook, and other blocklist without notifying users. One person said the NSA blocklist was also down. The company had made no responses to complaints on the community server when I checked earlier. Crickets…
I noticed Android and Linux being unable to access the app and web interface to confirm connections, starting some time on November 4th. I was able to switch DNS providers on Android and switch back, after which NextDNS seemed to work. On Linux however, systemd confirmed it was enabled but it went right to google’s webpage with no block.
If you’re on NextDNS, go check your domain filters ASAP. I switched to RethinkDNS, and it’s been decent so far. What is everyones preferred solution?
It apprears that NextDNS has removed No Google, No Facebook, and other blocklist without notifying users. One person said the NSA blocklist was also down. The company had made no responses to complaints on the community server when I checked earlier. Crickets…
I noticed Android and Linux being unable to access the app and web interface to confirm connections, starting some time on November 4th. I was able to switch DNS providers on Android and switch back, after which NextDNS seemed to work. On Linux however, systemd confirmed it was enabled but it went right to google’s webpage with no block.
If you’re on NextDNS, go check your domain filters ASAP. I switched to RethinkDNS, and it’s been decent so far. What is everyones preferred solution?
Developers of virtual private network (VPN) apps are reporting that their products are again being pulled from Apple’s App Store in Russia. This is an unacceptable crackdown on a vital tool to protect privacy and speech online. Why? VPNs give people a way to control their own online activities. When you visit a website through…
Developers of virtual private network (VPN) apps are reporting that their products are again being pulled from Apple’s App Store in Russia. This is an unacceptable crackdown on a vital tool to protect privacy and speech online. Why? VPNs give people a way to control their own online activities. When you visit a website through…
Decidim - A digital platform for participation and community governance.
Some interesting panel discussions and presentations, mostly related to digital privacy, freedom, democracy and empowerment.
Decidim - A digital platform for participation and community governance.
Some interesting panel discussions and presentations, mostly related to digital privacy, freedom, democracy and empowerment.

cross-posted from: lemmy.world/post/54248497
Bluesky, keep your “Age Assurance”, I’m definitely not going to upload my ID, biometrics or anything else to your partner “Kids Web Services”
Would never trust their parent company Epic Games (owned by Disney / Tencent…)
Luckily there are plenty of ways to bypass this: gist.github.com/…/e92af851c2d2d015c67aaa0170baaef…
Privacy Matters!
cross-posted from: lemmy.world/post/54248497
Bluesky, keep your “Age Assurance”, I’m definitely not going to upload my ID, biometrics or anything else to your partner “Kids Web Services”
Would never trust their parent company Epic Games (owned by Disney / Tencent…)
Luckily there are plenty of ways to bypass this: gist.github.com/…/e92af851c2d2d015c67aaa0170baaef…
Privacy Matters!

Stolen from 4chan. What do you think?
Stolen from 4chan. What do you think?

cross-posted from: lemmy.world/post/54244922
Guess they are opening up about how they be using AI, as invasively as possible, to completely analyze and categorize all users:
“…use AI to analyze entire profiles for contextual clues, such as birthday celebrations or mentions of school grades…The company also looks at visual cues from photos and videos, including a person’s height or bone structure.”
Good excuse to collect biometrics!
cross-posted from: lemmy.world/post/54244922
Guess they are opening up about how they be using AI, as invasively as possible, to completely analyze and categorize all users:
“…use AI to analyze entire profiles for contextual clues, such as birthday celebrations or mentions of school grades…The company also looks at visual cues from photos and videos, including a person’s height or bone structure.”
Good excuse to collect biometrics!
Hi all,
I’m planning to set up outdoor security cameras (garden and garage) and want to do it fully local, with no cloud.
My constraints:
Questions:
Thanks!
Hi all,
I’m planning to set up outdoor security cameras (garden and garage) and want to do it fully local, with no cloud.
My constraints:
Questions:
Thanks!
I’m looking for a robust translation app that respect privacy and doesn’t collect user data or send text to servers.
I’ve tried a few options, but I’d like to hear about your experiences: What do you actually use?
Thanks in advance 🙏
I’m looking for a robust translation app that respect privacy and doesn’t collect user data or send text to servers.
I’ve tried a few options, but I’d like to hear about your experiences: What do you actually use?
Thanks in advance 🙏
By Erica C. Barnett The NYU Policing Project released its long-awaited privacy and civil-liberties audit of the Seattle Police…
By Erica C. Barnett The NYU Policing Project released its long-awaited privacy and civil-liberties audit of the Seattle Police…
it’s difficult to find information on the topic which is why i’m posting here. a large number, likely a majority, of tor nodes are based in fourteen eyes countries. having both your entrance and exit nodes monitored (say, by their ISPs) opens you up to a more-or-less trivial timing correlation attack. on the other hand, blocking huge swaths of the network, according to the tor project, can open you up to deanonymization too.
it’s often been said that if your adversary is the intelligence agencies, you’re fucked anyway. that’s more than reasonable for active attacks. i don’t think that’s necessarily true for passive dragnet surveillance. so my question is, has anyone considered this particular vector of attack? is it better to block fourteen eyes or not? is it even worth asking the question?
it’s difficult to find information on the topic which is why i’m posting here. a large number, likely a majority, of tor nodes are based in fourteen eyes countries. having both your entrance and exit nodes monitored (say, by their ISPs) opens you up to a more-or-less trivial timing correlation attack. on the other hand, blocking huge swaths of the network, according to the tor project, can open you up to deanonymization too.
it’s often been said that if your adversary is the intelligence agencies, you’re fucked anyway. that’s more than reasonable for active attacks. i don’t think that’s necessarily true for passive dragnet surveillance. so my question is, has anyone considered this particular vector of attack? is it better to block fourteen eyes or not? is it even worth asking the question?
From Twitter/X:
Big Tech companies block law that would protect children 😡🚩
Google, Meta and TikTok are suing California to block a law that would protect teenagers from its exploitative and addicted-making features📱
Question: If you’re a parent, how do you navigate social media use with your child/children? 💭
This is your sign to ditch Big Tech and look for alternatives 🔐
More information about ethical alternatives 👉 tuta.com/blog/degoogle-list
From Twitter/X:
Big Tech companies block law that would protect children 😡🚩
Google, Meta and TikTok are suing California to block a law that would protect teenagers from its exploitative and addicted-making features📱
Question: If you’re a parent, how do you navigate social media use with your child/children? 💭
This is your sign to ditch Big Tech and look for alternatives 🔐
More information about ethical alternatives 👉 tuta.com/blog/degoogle-list
I’m guessing that the answer is yes, but maybe someone with 1st hand experience or any sort of expertise may want to weigh in?
I really just want to order cookware from a German company that no longer ships to the US (given the toddler tantrums that have replaced our trade policy, I don’t blame them). I think reshipping companies in the EU all have to get some sort of ID verification to combat credit card fraud (side note: I live in the US so I can hardly throw stones but WTF EU? It seems like a terrible privacy law enacted to protect banks?).
Anyway, if I want to use the service, this is the deal:
We take the protection of your data very seriously, especially when it is about your identity data. Our partner for verifying your identity is Veriff, a well-known and trusted KYC provider. They will securely store your data and only transmit the status of your verification to our system. Of course your data will never be disclosed to third parties.
Feels yucky, but maybe I’m being paranoid? Pretty much everyone in my country has already been boned by Experian and Social Security leaks already 🤷🏾
I’m guessing that the answer is yes, but maybe someone with 1st hand experience or any sort of expertise may want to weigh in?
I really just want to order cookware from a German company that no longer ships to the US (given the toddler tantrums that have replaced our trade policy, I don’t blame them). I think reshipping companies in the EU all have to get some sort of ID verification to combat credit card fraud (side note: I live in the US so I can hardly throw stones but WTF EU? It seems like a terrible privacy law enacted to protect banks?).
Anyway, if I want to use the service, this is the deal:
We take the protection of your data very seriously, especially when it is about your identity data. Our partner for verifying your identity is Veriff, a well-known and trusted KYC provider. They will securely store your data and only transmit the status of your verification to our system. Of course your data will never be disclosed to third parties.
Feels yucky, but maybe I’m being paranoid? Pretty much everyone in my country has already been boned by Experian and Social Security leaks already 🤷🏾
Protonmail.uservoice.com is supposedly “The Voice of the Proton Community”. Well last week I was tracking a post that was rising rapidly to the top-most voted in the “general ideas” category. And this morning when I went to check if it was at the top yet, it’s just gone without a trace. No sign that it was ever there.
Protonmail.uservoice.com is supposedly “The Voice of the Proton Community”. Well last week I was tracking a post that was rising rapidly to the top-most voted in the “general ideas” category. And this morning when I went to check if it was at the top yet, it’s just gone without a trace. No sign that it was ever there.
Hi everyone,
I currently use Telegram to send photos, PDFs and text messages between my Android phone and my Debian laptop. It works, but everything goes through a third-party server, and I would like a fully local, privacy-friendly alternative.
What I need: Send photos, PDFs and other files in both directions (phone ↔ laptop) Send short text messages or clipboard content Works locally
Thanks for any advice and experience!
Hi everyone,
I currently use Telegram to send photos, PDFs and text messages between my Android phone and my Debian laptop. It works, but everything goes through a third-party server, and I would like a fully local, privacy-friendly alternative.
What I need: Send photos, PDFs and other files in both directions (phone ↔ laptop) Send short text messages or clipboard content Works locally
Thanks for any advice and experience!
Penlink’s Webloc is sold to police in the US, UK and worldwide. It uses technology found in weather, gaming, email and religious apps to locate people using their cellphones.
In presentations prepared last year for international law enforcement agencies, representatives of US digital intelligence company Penlink showed off their flagship technology, Webloc. They demonstrated the system tracking people as they walked down Fifth Avenue in New York City, visited the European Central Bank in Frankfurt, and moved close to the UK Parliament in central London.
The presentations said that Webloc, originally developed by an Israeli startup, Cobwebs, can track hundreds of millions of mobile phones across the world. For law enforcement, that’s a powerful capability — made more so by the fact that in the US it can be used without the need for any kind of search warrant or judicial authorization.
Penlink’s Webloc is sold to police in the US, UK and worldwide. It uses technology found in weather, gaming, email and religious apps to locate people using their cellphones.
In presentations prepared last year for international law enforcement agencies, representatives of US digital intelligence company Penlink showed off their flagship technology, Webloc. They demonstrated the system tracking people as they walked down Fifth Avenue in New York City, visited the European Central Bank in Frankfurt, and moved close to the UK Parliament in central London.
The presentations said that Webloc, originally developed by an Israeli startup, Cobwebs, can track hundreds of millions of mobile phones across the world. For law enforcement, that’s a powerful capability — made more so by the fact that in the US it can be used without the need for any kind of search warrant or judicial authorization.
I’ve checked Exodus: the main score apps (FotMob, 365Scores, Yalla Shoot) all carry 10+ trackers each. I found a few hobby projects on GitHub but nothing mature.
Does anyone here use an open-source app for live scores they’d actually recommend?
I’ve checked Exodus: the main score apps (FotMob, 365Scores, Yalla Shoot) all carry 10+ trackers each. I found a few hobby projects on GitHub but nothing mature.
Does anyone here use an open-source app for live scores they’d actually recommend?