0

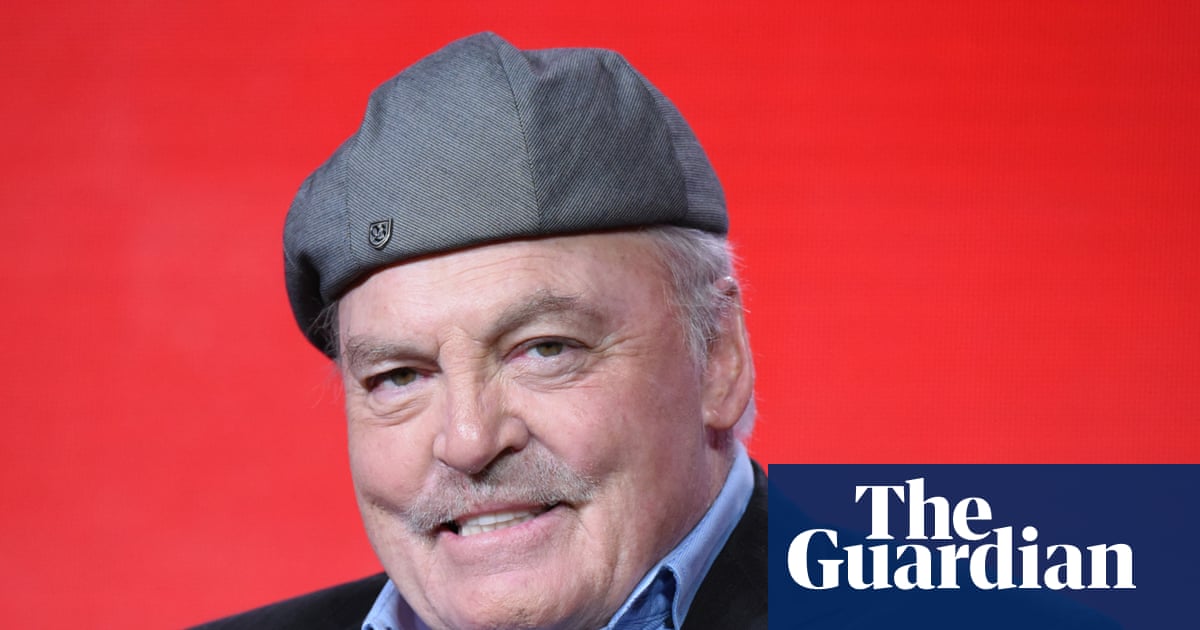
Stacy Keach, Mike Hammer actor whose career spanned stage and screen, dies aged 85

the Guardian Stacy Keach, Mike Hammer actor whose career spanned stage and screen, dies aged 85 www.theguardian.com
preview

cross-posted from: lemmy.world/post/54269690

Stacy Keach, one of America’s finest stage actors who became best known for playing scruffy private eye Mike Hammer on TV and whose career was nearly derailed after he was imprisoned in 1984 for trying to smuggle cocaine into Britain, has died aged 85.

cross-posted from: lemmy.world/post/54269690

Stacy Keach, one of America’s finest stage actors who became best known for playing scruffy private eye Mike Hammer on TV and whose career was nearly derailed after he was imprisoned in 1984 for trying to smuggle cocaine into Britain, has died aged 85.

0

How Abdul El-Sayed's critics smeared his defence of Palestinians as 'hate'

Middle East Eye How Abdul El-Sayed's critics smeared his defence of Palestinians as 'hate' www.middleeasteye.net
preview

In Michigan, the accusation of hate failed to buy the Senate seat, but the currency itself still circulates. “Hate” will outlive the ballot. It is the keyword of American politics around Muslim candidates, Arabs and Palestine. In practice, its working opposite was not “love”, as Sayed claimed. It was unity.

Democrats staged unity events, and Sayed called former Vice President Kamala Harris’s visit a matter of unity, standing with a leader of the administration that armed Israel’s genocide in Gaza. Former President Barack Obama, whose drone wars killed Muslims from Pakistan to Yemen, came too.

In Michigan, the accusation of hate failed to buy the Senate seat, but the currency itself still circulates. “Hate” will outlive the ballot. It is the keyword of American politics around Muslim candidates, Arabs and Palestine. In practice, its working opposite was not “love”, as Sayed claimed. It was unity.

Democrats staged unity events, and Sayed called former Vice President Kamala Harris’s visit a matter of unity, standing with a leader of the administration that armed Israel’s genocide in Gaza. Former President Barack Obama, whose drone wars killed Muslims from Pakistan to Yemen, came too.

0

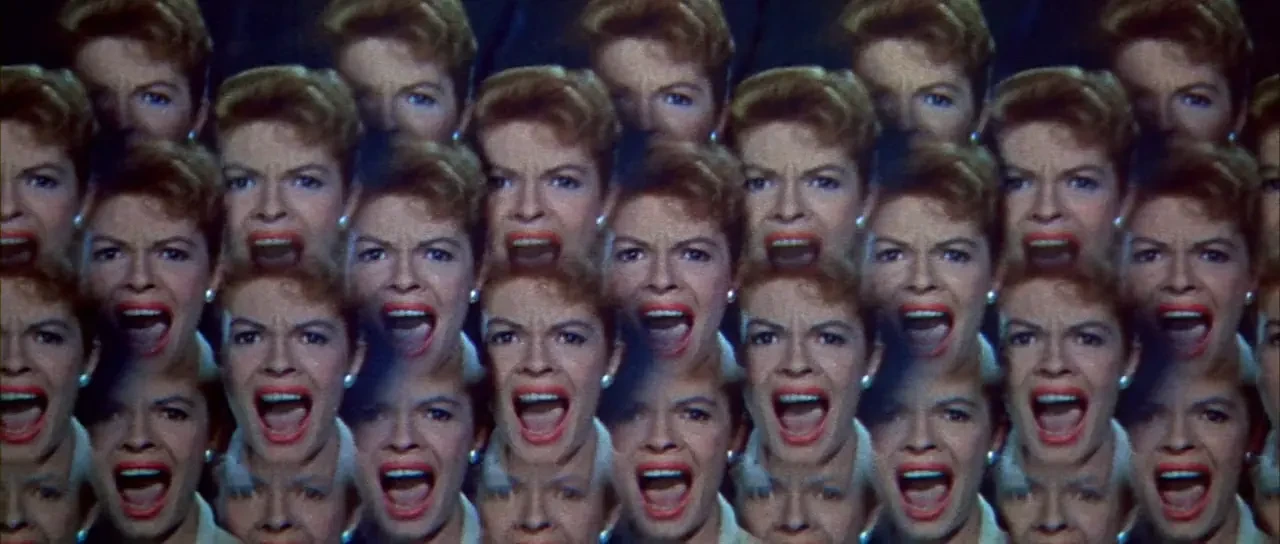
The Fly, Kurt Neumann (1958)

A view of a woman screaming, repeated many times as though viewed from a compound eye.
preview

Hélène (Patricia Owens) screaming as she sees how her husband André (David Heddison) has been transformed into a part-fly creature, from the point of view of André now that he has fly-like compound eyes.

Hélène (Patricia Owens) screaming as she sees how her husband André (David Heddison) has been transformed into a part-fly creature, from the point of view of André now that he has fly-like compound eyes.

0

Ich höre im Radio das laut einer neuen Studie das Vertrauen der Menschen in die Demokratie abnimmt...

preview

Ich höre im Radio das laut einer neuen Studie das Vertrauen der Menschen in die Demokratie abnimmt…

…und frage mich ob nicht viel mehr das Vertrauen in den Parlamentarismus, unser System das man uns als Demokratie verkauft abnimmt.

Ob die Demokratie oder das was wir hier in Deutschland daraus gemacht haben das Problem ist. Ich tippe nämlich genau darauf!

#Meinung #Demokratie #Zuspruch #Deutschland #Studie #Radio @deutschland

Ich höre im Radio das laut einer neuen Studie das Vertrauen der Menschen in die Demokratie abnimmt…

…und frage mich ob nicht viel mehr das Vertrauen in den Parlamentarismus, unser System das man uns als Demokratie verkauft abnimmt.

Ob die Demokratie oder das was wir hier in Deutschland daraus gemacht haben das Problem ist. Ich tippe nämlich genau darauf!

#Meinung #Demokratie #Zuspruch #Deutschland #Studie #Radio @deutschland

0

Fallout 76 Daily Update

preview

Atomic Shop

  • Soft Serve Paint (Cryolator) (250⚛️ (50% off!)), Leaves on (12-Nov-2026)
  • Abandoned Nest (Free (FO1st)), Leaves on (1-Dec-2026)
  • Speckled Axolotl Plushie (Free), Leaves on (1-Dec-2026)
  • Quantum Paint (Cryolator) (500⚛️), Leaves on (1-Dec-2026)
  • Vat of FEV (500⚛️), Leaves on (1-Dec-2026)
  • Deathclaw Delight Bundle (1500⚛️), Leaves on (1-Dec-2026)
  • Vault 76 Anniversary Bundle (Fallout 1st) (1200⚛️), Leaves on (1-Dec-2026)
  • Assaultron Assembly Platform (500⚛️), Leaves on (1-Dec-2026)
  • Anniversary Parade Float (600⚛️), Leaves on (1-Dec-2026)
  • Nuka-Cola Collectibles Bundle (Fallout 1st) (1000⚛️), Leaves on (1-Dec-2026)
  • Fallout Fanatic Bundle (2000⚛️), Leaves on (1-Dec-2026)
  • Enclave Endurance Trainer (500⚛️), Leaves on (1-Dec-2026)

Current Events

  • ANNIVERSARY EVENTS, Ends on (17-Nov-2026)
  • Season 26: Beware the Blood Moon, Ends on (1-Dec-2026)

Fishing

  • Speckled Axolotl, Regions: Cranberry Bog & Forest, Changes on: (1-Dec-2026)
  • Festerkoi, Regions: Ash Heap, Burning Springs, Toxic Valley, Changes on: (22-Dec-2026)
  • Sludge Eye, Location: The Sludge Works, Changes on: (22-Dec-2026)

Daily Challenges

  • 1ˢᵗ Drink Nuka-Cola (x3) 250
  • ⭐ Gold Star: Complete a Daily Challenge (x6) 1000
  • Build a Decoration in a Shelter (x5) 250
  • Collect a Teddy Bear (x3) 250
  • Eat a Cooked Meal (x10) 250
  • Kill a Festive Scorched (x10) 250
  • Kill a Honey Beast (x1) 250
  • Kill a Radhog (x5) 250

Minerva’s Location: Away She will next be at The Whitespring Resort on 12-Nov-2026

Daily OPS: Uplink

  • Location: Glassed Caverns
  • Enemy Faction: Pint-Sized Phantoms
  • Enemy Mutations: Piercing Gaze, Freezing Touch

Atomic Shop

  • Soft Serve Paint (Cryolator) (250⚛️ (50% off!)), Leaves on (12-Nov-2026)
  • Abandoned Nest (Free (FO1st)), Leaves on (1-Dec-2026)
  • Speckled Axolotl Plushie (Free), Leaves on (1-Dec-2026)
  • Quantum Paint (Cryolator) (500⚛️), Leaves on (1-Dec-2026)
  • Vat of FEV (500⚛️), Leaves on (1-Dec-2026)
  • Deathclaw Delight Bundle (1500⚛️), Leaves on (1-Dec-2026)
  • Vault 76 Anniversary Bundle (Fallout 1st) (1200⚛️), Leaves on (1-Dec-2026)
  • Assaultron Assembly Platform (500⚛️), Leaves on (1-Dec-2026)
  • Anniversary Parade Float (600⚛️), Leaves on (1-Dec-2026)
  • Nuka-Cola Collectibles Bundle (Fallout 1st) (1000⚛️), Leaves on (1-Dec-2026)
  • Fallout Fanatic Bundle (2000⚛️), Leaves on (1-Dec-2026)
  • Enclave Endurance Trainer (500⚛️), Leaves on (1-Dec-2026)

Current Events

  • ANNIVERSARY EVENTS, Ends on (17-Nov-2026)
  • Season 26: Beware the Blood Moon, Ends on (1-Dec-2026)

Fishing

  • Speckled Axolotl, Regions: Cranberry Bog & Forest, Changes on: (1-Dec-2026)
  • Festerkoi, Regions: Ash Heap, Burning Springs, Toxic Valley, Changes on: (22-Dec-2026)
  • Sludge Eye, Location: The Sludge Works, Changes on: (22-Dec-2026)

Daily Challenges

  • 1ˢᵗ Drink Nuka-Cola (x3) 250
  • ⭐ Gold Star: Complete a Daily Challenge (x6) 1000
  • Build a Decoration in a Shelter (x5) 250
  • Collect a Teddy Bear (x3) 250
  • Eat a Cooked Meal (x10) 250
  • Kill a Festive Scorched (x10) 250
  • Kill a Honey Beast (x1) 250
  • Kill a Radhog (x5) 250

Minerva’s Location: Away She will next be at The Whitespring Resort on 12-Nov-2026

Daily OPS: Uplink

  • Location: Glassed Caverns
  • Enemy Faction: Pint-Sized Phantoms
  • Enemy Mutations: Piercing Gaze, Freezing Touch
0

HDMI to audio/video output I used for my CRT

preview

I got a ton of questions asking how I set up my steamdeck to my CRT. This is the specific adapter, although theres actually a ton out there just like this one, but it works. Just FYI, the plastic case is super cheap.

I got it in 2022 and it still works. Although Ive had to repair it once. It was outside for a little bit and the plastic got warped.

I got a ton of questions asking how I set up my steamdeck to my CRT. This is the specific adapter, although theres actually a ton out there just like this one, but it works. Just FYI, the plastic case is super cheap.

I got it in 2022 and it still works. Although Ive had to repair it once. It was outside for a little bit and the plastic got warped.

0

Daily community recommendation: !canada@lemmy.ca

preview

Canada— Join Canada’s community for daily news and discussions, where top posts like Alberta’s vote get shared.

12,640 subscribers
49 posts per month
297 comments per month

What’s going on Canada?

Sample discussion: Alberta votes to stay in Canada, CBC News projects (209 votes, 85 comments)

➡️ !canada@lemmy.ca (lemmy.ca/c/canada)

Know an underrated community? Send the bot a private message with !suggest !community@instance and it joins the candidate pool.

Canada— Join Canada’s community for daily news and discussions, where top posts like Alberta’s vote get shared.

12,640 subscribers
49 posts per month
297 comments per month

What’s going on Canada?

Sample discussion: Alberta votes to stay in Canada, CBC News projects (209 votes, 85 comments)

➡️ !canada@lemmy.ca (lemmy.ca/c/canada)

Know an underrated community? Send the bot a private message with !suggest !community@instance and it joins the candidate pool.

0

Sleepy yorkie on the couch

preview

Bruno is a little over 70 in dog years. He may struggle to get on the couch, but he never struggles to get to my heart.

Bruno is a little over 70 in dog years. He may struggle to get on the couch, but he never struggles to get to my heart.

0

Entity 150

preview

Oculi Fungorum are small, red mushrooms found within grassy plains. Their appearance is similar to an Amanita muscaria, circular red caps with white warts all over. They usually have a veil underneath the cap and have a usually white or beige stipe. When taken out of their position (not recommended) they don’t leave behind any mycelium or anything underground. Oculi Fungorum are entities and not mushrooms, despite their fungal looks, as inside them you can find bone structure, muscle, organs and more. They contain gills…

Oculi Fungorum are small, red mushrooms found within grassy plains. Their appearance is similar to an Amanita muscaria, circular red caps with white warts all over. They usually have a veil underneath the cap and have a usually white or beige stipe. When taken out of their position (not recommended) they don’t leave behind any mycelium or anything underground. Oculi Fungorum are entities and not mushrooms, despite their fungal looks, as inside them you can find bone structure, muscle, organs and more. They contain gills…

0

Hillthorn: un gioco investigativo con le carte

OneUpNerd Hillthorn: Review - OneUpNerd oneupnerd.com
preview

Hillthorn: un gioco investigativo con le carte

@videogiochi

Hillthorn è un videogioco investigativo che utilizza le carte per interfacciarsi con il giocatore. Niente testi, solo carte.
Un’esperienza travolgente che ci porta ad investigare su una strana setta in cima ad una montagna.

https://oneupnerd.com/review/hillthorn-review/

#videogiochi #investigazione #indie

Hillthorn: un gioco investigativo con le carte

@videogiochi

Hillthorn è un videogioco investigativo che utilizza le carte per interfacciarsi con il giocatore. Niente testi, solo carte.
Un’esperienza travolgente che ci porta ad investigare su una strana setta in cima ad una montagna.

https://oneupnerd.com/review/hillthorn-review/

#videogiochi #investigazione #indie

0

The Golden State Killer never anticipated DNA Evidence, much like those who commit thought crimes today haven't anticipated the mind reading laser of 2050 CE

preview

Yes YOU. Filthy Thought Sinner.

We’re watching you!

-Sincerely, the Department of Temporal Justice, United Empire of Earth

Yes YOU. Filthy Thought Sinner.

We’re watching you!

-Sincerely, the Department of Temporal Justice, United Empire of Earth

0

Report: Sources inside TKO cite frustration with 'gross' decision to stage events in Middle East amid conflict

POST Wrestling | Podcasts, News, Reviews | WWE AEW NXT NJPW Report: Sources inside TKO cite frustration with 'gross' decision to stage events in Middle East amid conflict - POST Wrestling | Podcasts, News, Reviews | WWE AEW NXT NJPW www.postwrestling.com
preview

A new report has uncovered some of the frustrations inside TKO Group Holdings amid the company’s recent stretch of events in the Middle East.

TKO-owned properties like WWE, UFC, and Zuffa Boxing all remain scheduled to visit the Middle East in the coming months for events, this despite the region currently being in conflict.

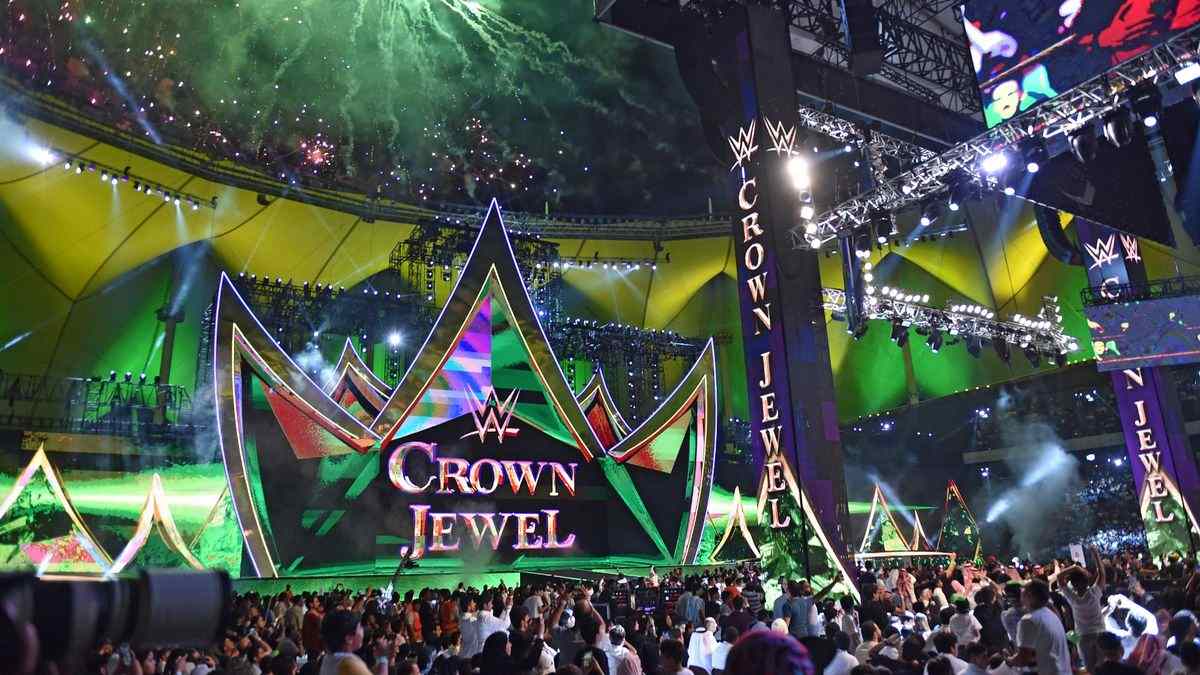
UFC is planning to visit Riyadh, Saudi Arabia, on December 5 for a Fight Night card. This Saturday, Zuffa Boxing will be in the country for an event. And WWE, which was in the country just days ago for Crown Jewel, is expected to return next year for WrestleMania.

The push to host the events is sustained despite Saudi Arabia suffering numerous attacks from the Houthi militia in recent months – including an attack which left over 300 injured and 13 dead – has left many in the company frustrated.

A series of anonymous sources inside the company recently told Ben Fowlkes of Yahoo!’s Uncrowned about their frustration:

Why are you still even having these shows at this point? I think the answer is, if they chose not to do the show, they would lose out on millions and millions of dollars. If we don’t do the shows in Saudi Arabia or [United Arab Emirates] or Doha or wherever we are going, then our fourth-quarter earnings will be off and our shareholders aren’t going to get their money. So it’s all about greed. They don’t care about anybody’s well-being. The level of greed with this company is so gross.

During TKO’s Q3 earnings call last week, company President Mark Shapiro said the risk of events getting cancelled in the region this year was “extremely minimal,” and said the operation was “all systems go.”

POST’s Brandon Thurston previously reported that Shapiro assured TKO employees during a town hall that the company “would not hesitate” to cancel events in the region if any conflict escalated.

Uncrowned reached out to TKO for comment before publishing their story but didn’t receive a response.

Uncrowned spoke with a source who expressed frustration that contingency plans haven’t been made public: “Not one email has gone out saying, ‘Here are the details and the plans for December 5th.’ That’s crazy. They don’t tell you anything. They just throw it at you. How about a backup plan? How about a safety letter? ‘Hey, if x happens, we go do y. We’ll all meet here. We’ll do this. We’ll do that.’ Nothing.”

A source told Uncrowned that many inside the company are discussing whether they could get out of having to work events in the region.

Everyone is talking about the Middle East shows. Who has to go, who can get out of going. Some people say they are waiting until the time to fly comes and telling [executives] that they won’t go. But I don’t know how many will follow through with that. This is a company that can fire you for no reason or any reason. Everyone just can’t believe this is a choice that they are being forced to make — fly into a war zone or risk getting fired before Christmas.

Uncrowned’s report can be read here.

A new report has uncovered some of the frustrations inside TKO Group Holdings amid the company’s recent stretch of events in the Middle East.

TKO-owned properties like WWE, UFC, and Zuffa Boxing all remain scheduled to visit the Middle East in the coming months for events, this despite the region currently being in conflict.

UFC is planning to visit Riyadh, Saudi Arabia, on December 5 for a Fight Night card. This Saturday, Zuffa Boxing will be in the country for an event. And WWE, which was in the country just days ago for Crown Jewel, is expected to return next year for WrestleMania.

The push to host the events is sustained despite Saudi Arabia suffering numerous attacks from the Houthi militia in recent months – including an attack which left over 300 injured and 13 dead – has left many in the company frustrated.

A series of anonymous sources inside the company recently told Ben Fowlkes of Yahoo!’s Uncrowned about their frustration:

Why are you still even having these shows at this point? I think the answer is, if they chose not to do the show, they would lose out on millions and millions of dollars. If we don’t do the shows in Saudi Arabia or [United Arab Emirates] or Doha or wherever we are going, then our fourth-quarter earnings will be off and our shareholders aren’t going to get their money. So it’s all about greed. They don’t care about anybody’s well-being. The level of greed with this company is so gross.

During TKO’s Q3 earnings call last week, company President Mark Shapiro said the risk of events getting cancelled in the region this year was “extremely minimal,” and said the operation was “all systems go.”

POST’s Brandon Thurston previously reported that Shapiro assured TKO employees during a town hall that the company “would not hesitate” to cancel events in the region if any conflict escalated.

Uncrowned reached out to TKO for comment before publishing their story but didn’t receive a response.

Uncrowned spoke with a source who expressed frustration that contingency plans haven’t been made public: “Not one email has gone out saying, ‘Here are the details and the plans for December 5th.’ That’s crazy. They don’t tell you anything. They just throw it at you. How about a backup plan? How about a safety letter? ‘Hey, if x happens, we go do y. We’ll all meet here. We’ll do this. We’ll do that.’ Nothing.”

A source told Uncrowned that many inside the company are discussing whether they could get out of having to work events in the region.

Everyone is talking about the Middle East shows. Who has to go, who can get out of going. Some people say they are waiting until the time to fly comes and telling [executives] that they won’t go. But I don’t know how many will follow through with that. This is a company that can fire you for no reason or any reason. Everyone just can’t believe this is a choice that they are being forced to make — fly into a war zone or risk getting fired before Christmas.

Uncrowned’s report can be read here.

0

Au procès de Michel Zecler, accusé de s'être fait frapper par trois policiers

Blast le souffle de l’info Au procès de Michel Zecler, accusé de s'être fait frapper par trois policiers www.blast-info.fr
preview

Il y a six ans, Michel Zecler était passé à tabac dans son studio d’enregistrement par trois policiers avant que les images ne deviennent emblématiques des violences policières. Au procès, entre les éloges reçus par les fonctionnaires, les procédures…

Il y a six ans, Michel Zecler était passé à tabac dans son studio d’enregistrement par trois policiers avant que les images ne deviennent emblématiques des violences policières. Au procès, entre les éloges reçus par les fonctionnaires, les procédures…

0

Bękarty dokolonizacji | transmisje. Dekolonialne rozmowy o świecie vol. 5 - 12.11.2026

preview

cross-posted from: szmer.info/post/17053244

Bękarty dekolonizacji. O tym jak siła podporządkowanych zmienia historię. 👉 12 listopada, godz.19:00 Kaliska 8/10 Wstęp wolny

Historycy dotychczas opowiadali o imperiach, zwykle skupiając się na ich chwale, rzadziej na popełnianych w ich imieniu zbrodniach. Idzie jednak o to, by dostrzec tych, którzy zdolni są imperia obalać. Tych, dla których dekolonizacja nie była ideą polityczną, ale potrzebą wyrastającą z doświadczenia codziennych upokorzeń, nędzy i niesprawiedliwości. Na początku lat. 80. XX wieku taką właśnie perspektywę w opowiadaniu o rzeczywistości społeczeństw pod panowaniem kolonialnym przyjęła grupa indyjskich historyków. Ich podejście, które nazwano Subaltern Studies, czyli badaniami nad podporządkowanymi, zrewolucjonizowało sposób uprawiania historii, ale także to jak myślimy o procesach społecznych rozgrywających się współcześnie. Chłopi, niewolnicy, kobiety, plebejusze wszystkich płci, kolorów i wyznań szeroko wkroczyli na arenę dziejów jako siła zdolna zmieniać świat w co najmniej takim samym stopniu jak państwa, kapitał czy kościoły. Skąd się bierze siła podporządkowanych i jak ją dostrzec w archiwach? Czy opór zwykłych ludzi to tylko działania polityczne? Czy dekolonizacja nigdy się nie kończy? Czym jest tradycja Subaltern Studies dziś? Co ma wspólnego z historiami ludowymi?

Na te m.in. pytania odpowiemy w kolejnym wydaniu cyklu Transmisje. Dekolonialne rozmowy o świecie wraz z dr. hab. Michałem Rauszerem, antropologiem z Uniwersytetu Warszawskiego.

Prowadzenie: Przemysław Wielgosz, eseista i kurator, redaktor naczelny Le Monde diplomatique – edycja polska

Gość: Michał Rauszer, antropolog, profesor Uniwersytetu Warszawskiego, autor książek, m.in. „Bękarty pańszczyzny” (2020), “Siła podporządkowanych” (2021). Wkrótce ukaże się jego nowa książka zatytułowana „Polska zbuntowana” poświęcona ruchom chłopskim w Polsce po zniesieniu pańszczyzny.

O cyklu: Przez kilka dekad w świecie zachodnim dominowało przekonanie, że kolonializm się skończył. Czy na pewno? Los zgotowany przez Izrael i USA Strefie Gazy, Libanowi, Jemenowi i Iranowi, a Ukrainie przez Rosję sugeruje coś innego. Koncepcja postkolonialności okazała się zbyt optymistyczna. O ile formalna kolonizacja jest dziś wyjątkiem, to brutalne polityki kolonialne przeżywają swój renesans. Od początku tego stulecia – wraz z kryzysem globalnego kapitalizmu, schyłkiem amerykańskiej hegemonii i dokonującą się w odpowiedzi na te zjawiska recydywą imperializmu – przekonujemy się, że kapitalizm nie może istnieć bez polaryzacji geograficznej, bez wynajdywania i eksploatacji peryferii, bez spychania krajów podporządkowanych w ubóstwo, autorytaryzm i chaos. Niestety tendencje do rekolonizacji mają swoją przyszłość. Dlatego perspektywa dekolonialna może być dziś lepszym sposobem na zrozumienie procesów zachodzących dokoła nas niż tradycyjne, europocentryczne narzędzia opisu świata. Dlatego też dekoloniana praktyka – polityczna, artystyczna czy kulturowa – daje więcej podstaw do nadziei na przezwyciężenie obecnych kryzysów niż odwoływanie się do zużytych schematów zarządzania politycznego wypracowanych w globalnych centrach władzy i kapitału.

ℹ️ ℹ️ ℹ️ Cykl “Transmisje. Dekolonialne rozmowy o świecie” są częścią projektu “Centrum działań kulturalno-artystycznych Strefy WolnoSłowej - Kaliska 8/10” finansowanego przez m.st. Warszawy.

cross-posted from: szmer.info/post/17053244

Bękarty dekolonizacji. O tym jak siła podporządkowanych zmienia historię. 👉 12 listopada, godz.19:00 Kaliska 8/10 Wstęp wolny

Historycy dotychczas opowiadali o imperiach, zwykle skupiając się na ich chwale, rzadziej na popełnianych w ich imieniu zbrodniach. Idzie jednak o to, by dostrzec tych, którzy zdolni są imperia obalać. Tych, dla których dekolonizacja nie była ideą polityczną, ale potrzebą wyrastającą z doświadczenia codziennych upokorzeń, nędzy i niesprawiedliwości. Na początku lat. 80. XX wieku taką właśnie perspektywę w opowiadaniu o rzeczywistości społeczeństw pod panowaniem kolonialnym przyjęła grupa indyjskich historyków. Ich podejście, które nazwano Subaltern Studies, czyli badaniami nad podporządkowanymi, zrewolucjonizowało sposób uprawiania historii, ale także to jak myślimy o procesach społecznych rozgrywających się współcześnie. Chłopi, niewolnicy, kobiety, plebejusze wszystkich płci, kolorów i wyznań szeroko wkroczyli na arenę dziejów jako siła zdolna zmieniać świat w co najmniej takim samym stopniu jak państwa, kapitał czy kościoły. Skąd się bierze siła podporządkowanych i jak ją dostrzec w archiwach? Czy opór zwykłych ludzi to tylko działania polityczne? Czy dekolonizacja nigdy się nie kończy? Czym jest tradycja Subaltern Studies dziś? Co ma wspólnego z historiami ludowymi?

Na te m.in. pytania odpowiemy w kolejnym wydaniu cyklu Transmisje. Dekolonialne rozmowy o świecie wraz z dr. hab. Michałem Rauszerem, antropologiem z Uniwersytetu Warszawskiego.

Prowadzenie: Przemysław Wielgosz, eseista i kurator, redaktor naczelny Le Monde diplomatique – edycja polska

Gość: Michał Rauszer, antropolog, profesor Uniwersytetu Warszawskiego, autor książek, m.in. „Bękarty pańszczyzny” (2020), “Siła podporządkowanych” (2021). Wkrótce ukaże się jego nowa książka zatytułowana „Polska zbuntowana” poświęcona ruchom chłopskim w Polsce po zniesieniu pańszczyzny.

O cyklu: Przez kilka dekad w świecie zachodnim dominowało przekonanie, że kolonializm się skończył. Czy na pewno? Los zgotowany przez Izrael i USA Strefie Gazy, Libanowi, Jemenowi i Iranowi, a Ukrainie przez Rosję sugeruje coś innego. Koncepcja postkolonialności okazała się zbyt optymistyczna. O ile formalna kolonizacja jest dziś wyjątkiem, to brutalne polityki kolonialne przeżywają swój renesans. Od początku tego stulecia – wraz z kryzysem globalnego kapitalizmu, schyłkiem amerykańskiej hegemonii i dokonującą się w odpowiedzi na te zjawiska recydywą imperializmu – przekonujemy się, że kapitalizm nie może istnieć bez polaryzacji geograficznej, bez wynajdywania i eksploatacji peryferii, bez spychania krajów podporządkowanych w ubóstwo, autorytaryzm i chaos. Niestety tendencje do rekolonizacji mają swoją przyszłość. Dlatego perspektywa dekolonialna może być dziś lepszym sposobem na zrozumienie procesów zachodzących dokoła nas niż tradycyjne, europocentryczne narzędzia opisu świata. Dlatego też dekoloniana praktyka – polityczna, artystyczna czy kulturowa – daje więcej podstaw do nadziei na przezwyciężenie obecnych kryzysów niż odwoływanie się do zużytych schematów zarządzania politycznego wypracowanych w globalnych centrach władzy i kapitału.

ℹ️ ℹ️ ℹ️ Cykl “Transmisje. Dekolonialne rozmowy o świecie” są częścią projektu “Centrum działań kulturalno-artystycznych Strefy WolnoSłowej - Kaliska 8/10” finansowanego przez m.st. Warszawy.

0

Science Fiction Is Changing... or is it Slipstream?

preview

Dear readers, I’m getting increasingly interested in current debates about the reemergence – nothing new, yet more noticeable in/by the mainstream now – of the so-called Slipstream literature. These are literary fiction works that combine speculative fiction modes and themes often associated with sci-fi.

Any fans out there? And what is your take on the YT Speculative Reader’s video essay about this mode of recent literature? Video essay – check video from minute 11 onwards.

Dear readers, I’m getting increasingly interested in current debates about the reemergence – nothing new, yet more noticeable in/by the mainstream now – of the so-called Slipstream literature. These are literary fiction works that combine speculative fiction modes and themes often associated with sci-fi.

Any fans out there? And what is your take on the YT Speculative Reader’s video essay about this mode of recent literature? Video essay – check video from minute 11 onwards.

0

Apple has new Mac app coming to make running local AI models easy

9to5Mac Apple has new Mac app coming to make running local AI models easy - 9to5Mac 9to5mac.com
preview

Leaker Aaron Perris has discovered evidence of a new Mac app in the works at Apple that makes it easy to run local AI models.

Leaker Aaron Perris has discovered evidence of a new Mac app in the works at Apple that makes it easy to run local AI models.

0

I could use some advice for connecting my pc to a crt tv.

preview

Hello,

A little while back I got an Samsung CW-29Z418T (Pal without hdmi) for free (someone was throwing it away) to which I connected my PS2 and a vhs/dvd player my grandpa had lying around.

Recently I saw a video by Epos Vox where he connected it to a pc and just today on Lemmy I saw someone use a Steam Deck on a tv.

My question, is there a budget converter with which I could connect my pc to the TV? Preferably Display Port but if HDMi is the only option I can work with it.

I would like to thank you guys, gals and anyone in between for any help you could give me.

Hello,

A little while back I got an Samsung CW-29Z418T (Pal without hdmi) for free (someone was throwing it away) to which I connected my PS2 and a vhs/dvd player my grandpa had lying around.

Recently I saw a video by Epos Vox where he connected it to a pc and just today on Lemmy I saw someone use a Steam Deck on a tv.

My question, is there a budget converter with which I could connect my pc to the TV? Preferably Display Port but if HDMi is the only option I can work with it.

I would like to thank you guys, gals and anyone in between for any help you could give me.

0

“The Rats Are Fleeing The Sinking Ship”: Trump’s Anti-Trans Civil Division Chief Resigns

“The Rats Are Fleeing The Sinking Ship”: Trump’s Anti-Trans Civil Division Chief Resigns www.erininthemorning.com
preview

Brett Shumate spent his time at the DOJ subpoenaing the records of thousands of transgender children and defending bogus investigations into gender-affirming care.

Brett Shumate spent his time at the DOJ subpoenaing the records of thousands of transgender children and defending bogus investigations into gender-affirming care.

0

I cooked delicious pasta with disastrous consequences

preview

Folks, I need an F in the chat.

Today I was scrolling Lemmy and I saw a discussion about bland noodles, and someone said the Italian Rule is to make sure the water is as salty as the sea.

So I made pasta, and this time I followed the Italian Rule. Folks, the pasta was so fucking tasty. I barely even chewed it before swallowing.

Now, I don’t know if it was that or the ghost pepper I put in the sauce, but I just spent the last two hours intermittently shitting My guts out in between grinding mobs in Starmourn. I wanted to go to bed more than 2 hours ago, but My guts said it was time to shit instead.

It hurt so bad, folks. And you know the worst part? It was worth it. I’m gonna do it again tomorrow 😭

Folks, I need an F in the chat.

Today I was scrolling Lemmy and I saw a discussion about bland noodles, and someone said the Italian Rule is to make sure the water is as salty as the sea.

So I made pasta, and this time I followed the Italian Rule. Folks, the pasta was so fucking tasty. I barely even chewed it before swallowing.

Now, I don’t know if it was that or the ghost pepper I put in the sauce, but I just spent the last two hours intermittently shitting My guts out in between grinding mobs in Starmourn. I wanted to go to bed more than 2 hours ago, but My guts said it was time to shit instead.

It hurt so bad, folks. And you know the worst part? It was worth it. I’m gonna do it again tomorrow 😭

0

Grok Build coding agent leaks oodles of confidential info, some belonging to SpaceXSI

Ars Technica Grok Build coding agent leaks oodles of confidential info, some belonging to SpaceXSI arstechnica.com
preview

Grok Build, the vibe-coding agent from SpaceXSI, is leaking data—some of it proprietary business information and other sensitive secrets—from thousands of its users, including the very same Elon Musk-owned company that offers the platform, new research shows.

The information is revealed through links allowing Grok Build users to share their apps with others. Grok takes steps to randomize the URLs so only people who know the exact URL can access the data stored there. A design decision by developers of the platform, however, completely torpedoes that objective and makes it possible for anyone to enumerate thousands of live Grok Build projects. Except in rare cases, clicking those links opens the app and reveals all data associated with it.

You had one job

Research from security firm Claroc shows that the exposed data includes things like internal business plans, ad proposals, medical exam results, galley checklists from a celebrity cruise line, and employee names and ID numbers. Ironically, some of the sensitive data comes from two-dozen apps built by SpaceXSI (the name of the now-merged SpaceX and xAI) itself. A small sampling of the documents revealed in the SpaceXSI apps—Claroc found 24 of them—include an onboarding plan, marked confidential, for a new member of SpaceXSI’s enterprise sales team, a sales territory map of 594 accounts, internal system addresses for sales team tools, and advertising proposals.

“We were shocked,” Claroc said in a Tuesday post. “The company that makes Grok had its own internal material open to anyone holding the link, and we had never been given it. Had the sales team bought a tool for this, it would have sat behind company sign-in, open only to the team. Built with AI, it went live open to anyone with the link.

Claroc notified SpaceXSI of the privacy spill on Sunday. When no one responded, a Claroc official took to X to tag both Musk and Grok Manager Matt Palmer about the threat. At the time this post went live almost all data remained available with one notable exception: the contents from the 24 SpaceXSI apps. All of them were exposing the information on Monday evening. SpaceXSI began removing the links within a few hours of Ars sending an email with questions for this article. At the time this post went live, links for all 24 apps returned an “app not found” error.

Claroc found sensitive data belonging to other Grok Build users, some working for Fortune 500 companies and a defense contractor. Some of the affected organizations and data revealed includes:

A Peruvian construction company: occupational-health dashboard with 3,784 worker medical exams

Tesla: service-center scorecard naming 22 technicians with productivity and bonus status

A US-Navy ship engineering contractor: roster of 108 people on a Navy logistics support contract

A leading luxury cruise company: a galley checklist for a celebrity cruise line listing crew by full name and employee ID

A healthcare company: hospital staff app with a roster of about 3,565 employees by name and ID

A US IT services company: a confidential proposal to a large retail customer with the hardware bill of materials

A Norwegian-Finnish aerospace and defense group: load board and loading procedure for an explosives building at a US plant, plus its HSE training matrix

A US home construction company: sales callsheet with about 583 home-buyer prospects, budgets and financing notes

A Malaysian holding company: project monitor for 37 developments with profit and sales figures

An auto transport company: quote desk with about 4,000 vehicle-transport orders, prices, and margins

A US data center colocation and hosting service: confidential IP transit proposal to a European carrier

Asaf Aprozper, the co-founder and CTO of Claroc, said he’s in the process of notifying companies. After speaking to the CISO of the luxury cruise company, it “pulled in their whole security team as soon as we shared the findings and are already working to contain the Grok exposure.”

A fatal flaw… shared by most other AI platforms

Link sharing for Grok Build is intended to streamline the process of developing and deploying apps. A user can input speech or text and have a working app ready for internal testing within minutes. The links are designed to give developers a way to get the app in front of authorized users quickly. The very left of the URLs contain two or more “dice words,” meaning randomly generated phrases such as “failing chassis traders,” although users can modify them. The rightmost portion of the link is grok.me. The URL for an X ads campaign plan was: cinder-crane-sand-frost.grok.me.

The scheme is intended to prevent links from being easily guessable. When done correctly, a phrase comprising three dice words has roughly 38 bits of entropy, amounting to billions of possible combinations. The idea—sometimes called capability-based access control—is that possession of the URL serves as authorization to the resources behind it. Google has long used this technique to make URLs easy to share but hard to guess. A URL share on that platform might look like: docs.google.com/document/d/…/edit

There’s a fatal flaw in the way SpaceXSI has implemented the mechanism. Instead of being to the right of the domain—as is the case with Google links—the randomness for Grok Build links is positioned to the left of it. That allows the links to be easily enumerated using passive DNS services. These services monitor central DNS lookup servers. When a server lookup requests the IP address of a previously never-before-seen URL, the transaction is captured in a publicly searchable database. Had Grok followed Google’s approach, the links would have been invisible to passive DNS searchers. Muse, the Meta agent that CEO Mark Zuckerberg said was built from the ground up for security, recently suspended a link-sharing feature after it too was found leaking sensitive data.

Aprozper said a passive DNS search returned 43,601 links ending in grok.me. Of them, more than 35,000, or nearly 95 percent, were public, meaning that clicking on the link opened the corresponding app and all data it stored. He said that tests he conducted over the past week showed that, by default, Grok sets links to “Anyone with the link.” Users have the option to change the setting to “invited users” or “only you.”

A representative with Cursor, the AI coding service SpaceXSI recently acquired, said in an email that Grok Build “apps are private by default and nothing goes public unless the creator chooses to share it.” The representative said that competing coding agents from ChatGPT, Lovable, and Bolt also give users the ability to generate shareable links.

Aprozper’s tests contradict the representative’s statement. In all cases, Grok Build required users to change anyone with the link to one of the other two options.

The Cursor statement regarding other AI coding platforms is correct. Aprozper said that app builders, including Lovable, Bolt, and Replit, “also give each app its own web address, so the same DNS records expose them, too. However, Grok is where we found by far the most sensitive company data.” That means that people using these other platforms are also at risk of exposing sensitive data through shared links. Interestingly, AI platforms that follow the correct sharing link practice include Claude’s published artifacts (claude.ai/public/artifacts/), ChatGPT’s shared conversations (chatgpt.com/share/), and Gemini (gemini.google.com/share/). For all three, the secret randomness is in the path, so DNS never sees it.

The representative didn’t respond to follow-up questions, including if SpaceXSI intentionally exposed the proprietary internal information, why the company removed the data after Ars asked about it, and if it planned to notify customers who also exposed similar types of information. Anyone using shareable links with Grok Build should choose the “invite others” option unless they intend to make an app widely available.
Grok Build, the vibe-coding agent from SpaceXSI, is leaking data—some of it proprietary business information and other sensitive secrets—from thousands of its users, including the very same Elon Musk-owned company that offers the platform, new research shows.

The information is revealed through links allowing Grok Build users to share their apps with others. Grok takes steps to randomize the URLs so only people who know the exact URL can access the data stored there. A design decision by developers of the platform, however, completely torpedoes that objective and makes it possible for anyone to enumerate thousands of live Grok Build projects. Except in rare cases, clicking those links opens the app and reveals all data associated with it.

You had one job

Research from security firm Claroc shows that the exposed data includes things like internal business plans, ad proposals, medical exam results, galley checklists from a celebrity cruise line, and employee names and ID numbers. Ironically, some of the sensitive data comes from two-dozen apps built by SpaceXSI (the name of the now-merged SpaceX and xAI) itself. A small sampling of the documents revealed in the SpaceXSI apps—Claroc found 24 of them—include an onboarding plan, marked confidential, for a new member of SpaceXSI’s enterprise sales team, a sales territory map of 594 accounts, internal system addresses for sales team tools, and advertising proposals.

“We were shocked,” Claroc said in a Tuesday post. “The company that makes Grok had its own internal material open to anyone holding the link, and we had never been given it. Had the sales team bought a tool for this, it would have sat behind company sign-in, open only to the team. Built with AI, it went live open to anyone with the link.

Claroc notified SpaceXSI of the privacy spill on Sunday. When no one responded, a Claroc official took to X to tag both Musk and Grok Manager Matt Palmer about the threat. At the time this post went live almost all data remained available with one notable exception: the contents from the 24 SpaceXSI apps. All of them were exposing the information on Monday evening. SpaceXSI began removing the links within a few hours of Ars sending an email with questions for this article. At the time this post went live, links for all 24 apps returned an “app not found” error.

Claroc found sensitive data belonging to other Grok Build users, some working for Fortune 500 companies and a defense contractor. Some of the affected organizations and data revealed includes:

A Peruvian construction company: occupational-health dashboard with 3,784 worker medical exams

Tesla: service-center scorecard naming 22 technicians with productivity and bonus status

A US-Navy ship engineering contractor: roster of 108 people on a Navy logistics support contract

A leading luxury cruise company: a galley checklist for a celebrity cruise line listing crew by full name and employee ID

A healthcare company: hospital staff app with a roster of about 3,565 employees by name and ID

A US IT services company: a confidential proposal to a large retail customer with the hardware bill of materials

A Norwegian-Finnish aerospace and defense group: load board and loading procedure for an explosives building at a US plant, plus its HSE training matrix

A US home construction company: sales callsheet with about 583 home-buyer prospects, budgets and financing notes

A Malaysian holding company: project monitor for 37 developments with profit and sales figures

An auto transport company: quote desk with about 4,000 vehicle-transport orders, prices, and margins

A US data center colocation and hosting service: confidential IP transit proposal to a European carrier

Asaf Aprozper, the co-founder and CTO of Claroc, said he’s in the process of notifying companies. After speaking to the CISO of the luxury cruise company, it “pulled in their whole security team as soon as we shared the findings and are already working to contain the Grok exposure.”

A fatal flaw… shared by most other AI platforms

Link sharing for Grok Build is intended to streamline the process of developing and deploying apps. A user can input speech or text and have a working app ready for internal testing within minutes. The links are designed to give developers a way to get the app in front of authorized users quickly. The very left of the URLs contain two or more “dice words,” meaning randomly generated phrases such as “failing chassis traders,” although users can modify them. The rightmost portion of the link is grok.me. The URL for an X ads campaign plan was: cinder-crane-sand-frost.grok.me.

The scheme is intended to prevent links from being easily guessable. When done correctly, a phrase comprising three dice words has roughly 38 bits of entropy, amounting to billions of possible combinations. The idea—sometimes called capability-based access control—is that possession of the URL serves as authorization to the resources behind it. Google has long used this technique to make URLs easy to share but hard to guess. A URL share on that platform might look like: docs.google.com/document/d/…/edit

There’s a fatal flaw in the way SpaceXSI has implemented the mechanism. Instead of being to the right of the domain—as is the case with Google links—the randomness for Grok Build links is positioned to the left of it. That allows the links to be easily enumerated using passive DNS services. These services monitor central DNS lookup servers. When a server lookup requests the IP address of a previously never-before-seen URL, the transaction is captured in a publicly searchable database. Had Grok followed Google’s approach, the links would have been invisible to passive DNS searchers. Muse, the Meta agent that CEO Mark Zuckerberg said was built from the ground up for security, recently suspended a link-sharing feature after it too was found leaking sensitive data.

Aprozper said a passive DNS search returned 43,601 links ending in grok.me. Of them, more than 35,000, or nearly 95 percent, were public, meaning that clicking on the link opened the corresponding app and all data it stored. He said that tests he conducted over the past week showed that, by default, Grok sets links to “Anyone with the link.” Users have the option to change the setting to “invited users” or “only you.”

A representative with Cursor, the AI coding service SpaceXSI recently acquired, said in an email that Grok Build “apps are private by default and nothing goes public unless the creator chooses to share it.” The representative said that competing coding agents from ChatGPT, Lovable, and Bolt also give users the ability to generate shareable links.

Aprozper’s tests contradict the representative’s statement. In all cases, Grok Build required users to change anyone with the link to one of the other two options.

The Cursor statement regarding other AI coding platforms is correct. Aprozper said that app builders, including Lovable, Bolt, and Replit, “also give each app its own web address, so the same DNS records expose them, too. However, Grok is where we found by far the most sensitive company data.” That means that people using these other platforms are also at risk of exposing sensitive data through shared links. Interestingly, AI platforms that follow the correct sharing link practice include Claude’s published artifacts (claude.ai/public/artifacts/), ChatGPT’s shared conversations (chatgpt.com/share/), and Gemini (gemini.google.com/share/). For all three, the secret randomness is in the path, so DNS never sees it.

The representative didn’t respond to follow-up questions, including if SpaceXSI intentionally exposed the proprietary internal information, why the company removed the data after Ars asked about it, and if it planned to notify customers who also exposed similar types of information. Anyone using shareable links with Grok Build should choose the “invite others” option unless they intend to make an app widely available.

0

Router question

preview

With all the gov’t attacks on privacy these days I’ve been thinking about getting my own router. I’ve never done it and am pretty new to network stuff overall. I certainly welcome any recommendations for routers but I mainly have a stupid question:

Is it as simple as just swapping out the isp router? I’ve disconnected anything I had exposed to the internet and use LAN only right now so none of my old port forwarding rules are needed.

With all the gov’t attacks on privacy these days I’ve been thinking about getting my own router. I’ve never done it and am pretty new to network stuff overall. I certainly welcome any recommendations for routers but I mainly have a stupid question:

Is it as simple as just swapping out the isp router? I’ve disconnected anything I had exposed to the internet and use LAN only right now so none of my old port forwarding rules are needed.

0

Qwen3.8-27B Unsloth Dynamic v3.1 GGUFs out now!

preview

Hey guys! Today, we’re releasing the highest accuracy Qwen3.8-27B GGUFs.

Our new Unsloth AI Dynamic V3.1 GGUFs lead by 5–10% on average across Terminal Bench, DeepSWE & more benchmarks. We’re working on even better version of Dynamic quants for Qwen4

Run on 12GB+ RAM setups.

To compare GSQ-RCO and Exllama-v3, we had to exclude the token embedding layer from the x axis, as Exllama-v3 uses BF16 for it. If you consider the full download size and total RAM usage for Exllama-v3, then adding the BF16 embedding table and including all embedding sizes changes the plots. Our main plots’s x axis removes the embedding layer sizes from all quant providers. However on pure RAM usage and disk space usage vs accuracy, the below plot in the comments the true reflection of actual usage.
GGUF: huggingface.co/unsloth/Qwen3.8-27B-GGUF

Blog: unsloth.ai/docs/models/qwen3.8

From their Reddit post.

Hey guys! Today, we’re releasing the highest accuracy Qwen3.8-27B GGUFs.

Our new Unsloth AI Dynamic V3.1 GGUFs lead by 5–10% on average across Terminal Bench, DeepSWE & more benchmarks. We’re working on even better version of Dynamic quants for Qwen4

Run on 12GB+ RAM setups.

To compare GSQ-RCO and Exllama-v3, we had to exclude the token embedding layer from the x axis, as Exllama-v3 uses BF16 for it. If you consider the full download size and total RAM usage for Exllama-v3, then adding the BF16 embedding table and including all embedding sizes changes the plots. Our main plots’s x axis removes the embedding layer sizes from all quant providers. However on pure RAM usage and disk space usage vs accuracy, the below plot in the comments the true reflection of actual usage.

GGUF: huggingface.co/unsloth/Qwen3.8-27B-GGUF

Blog: unsloth.ai/docs/models/qwen3.8

From their Reddit post.

0

Deepin 25.3 Adds Freeze Protection, AI Improvements, and Better Recovery

Linuxiac Deepin 25.3 Adds Freeze Protection, AI Improvements, and Better Recovery linuxiac.com
preview

The Deepin team has just released Deepin 25.3, the latest version of their China-developed, immutable Debian-based Linux distro. One of the most useful changes is a new freeze-protection mechanism that keeps core desktop components accessible if the system becomes extremely unresponsive.

In other words, under heavy load, you should still be able to get to the taskbar, the app launcher, and the System Monitor to see what’s going on and kill off the offending processes.

The devs have also been working on application startup performance, particularly the Control Center and the various office apps. System logs are now capped at 5GB by default and will automatically stop logging when disk space falls below 5% to prevent them from getting out of hand.

On the kernel side, Deepin 25.3 upgrades the default Linux kernel to 6.6.159, with fixes for several security vulnerabilities and boot issues on certain devices. For users with more modern hardware, 6.18.56 is available via Kernel Manager.

UOS AI, Deepin’s own AI assistant, can now create reminders, scheduled tasks, and recurring tasks from natural language. Moreover, it now has a whole-disk knowledge base so you can search the contents of authorized local files. There’s also a unified interface that brings MCP, Skills, and the various AI agents together.

Regarding system recovery, the immutable system in Deepin now allows snapshots to be stored on local disk, USB stick, and external HDD, with the ability to restore directly from a snapshot stored at a given location. The backup and rollback process has also been tweaked to reduce the amount of additional disk space consumed during an upgrade.

For the desktop, the update brings several fixes to Treeland (Deepin’s Wayland compositor), including Xwayland compatibility issues, incorrect window rendering when maximizing or going into fullscreen, and input method issues. The login screen has also been tweaked to ensure the controls are readable on light wallpapers.

On the Graphics support side, the NVIDIA Container Toolkit is now preinstalled to enable GPU acceleration for Linyaps containerized applications. The installer will also be able to automatically pick an appropriate NVIDIA driver version based on the graphics hardware that it detects.

Several bundled apps have received improvements as well. Image Viewer now supports cropping, rotation, annotations, mosaics, and blurring all within the viewer itself. Document Viewer now remembers your last position and layout, and Text Editor now has Markdown support.

On top of that, File Manager has an expandable directory tree in the sidebar, Calendar now supports third-party schedules, and App Store has proxy configuration options as well as more accessible installation error information.

Finally, Deepin 25.3 fixes several security issues in various components (Qt, curl, FFmpeg, glibc, OpenVPN, BlueZ, Xorg, and nginx), and the team has addressed some command injection, permission validation, and information disclosure issues in various system utilities.

For more details, see the release announcement.

The Deepin team has just released Deepin 25.3, the latest version of their China-developed, immutable Debian-based Linux distro. One of the most useful changes is a new freeze-protection mechanism that keeps core desktop components accessible if the system becomes extremely unresponsive.

In other words, under heavy load, you should still be able to get to the taskbar, the app launcher, and the System Monitor to see what’s going on and kill off the offending processes.

The devs have also been working on application startup performance, particularly the Control Center and the various office apps. System logs are now capped at 5GB by default and will automatically stop logging when disk space falls below 5% to prevent them from getting out of hand.

On the kernel side, Deepin 25.3 upgrades the default Linux kernel to 6.6.159, with fixes for several security vulnerabilities and boot issues on certain devices. For users with more modern hardware, 6.18.56 is available via Kernel Manager.

UOS AI, Deepin’s own AI assistant, can now create reminders, scheduled tasks, and recurring tasks from natural language. Moreover, it now has a whole-disk knowledge base so you can search the contents of authorized local files. There’s also a unified interface that brings MCP, Skills, and the various AI agents together.

Regarding system recovery, the immutable system in Deepin now allows snapshots to be stored on local disk, USB stick, and external HDD, with the ability to restore directly from a snapshot stored at a given location. The backup and rollback process has also been tweaked to reduce the amount of additional disk space consumed during an upgrade.

For the desktop, the update brings several fixes to Treeland (Deepin’s Wayland compositor), including Xwayland compatibility issues, incorrect window rendering when maximizing or going into fullscreen, and input method issues. The login screen has also been tweaked to ensure the controls are readable on light wallpapers.

On the Graphics support side, the NVIDIA Container Toolkit is now preinstalled to enable GPU acceleration for Linyaps containerized applications. The installer will also be able to automatically pick an appropriate NVIDIA driver version based on the graphics hardware that it detects.

Several bundled apps have received improvements as well. Image Viewer now supports cropping, rotation, annotations, mosaics, and blurring all within the viewer itself. Document Viewer now remembers your last position and layout, and Text Editor now has Markdown support.

On top of that, File Manager has an expandable directory tree in the sidebar, Calendar now supports third-party schedules, and App Store has proxy configuration options as well as more accessible installation error information.

Finally, Deepin 25.3 fixes several security issues in various components (Qt, curl, FFmpeg, glibc, OpenVPN, BlueZ, Xorg, and nginx), and the team has addressed some command injection, permission validation, and information disclosure issues in various system utilities.

For more details, see the release announcement.

0

Hedley and Bennett Mystery Aprons: A Cautionary Tale

preview

Long story short: I ordered two mystery aprons from Hedley and Bennett. Behold, the Sgt. Pepper’s apron they sent me.

Taste is not universal; would anyone want this thing? Does anyone want this thing? Do I email them, knowing they don’t do refunds on mystery picks, making a fun thing exceptionally not fun? Do I bleach it, or dye it? Hideous as I find this, I don’t want to just pitch it.

Their normal aprons are great. My mystery apron was supposed to be fun and I’m a little peeved they went this far off the board; I actually checked every single apron they have on the site before I bought to see how bad it could get, but this isn’t listed in their product listings since they’re mostly sold out. I wasn’t aware anything this hideous was in the realm of possibility.

A quote from the product listing:

both aprons will be ready for just about anything.

Ready for the circus maybe.

Obviously I would not recommend this. I’ve functionally paid 20% more for one decent, usable to me apron.

Long story short: I ordered two mystery aprons from Hedley and Bennett. Behold, the Sgt. Pepper’s apron they sent me.

Taste is not universal; would anyone want this thing? Does anyone want this thing? Do I email them, knowing they don’t do refunds on mystery picks, making a fun thing exceptionally not fun? Do I bleach it, or dye it? Hideous as I find this, I don’t want to just pitch it.

Their normal aprons are great. My mystery apron was supposed to be fun and I’m a little peeved they went this far off the board; I actually checked every single apron they have on the site before I bought to see how bad it could get, but this isn’t listed in their product listings since they’re mostly sold out. I wasn’t aware anything this hideous was in the realm of possibility.

A quote from the product listing:

both aprons will be ready for just about anything.

Ready for the circus maybe.

Obviously I would not recommend this. I’ve functionally paid 20% more for one decent, usable to me apron.

0

Linux’s exFAT Progs 1.4.4 Adds Optional I/O Statistics Collection for Profiling

9to5Linux Linux’s exFAT Progs 1.4.4 Adds Optional I/O Statistics Collection for Profiling - 9to5Linux 9to5linux.com
preview

Exfatprogs (exFAT Progs) 1.4.4, exFAT filesystem userspace utilities for Linux, has been released today with several improvements, a new feature, and multiple bug fixes.

Exfatprogs 1.4.4 is the fourth minor update in the Exfatprogs 1.4 series, coming three months after Exfatprogs 1.4.3. This release introduces a new feature to the exfatprogs command, namely optional I/O statistics collection for profiling read, write, discard, zero-out, and sync operations.

This release also updates mkfs.exfat to increase full-format speed by using BLKZEROOUT when supported, selecting larger zeroing batches, and improving quiet and trace progress output, and reducing page-cache pollution during full formatting on systems that support POSIX_FADV_NOREUSE.

Several bugs were fixed in Exfatprogs 1.4.4 for the mkfs.exfat command, avoiding memory-reservation failures when creating very large allocation bitmaps, and marking the percentage of used clusters as unknown until it is calculated.

The fsck.exfat command received the most attention, with fixes to prevent arithmetic overflows and out-of-bounds reads by rejecting malformed boot sector geometry, avoid printing version information during automatic repair with the “-p” or “-a” arguments, and missing line breaks in error messages.

In addition, the fsck.exfat command now stops immediately on I/O errors instead of treating them as file system inconsistencies. The dump.exfat command was updated to print complete file timestamps in raw and ISO formats, while the exfat2img command now keeps metadata image output on stdout free of status messages.

Last but not least, the exfatprogs command received fixes for parsing kernel versions and boolean environment variables, and showing the correct usage text for overwrite and read-back verification options.

Check out the release notes on the project’s GitHub page for more details about the changes included in exFAT Progs 1.4.4, from where you can download the source tarball if you want to compile it on your Linux distro. However, it is recommended to install Exfatprogs from your distro’s stable repositories.

Exfatprogs was designed as official userspace utilities that contain all of the standard utilities for creating, fixing, and debugging exFAT filesystems in Linux distributions. The goal of the exfatprogs project is to provide Linux users with the same high performance and quality as the exFAT utilities in Windows.

Exfatprogs (exFAT Progs) 1.4.4, exFAT filesystem userspace utilities for Linux, has been released today with several improvements, a new feature, and multiple bug fixes.

Exfatprogs 1.4.4 is the fourth minor update in the Exfatprogs 1.4 series, coming three months after Exfatprogs 1.4.3. This release introduces a new feature to the exfatprogs command, namely optional I/O statistics collection for profiling read, write, discard, zero-out, and sync operations.

This release also updates mkfs.exfat to increase full-format speed by using BLKZEROOUT when supported, selecting larger zeroing batches, and improving quiet and trace progress output, and reducing page-cache pollution during full formatting on systems that support POSIX_FADV_NOREUSE.

Several bugs were fixed in Exfatprogs 1.4.4 for the mkfs.exfat command, avoiding memory-reservation failures when creating very large allocation bitmaps, and marking the percentage of used clusters as unknown until it is calculated.

The fsck.exfat command received the most attention, with fixes to prevent arithmetic overflows and out-of-bounds reads by rejecting malformed boot sector geometry, avoid printing version information during automatic repair with the “-p” or “-a” arguments, and missing line breaks in error messages.

In addition, the fsck.exfat command now stops immediately on I/O errors instead of treating them as file system inconsistencies. The dump.exfat command was updated to print complete file timestamps in raw and ISO formats, while the exfat2img command now keeps metadata image output on stdout free of status messages.

Last but not least, the exfatprogs command received fixes for parsing kernel versions and boolean environment variables, and showing the correct usage text for overwrite and read-back verification options.

Check out the release notes on the project’s GitHub page for more details about the changes included in exFAT Progs 1.4.4, from where you can download the source tarball if you want to compile it on your Linux distro. However, it is recommended to install Exfatprogs from your distro’s stable repositories.

Exfatprogs was designed as official userspace utilities that contain all of the standard utilities for creating, fixing, and debugging exFAT filesystems in Linux distributions. The goal of the exfatprogs project is to provide Linux users with the same high performance and quality as the exFAT utilities in Windows.

0

Mozilla Thunderbird 160 Email Client Released with Various Improvements

9to5Linux Mozilla Thunderbird 160 Email Client Released with Various Improvements - 9to5Linux 9to5linux.com
preview

Following the release of the Mozilla Firefox 160 web browser today, Mozilla also released the Mozilla Thunderbird 160 open-source email, chat, address book, news, and calendar client for all supported platforms.

Mozilla Thunderbird 160 adds support for the Ctrl+A keyboard shortcut for selecting all filters in the Message Filters dialog, improves OAuth sign-in windows to explain when blocked cookies may prevent sign-in, and updates Office 365 account setup to no longer automatically offer EWS configuration.

Thunderbird 160 fixes numerous bugs, starting with a crash that could occur when opening a window, a crash caused by message database updates, and a freeze of new mail notifications when processing some sender addresses.

IMAP retention settings no longer delete newer messages instead of older ones, folders no longer disappear after a restart on servers using compression, and namespace root folders are no longer missing or given incorrect permissions.

Undo is no longer disabled after deleting messages, dragging multiple selected folders now moves all of them, renaming or moving folders no longer removes them from saved searches, and Thunderbird now warns before repairing folders with offline message storage.

POP3 and news messages with LF line endings are no longer parsed incorrectly, Edit as New Message now works for some news messages, and empty message filter conditions no longer cause incorrect matches. The News Reader and Feed Reader also got various improvements.

On the interface side, Mozilla Thunderbird 160 improves the macOS Dock badge to no longer omit unread counts with multiple accounts, improves the Windows system tray icon to update when new mail arrives, brings back the option to create a mailing list, and updates toolbar defaults to no longer close the customization dialog.

Composing sees fixes too, with the spelling dictionary menu no longer empty in the Subject field, tabbing from the Subject field now moving focus to the message body instead of the header divider, and replies to saved messages no longer blocked despite a valid Reply-To address.

On top of all that, account setup got better as Exchange autodiscovery no longer fails when redirected to another email address, Graph account setup now works for tenants without a SharePoint license, and address book setup no longer returns to mail setup when no mail account exists.

Address books and CardDAV also see fixes, with filter conditions now matching messages that have missing addresses, website fields no longer prefixing non-HTTP links with HTTPS, and CardDAV contacts with multiline street addresses no longer appearing empty.

Also, CardDAV contacts are now saved in a format supported by more servers, and photos saved in vCard 3.0 contacts now appear correctly in other clients. Lastly, Delete Event is no longer enabled for read-only calendars in the Today Pane, and attendance options now appear for all recurring event series.

Furthermore, the task list no longer stops updating after toolbar customization, and CalDAV reminders can be dismissed and snoozed again. Some webcal calendar subscriptions are no longer incorrectly blocked, and invalid ICS calendar files are no longer overwritten when events are changed.

Check out the release notes for more details about the changes included in Mozilla Thunderbird 160, which is available for download right now from the official website as binaries for Linux, macOS, and Windows systems. Linux users can also install Thunderbird from their distro’s repositories or from Flathub.

Following the release of the Mozilla Firefox 160 web browser today, Mozilla also released the Mozilla Thunderbird 160 open-source email, chat, address book, news, and calendar client for all supported platforms.

Mozilla Thunderbird 160 adds support for the Ctrl+A keyboard shortcut for selecting all filters in the Message Filters dialog, improves OAuth sign-in windows to explain when blocked cookies may prevent sign-in, and updates Office 365 account setup to no longer automatically offer EWS configuration.

Thunderbird 160 fixes numerous bugs, starting with a crash that could occur when opening a window, a crash caused by message database updates, and a freeze of new mail notifications when processing some sender addresses.

IMAP retention settings no longer delete newer messages instead of older ones, folders no longer disappear after a restart on servers using compression, and namespace root folders are no longer missing or given incorrect permissions.

Undo is no longer disabled after deleting messages, dragging multiple selected folders now moves all of them, renaming or moving folders no longer removes them from saved searches, and Thunderbird now warns before repairing folders with offline message storage.

POP3 and news messages with LF line endings are no longer parsed incorrectly, Edit as New Message now works for some news messages, and empty message filter conditions no longer cause incorrect matches. The News Reader and Feed Reader also got various improvements.

On the interface side, Mozilla Thunderbird 160 improves the macOS Dock badge to no longer omit unread counts with multiple accounts, improves the Windows system tray icon to update when new mail arrives, brings back the option to create a mailing list, and updates toolbar defaults to no longer close the customization dialog.

Composing sees fixes too, with the spelling dictionary menu no longer empty in the Subject field, tabbing from the Subject field now moving focus to the message body instead of the header divider, and replies to saved messages no longer blocked despite a valid Reply-To address.

On top of all that, account setup got better as Exchange autodiscovery no longer fails when redirected to another email address, Graph account setup now works for tenants without a SharePoint license, and address book setup no longer returns to mail setup when no mail account exists.

Address books and CardDAV also see fixes, with filter conditions now matching messages that have missing addresses, website fields no longer prefixing non-HTTP links with HTTPS, and CardDAV contacts with multiline street addresses no longer appearing empty.

Also, CardDAV contacts are now saved in a format supported by more servers, and photos saved in vCard 3.0 contacts now appear correctly in other clients. Lastly, Delete Event is no longer enabled for read-only calendars in the Today Pane, and attendance options now appear for all recurring event series.

Furthermore, the task list no longer stops updating after toolbar customization, and CalDAV reminders can be dismissed and snoozed again. Some webcal calendar subscriptions are no longer incorrectly blocked, and invalid ICS calendar files are no longer overwritten when events are changed.

Check out the release notes for more details about the changes included in Mozilla Thunderbird 160, which is available for download right now from the official website as binaries for Linux, macOS, and Windows systems. Linux users can also install Thunderbird from their distro’s repositories or from Flathub.