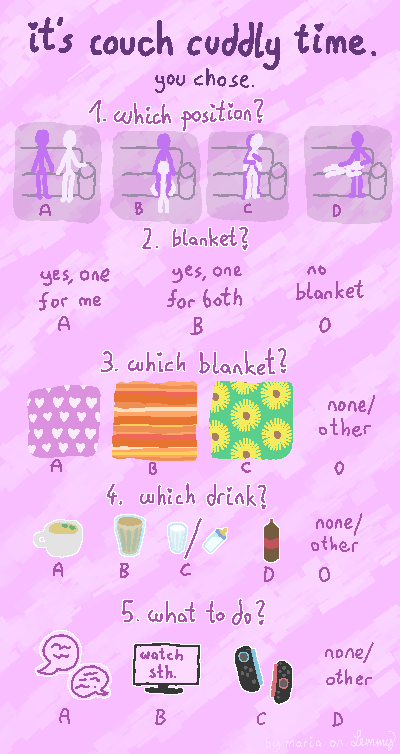The Steam Frame Is More Than Just Another VR Headset - Aftermath (Chris Person)

Aftermath The Steam Frame Is More Than Just Another VR Headset
preview

Conclusion below, but full read is highly recommended:

#The Frame

The Steam Frame is not for everyone; I’d argue VR isn’t generally. But despite taking far longer than it should have to materialize and costing more than I’d like, the Steam Frame is one of the most exciting pieces of hardware I’ve seen in the space in years, one that gave me that same feeling of optimism that the Index did so years ago. The Frame builds on the work done by its competitors in the years since the Index and solves so many friction points I’d had to actually engaging with VR as a medium at all. It is a device that is doing massive amounts of hard work to unify several different use cases into a single open platform, and, despite its individual parts being less novel, that unity is game changing. It is hardware whose importance may ultimately eclipse its remit, one with potentially massive consequences for PC gaming, but on its own terms it hits the sweet spot that I’ve yearned for so much from a successor. I only pray we do not have to wait another seven years for more.

The contagion of fear

The Observation Deck The contagion of fear | The Observation Deck
preview

[…] We should heed the wisdom of the late Carl Sagan that extraordinary claims require extraordinary evidence: the claims from Coxon and his ilk are the most extraordinary a technologist can make, and we must demand evidence commensurate with the claims. That said, we should not expect the public to understand LLMs, critical infrastructure, bioweapons, extinction biology, etc. — that burden must lie with those making the claim. The lesson that I learned (shamefully) decades ago is that domain experts, by way of their expertise, implicitly hold the public’s trust — and we must not abuse it. It is incumbent upon us to be circumspect in our claims — and maximally so when raising the alarm.

What sort of setup would you have for secure file storage on a VPS?

preview

Purely a hypothetical for me; I don’t have the means for a VPS or that many files. But in the future, if I’d want to use the 3-2-1 rule with a VPS subscription, what sort of software would I need to ensure that my files can’t be accessed on the VPS and need off-site decryption keys? What kind of setup would allow you to access said files from a different device if the decryption keys are stored locally on it? People who’ve done something similar, how has that gone for you?

Anyone else seeing that unhinged "UK phones require digital ID or get child-locked" screenshot making the rounds?

A hand holding a smartphone displaying an age verification screen with text that reads "Confirm You Are 18+ UK law requires you to confirm you are an adult to change content restrictions," with a bold news banner across the bottom reading "BREAKING: ALL UK USERS TO SUBMIT DIGITAL ID OR LOSE FULL PHONE ACCESS."
preview

My feeds have been flooded with it over the past 24 hours, and even some prominent privacy groups have been amplifying the hysteria. The panic claims everyone is about to lose full phone access unless they submit to digital ID checks.

While the actual situation stems from recent Westminster pressure on tech giants around device-level age controls and online safety, the viral framing is completely overblown. There’s no law turning every adult’s phone into a brick tomorrow.

That said, the underlying trend of pushing age-verification and filtering hooks deeper into OS-level infrastructure is still a massive red flag for encryption and digital sovereignty.

VC isn’t VC anymore — understanding the rise of Cancer Capital

VC isn’t VC anymore — understanding the rise of Cancer Capital - Anil Dash
preview

We really, really need to talk about venture capital. Because it’s not “venture capital” anymore.

There’s a huge disconnect between what most people think of VC, where an investor has a big fund and cuts checks to help a founder build a company, and the current reality, where a handful of billionaire extremists use the cover of “VC” to advance an outrageous agenda where they’re accountable to no one.

I’m gonna explain this from a standpoint that almost never gets articulated: I’ve personally raised tens of millions of dollars in venture capital funding as CEO of startups, and been directly involved as a board member or advisor in raising hundreds of millions more. I’ve sat in board rooms, across the table from the people I’m talking about here, or been at the industry events that they frequent. So this isn’t sour grapes because these VCs wouldn’t cut me a check, or some chip on my shoulder about these investors due to a business deal. This is what I know about these bad actors because I’m part of the community of creators and inventors who build the things that they used to invest in — back when they still cared about innovation.

Many of the trends in society and politics that people are most angry about, from data centers being forced down everyone’s throats, to all of our favorite apps and services being enshittified, to politicians being paid to ignore the will of the people, are all being supercharged by these cancer capitalists. They have warped the structure of venture capital into a form of oligarchy that answers to no market, no regulators, and no voters. So it’s worth understanding exactly how they did it.

Pre-enshittification tech. [discussion/fun]

preview

What kind of pre-enshittification tech do you all use? Stuff where ppl look at you like you’re an alien b/c nobody does it that any more.

Me ->

Oldschool offline mp3 player rather than Spottify or other streaming or phone app, to use when running.

Paper books rather than e-books.

DRM free games I buy on GOG to avoid rootkitting my own comp.

Wired speakers rather than smart speakers.

Old ass pre-connected car.

Prob more but I can’t think of it all rn.

couch cuddly rule. DAY 52 [OC, brainmade]

digital drawing. a "this or that" type post. title: "it's couch cuddly time! you chose". there are 5 multiple choice questions. first: "which position? A: sitting beside one another, B: one sitting on couch, other sitting on floor between legs, C: one holding the other from behind, D: one laying their head in the others lap". second: "blanket? A: yes, one for me, B: yes, one for both, C: no blanket". third: "which blanket? A: with hearts on it, B: with warm stripes on it, C: with flowers on it, O: none or other". fourth: "which drink? A: tea, B: chocolate milk, C: regular milk optionally in a baby bottle, D: soft drink, O: none or other". fifth: "what to do? A: talk a bit, B: watch something, C: play games, D: none or other". bottom right says "by maria on lemmy"
preview

even more blanket posts. great, right? we have all been waiting for another blanketpost, can’t get enough of em.

alt image (catbox, high quality)

felt like making a “this or that” type post for a whiiiiile. this dates back about 2 years when i looked at some of em and thought “this is fun!”

i’d love to hear about your picks!

my picks areee ummm… this is difficult. lemme think.
okay, my picks are: B-A-A-A-A …
yea, apparently i drew put all my favorites first. whoops. in question 2 i would love B but that doesn’t work with position B. oh well.

i wish you a wonderful day where you chose your own adventure.

AI Is Creating New Jobs But Millions of Workers May Not Be Ready

My Blog AI Creating New Jobs: Why Workers Need New Skills
preview

Artificial intelligence is creating new career opportunities while also changing the skills employers need. As AI becomes increasingly integrated into the workplace, millions of workers may need to adapt and develop new digital and technical skills to remain competitive The impact of AI is not only about job displacement. It is also creating new roles and changing how people work across different industries

What skills do you think workers should focus on as AI continues to reshape the job market?

old Datto (OpenMesh) switches management

preview

I’m posting this in case it’ll help anyone else out that may have access to some of the old Datto switches.

I work for a business that previously used Datto extensively (before they were sold to Kaseya) and we had a lot of old Datto hardware because of that. We’ve since moved on to other hardware solutions for clients but we kinda got stuck with this old hardware and I ended up taking some of the switches we had (an S24 and a E48) - I took them with the expectation that I’ll just use them as dumb unmanaged PoE switches. My employer tried to give these away for free through facebook marketplace and other similar sites just to get them out of their hair and would get people asking about them but nobody ultimately took them.

Well I did use them as unmanaged switches for a bit; I blocked internet access for them on my firewall just in case it was reaching out to the cloud, so nothing could potentially be modified suddenly. I recently spent some time looking into the console access on them to see if there’s anything there. After a bit of searching I found that if you factory reset them and prevent access to the cloud, they have a default openmesh password ( 0p3nm3$h! ) on the admin account which you can use to gain full access to the CLI and thus some level of management of the switch.

I then examined the running config and discovered they have a local web interface (and ssh and telnet) which is disabled by default and you can enable, you can also create other users on it for management. So, through the console I obviously enabled those to see if they function and to my surprise they indeed do function. So now I have proper 24 and 48 port managed PoE switches at my disposal which made me pretty happy.

Anyway, if anyone happens to stumble upon these switches (at least the S24 and E48 models) and you can use them, know that you can now fully manage them on your own if you so desire. The console connection requires a baud rate of 115200 and then you can just login with username admin and password 0p3nm3$h!. From there you can use the contextual help (?) to figure out the commands. To enable the web interface, after logging in you can do this:

configure  
ip https  
exit  
save  

then you can simply access it in a browser at https://{ip-address-of-switch} using an existing user account. For reference, to create an account you can use a command like this:

configure  
username {USERNAMEHERE} secret {PASSWORDHERE}  
exit  
save  

I did verify that changes made via the web interface do actually work and change the configuration, I half-expected it wouldn’t work but was pleasantly surprised it does.