

0
0




Explanation: one of today’s compromised root certificates had the number 4 as its private key.
Explanation: one of today’s compromised root certificates had the number 4 as its private key.



In copyright lawsuits over AI training, Meta has spent weeks blaming staff for downloading torrents. The company has now been ordered to name executives who authorized decisions to pirate books from shadow libraries like Anna’s Archive and LibGen, TorrentFreak reported.
In copyright lawsuits over AI training, Meta has spent weeks blaming staff for downloading torrents. The company has now been ordered to name executives who authorized decisions to pirate books from shadow libraries like Anna’s Archive and LibGen, TorrentFreak reported.

cross-posted from: !nikke@lemmy.world
cross-posted from: !nikke@lemmy.world
I’m currently running a bunch of services behind a reverse proxy and that proxy is configured to use let’s encrypt for ssl certs using DNS-01 challenges for renewals. All of the services are configured to only work using Tailscale IPs, so, as far as I’m aware, none of the services are open to the internet, except for port 80.
I noticed if I don’t leave port 80 open, when it’s time for renewal, everything fails. This leads to a bunch of logs on my Unifi setup saying intrusion attempts have been blocked on port 80. I thought I could go to Let’s Encrypt’s website and find a list of IPs I could put on an allow list but they don’t post those. So my questions are:
1. If I understand the process correctly, Let’s Encrypt checks the DNS TXT record to verify I own a domain, then sends a new cert to my server over port 80; meaning, I have to have port 80 open during the renewal process, correct? Nope
2. If that’s correct, what do you all do about port 80? Do you just have a script to open the port during the renewal process and close it afterwards or do you just leave it open all the time? Is there maybe a tool that already has this functionality? not if using DNS-01 challenges
3. I think I have port 443 open as well but I don’t remember if that’s needed or if I just did that when I opened port 80 trying to get all my services working again. Does 443 need to be open too? not if using DNS-01 challenges
4. If there is a better way to do all this or if I fucked up somewhere, please share. This was just the first setup I got working. I fucked up, see below
Thanks
EDIT: After deleting the current certificate and going through the process of generating a new one, everything is working without port 80 open. I’m using NGINX Proxy Manager and I must have clicked on “Lets Encrypt via HTTP” and not “Lets Encrypt via DNS” when originally setting this up. Not sure how else this could have happened 😅
I’m currently running a bunch of services behind a reverse proxy and that proxy is configured to use let’s encrypt for ssl certs using DNS-01 challenges for renewals. All of the services are configured to only work using Tailscale IPs, so, as far as I’m aware, none of the services are open to the internet, except for port 80.
I noticed if I don’t leave port 80 open, when it’s time for renewal, everything fails. This leads to a bunch of logs on my Unifi setup saying intrusion attempts have been blocked on port 80. I thought I could go to Let’s Encrypt’s website and find a list of IPs I could put on an allow list but they don’t post those. So my questions are:
1. If I understand the process correctly, Let’s Encrypt checks the DNS TXT record to verify I own a domain, then sends a new cert to my server over port 80; meaning, I have to have port 80 open during the renewal process, correct? Nope
2. If that’s correct, what do you all do about port 80? Do you just have a script to open the port during the renewal process and close it afterwards or do you just leave it open all the time? Is there maybe a tool that already has this functionality? not if using DNS-01 challenges
3. I think I have port 443 open as well but I don’t remember if that’s needed or if I just did that when I opened port 80 trying to get all my services working again. Does 443 need to be open too? not if using DNS-01 challenges
4. If there is a better way to do all this or if I fucked up somewhere, please share. This was just the first setup I got working. I fucked up, see below
Thanks
EDIT: After deleting the current certificate and going through the process of generating a new one, everything is working without port 80 open. I’m using NGINX Proxy Manager and I must have clicked on “Lets Encrypt via HTTP” and not “Lets Encrypt via DNS” when originally setting this up. Not sure how else this could have happened 😅


Long Distance Calling werden nicht umsonst von der Kritik gefeiert: Seit ihrer Gründung im Jahr 2006 überzeugen die Münsteraner auf ihren vorwiegend instrumentalen Alben mit der Virtuosität wahrer Klangkünstler.
Long Distance Calling werden nicht umsonst von der Kritik gefeiert: Seit ihrer Gründung im Jahr 2006 überzeugen die Münsteraner auf ihren vorwiegend instrumentalen Alben mit der Virtuosität wahrer Klangkünstler.


Only a couple of days left before women in some European countries start working for free the rest of the year.
Not accounting for all the non-paid hidden work women do every day at home.
Only a couple of days left before women in some European countries start working for free the rest of the year.
Not accounting for all the non-paid hidden work women do every day at home.

That should be new Java slogan
That should be new Java slogan
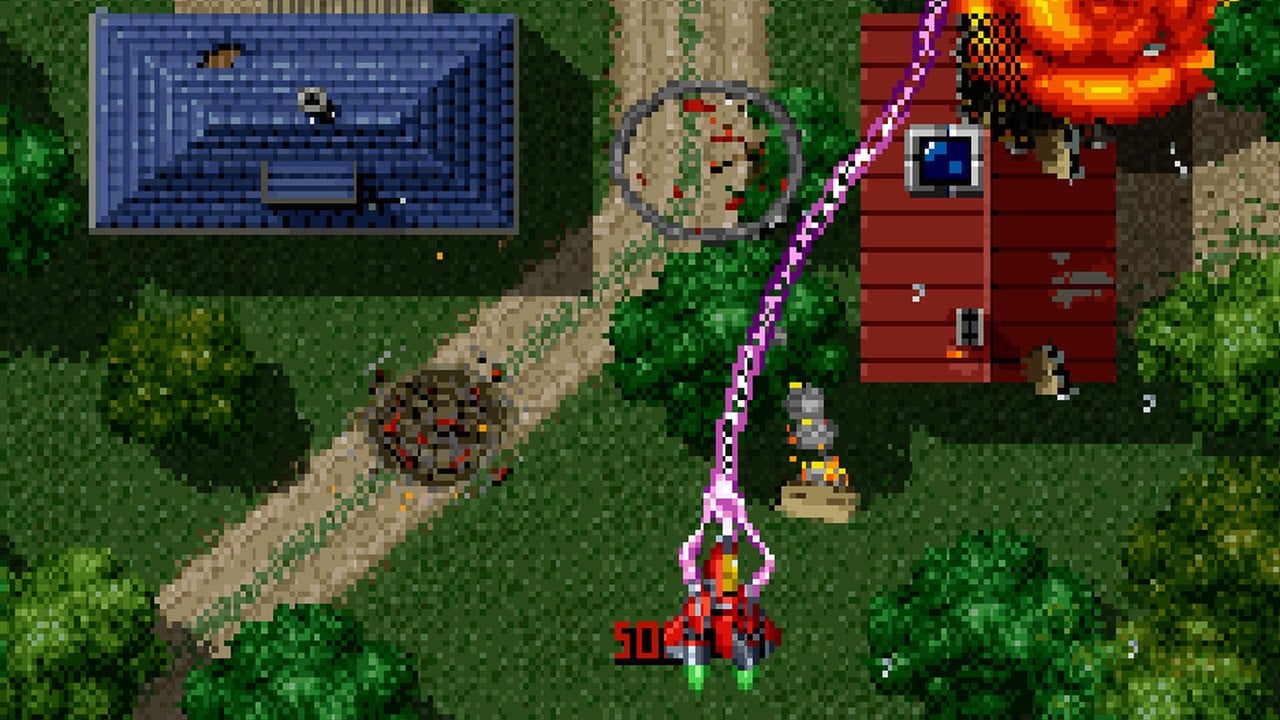
I’ve only played the PS1 versions of Raiden via emulation of course, but I liked them well enough. Raiden is super old-school hard though.
I’ve only played the PS1 versions of Raiden via emulation of course, but I liked them well enough. Raiden is super old-school hard though.
Atari Jaguar love in 2027! Who’d have thought that was going to happen!
Atari Jaguar love in 2027! Who’d have thought that was going to happen!
Mass Effect will not continue.
Mass Effect will not continue.

On Nintendo Switch 2, it’s a game-key card. In contrast, everything is on the cartridge for Nintendo Switch 1. With a game-key card, you’ll need to download all game data before the title can start. Collectors may therefore be more interested in the Nintendo Switch version.
On Nintendo Switch 2, it’s a game-key card. In contrast, everything is on the cartridge for Nintendo Switch 1. With a game-key card, you’ll need to download all game data before the title can start. Collectors may therefore be more interested in the Nintendo Switch version.
During the welcoming ceremony the boss says, “You’re all part of our team now. You can earn good money here, and you can go to the cafeteria for something to eat. So please don’t trouble any of the other employees”.
The cannibals promise.
Four weeks later the boss returns and says, “You’re all working very hard, and I’m very satisfied with all of you. However, one of our janitors has disappeared. Do any of you know what happened to him?”
The cannibals all shake their heads no.
After the boss has left, the leader of the cannibals says to the others, “Which one of you idiots ate the janitor?”
A hand raises hesitantly, to which the leader of the cannibals replies, “You fool! For four weeks we’ve been eating Team Leaders, Supervisors and Project Managers and no one noticed anything, and then you have to go and eat the fucking janitor!”
(unknown source)
During the welcoming ceremony the boss says, “You’re all part of our team now. You can earn good money here, and you can go to the cafeteria for something to eat. So please don’t trouble any of the other employees”.
The cannibals promise.
Four weeks later the boss returns and says, “You’re all working very hard, and I’m very satisfied with all of you. However, one of our janitors has disappeared. Do any of you know what happened to him?”
The cannibals all shake their heads no.
After the boss has left, the leader of the cannibals says to the others, “Which one of you idiots ate the janitor?”
A hand raises hesitantly, to which the leader of the cannibals replies, “You fool! For four weeks we’ve been eating Team Leaders, Supervisors and Project Managers and no one noticed anything, and then you have to go and eat the fucking janitor!”
(unknown source)
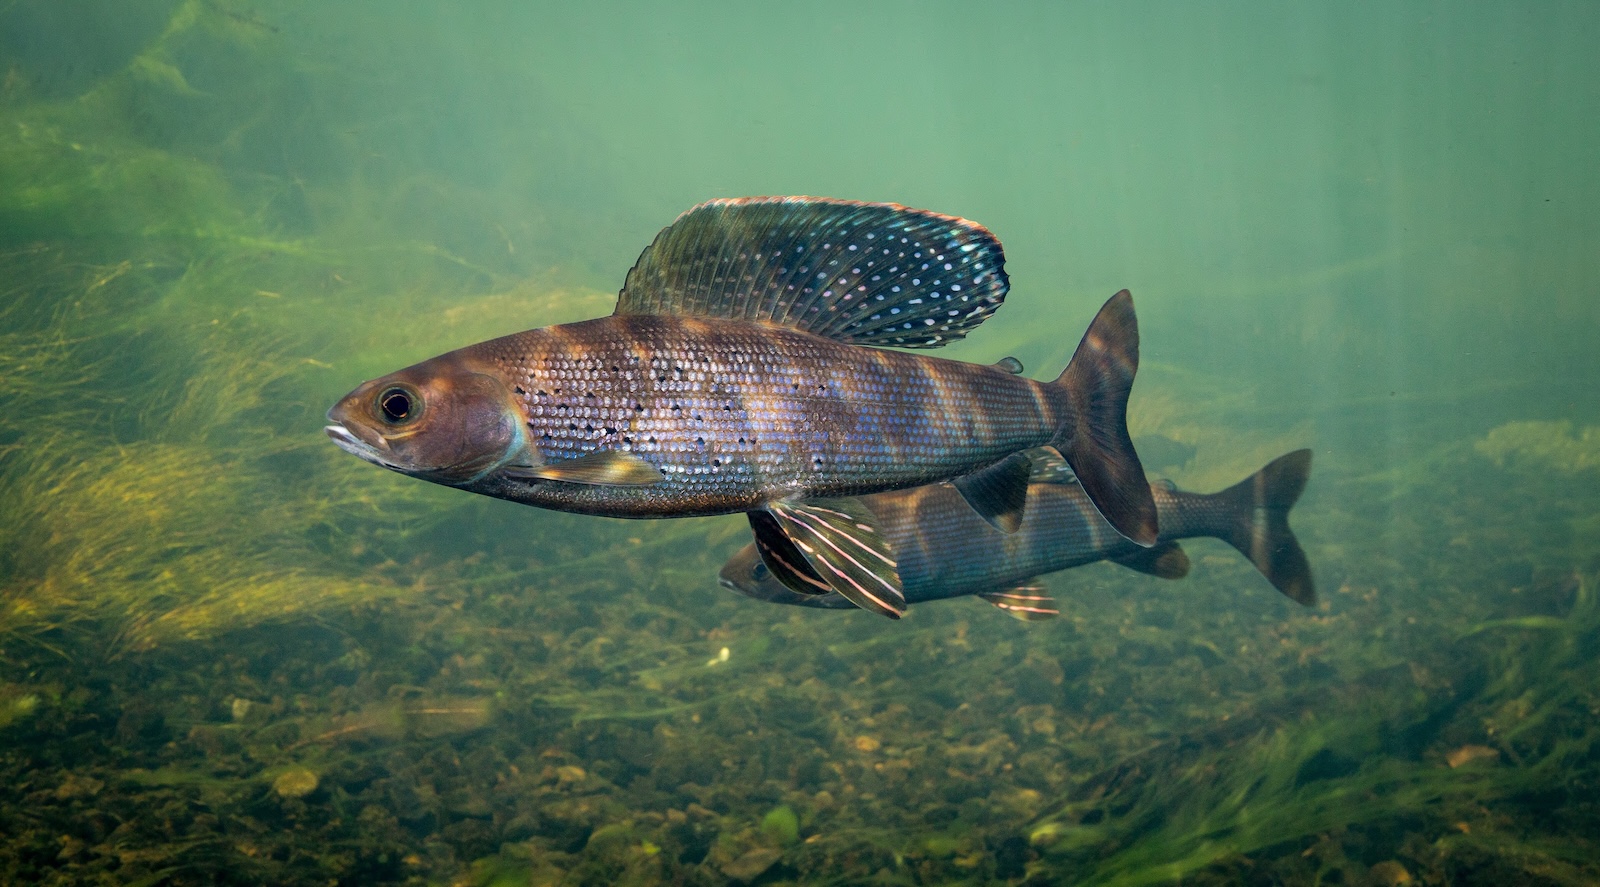
“Some of these might be catchable by the end of next year,” Leask said. “I don’t know what their growth will look like in the wild.”
That’s because Arctic grayling haven’t been seen in Michigan waters for almost a century. By the 1930s, industrial activity like logging and overfishing, along with competition from non-native fish, had decimated their numbers. But three northern Michigan tribes and the state are trying to change that by reintroducing the fish to local waters.
“Our taking care of them and helping them to reestablish their population helps us to reestablish ourselves, our culture, and our traditions,” said Tina Frankenberger, the Grand Traverse Band’s tribal environmental resiliency lead.
Their work joins broader efforts by tribes around the country to restore native species — from salmon to oysters to condors — that are culturally and economically important, while also strengthening the ecosystems that these species depend on against threats like climate change.
“Some of these might be catchable by the end of next year,” Leask said. “I don’t know what their growth will look like in the wild.”
That’s because Arctic grayling haven’t been seen in Michigan waters for almost a century. By the 1930s, industrial activity like logging and overfishing, along with competition from non-native fish, had decimated their numbers. But three northern Michigan tribes and the state are trying to change that by reintroducing the fish to local waters.
“Our taking care of them and helping them to reestablish their population helps us to reestablish ourselves, our culture, and our traditions,” said Tina Frankenberger, the Grand Traverse Band’s tribal environmental resiliency lead.
Their work joins broader efforts by tribes around the country to restore native species — from salmon to oysters to condors — that are culturally and economically important, while also strengthening the ecosystems that these species depend on against threats like climate change.
Weekly thread to discuss whatever you’re working on, big or small, at work or in your free time.
But let me guess… something TLS cert or PHP-related? 😆😭
Weekly thread to discuss whatever you’re working on, big or small, at work or in your free time.
But let me guess… something TLS cert or PHP-related? 😆😭



Remote computer management sounds simple until you actually have to manage several devices.
Being able to connect to a computer remotely is useful, but I think the more important question is what you can actually do once you’re connected.
For example, useful controls might include:
For people who have actually used remote-management or monitoring software, which feature made the biggest practical difference for you?
And which feature sounded useful on paper but turned out not to matter much in real use?
Remote computer management sounds simple until you actually have to manage several devices.
Being able to connect to a computer remotely is useful, but I think the more important question is what you can actually do once you’re connected.
For example, useful controls might include:
For people who have actually used remote-management or monitoring software, which feature made the biggest practical difference for you?
And which feature sounded useful on paper but turned out not to matter much in real use?
GOG temporarily offline for maintenance
I second others’ comments that #GOG is down likely for the #PHP issues made public.
GOG temporarily offline for maintenance
I second others’ comments that #GOG is down likely for the #PHP issues made public.

Makes you realize getting around by car has never been the most efficient form of travel no matter the width of a lane or roadway.
Congestion is always a thing caused by cars themselves.
Makes you realize getting around by car has never been the most efficient form of travel no matter the width of a lane or roadway.
Congestion is always a thing caused by cars themselves.
Hi everyone,
I am new to self-hosting and this is also my first post on Lemmy. I have a navidrome instance for my music (installed via docker compose) and a jellyfin instance for movies and shows (also installed via docker compose) running on a Raspberry Pi 4 8GB. I know I could also use music over jellyfin but I prefer to have it in navidrome.
The next thing that I want to achieve on my journey through the world of self-hosting is to run my own matrix server. The ideal eventual goal would be to have my own server on that same Raspberry Pi which I can then use to bridge Whatsapp to so I finally can get rid of that App from my primary phone. Receiving Whatsapp messages is unfortunately necessary for me to keep contact with certain people, although I would prefer to get rid of it completely as well, but who am I telling that, there are plenty of people out there facing the same issue.
As Whatsapp needs to run somewhere, which is required to have the bridge properly working, it would ideally run in an Android Virtual Device although that is no requirement as I know physical phones are recommended and emulated devices get blocked more often.
Ideally, the matrix server would also be installed using docker compose. It is intended to have one user only which is me but should of course be able to communicate with other servers to enable me to talk to others. The main limitation is that all three services should be running on that Raspberry Pi at the same time.
As my experience regarding such a project is virtually zero, my questions are:
Is such a setup is feasible and generally a good or bad idea (considering running jellyfin, navidrome and matrix on one Raspberry Pi)?
What issues should I consider before starting such a project?
If there’s someone having a similar setup, what are your experiences?
Also important to note: The matrix server should be able to handle video and voice calls as well, not in large rooms of course, but rather in a context of 2 to 4 people max.
Any advice, information or personal experience is well appreciated! I want to properly inform myself before starting out and thought here might be a good starting point. If I forgot to mention any specific information that is needed please let me know.
Thanks a lot!
EDIT: Adjusted post title to better reflect the advise-seeking character of this post and adjusted question phrasing
Hi everyone,
I am new to self-hosting and this is also my first post on Lemmy. I have a navidrome instance for my music (installed via docker compose) and a jellyfin instance for movies and shows (also installed via docker compose) running on a Raspberry Pi 4 8GB. I know I could also use music over jellyfin but I prefer to have it in navidrome.
The next thing that I want to achieve on my journey through the world of self-hosting is to run my own matrix server. The ideal eventual goal would be to have my own server on that same Raspberry Pi which I can then use to bridge Whatsapp to so I finally can get rid of that App from my primary phone. Receiving Whatsapp messages is unfortunately necessary for me to keep contact with certain people, although I would prefer to get rid of it completely as well, but who am I telling that, there are plenty of people out there facing the same issue.
As Whatsapp needs to run somewhere, which is required to have the bridge properly working, it would ideally run in an Android Virtual Device although that is no requirement as I know physical phones are recommended and emulated devices get blocked more often.
Ideally, the matrix server would also be installed using docker compose. It is intended to have one user only which is me but should of course be able to communicate with other servers to enable me to talk to others. The main limitation is that all three services should be running on that Raspberry Pi at the same time.
As my experience regarding such a project is virtually zero, my questions are:
Is such a setup is feasible and generally a good or bad idea (considering running jellyfin, navidrome and matrix on one Raspberry Pi)?
What issues should I consider before starting such a project?
If there’s someone having a similar setup, what are your experiences?
Also important to note: The matrix server should be able to handle video and voice calls as well, not in large rooms of course, but rather in a context of 2 to 4 people max.
Any advice, information or personal experience is well appreciated! I want to properly inform myself before starting out and thought here might be a good starting point. If I forgot to mention any specific information that is needed please let me know.
Thanks a lot!
EDIT: Adjusted post title to better reflect the advise-seeking character of this post and adjusted question phrasing
October 21, 2026
October 21, 2026

Ive checked all my self hosted services and was happy to find out the only one was written in PHP, addy, formerly anonaddy.
You can use the awesome self hosted GitHub repo or this one already filtered for PHP
Ive checked all my self hosted services and was happy to find out the only one was written in PHP, addy, formerly anonaddy.
You can use the awesome self hosted GitHub repo or this one already filtered for PHP